
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 learner202649/cve-2026-47102-poc
The code for personally reproducing the corresponding vulnerability
 speatx/chamilolms-cve-2023-4220
CVE-2023-4220 — Unauthenticated file upload RCE in Chamilo LMS ≤ 1.11.24. OSCP-style and auto exploit.
 affapple/cve-2025-24813-poc
Proof-of-concept exploit for CVE-2025-24813, demonstrating Apache Tomcat RCE via misconfigured file-based session persistence in DefaultServlet.
 logggg2402/cve-2025-27407
Local lab and proof-of-concept exploit for CVE-2025-27407, targeting GitLab's GraphQL introspection schema loader via the Direct Transfer HTTP path.…
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).
 dungsocool/cve-2017-18349
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
 march0n/poc-cve-2022-22965-spring4shell
Description
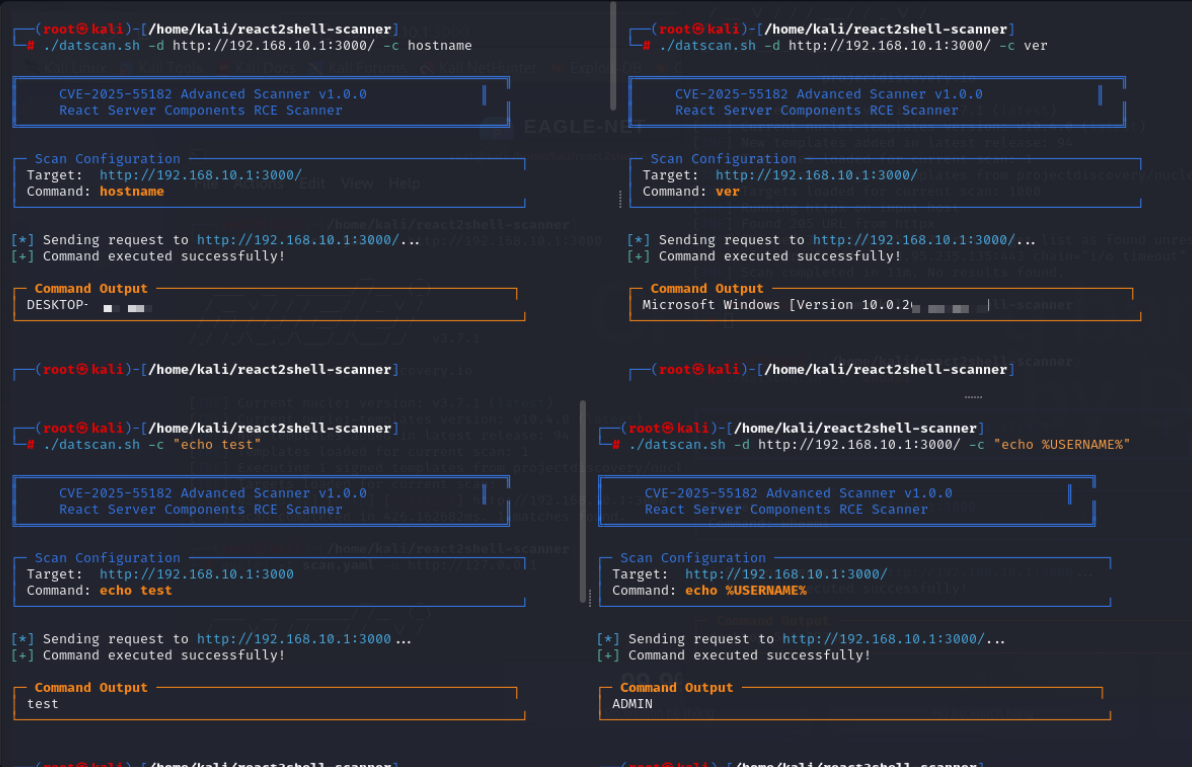 litndat/react2shell-poc-cve-2025-55182
PoC scanner and exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Detects vulnerable servers and executes remote…
 fineman999/poc_cve-2024-36420
Local reproduction lab and Nuclei template for CVE-2024-36420, an arbitrary file read vulnerability in Flowise via unsanitized fileName parameter.…
 nicolasjulian/bouncer-overflow
Working POC of CVE-2026-6664 written by Sonnet 4.6
 mythicaltree/cve-2019-2215
Proof-of-concept exploit for CVE-2019-2215 (Bad Binder) targeting Android 10 x86_64 emulator. Designed for isolated kernel exploitation research and…
 dylanclaudio/reporte-de-escalada-de-privilegios-local-dirty-frag
Se realizó una evaluación de vulnerabilidades sobre una máquina virtual con Kali Linux utilizando un script detector para la vulnerabilidad Dirty…
 swapnildeshpande/cve-2025-29927-lab
Reproduction lab for CVE-2025-29927 — Next.js middleware authorization bypass (CVSS 9.1)
 rootdirective-sec/cve-2026-8181-lab
Docker lab demonstrating CVE-2026-8181 authentication bypass in Burst Statistics WordPress plugin. Compares vulnerable and patched versions with a…
 jeanback1/cve-2025-2304-exploit
Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…
 sidjaz/crushftp-cve-2024-4040-proof-of-concept
Proof-of-concept exploit for CVE-2024-4040, demonstrating unauthenticated SSTI and local file read in CrushFTP, with Docker lab and mitigation…
 cthhhhhh/crushftp-ssti-lfi-proof-of-concept
Proof-of-concept for CVE-2024-4040 (CrushFTP SSTI -> unauthenticated LFI) in a controlled CS443 lab environment - for educational/authorised use only.
 akpmarcelin/cve-2026-24061-lab
Reproduction lab for CVE-2026-24061, an authentication bypass in GNU InetUtils telnetd. Provides a Vagrant-based isolated environment and…








