
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…
 athenasec16/cve-2026-29923
Proof-of-concept exploit for CVE-2026-29923, a BYOVD privilege escalation in pstrip64.sys. Demonstrates physical memory read/write via IOCTL to steal…
 shndnth/cve-2022-30190
Educational Proof-of-Concept for the CVE-2022-30190 (Follina) vulnerability.
 cryptomachio/cve-2025-5548
Estudio técnico de la vulnerabilidad CVE-2025-5548
 acseguin21/trust-boundary-ctf
Browser-based MCP CTF — OAuth token confusion and session isolation failure (CVE-2025-49596 pattern). DevTools only.
 joaovicdev/exploit-cve-2021-44228
Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
 h3raklez/cve-2024-3094
Educational lab replicating the XZ Utils backdoor (CVE-2024-3094) with a custom Ed448 key pair. Includes a patched liblzma, systemd service, and…
 salimelh94/web-penetration-test
Exploiting WordPress vulnerabilities (CVE-2025-34077), authentication bypass via cookie injection, and privilege escalation to root. Part of my…
 chernandez321/cve-2025-9074-docker-escape
Este script es para uso educativo y en entornos autorizados como HackTheBox. El uso contra sistemas sin permiso explícito es ilegal.
 0xblackash/cve-2026-5173
CVE-2026-5173
 devsecurityspro/cve-2026-34197
Proof-of-concept exploit for CVE-2026-34197, an RCE in Apache ActiveMQ via the Jolokia API. Includes a Python exploit, payload template, and Docker…
 zpol/cve-2026-23398-poc
Reproducible lab for CVE-2026-23398, a Linux kernel NULL dereference in icmp_tag_validation() triggered by ICMP Fragmentation Needed packets, causing…
 v0idw1re/htb-pterodactyl-writeup
HackTheBox — Pterodactyl (Medium/Linux) walkthrough. CVE-2025-49132 LFI → pearcmd RCE → bcrypt crack → SSH. Privesc via CVE-2025-6018 (PAM…
 bvabhishek/cve-2026-3288-lab
Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
 erev0s/vampi
Vulnerable REST API with OWASP top 10 vulnerabilities for security testing
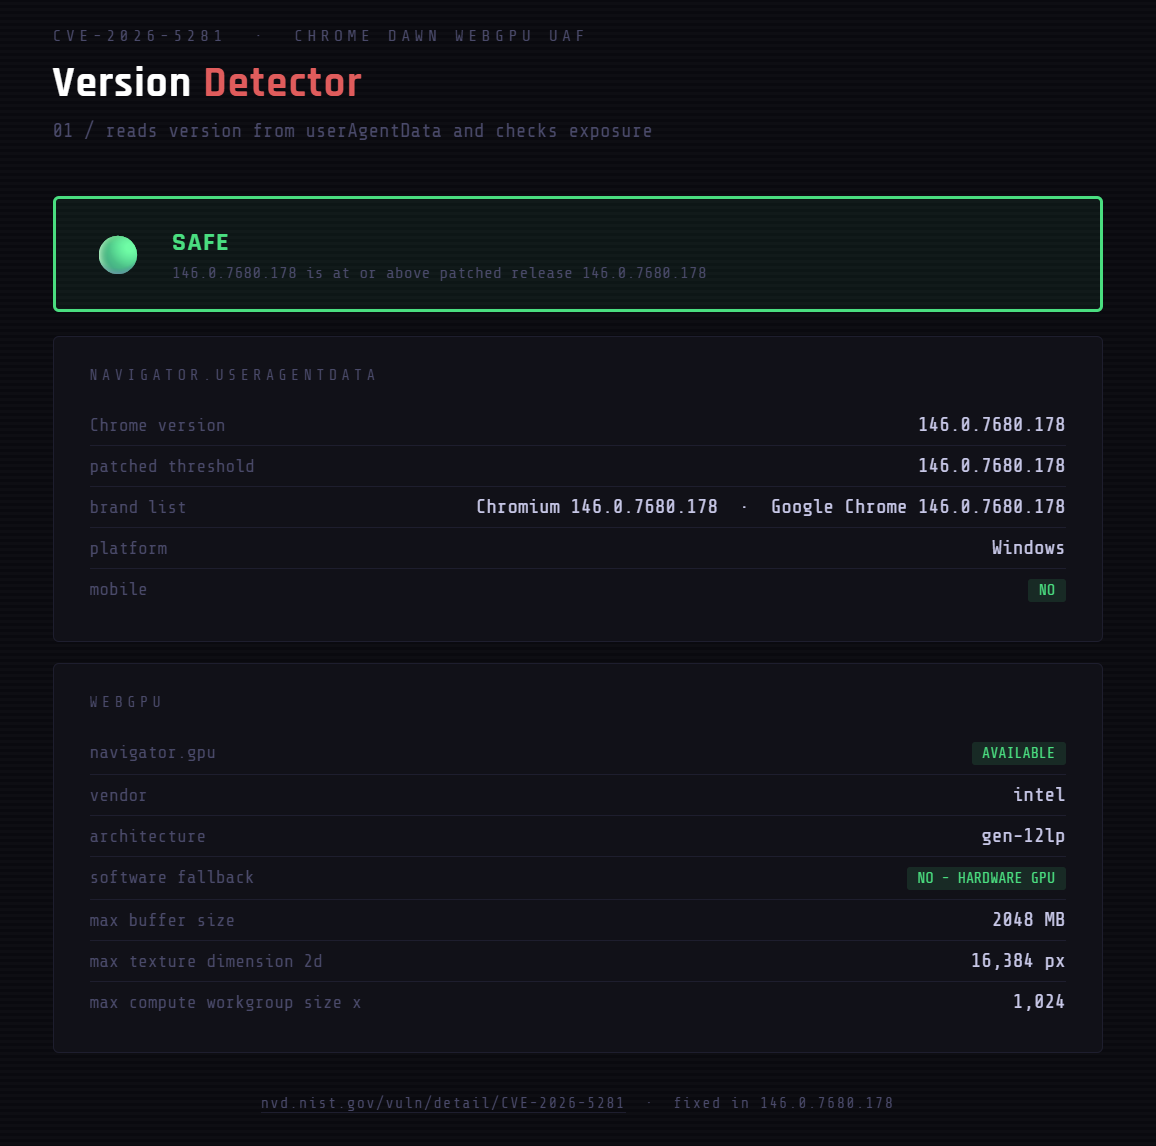 themalwareguardian/cve-2026-5281
CVE-2026-5281 (Chrome Dawn WebGPU UAF) analysis, lab validation tools, and reproducible environment for vulnerable vs patched builds.
 zsxen/cve-2025-1974-lab
Hands-on lab environment for exploiting CVE-2025-1974, designed for security training and vulnerability research practice.
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.








