
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended
 frosterdl/cve-2026-31431
Educational repository analyzing CVE-2026-31431, providing lab-based testing guidance and defensive awareness for authorized security research.
 themalwareguardian/cve-2026-33439
First publicly shared exploit implementation for CVE-2026-33439 (OpenAM pre-auth RCE via jato.clientSession deserialization).
 mobilehackinglab/cve-2026-0047-poc
CVE-2026-0047: Missing permission check in ActivityManagerService.dumpBitmapsProto() — steal UI bitmaps from every running app with zero permissions…
 simantchaudhari/cve-2025-24054-poc
Proof-of-concept exploit for CVE-2025-24054, a Windows Library (.library-ms) NTLM hash disclosure vulnerability. Generates a malicious .library-ms…
 heventafese/penetration-testing-walkthrough-hacksudo-thor
Black-box penetration test against HackSudo Thor : CVE-2014-6271 Shellshock RCE through Apache mod_cgi, chained with sudo misconfiguration and bash…
 kamal-418/vulnerable-lab-nextjs-cve-2025-29927
Deliberately vulnerable Next.js application designed for practicing exploitation of CVE-2025-29927, with a tutorial video for guided learning.
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
 navya240/intel471-threat-hunting-cve-2023-46604
My first hands-on Intel 471 threat hunting workshop experience investigating CVE-2023-46604 using Elastic SIEM, vulnerability intelligence, and…
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
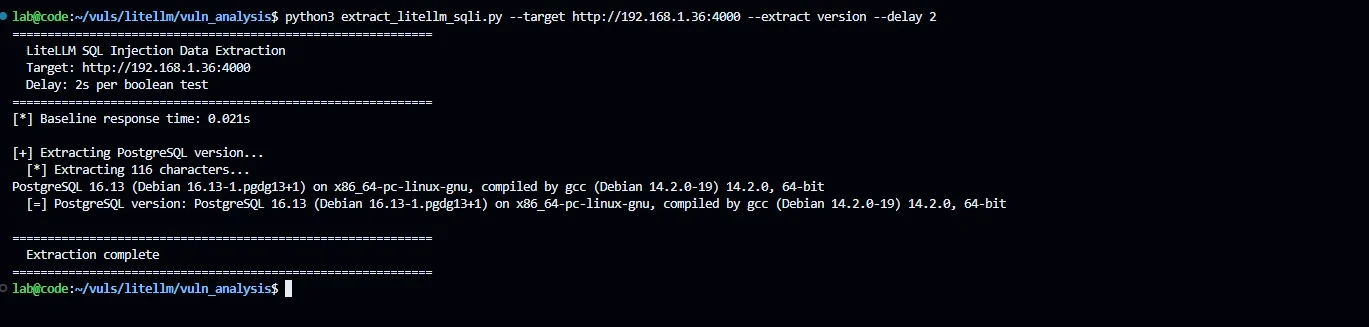 imjdl/cve-2026-42208_lab
Reproduction environment for a critical SQL injection in LiteLLM Proxy's API key authentication, with a time-based blind PoC and Docker setup for…
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 klmntbelgium/cve-2021-41773-exploration
Recreation and analysis of a curious logic error in Apache 2.4.49 that escalated to remote code execution
 eqstlab/cve-2026-33937
Handlebars.js AST Injection Remote Code Execution Vulnerability
 anthonydavidson189/free-interactive-ai-training-materials
Curated collection of free, interactive AI-powered training materials for security awareness education, with community contributions and practical…
 dhiaelhak-rached/cve-2026-39987-lab-or-marimo-cve-lab
Educational Docker lab demonstrating CVE-2026-39987, a pre-auth RCE via WebSocket authentication bypass in marimo, with exploit script and patch…
 jeanback1/cve-2025-2304-exploit
Python exploit script for CVE-2025-2304, a mass assignment privilege escalation in Camaleon CMS. Automates CSRF token parsing and role parameter…
 hivinmanjusri/ubuntu-cve-2019-14287-patch-manager
patch-manager
 baph00met/cve-2026-41651
Proof-of-concept exploit for CVE-2026-41651, a PackageKit TOCTOU local privilege escalation, with technical analysis, detection logic, and…








