
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 muhammedkayag/cve-2025-32463
Proof-of-concept demonstrating a local privilege escalation in sudo (CVE-2025-32463) via chroot configuration manipulation, intended for defensive…
 leonjza/inetutils-telnetd-auth-bypass
A small docker lab to play with cve-2026-24061, the inetutils-telnetd authentication bypass.
 lastvocher/redis-cve-2025-49844
Educational lab environment with a proof-of-concept exploit for CVE-2025-49844 (RediShell), a critical use-after-free in Redis Lua interpreter,…
 kanitan/log4j2-web-vulnerable
A vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
 k0nnect/cve-2026-21440-writeup-poc
poc and writeup for cve-2026-21440: a critical path traversal vulnerability in @adonisjs/bodyparser allowing arbitrary file writing
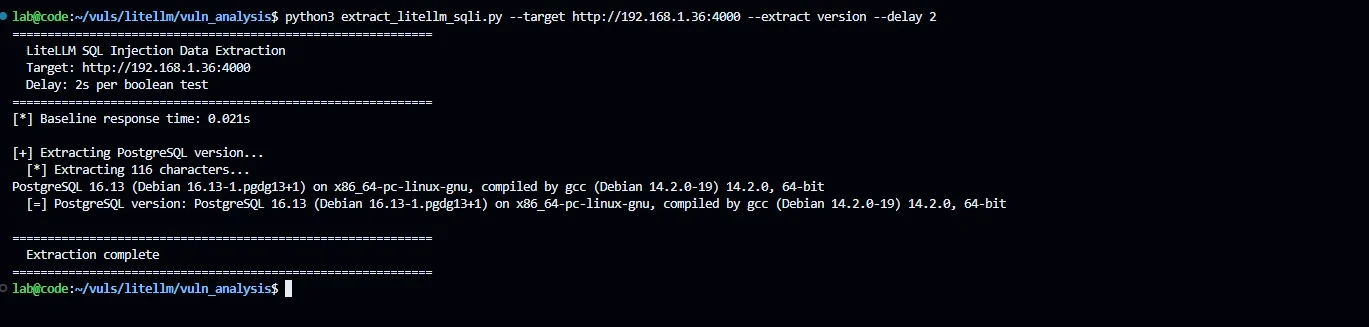 imjdl/cve-2026-42208_lab
Reproduction environment for a critical SQL injection in LiteLLM Proxy's API key authentication, with a time-based blind PoC and Docker setup for…
 gavz/cve-2026-21509-poc
Educational PoC generating a harmless DOCX with dummy OLE artifacts to test EDR/AV visibility, ASR rules, and sandbox analysis for CVE-2026-21509.…
 dinosn/pack2theroot-lab
CTF-style Docker lab for CVE-2026-41651 (Pack2TheRoot): PackageKit permissive-polkit local privilege escalation
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 carlosalbertotuma/cve-2026-2058-poc
Proof-of-concept exploit for CVE-2026-2058, a SQL injection in CloudClassroom PHP Project, with automated database enumeration and data extraction.
 bvabhishek/cve-2026-3288-lab
Docker-based vulnerable lab for CVE-2026-3288 NGINX Ingress configuration injection, with exploit scripts, detection monitoring, and remediation…
 baph00met/cve-2026-41651
Proof-of-concept exploit for CVE-2026-41651, a PackageKit TOCTOU local privilege escalation, with technical analysis, detection logic, and…
 av4nth1ka/jinjava-cve-2026-25526-poc
Step-by-step exploit harness and proof-of-concept for CVE-2026-25526 in Jinjava, demonstrating file read, file creation, and info disclosure with…
 androidteacher/cve-2026-24061-poc-telnetd
Proof-of-concept exploit for CVE-2026-24061, an unauthenticated remote root privilege escalation in inetutils-telnetd via USER environment variable…
 amusedx/cve-2026-22686
CTF challenge focused on sandbox escape via source code review of a JavaScript execution environment, designed for hands-on vulnerability analysis…
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
 abhayclasher/cve-2026-39866
Proof-of-concept lab demonstrating command injection in GitHub Actions workflow dispatch (CVE-2026-39866). Runs vulnerable and patched versions…
 abhayclasher/cve-2026-33331
Local lab reproducing stored XSS in oRPC's OpenAPI docs generation (CVE-2026-33331), with vulnerable and patched versions for comparison and a…








