
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 libasmon/exploite-cve-2023-30212-vulnerability
Docker environment and exploit the CVE-2023-30212 vulnerabilityVE-2023-30212 is a security vulnerability that affects versions of OURPHP prior to or…
 manishrawat21/detection-rules
This repository contains validated detection rules for adversary behaviors observed during APT29 simulation. Each rule was tested against the actual…
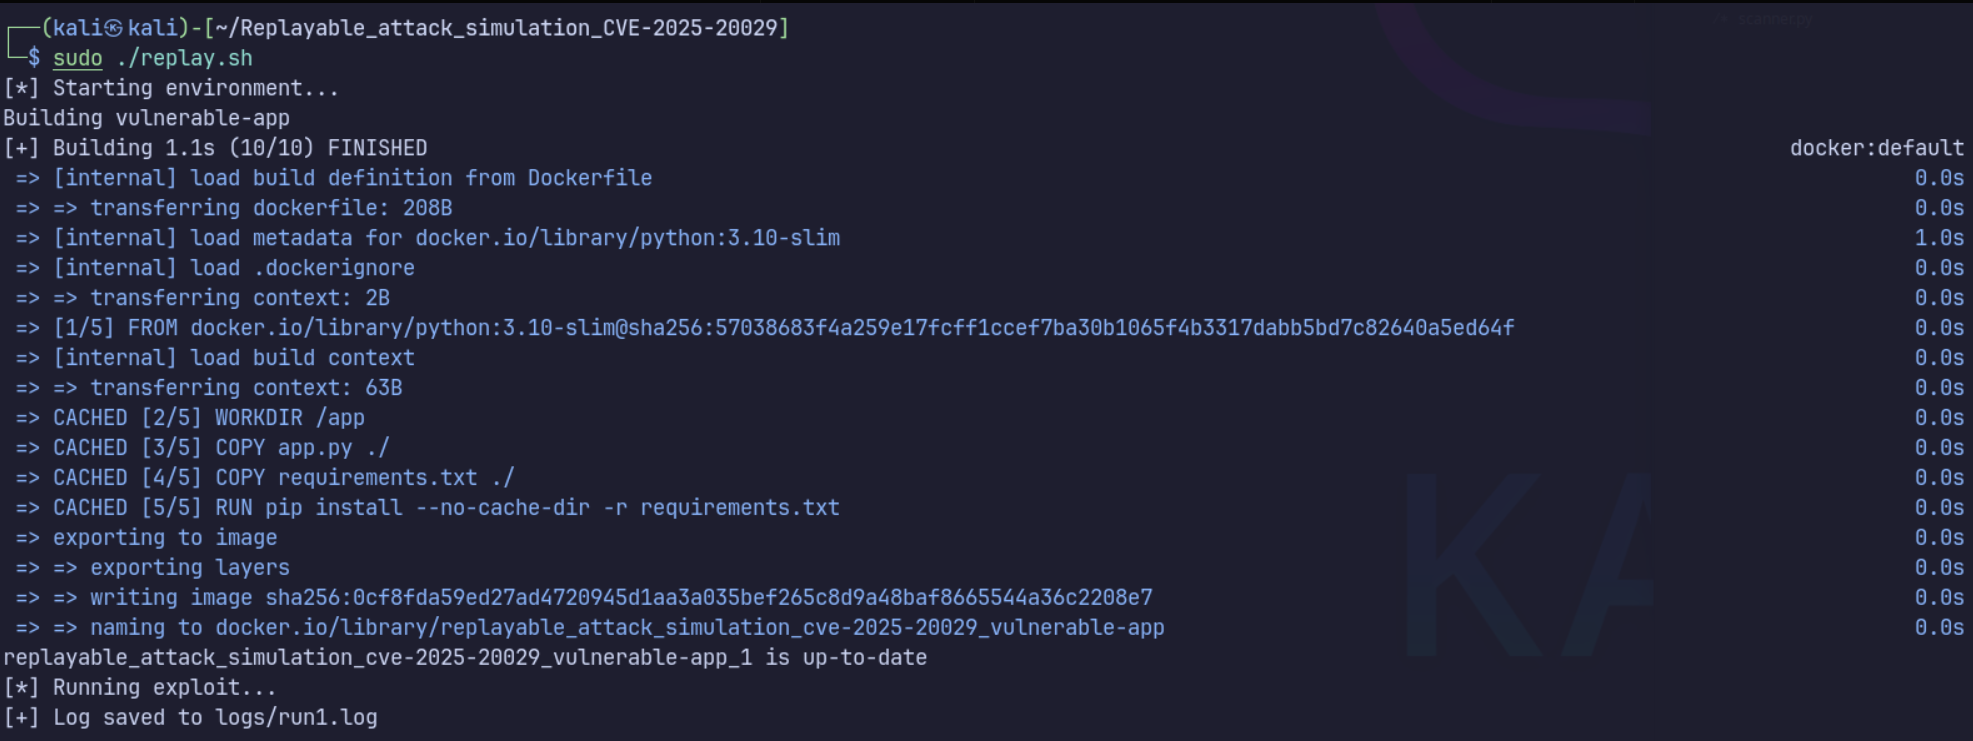 schoi1337/cve-2025-20029-simulation
Simulated environment for CVE-2025-20029 using Docker. Includes PoC and auto-reporting.
 trackflaw/cve-2024-1071-docker
CVE-2024-1071 with Docker

 rode0day/fuzzer-testing
Docker images for testing fuzzers on the Rode0day corpora
 ptantiku/cve-2015-2208
Docker simulating cve-2015-2208 vulnerability
 pouriam23/next.js-middleware-bypass-cve-2025-29927-
CTF challenge to learn and practice exploiting the Next.js middleware bypass vulnerability (CVE-2025-29927) by finding a flag in an admin page.
 mseymend/cve-2022-22954-testi
CVE-2022-22954 Açığı test etme
 j4ck3lsyn-gen2/cve-2025-53770
Lab & PoC
 imbios/lab-cve-2016-15042
CVE-2016-15042 lab: Dockerized WordPress PoC for unauthenticated file upload in Frontend File Manager <4.0 and N‑Media Post Front‑end Form <1.1
 qw3rtyou/cve-2021-44228_dockernize
Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
 kazuya256/next-js-auth-bypass
🔓 Next.js Auth Bypass Demo - Educational application demonstrating CVE-2025-29927 middleware authentication bypass vulnerability . ⚠️ For…
 hmlio/vaas-cve-2015-5477
Vulnerability as a service: showcasing CVS-2015-5447, a DDoS condition in the bind9 software
 hashdr1ft/soc274-palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400
SOC lab exercise for analyzing and responding to Palo Alto Networks PAN-OS command injection vulnerability (CVE-2024-3400) with step-by-step incident…
 flame-11/cve-2025-54068-livewire
Reproducible Docker-based lab for CVE-2025-54068 in Livewire v3.6.3, including a safe PoC exploit chain script for educational vulnerability analysis.
 awidardi/opsxcq-cve-2016-10033
To solve CTFS.me problem
 amalpvatayam67/day08-cisco-fmc-sim
This is a minimal, educational simulation that demonstrates the _impact_ class of a management-plane parsing RCE (inspired by CVE-2025-20265). It…
 acceis/exploit-cve-2023-38490
Kirby < 3.9.6 XML External Entity exploit








