
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 owasp/owasp-learning-gateway
OWASP Learning Gateway Project
 snyk-labs/pdfjs-vuln-demo
This project is intended to serve as a proof of concept to demonstrate exploiting the vulnerability in the PDF.js (pdfjs-dist) library reported in…
 nishanthanand21/cve-2023-4911-poc
Repository containing a Proof of Concept (PoC) demonstrating the impact of CVE-2023-4911, a vulnerability in glibc's ld.so dynamic loader, exposing…
 marcourbano/cve-2021-44228
PoC for CVE-2021-44228.
 ycdxsb/log4shell-cve-2021-44228-env
Log4Shell Docker Env
 yumeae/bootstrap-with-xss
A poc for Bootstrap XSS(CVE-2024-6485、CVE-2016-10735、CVE-2019-8331、CVE-2018-14040)
 unclesocks/cyberresponders
CyberResponders is a terminal-based cybersecurity training game that enables players to respond to different cyber incident scenarios. Here, they…
 trackflaw/cve-2024-10924-wordpress-docker
Vulnerable docker container for Really Simple Security (Free, Pro, and Pro Multisite) 9.0.0 – 9.1.1.1 – Authentication Bypass CVE-2023-50164
 anonymking/cve-2017-1000117
CVE-2017-1000117漏洞复现(PoC+Exp)
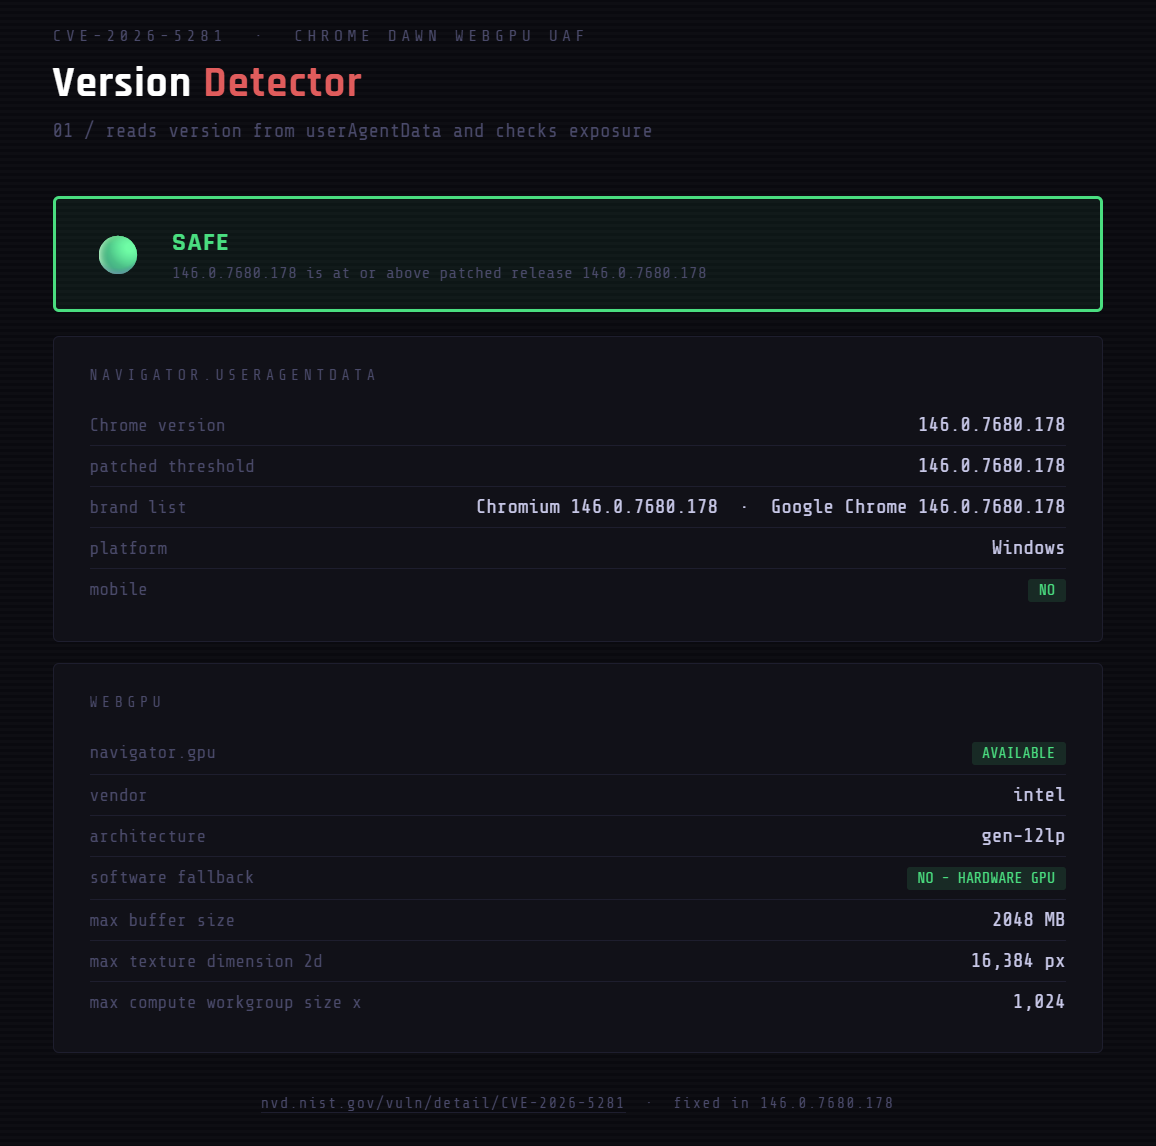 themalwareguardian/cve-2026-5281
CVE-2026-5281 (Chrome Dawn WebGPU UAF) analysis, lab validation tools, and reproducible environment for vulnerable vs patched builds.
 infosecantara/cve-2025-14765-and-cve-2025-14766
Interactive browser-based lab simulating Chrome memory corruption vulnerabilities (CVE-2025-14765/14766) for safe security training, featuring…
 sethwhy/bluedoor
Can you exploit the EternalBlue vulnerability (CVE-2017-0144) on a Windows 7 system and retrieve the hidden flag? Your goal is to gain administrative…
 m3ssap0/wordpress-jetpack-broken-access-control-vulnerable-application
WARNING: This is a vulnerable application to test the exploit for the Jetpack < 13.9.1 broken access control (CVE-2024-9926). Run it at your own risk!
 horkimhab/cve-2026-6875
CVE-2026-6875
 xxxtectationxxx/react2shell-cve-lab
A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…
 secvulnhub/cve-2025-32463-exploit
Proof-of-concept exploit for CVE-2023-42456, demonstrating privilege escalation via sudo NSS library hijacking through chroot injection. Includes…
 bananoname/cve-2021-42013
Python script to detect and exploit path traversal and remote code execution in Apache 2.4.50 (CVE-2021-42013), with bulk scanning and a Docker lab…
 betan423/cve-2024-23334-poc
This repository is a proof of concept (POC) for CVE-2024-23334, demonstrating an attempt to replicate the bug in aiohttp that leads to Local File…








