
 #1
Training labs, hands-on environments, and reproducible challenges for authorized, safe cybersecurity practice.
Kitploit recommended

 shivam-bathla/cve-2026-24061-setup
Docker setup for CVE-2026-24061
 enochgitgamefied/nextjs-cve-2025-29927
Intentionally vulnerable Next.js application demonstrating CVE-2025-29927 authentication bypass via middleware WAF evasion. Designed for security…
 edoverflow/bugbounty-cheatsheet
A list of interesting payloads, tips and tricks for bug bounty hunters.
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
 zealraj/cybersecurity-books
Here you will get awesome collection of mostly all well-known and usefull cybersecurity books from beginner level to expert for all cybersecurity…
 mobilehackinglab/cve-2026-0006-openapv-poc
CVE-2026-0006: Heap buffer overflow PoC for libopenapv (Android APV codec) - CVSS 9.8

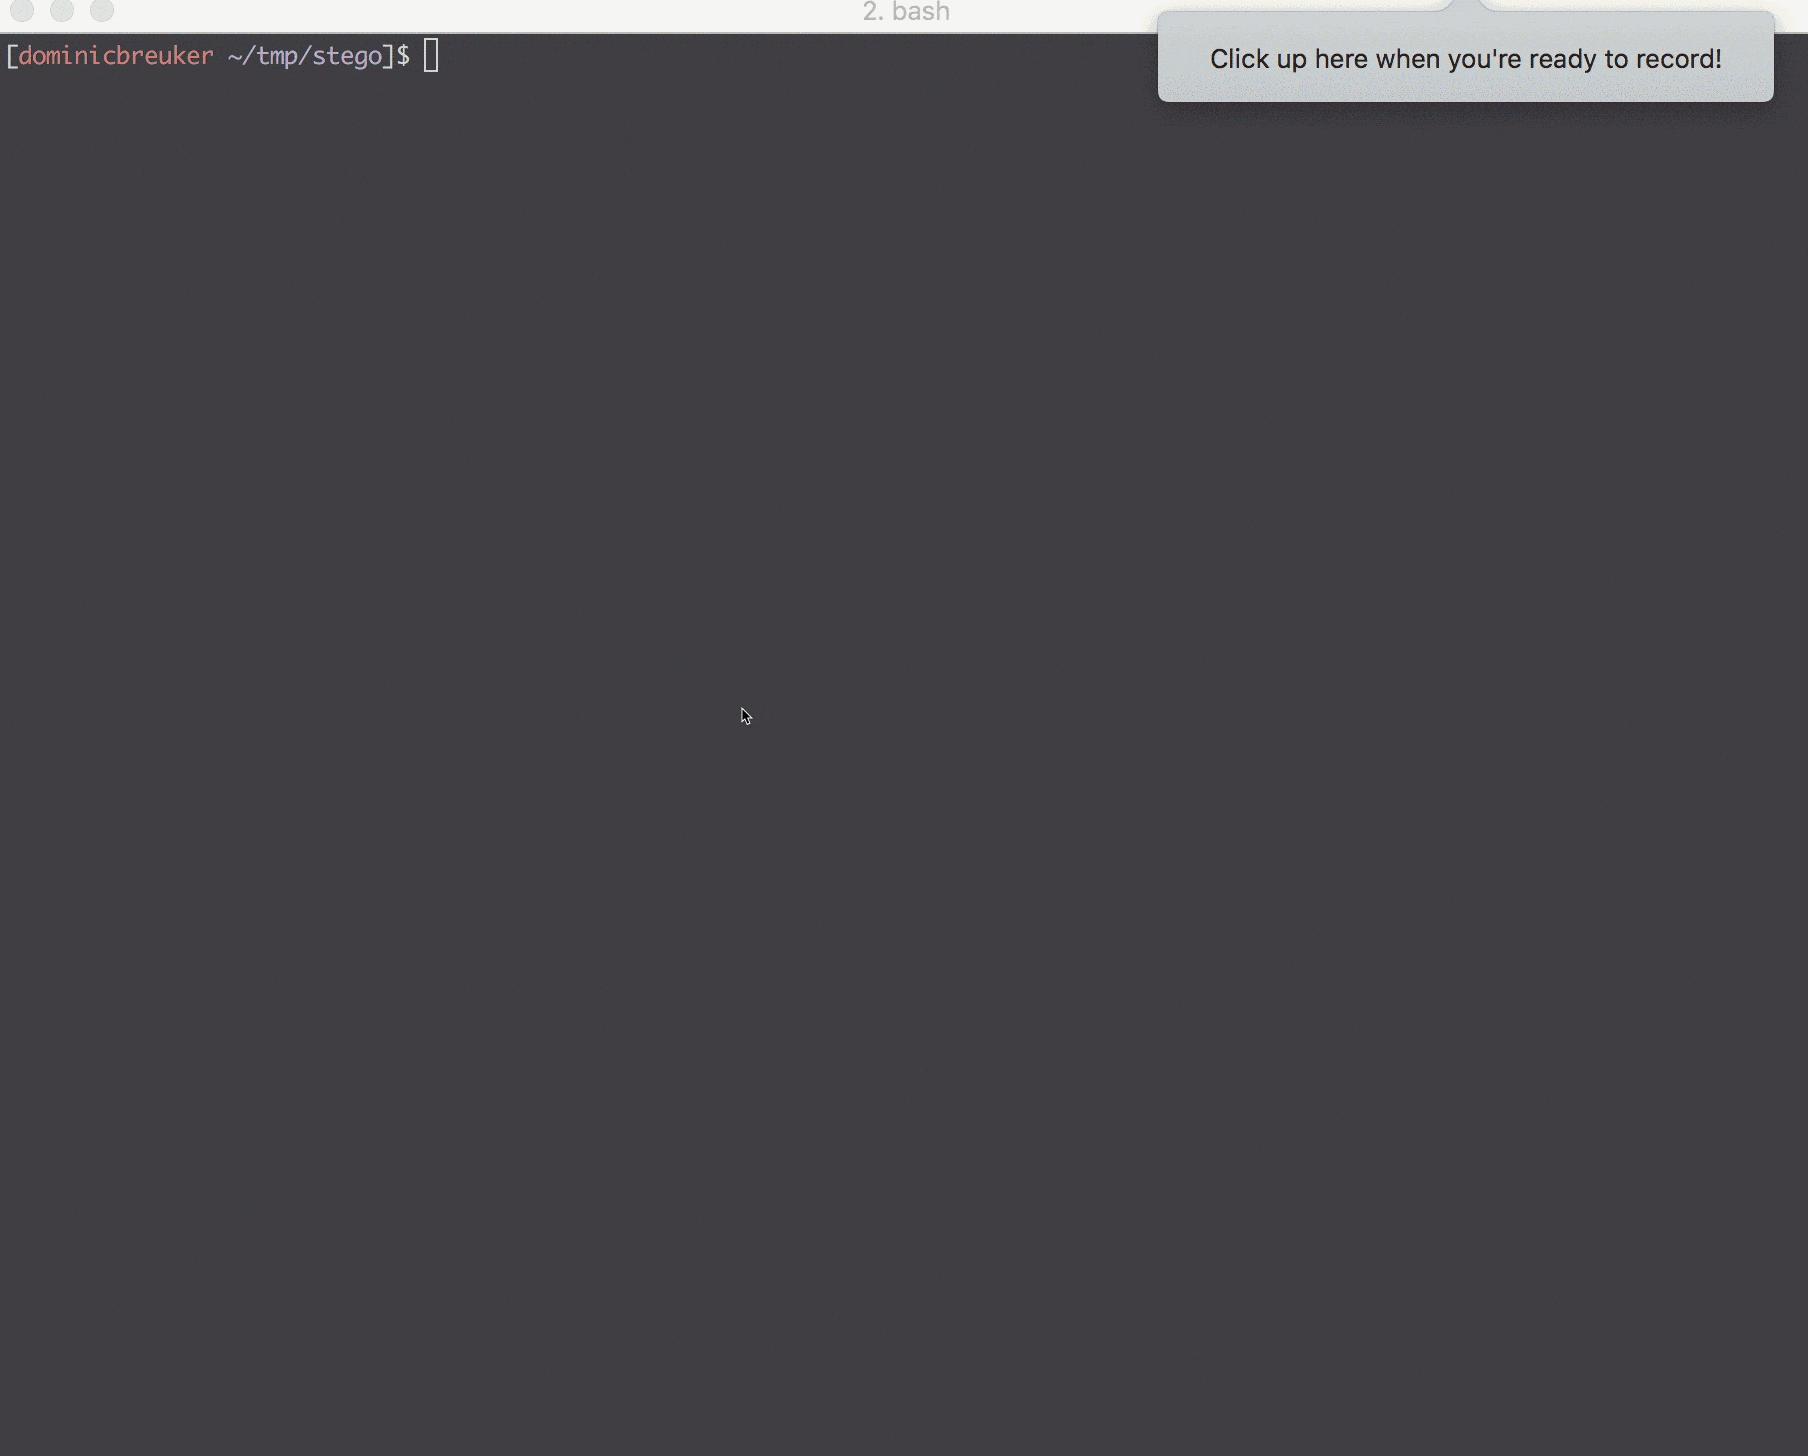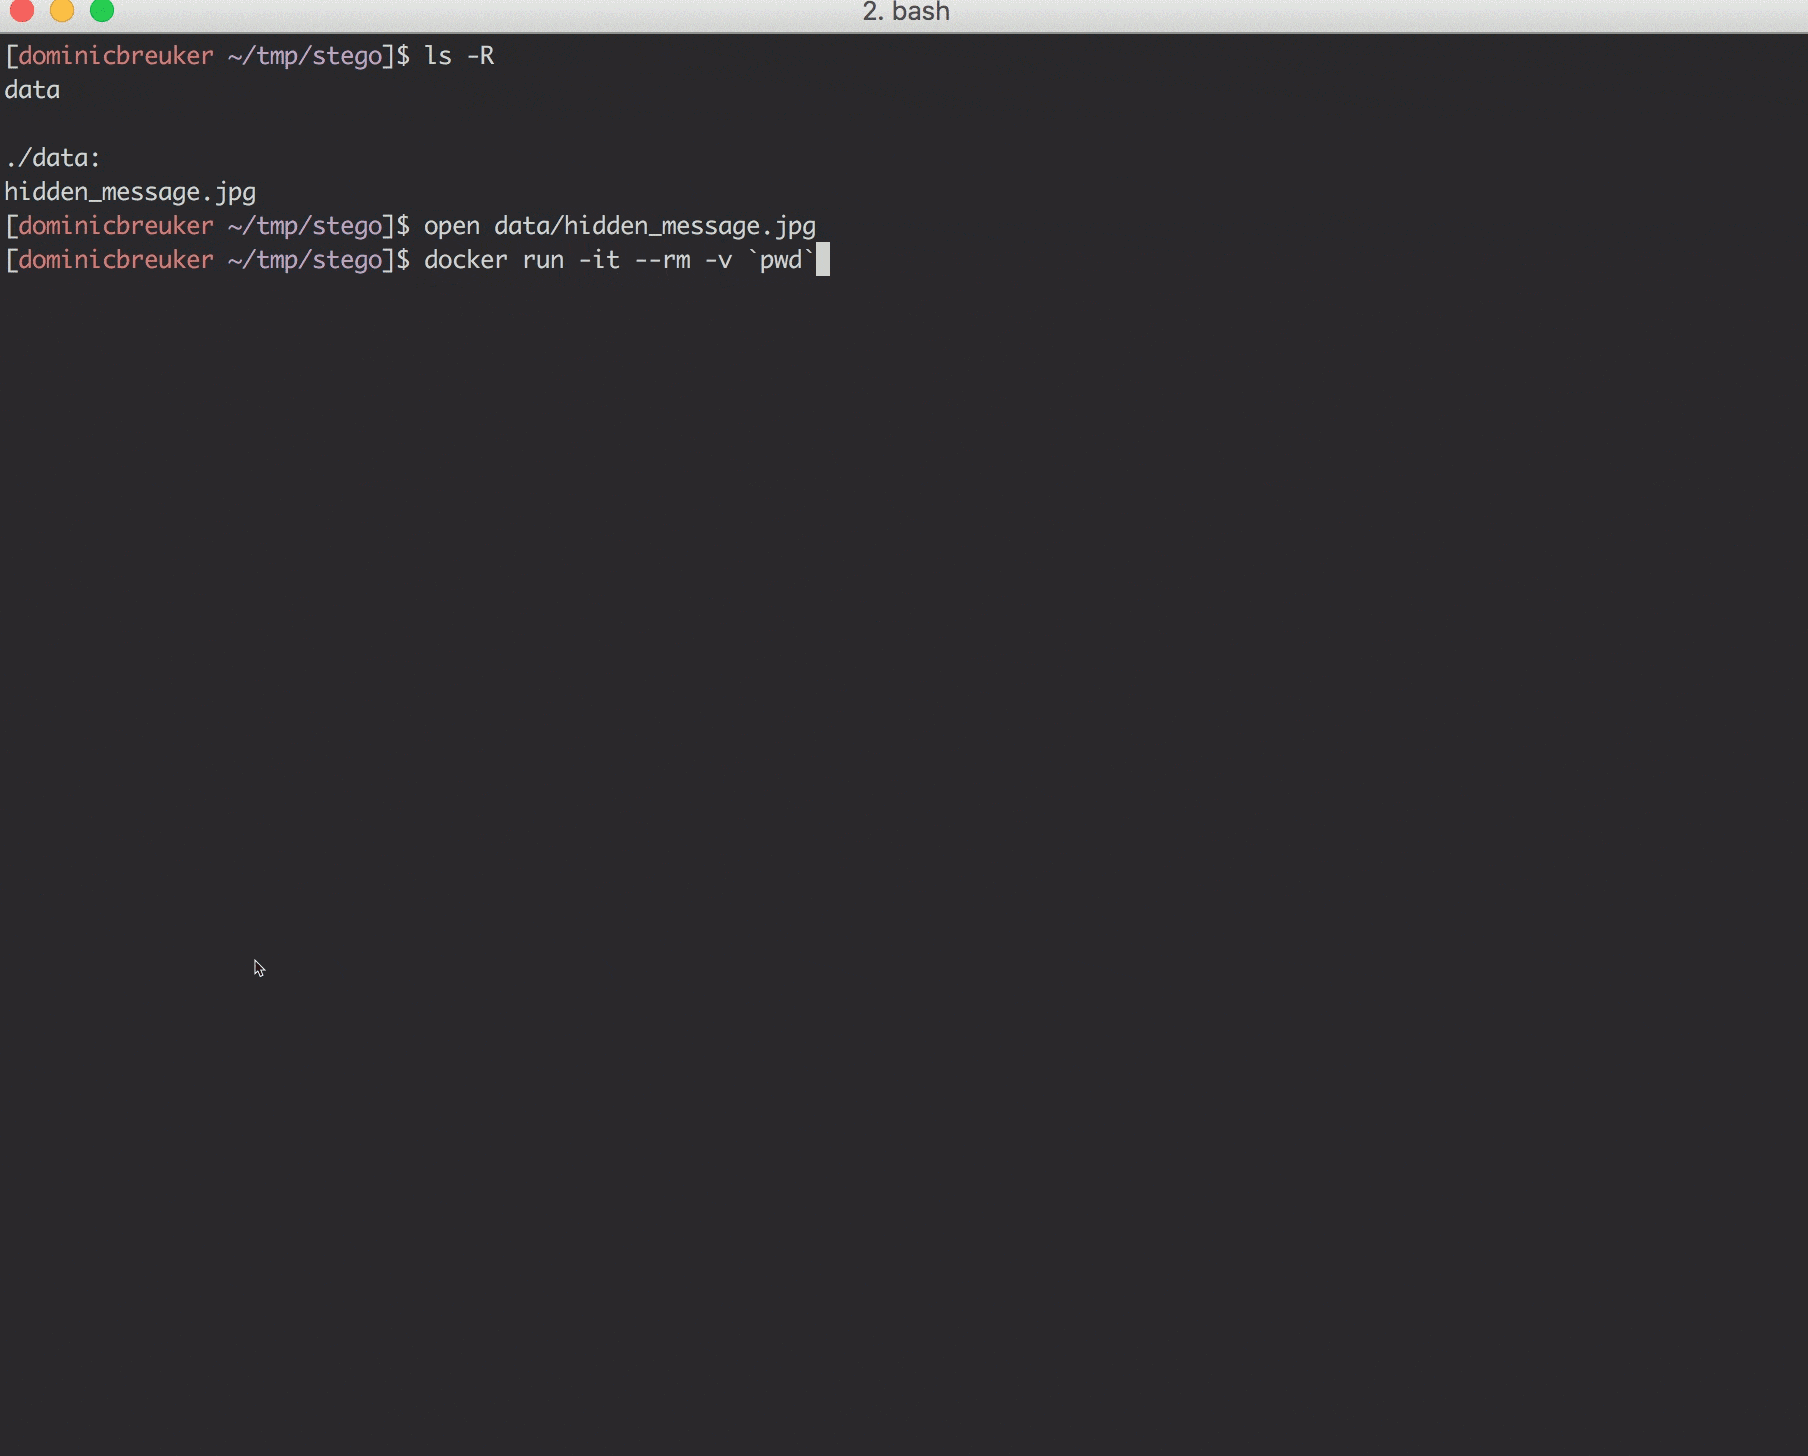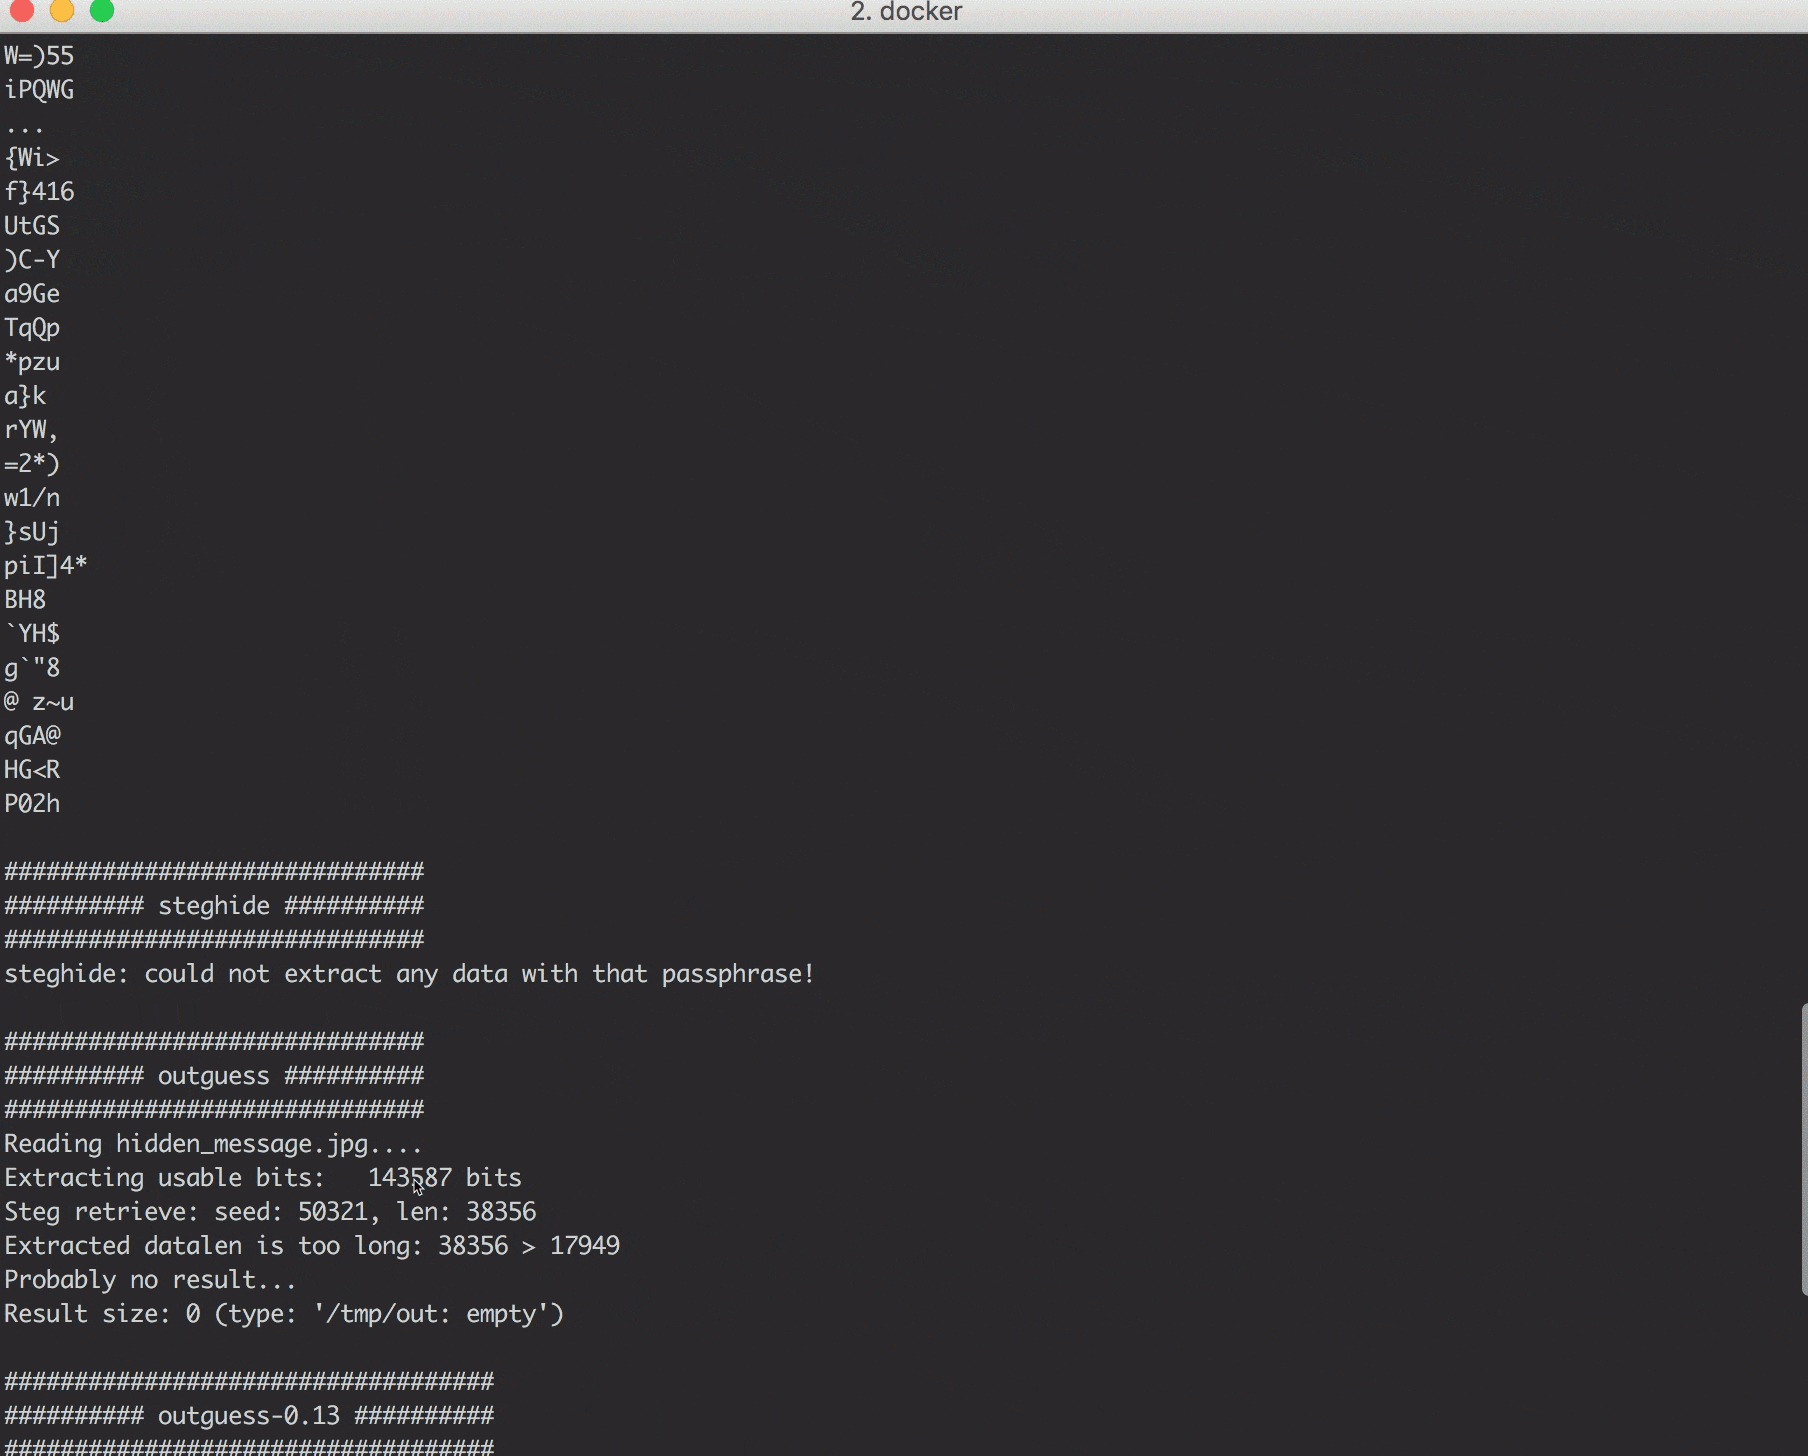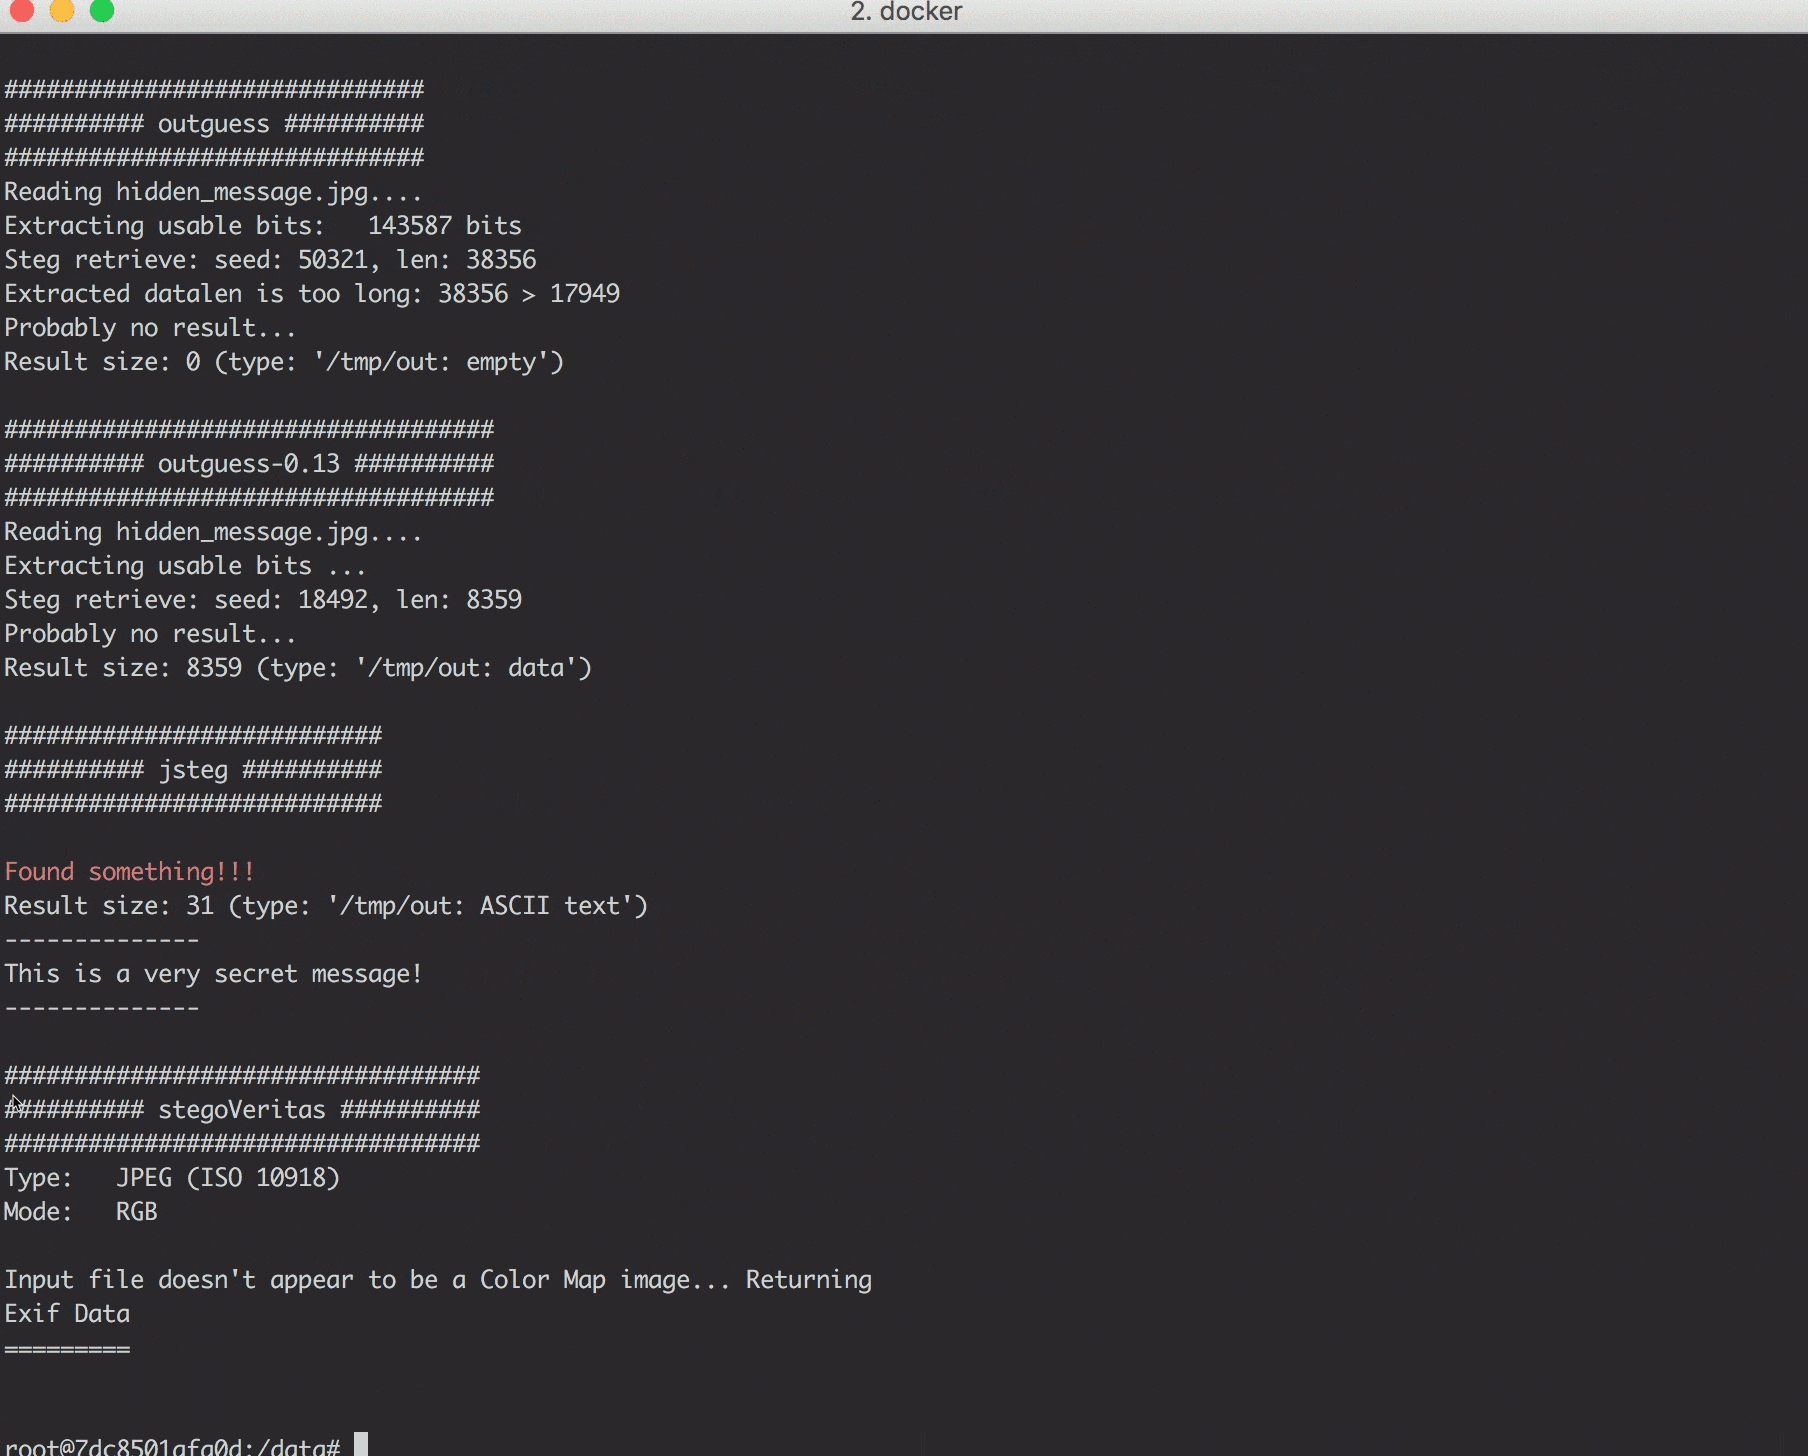 dominicbreuker/stego-toolkit
Collection of steganography tools - helps with CTF challenges
 bishopfox/cloudfoxable
Create your own vulnerable by design AWS penetration testing playground
 aramosf/joomla_exploits
Curated collection of validated Joomla exploit artifacts with Docker lab environments. Includes RCE, SQLi, XSS, and privilege escalation scripts…
 cves-labs/cve-2026-22241
Lab Environment for CVE-2026-22241
 yonliud/cve-2026-76904
One-Day POC | GeoServer Unauthenticated SQL injection to complete RCE
 momenbasel/htb-writeups
Structured collection of 500+ Hack The Box machine writeups, 400+ challenge solutions, and interactive learning tools including knowledge graphs,…
 saferman/cve-2020-7471
django 漏洞:CVE-2020-7471 Potential SQL injection via StringAgg(delimiter) 的漏洞环境和 POC
 revyhub/cve-2026-43284---dirtyfrag-analysis-thm-
TryHackMe Dirty Frag (CVE-2026-43284) — Linux LPE writeup
 cved-sources/cve-2018-3810
Docker container providing a vulnerable environment for CVE-2018-3810, designed for security testing and educational exploitation practice within…
 s3v3n-jg/cve-2026-76460
Educational Flask lab simulating CVE-2026-76460 authentication bypass, with vulnerable, secure, and strict modes plus a PoC exploit script and…
 trailofbits/not-going-anywhere
Intentionally vulnerable Golang programs exposing web, gRPC, and database/sql flaws for security training, vulnerability discovery, and remediation…








