
 #1
Tools for testing and securing Internet of Things (IoT) devices, protocols, and platforms.
Kitploit recommended
 cybervinner/tp-link-tl-wr820n-cve-2025-14175
Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
 joelczk/cve-2025-48461
Technical disclosure of a predictable session cookie vulnerability (CVE-2025-48461) in Advantech WISE-4060 IoT portal, enabling bruteforce…
 passwa11/re11s_1.11-formaccept-commandinjection
CVE-2025-22912
 semaja22/cve-2025-57174
CVE-2025-57174 Unauthenticated Remote Command Execution
 szym0n13k/cve-2025-55971-blind-unauthenticated-ssrf-in-tcl-smart-tv-upnp-dlna-avtransport
TCL 65C655 Smart TV, running firmware version V8-R75PT01-LF1V269.001116 (Android TV, Kernel 5.4.242+), is vulnerable to a blind, unauthenticated…
 h4ckusaur/cve-2024-57366
Remote code execution exploit for CVE-2024-57366 targeting WAVLINK routers via MAC address validation bypass and command injection, with automatic…
 renukaselvar/system_bt_aosp10_cve-2022-20140
Android Bluetooth stack (Fluoride) with a proof-of-concept for CVE-2022-20140, demonstrating a Bluetooth vulnerability and providing build…
 abizchi/cve-2018-9995_dvr_credentials
Python exploit for CVE-2018-9995 that retrieves exposed DVR credentials by bypassing authentication on vulnerable web interfaces.
 weedl/cve-2025-45619
CVE proof of concept regarding the CVE-2025-45619 vulnerabillity.
 finn79426/cve-2012-5960-poc
CVE-2012-5960, CVE-2012-5959 Proof of Concept
 goldenticketlabs/cve-2025-52413
repo for CVE-2025-52413
 nanopathi/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) source code for AOSP 10 r33, specifically related to CVE-2021-0431 Bluetooth vulnerability research and…
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 aseemjakhar/kcmd
Kankun Smart Socket Hijacker and Sniffer. The kankun smart socket and its mobile app use a hardcoded AES 256 bit key to encrypt and decrypt…
 lastvocher/hikvision-cve-2017-7921-decryptor
Decrypts Hikvision IP camera configuration files extracted via CVE-2017-7921 authentication bypass, recovering user credentials from weakly encrypted…
 tateydq/cve-2018-9995-modifiedbygwolfs
Exploit for CVE-2018-9995 to retrieve DVR credentials via directory traversal, with two methods for educational use.
 stigtsp/cve-2018-20162-digi-lr54-restricted-shell-escape
Proof-of-concept exploit for CVE-2018-20162: sandbox escape in Digi TransPort LR54 LTE router via SIGINT handling flaw, yielding root shell access.
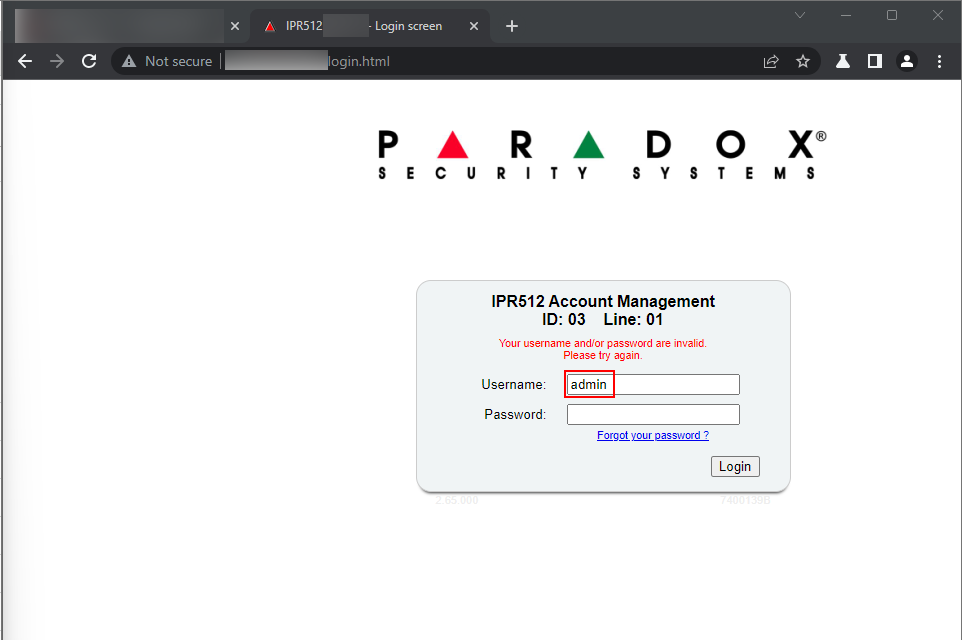 darknesschieftain/injection-vulnerability-in-paradox-security-systems-ipr512-cve-2023-24709-poc
In Paradox Security System IPR512 Web console login form page, attacker can input JavaScript string, such as "</script>" that will overwrite…








