#1
Tools focused on testing, reversing, and securing iOS applications and the iOS operating system.
Kitploit recommended
 bomberfish/mandela-classic
iOS customization app powered by CVE-2022-46689. No jailbreak required.
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
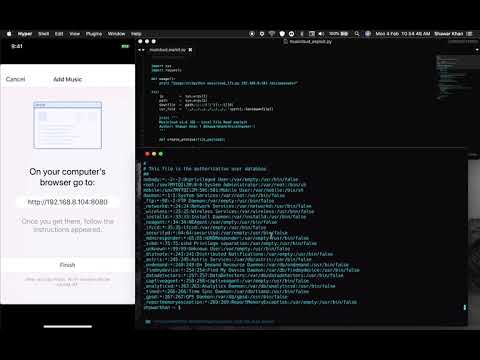 shawarkhanethicalhacker/cve-2019-8389
[CVE-2019-8389] An exploit code for exploiting a local file read vulnerability in Musicloud v1.6 iOS Application
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
 eastarctica/cve-2026-43813
CVE-2026-43813: CloudAttestation enforceEnvironment bypass
 omerporze/toothfairy
CVE-2018-4330 POC for iOS
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC
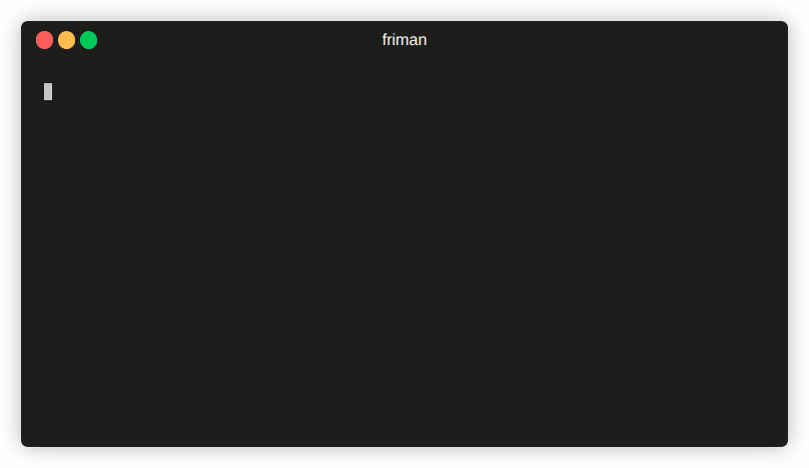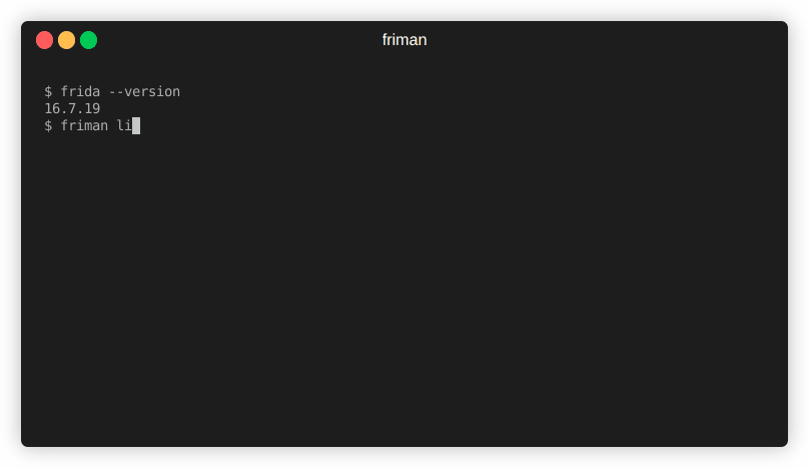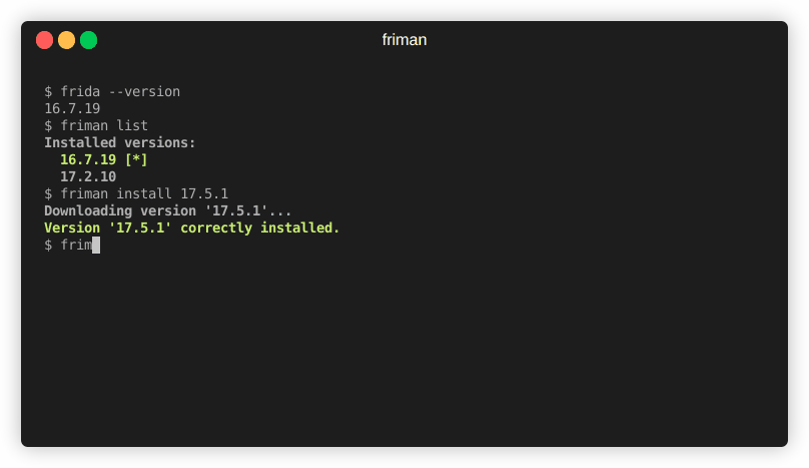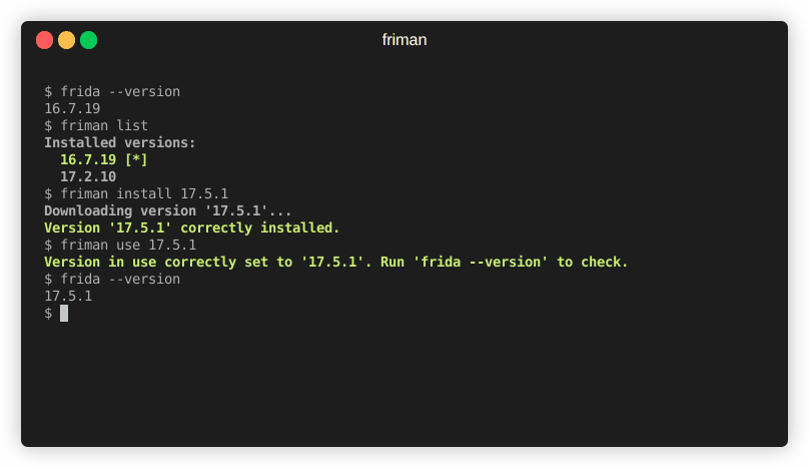 thelicato/friman
Frida version management tool
 acceleratortroll/acceleratortroll
Abusing CVE-2023-28206 to make something useful
 bytev0rtex/cve-2026-65330
Proof-of-concept for a fixed PAC diversifier bypass in the tmpfs setxattr handler on iOS 26.6, demonstrating reachability of the vulnerable signing…
 xcodeon1/ssh-killv2
SSH brute-force tool targeting jailbroken iPhones with default 'alpine' password, featuring network scanning, wordlist-based cracking, and file…
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
 kolbicz/appenumguard
CVE-2025-31207 mitigation and sandboxed tester for rootless and rootHide jailbreaks on iOS 15–18.4.1
 zteeed/cve-2018-4407-ios
POC: Heap buffer overflow in the networking code in the XNU operating system kernel
 jan0/isslfix
CVE-2011-0228 fix for older idevices/firmwares
 spiderlabs/twsl2011-007_ios_code_workaround
Workaround for the vulnerability identified by TWSL2011-007 or CVE-2008-0228 - iOS x509 Certificate Chain Validation Vulnerability