
 #1
Tools for managing, sharing, and integrating Indicators of Compromise (IOCs) into security defenses.
Kitploit recommended

 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…
 capacitorset/box-js
A tool for studying JavaScript malware.
 akamai/akamai-security-research
This repository includes code and IoCs that are the product of research done in Akamai's various security research teams.
 executemalware/malware-iocs
Curated collection of indicators of compromise extracted from real-world malware investigations, including hashes, domains, and IPs for threat…
 ncsc-nl/openssl-2022
Operational information regarding CVE-2022-3602 and CVE-2022-3786, two vulnerabilities in OpenSSL 3
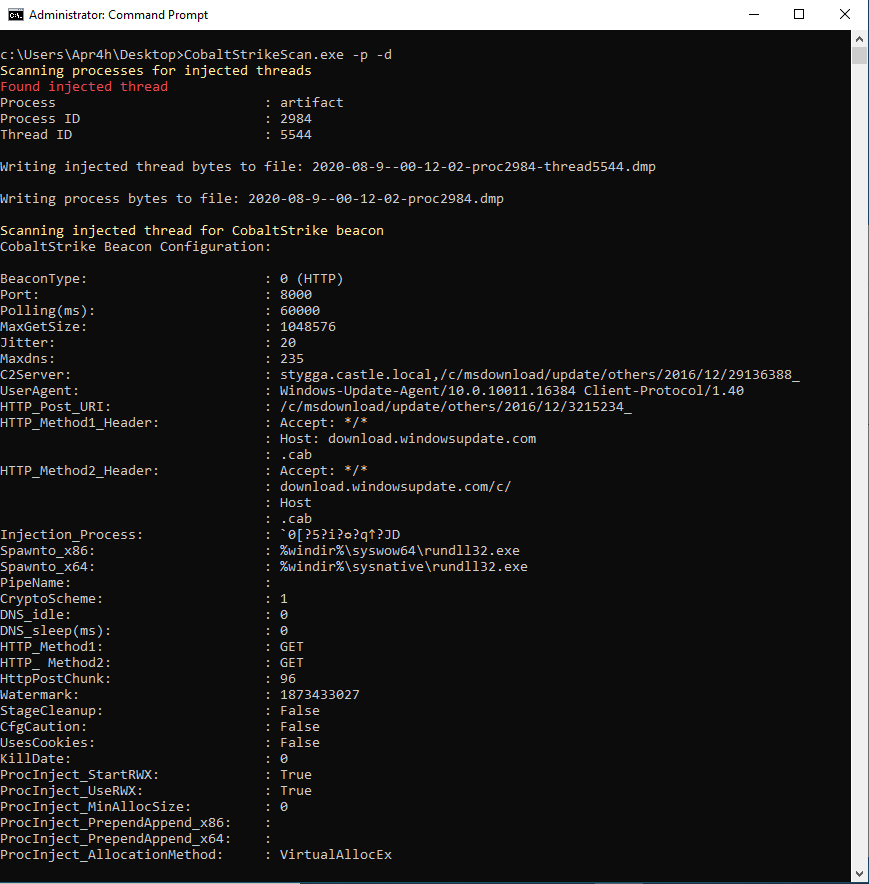 apr4h/cobaltstrikescan
Scan files or process memory for CobaltStrike beacons and parse their configuration
 biggiesmallsag/nighthawkresponse
Incident Response Forensic Framework
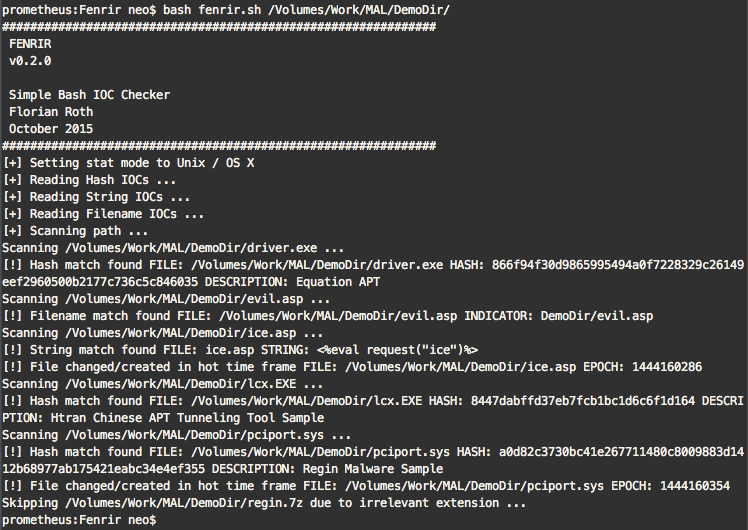
 neo23x0/loki-rs
🐍 High-performance, multi-threaded YARA & IOC scanner
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 back2root/log4shell-rex
PCRE RegEx matching Log4Shell CVE-2021-44228 IOC in your logs
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 toborrm9/malicious_extension_sentry
Malicious Extension Database
 trustedsec/artillery
Open-source blue team tool that protects Linux and Windows systems using multiple host and network defense and detection methods.
 pedramamini/iocextract
Defanged Indicator of Compromise (IOC) Extractor.
 qeeqbox/analyzer
Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 misp/misp-objects
Curated JSON object templates that define MISP attributes and relationship types for structured threat intelligence sharing and interoperable IOC…








