
 #1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…
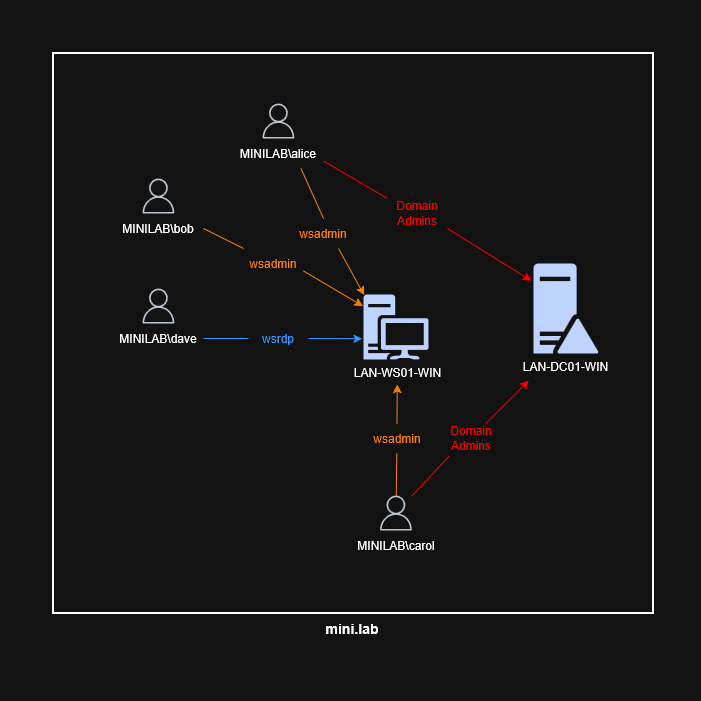 0xmr007/lab4purplesec
Lab4PurpleSec is a modular Purple Team homelab combining a vulnerable Active Directory environment (GOAD), a Docker-based web DMZ, pfSense +…
 wipi-hunter/pikarma
📡🍓🍍 Detects wireless network attacks performed by KARMA module (fake AP). Starts deauthentication attack (for fake access points)
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 the-dfir-report/sigma-rules
Rules generated from our investigations.
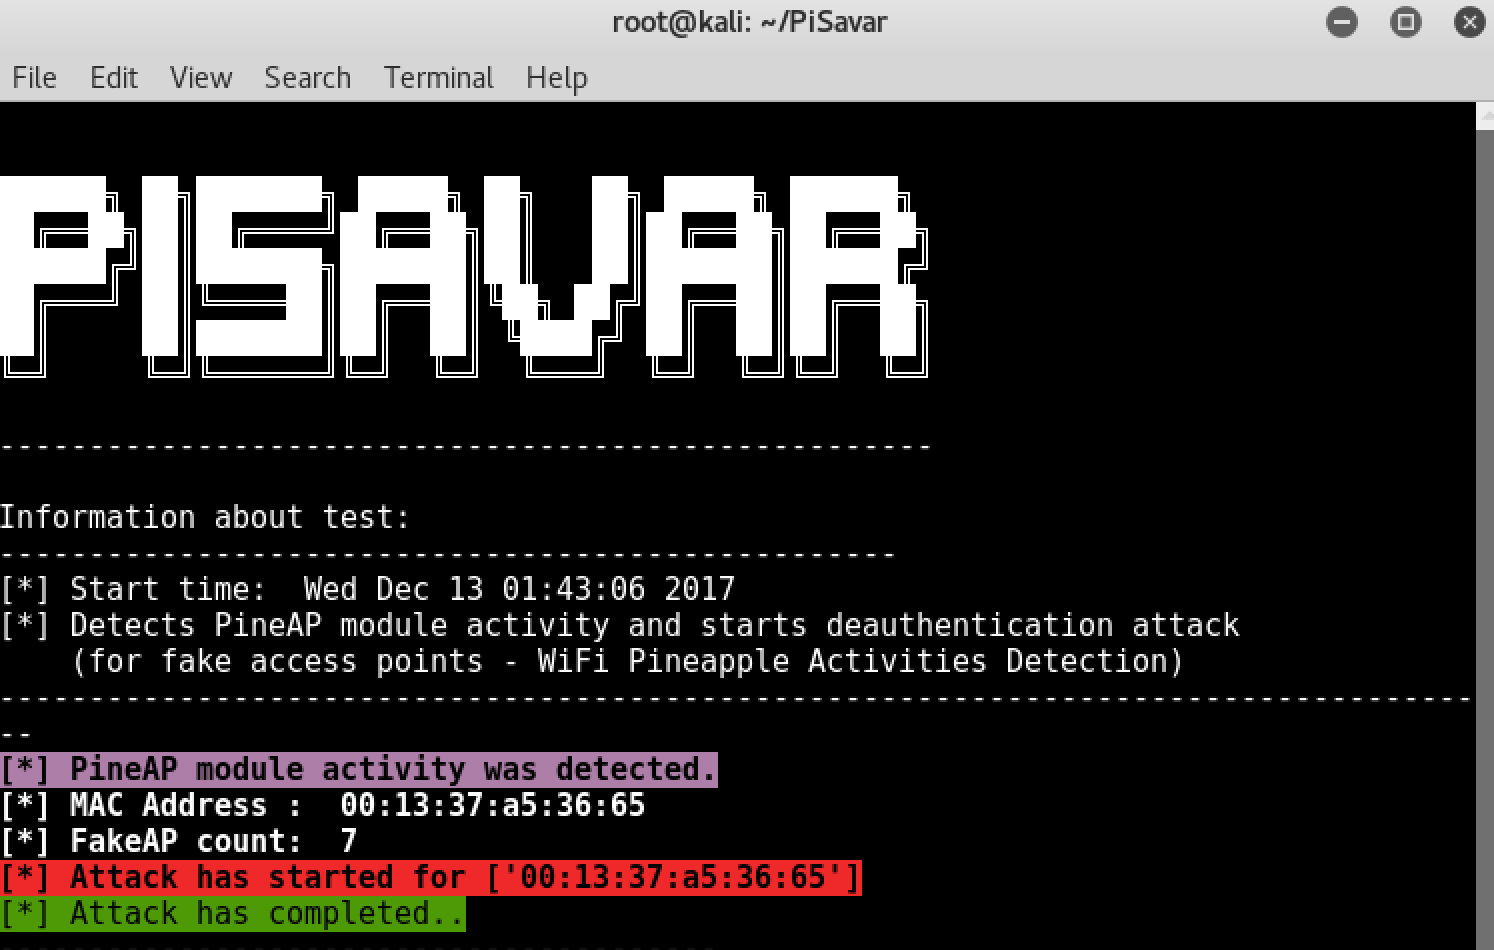 wipi-hunter/pisavar
📡 🍍Detects activities of PineAP module and starts deauthentication attack (for fake access points - WiFi Pineapple Activities Detection)
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks
 travisbgreen/hunting-rules
Suricata rules for network anomaly detection
 benjeems/packetstrider
A network packet forensics tool for SSH
 cisco-talos/deceive
DECeption with Evaluative Integrated Validation Engine (DECEIVE): Let an LLM do all the hard honeypot work!
 joesecurity/sigma-rules
Sigma rules from Joe Security
 pe3zx/crowdstrike-falcon-queries
A collection of Splunk's Search Processing Language (SPL) for Threat Hunting with CrowdStrike Falcon
 teler-sh/teler-waf
teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…
 stamparm/tsusen
Network traffic sensor
 hpfeeds/hpfeeds
Honeynet Project generic authenticated datafeed protocol
 ohmyadd/wetland
A high interaction SSH honeypot
 advanced-threat-research/cve-2020-16898
CVE-2020-16898 (Bad Neighbor) Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 ttlab-research/awesome-wazuh
🛡️Awesome lists about all kinds of interesting topics of Wazuh XDR/SIEM








