
 #1
IDS/IPS systems, network monitoring, anomaly-based detection, and threat alerting tools.
Kitploit recommended
 yili-soc/vm-homelab-log4shell-assessment
Full-lifecycle vulnerability management on a live Log4Shell (CVE-2021-44228) target — scan, manual exploitation, network detection, and remediation…
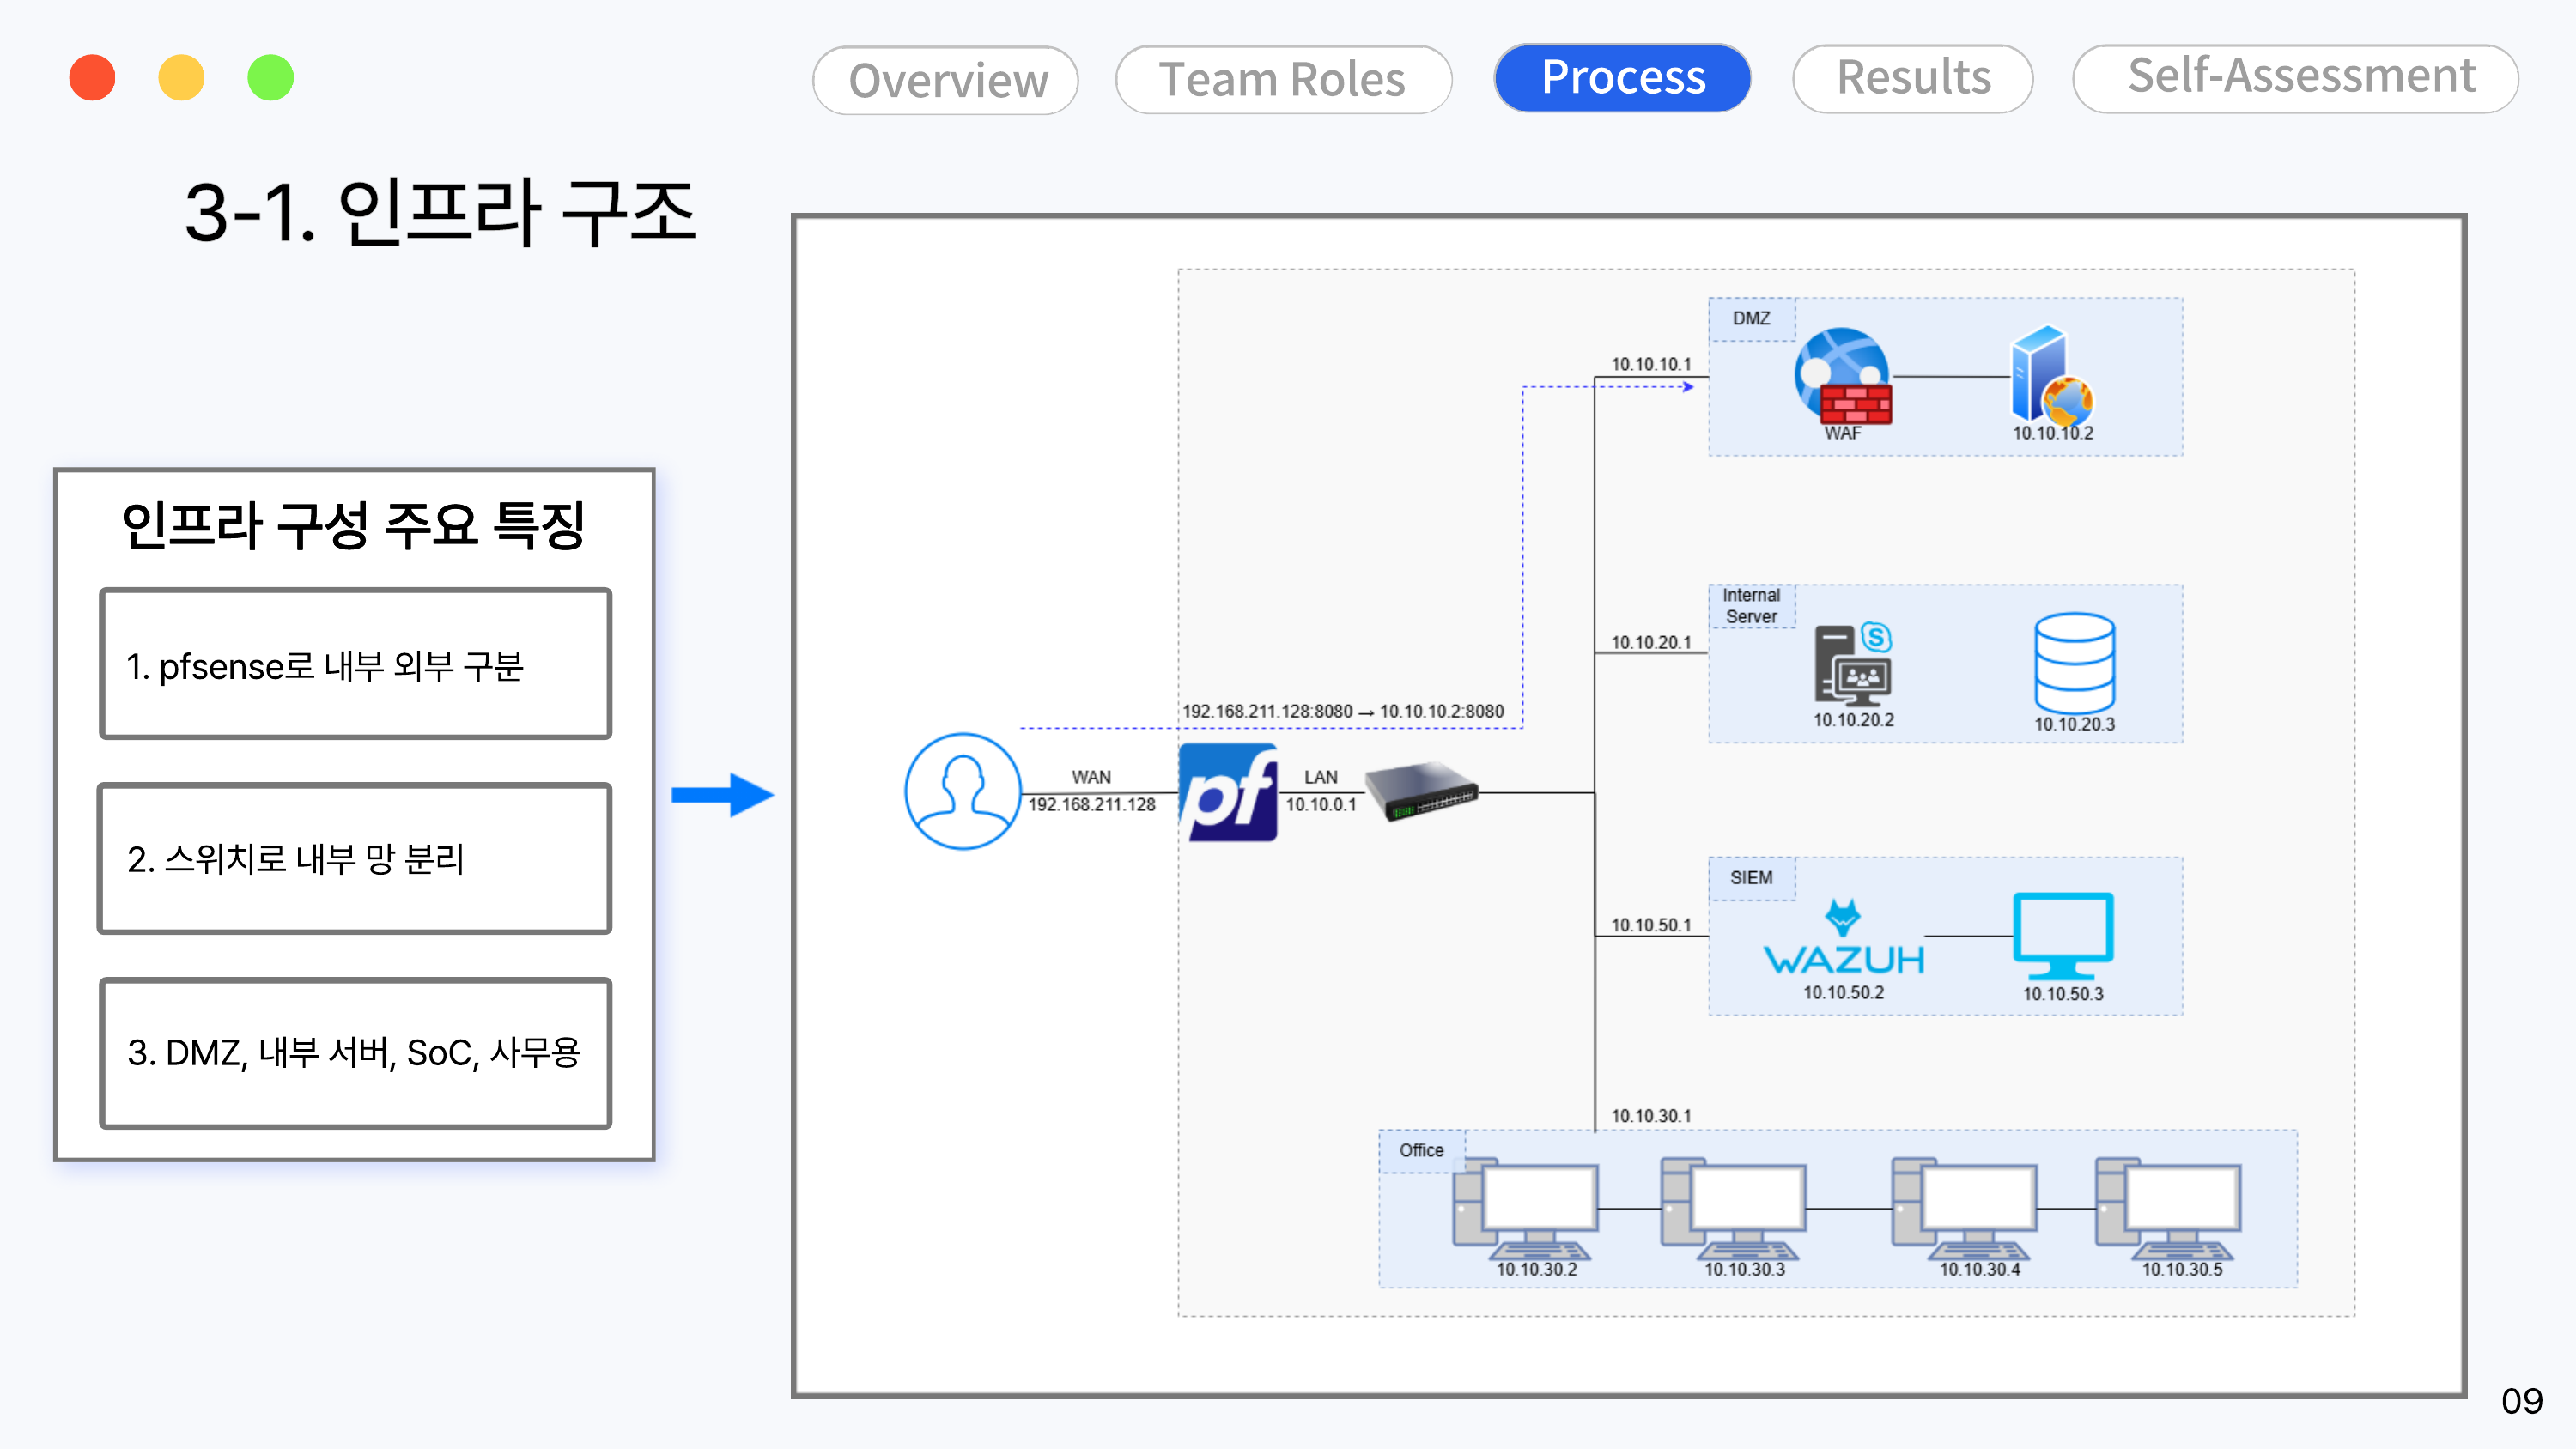 kevin9480/security_incident_report
React2Shell(CVE-2025-55182) 취약점 기반 침해 시나리오를 재현하고, Wazuh/Sysmon/Coraza WAF 로그로 침해사고를 분석·대응한 DFIR 프로젝트
 chpratik/nginx_2026_cve_bundle_cti_report
Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533
 mfarshad-abdullah-khan/cve-2025-53770-research
🚨 Threat intel & incident response research on SharePoint "ToolShell" RCE zero-day (CVE-2025-53770). 🕵️♂️ Covers root-cause deserialization flaws,…
 nabhan-mohy/dirty-frag-research-cve-2026-43284-
Comprehensive technical research on CVE-2026-43284 (Dirty Frag), including Linux kernel internals, root cause analysis, patch analysis, detection…
 millikanjohnl-blip/dirtyfrag-detection-rules
Detection rules and analysis for Dirty Frag (CVE-2026-43284/CVE-2026-43500) Linux kernel LPE vulnerability. Based on community research and health…
 1-bit-wonder/kestrel
Single-host runtime-security dashboard on eBPF — Go agent + SvelteKit. Live process tree, network map, and rule-based alerts for plain Linux hosts.
 dorser/cve-2024-21626
Educational demo of CVE-2024-21626 runc container escape with eBPF-based detection gadget for exploitation attempts.
 atlasvector/certighost-cve-2026-54121
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…
 m5050/cve-2019-0604
CVE-2019-0604: SharePoint RCE detection rules and sample PCAP
 elihiho/security-operations-labs
Threat Modeling, IT-/OT-Segmentierung, Snort Detection und reproduzierbare Validierung eines Drupal-Detection-Profils.
 glebusalt/cybersecurity_portfolio
Практические кейсы по информационной безопасности: развёртывание SIEM Wazuh и эксплуатация CVE-2021-41773
 michael-kanda/wp2shell-ioc-scanner
Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…
 h7hac9/cve-2020-1938
Suricata and Bro detection rules for CVE-2020-1938 (Ghostcat) Tomcat AJP file read vulnerability, enabling network-level monitoring and alerting.
 jdinovo/spade
SPaT Attack Detection and Evaluation dataset
 rickgeex/cve-2025-5777-citrixbleed
CitrixBleed-2 (CVE-2025-5777) – proof-of-concept exploit for NetScaler ADC/Gateway “memory bleed”
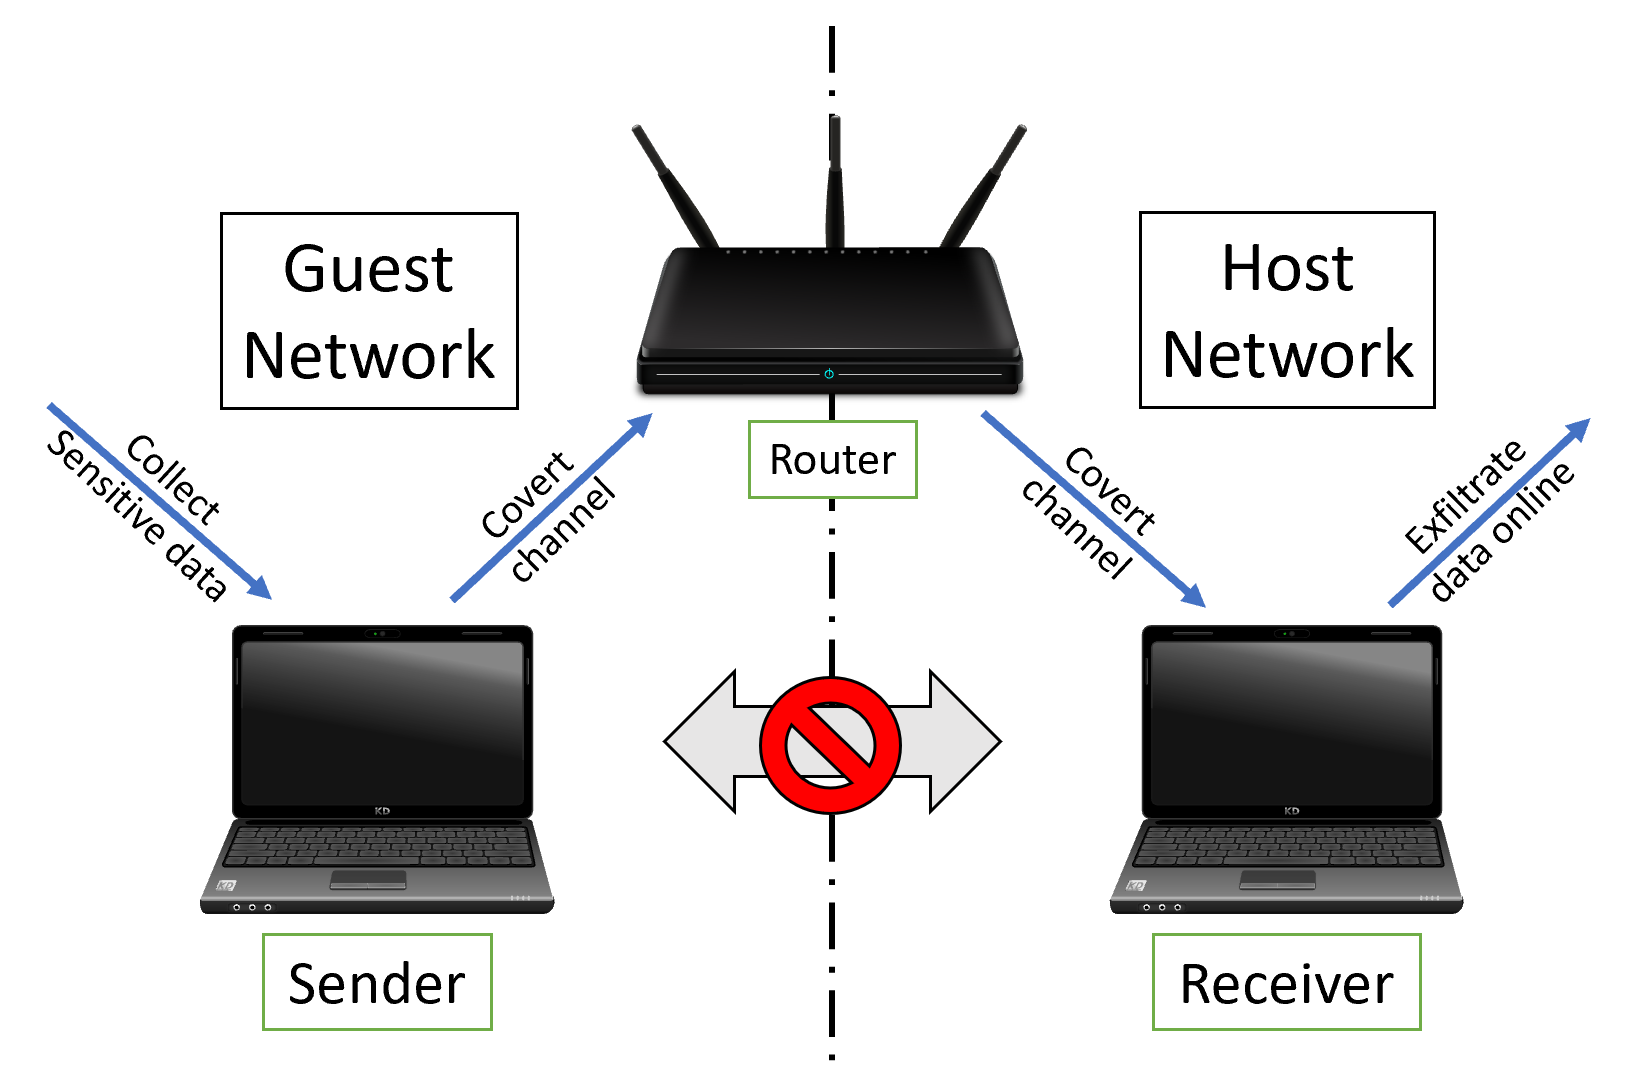 orensv/characterization-and-detection-of-cross-router-covert-channels
This repository includes the source code used in the "Characterization and Detection of Cross-Router Covert Channels" paper.
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…








