
 #1
General purpose tools for collecting various types of information about targets.
Kitploit recommended
 quantika14/osint-suite-tools
Repositorio del conjunto de herramientas para hacer OSINT y SOCMINT con Dante's Gates Minimal Version.
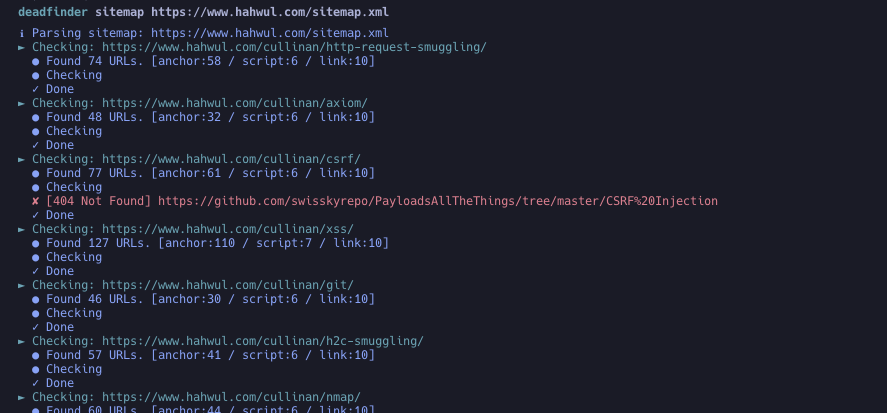 hahwul/deadfinder
Fast CLI tool to scan websites, sitemaps, and URL lists for broken links, with concurrent workers, coverage reporting, and multiple output formats.
 andromeda1957/netpwn
Tool made to automate tasks of pentesting.
 tismayil/ohmybackup
Scan Victim Backup Directories & Backup Files
 ebryx/gitdump
A pentesting tool that dumps the source code from .git even when the directory traversal is disabled
 b3rito/peeko
peeko – Browser-based XSS C2 for stealthy internal network exploration via infected browser.
 projectdiscovery/useragent
Curated list of categorized User Agents
 shivamrai2003/reconky-automated_bash_script
Reconky is an great Content Discovery bash script for bug bounty hunters which automate lot of task and organized in the well mannered form which…
 luemmelsec/apex
Azure Post Exploitation Framework
 whxitte/white-deface
This is a simple python tool to automatically deface webdav vulnerable websites.
 0xshe/fuck-cdn
Automated CDN origin-IP discovery skill for Claude Code that runs 40+ prioritized OSINT methods, cross-validates candidates via SSL and HTTP…
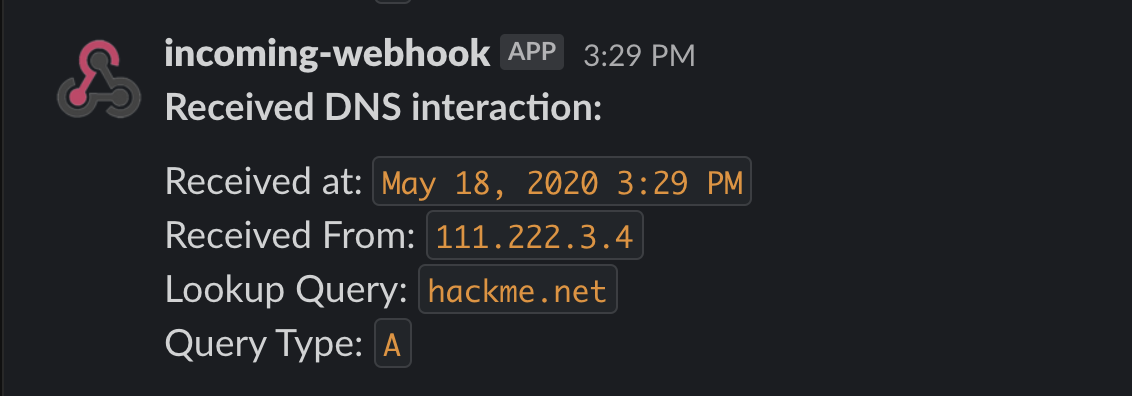 allyomalley/dnsobserver
A handy DNS service written in Go to aid in the detection of several types of blind vulnerabilities. It monitors a pentester's server for out-of-band…
 tothi/servicedetector
Detect whether a service is installed (blindly) and/or running (if exposing named pipes) on a remote machine without using local admin privileges.
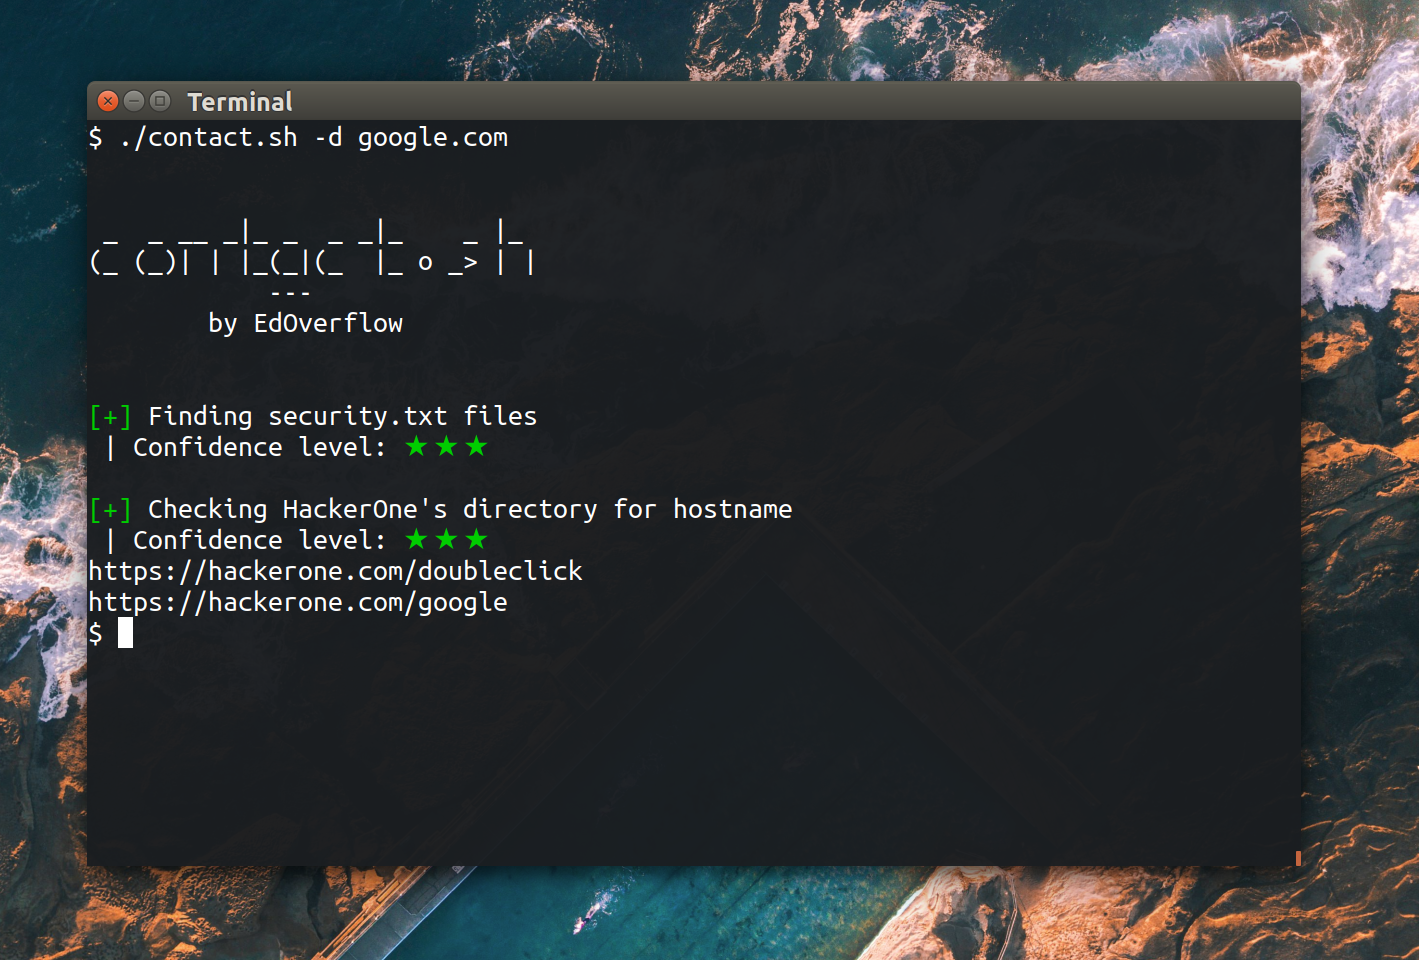 edoverflow/contact.sh
An OSINT tool to find contacts in order to report security vulnerabilities.
 codingo/dorky
A tool to quickly do keyword searches over Gitlab and Github for OSINT & bug bounty recon
 ctxis/snitchdns
Database Driven DNS Server with a Web UI
 daffainfo/oneliner-bugbounty
A collection oneliner scripts for bug bounty
 nvisosecurity/pycobalthound
pyCobaltHound is an Aggressor script extension for Cobalt Strike which aims to provide a deep integration between Cobalt Strike and Bloodhound.








