
 #1
General purpose tools for collecting various types of information about targets.
Kitploit recommended
 josehelps/git-wild-hunt
A tool to hunt for credentials in github wild AKA git*hunt
 owasp/d4n155
OWASP D4N155 - Intelligent and dynamic wordlist using OSINT
 puliczek/cve-2022-0337-poc-google-chrome-microsoft-edge-opera
🎩 🤟🏻 [P1-$10,000] Google Chrome, Microsoft Edge and Opera - vulnerability reported by Maciej Pulikowski - System environment variables leak -…
 dark-warlord14/jsscanner
You can read the writeup on this script here
 capture0x/lfi-space
Automated Local File Inclusion (LFI) vulnerability scanner with Google Dork search and targeted URL scan modes for web application security testing.

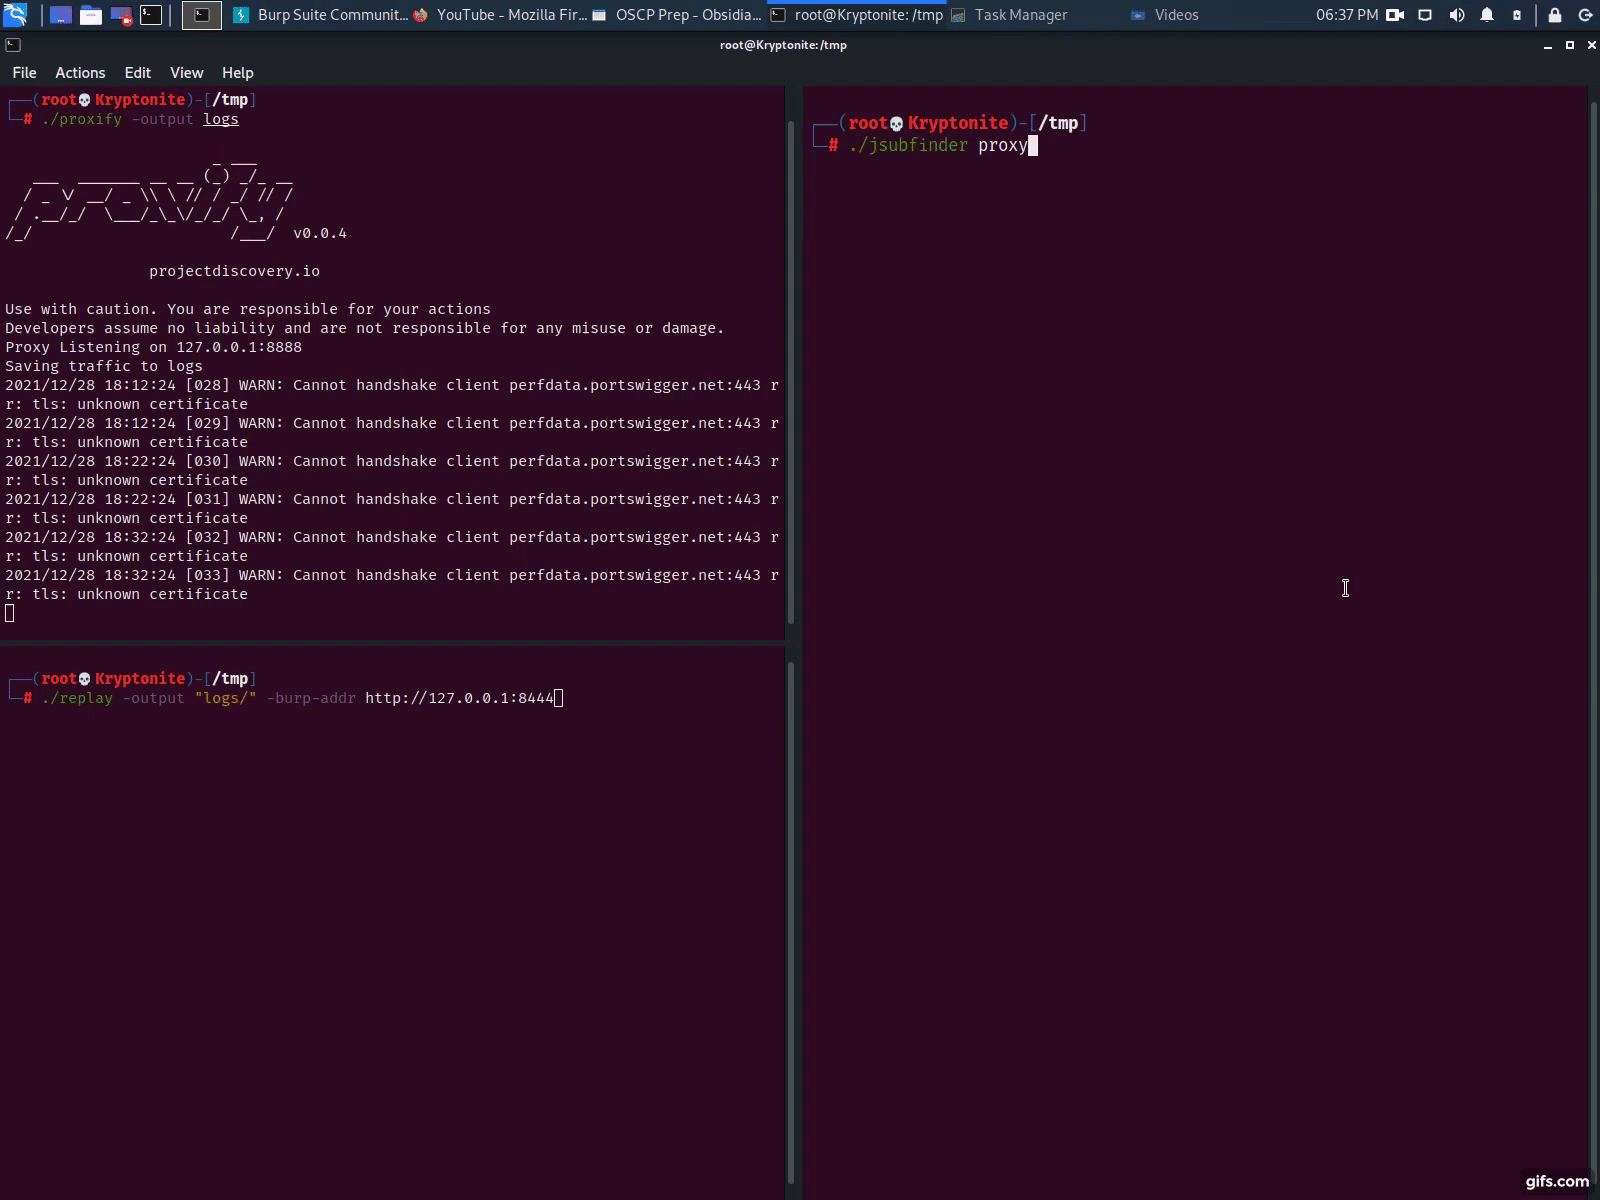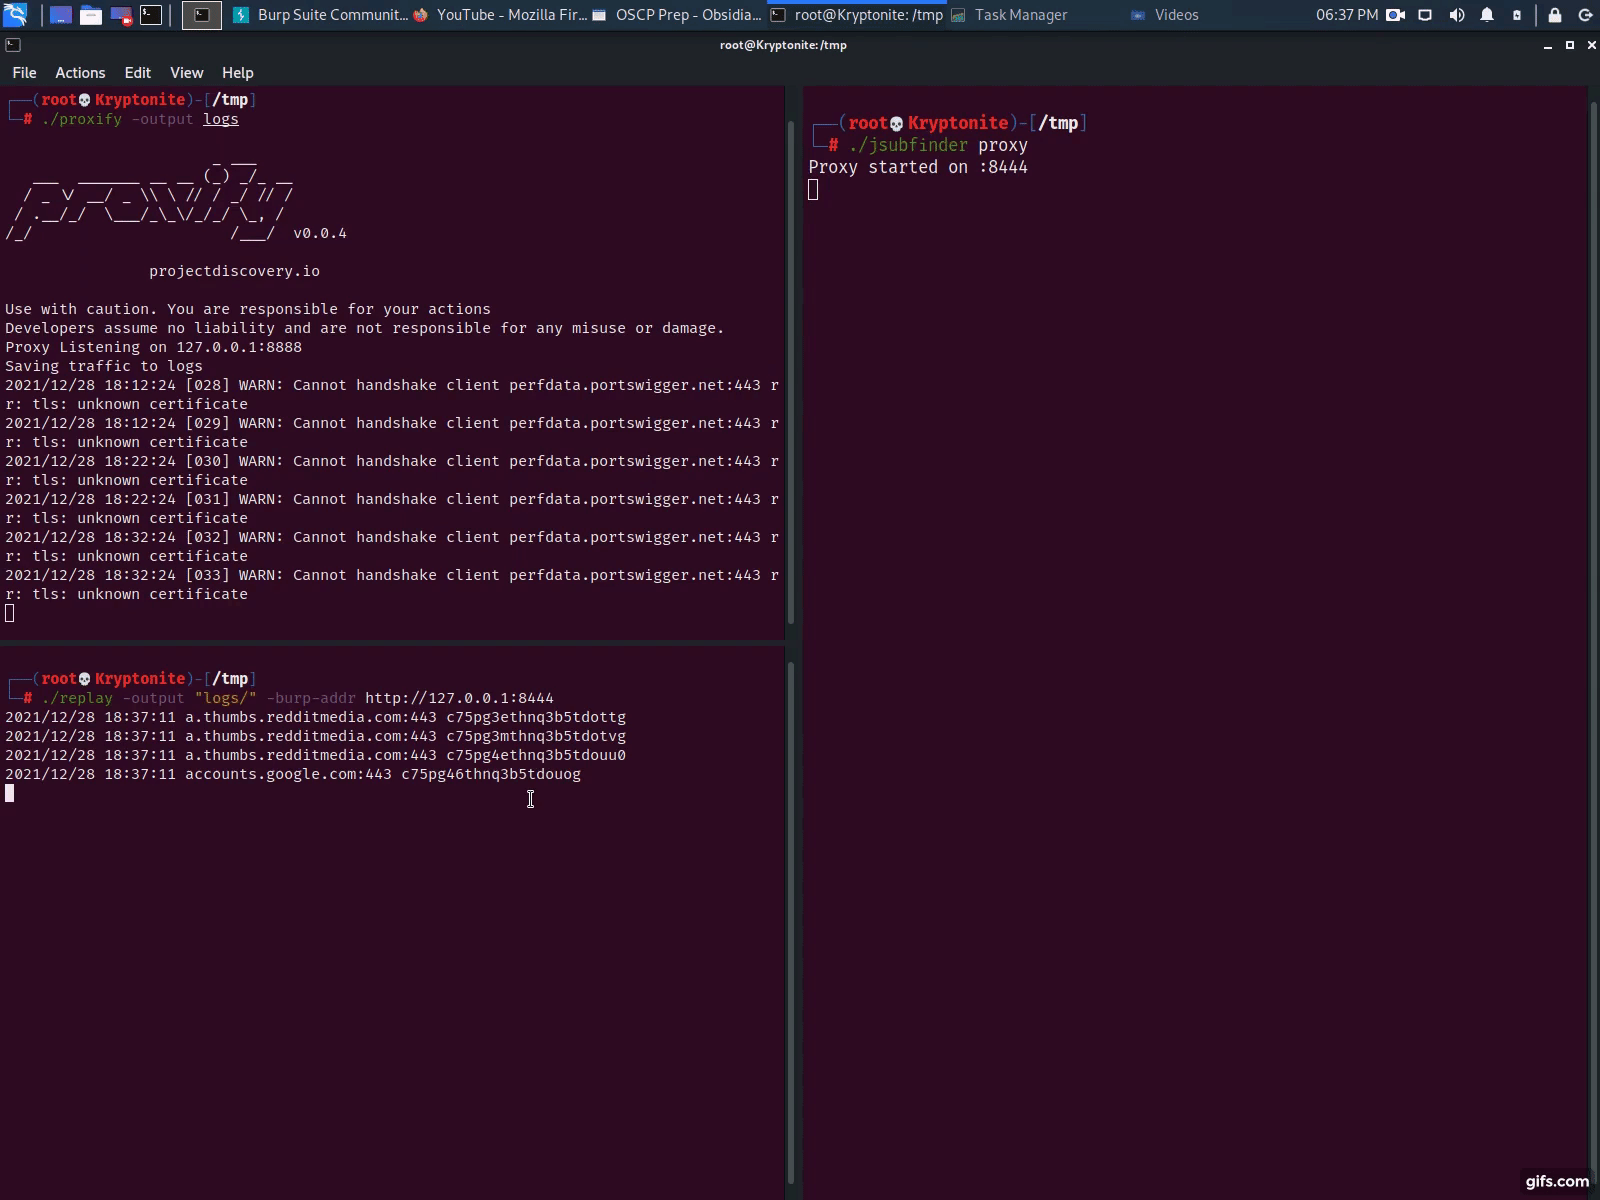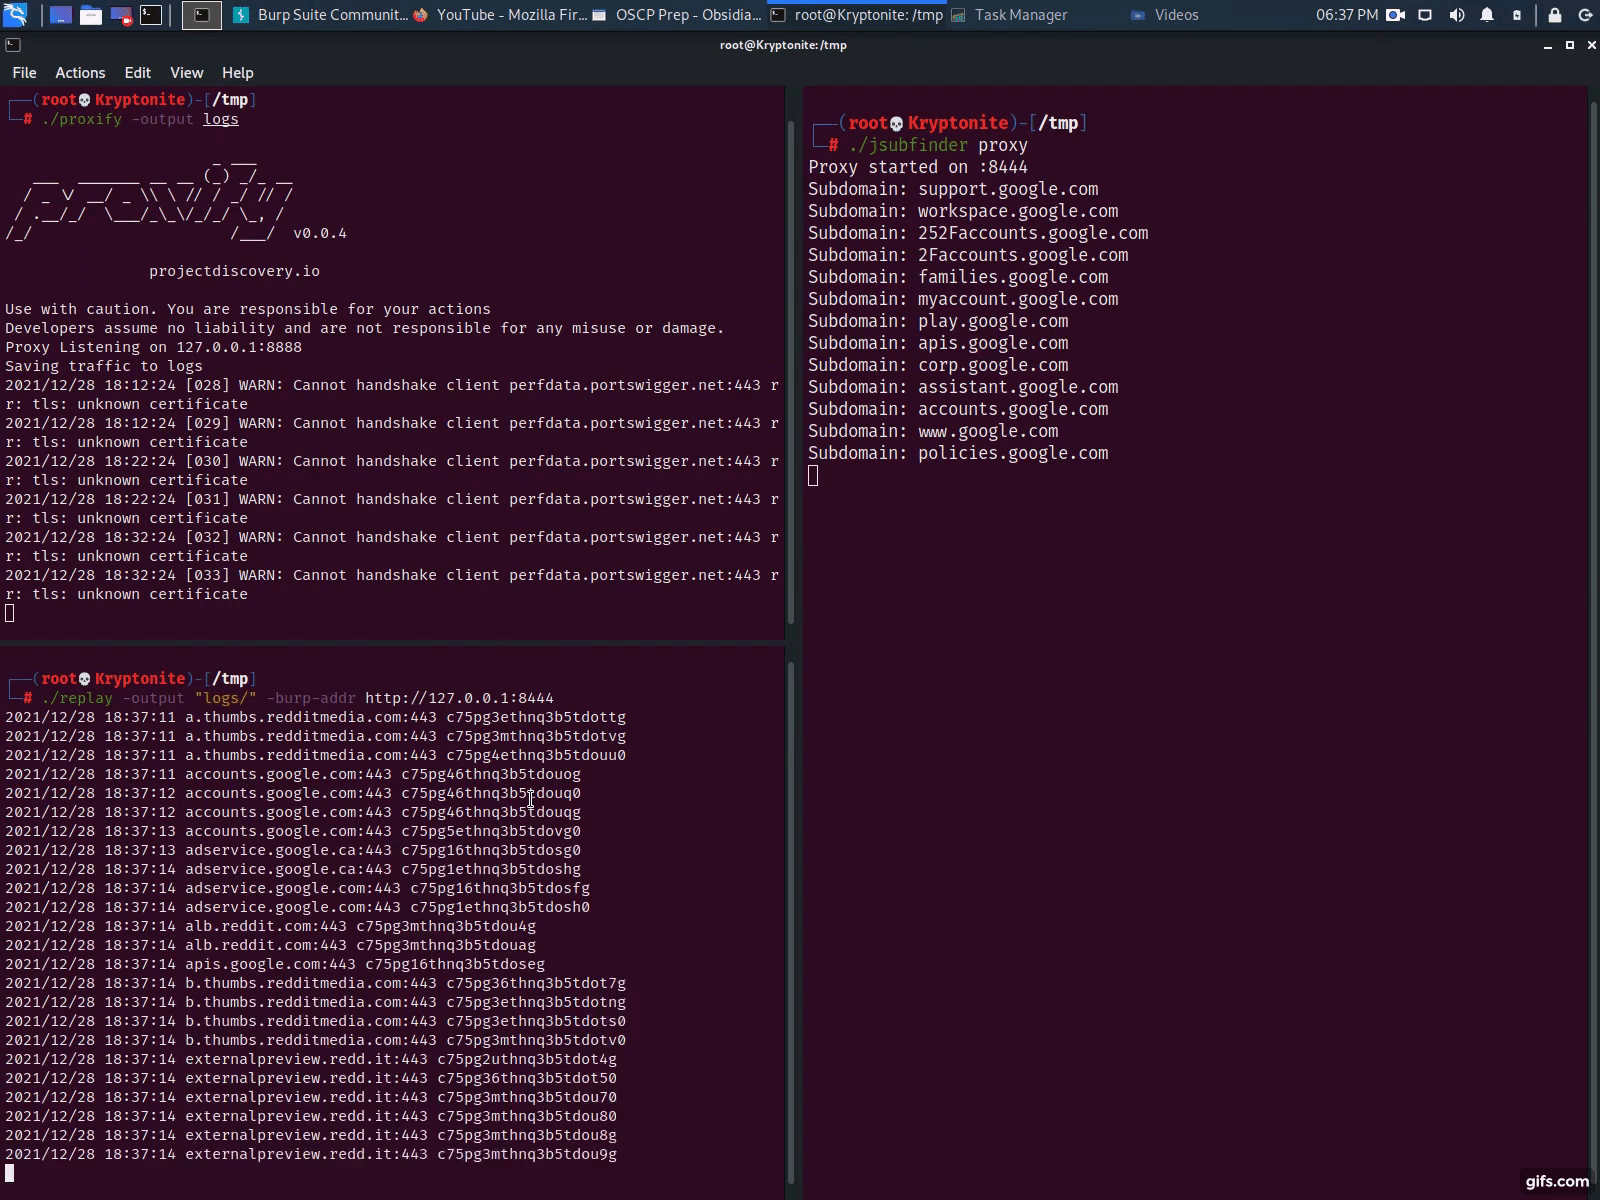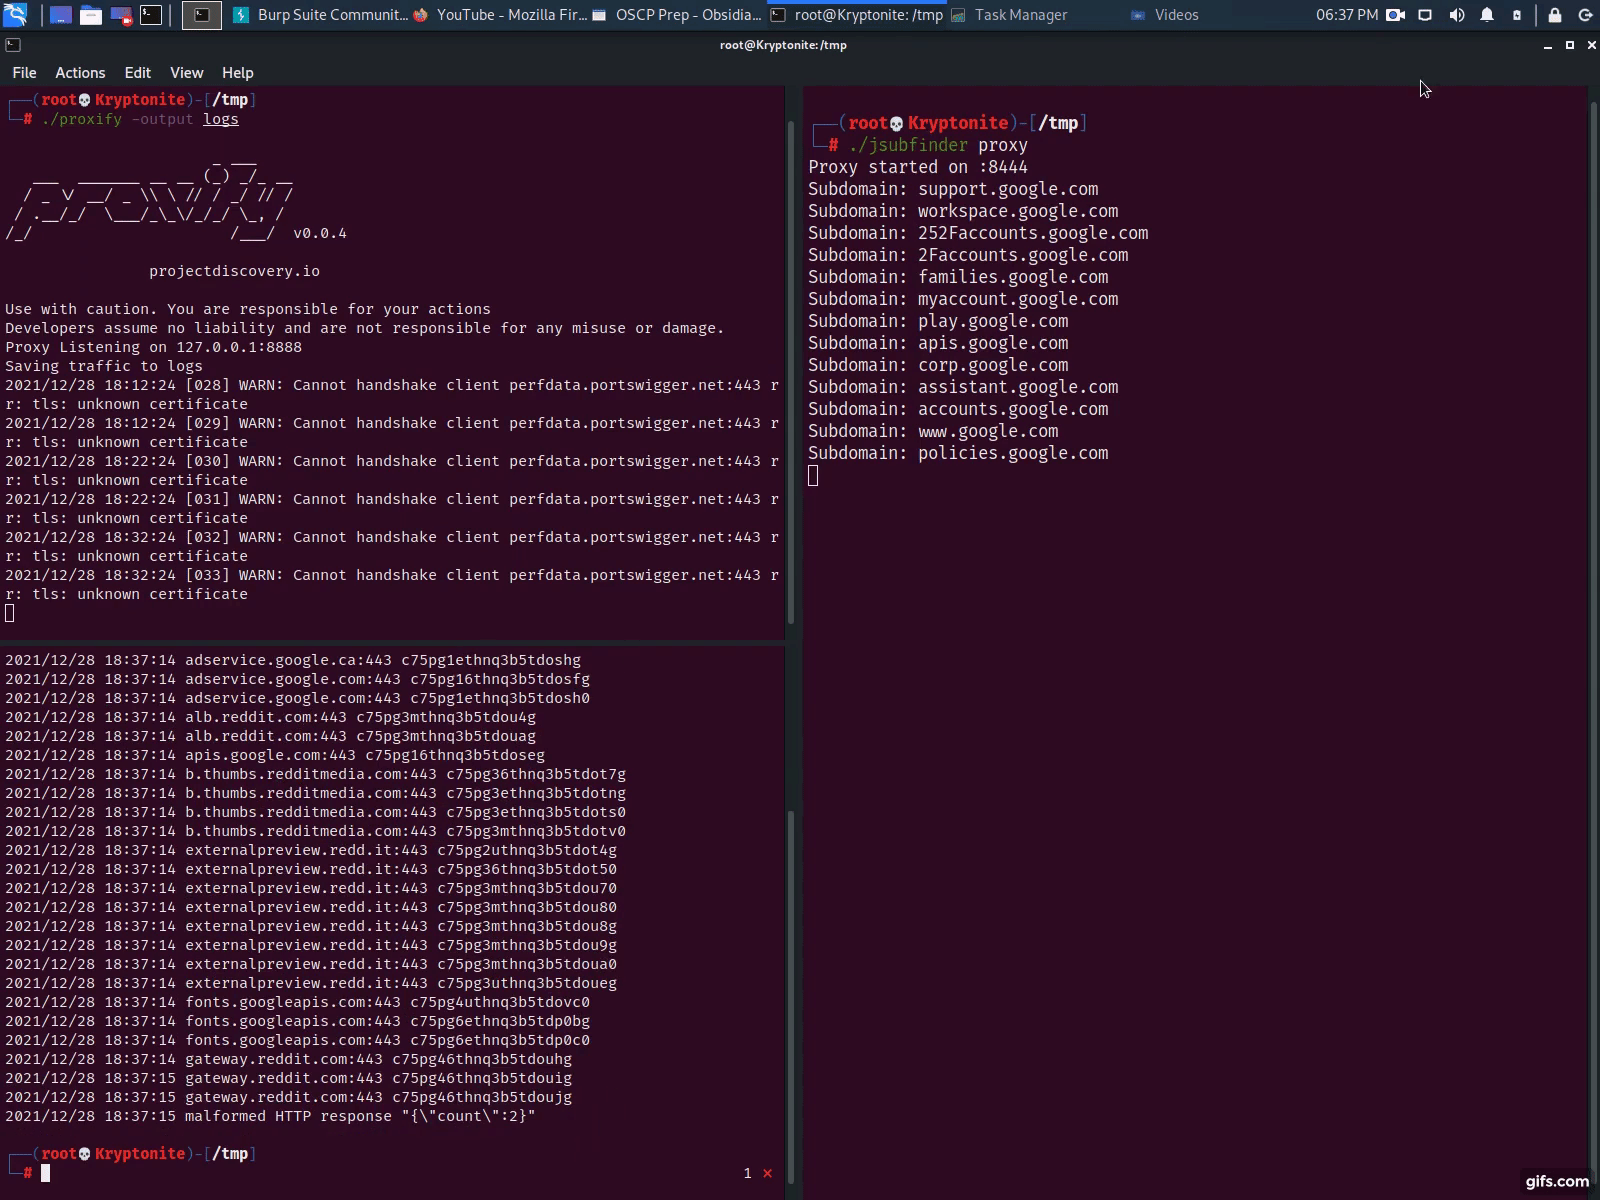 threatunknown/jsubfinder
Go-based tool that scans webpages and JavaScript files to discover hidden subdomains and secrets, with optional crawling and real-time proxy analysis…
 aydinnyunus/exiflooter
Extracts geolocation and EXIF metadata from image URLs and directories, with OpenStreetMap integration for mapping GPS coordinates.
 researchanddestroy/dorxng
Next Generation DorX. Built by Dorks, for Dorks. 🤓
 hakluke/haklistgen
Turns any junk text into a usable wordlist for brute-forcing.

 opencybersecurityalliance/kestrel-lang
Kestrel threat hunting language: building reusable, composable, and shareable huntflows across different data sources and threat intel.
 0xdsm/pinkerton
🕵️ Python project to crawl for JavaScript files and search for secrets like API keys, authorization tokens, hardcoded credentials, etc.
 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
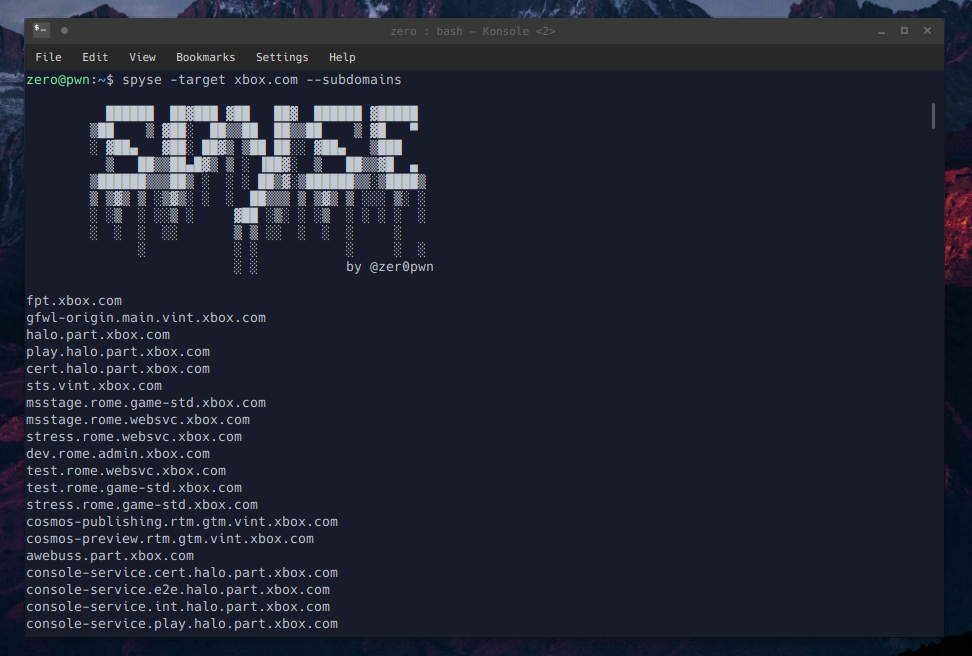 zeropwn/spyse.py
Python API wrapper and command-line client for the tools hosted on spyse.com.
 redeye-framework/redeye
Collaborative pentest data management platform for organizing servers, users, vulnerabilities, attack vectors, and files with API access and graph…
 p0dalirius/extractbitlockerkeys
A system administration or post-exploitation script to automatically extract the bitlocker recovery keys from a domain.
 zxsecurity/steamer
For importing, searching, and managing public password breach data








