
 #1
General purpose tools for collecting various types of information about targets.
Kitploit recommended
 evildevill/devil
Menu-driven shell framework bundling brute-force login attacks, friendlist and profile data harvesting, and automated Facebook account-grabbing…
 justakazh/sicat
Multi-source vulnerability and exploit aggregator with auto-discovery via Nmap and Wappalyzer, searching Exploit-DB, NVD, CVE.org, GitHub, Nuclei,…
 caspergn/activedirectoryenumeration
Enumerate AD through LDAP with a collection of helpfull scripts being bundled
 fleetcaptain/everest-backup-cve-2025-11380
Proof-of-concept exploit for CVE-2025-11380 demonstrating unauthenticated backup access in the Everest Backup WordPress plugin, enabling security…
 expert21/hermes-osint
Hermes — an ephemeral, Docker-powered OSINT framework for testing, tinkering, and secure investigative automation.
 steampunk424/cve-2025-36911-wisper_pair_target_finder
This is not an exploit for CVE-2025-36911!!! This is a detector for finding potentially vulnerable devices! Only use on your own devices! I am not…
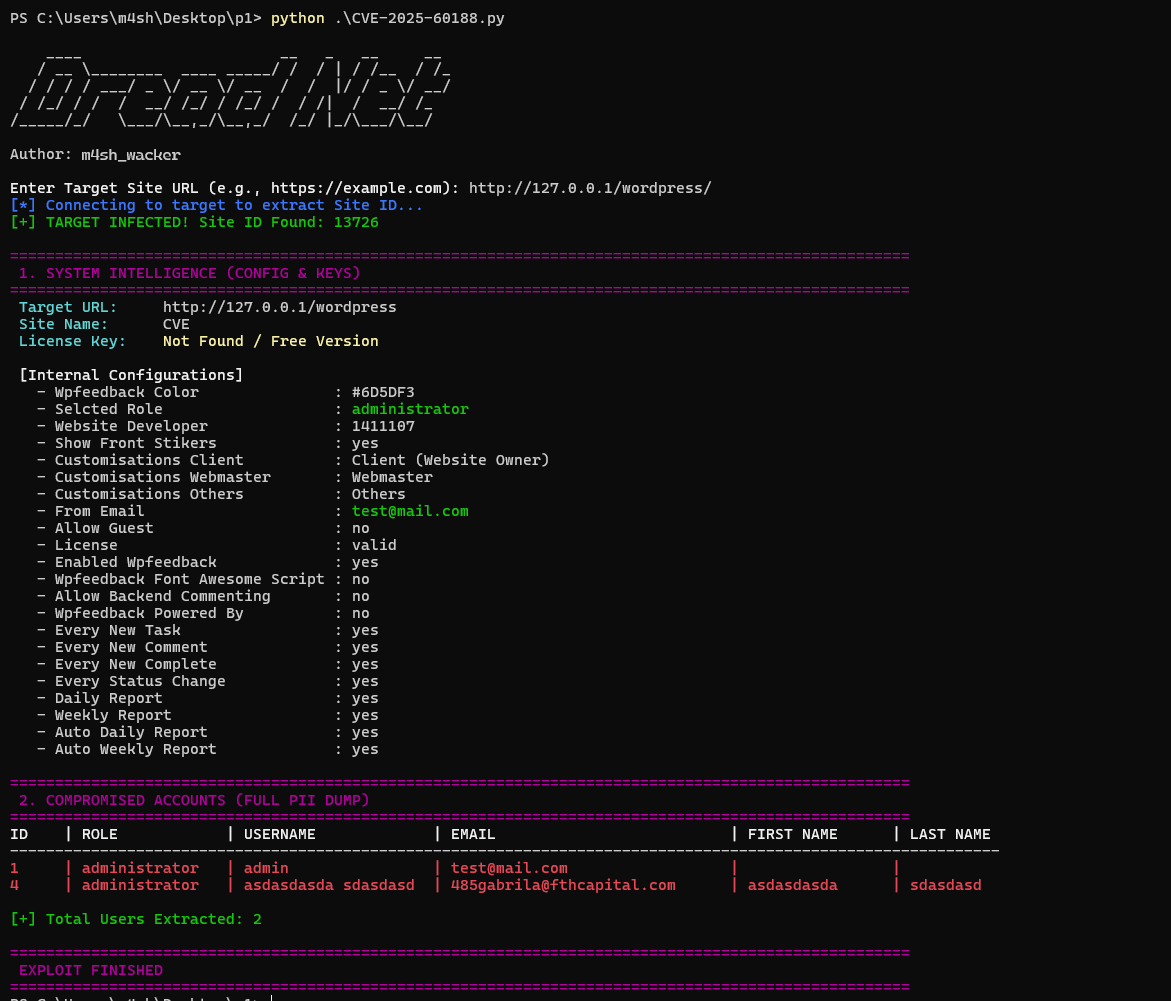 m4sh-wacker/cve-2025-60188-atarim-plugin-exploit
CVE-2025-60188 Atarim Plugin Exploit
 cedric-martz/cve-2025-36911_scan
This script can be used to check if a Bluetooth device is vulnerable to CVE-2025-36911.
 loresuso/psc
the ps utility, with an eBPF twist and container context
 preludeorg/cua-kit
Tools for attacking Computer Use Agents
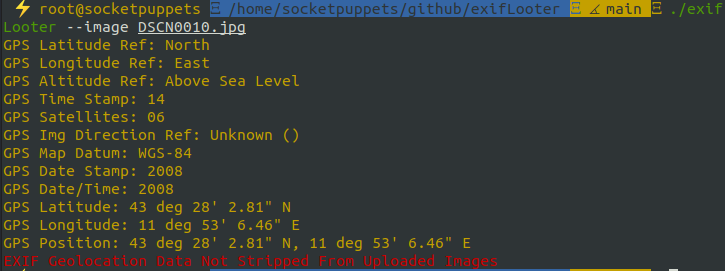 aydinnyunus/exiflooter
Extracts geolocation and EXIF metadata from image URLs and directories, with OpenStreetMap integration for mapping GPS coordinates.
 rivek619/cve-2025-69581
An issue was discovered in Chamillo LMS 1.11.2. The Social Network /personal_data endpoint exposes full sensitive user information even after logout…
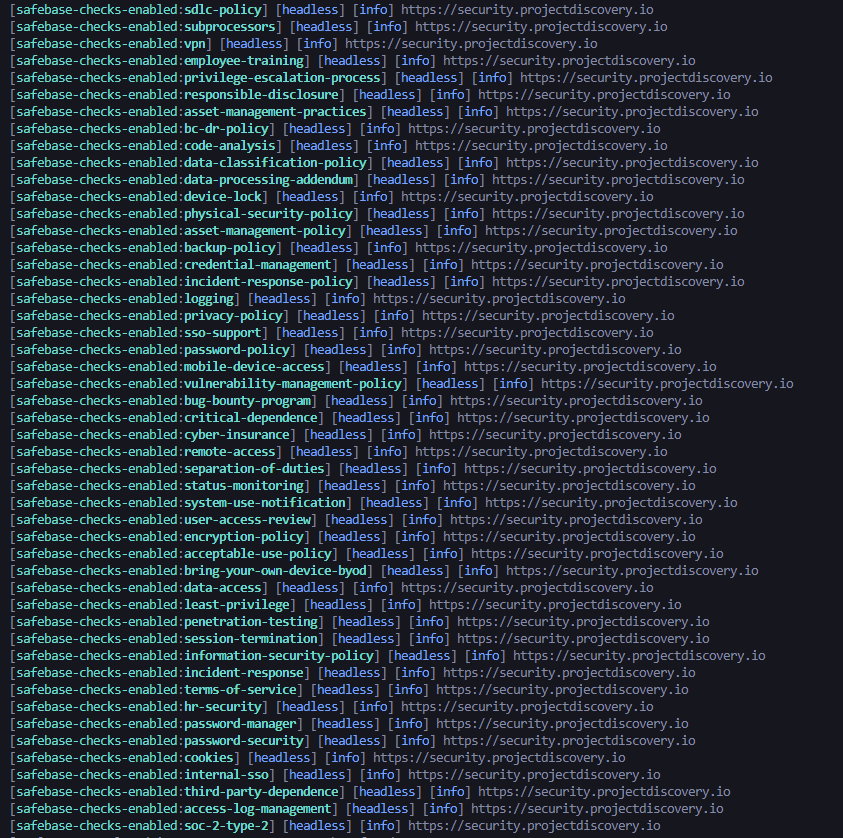 rxerium/internal-security-detect
The detection of internal security controls at a company
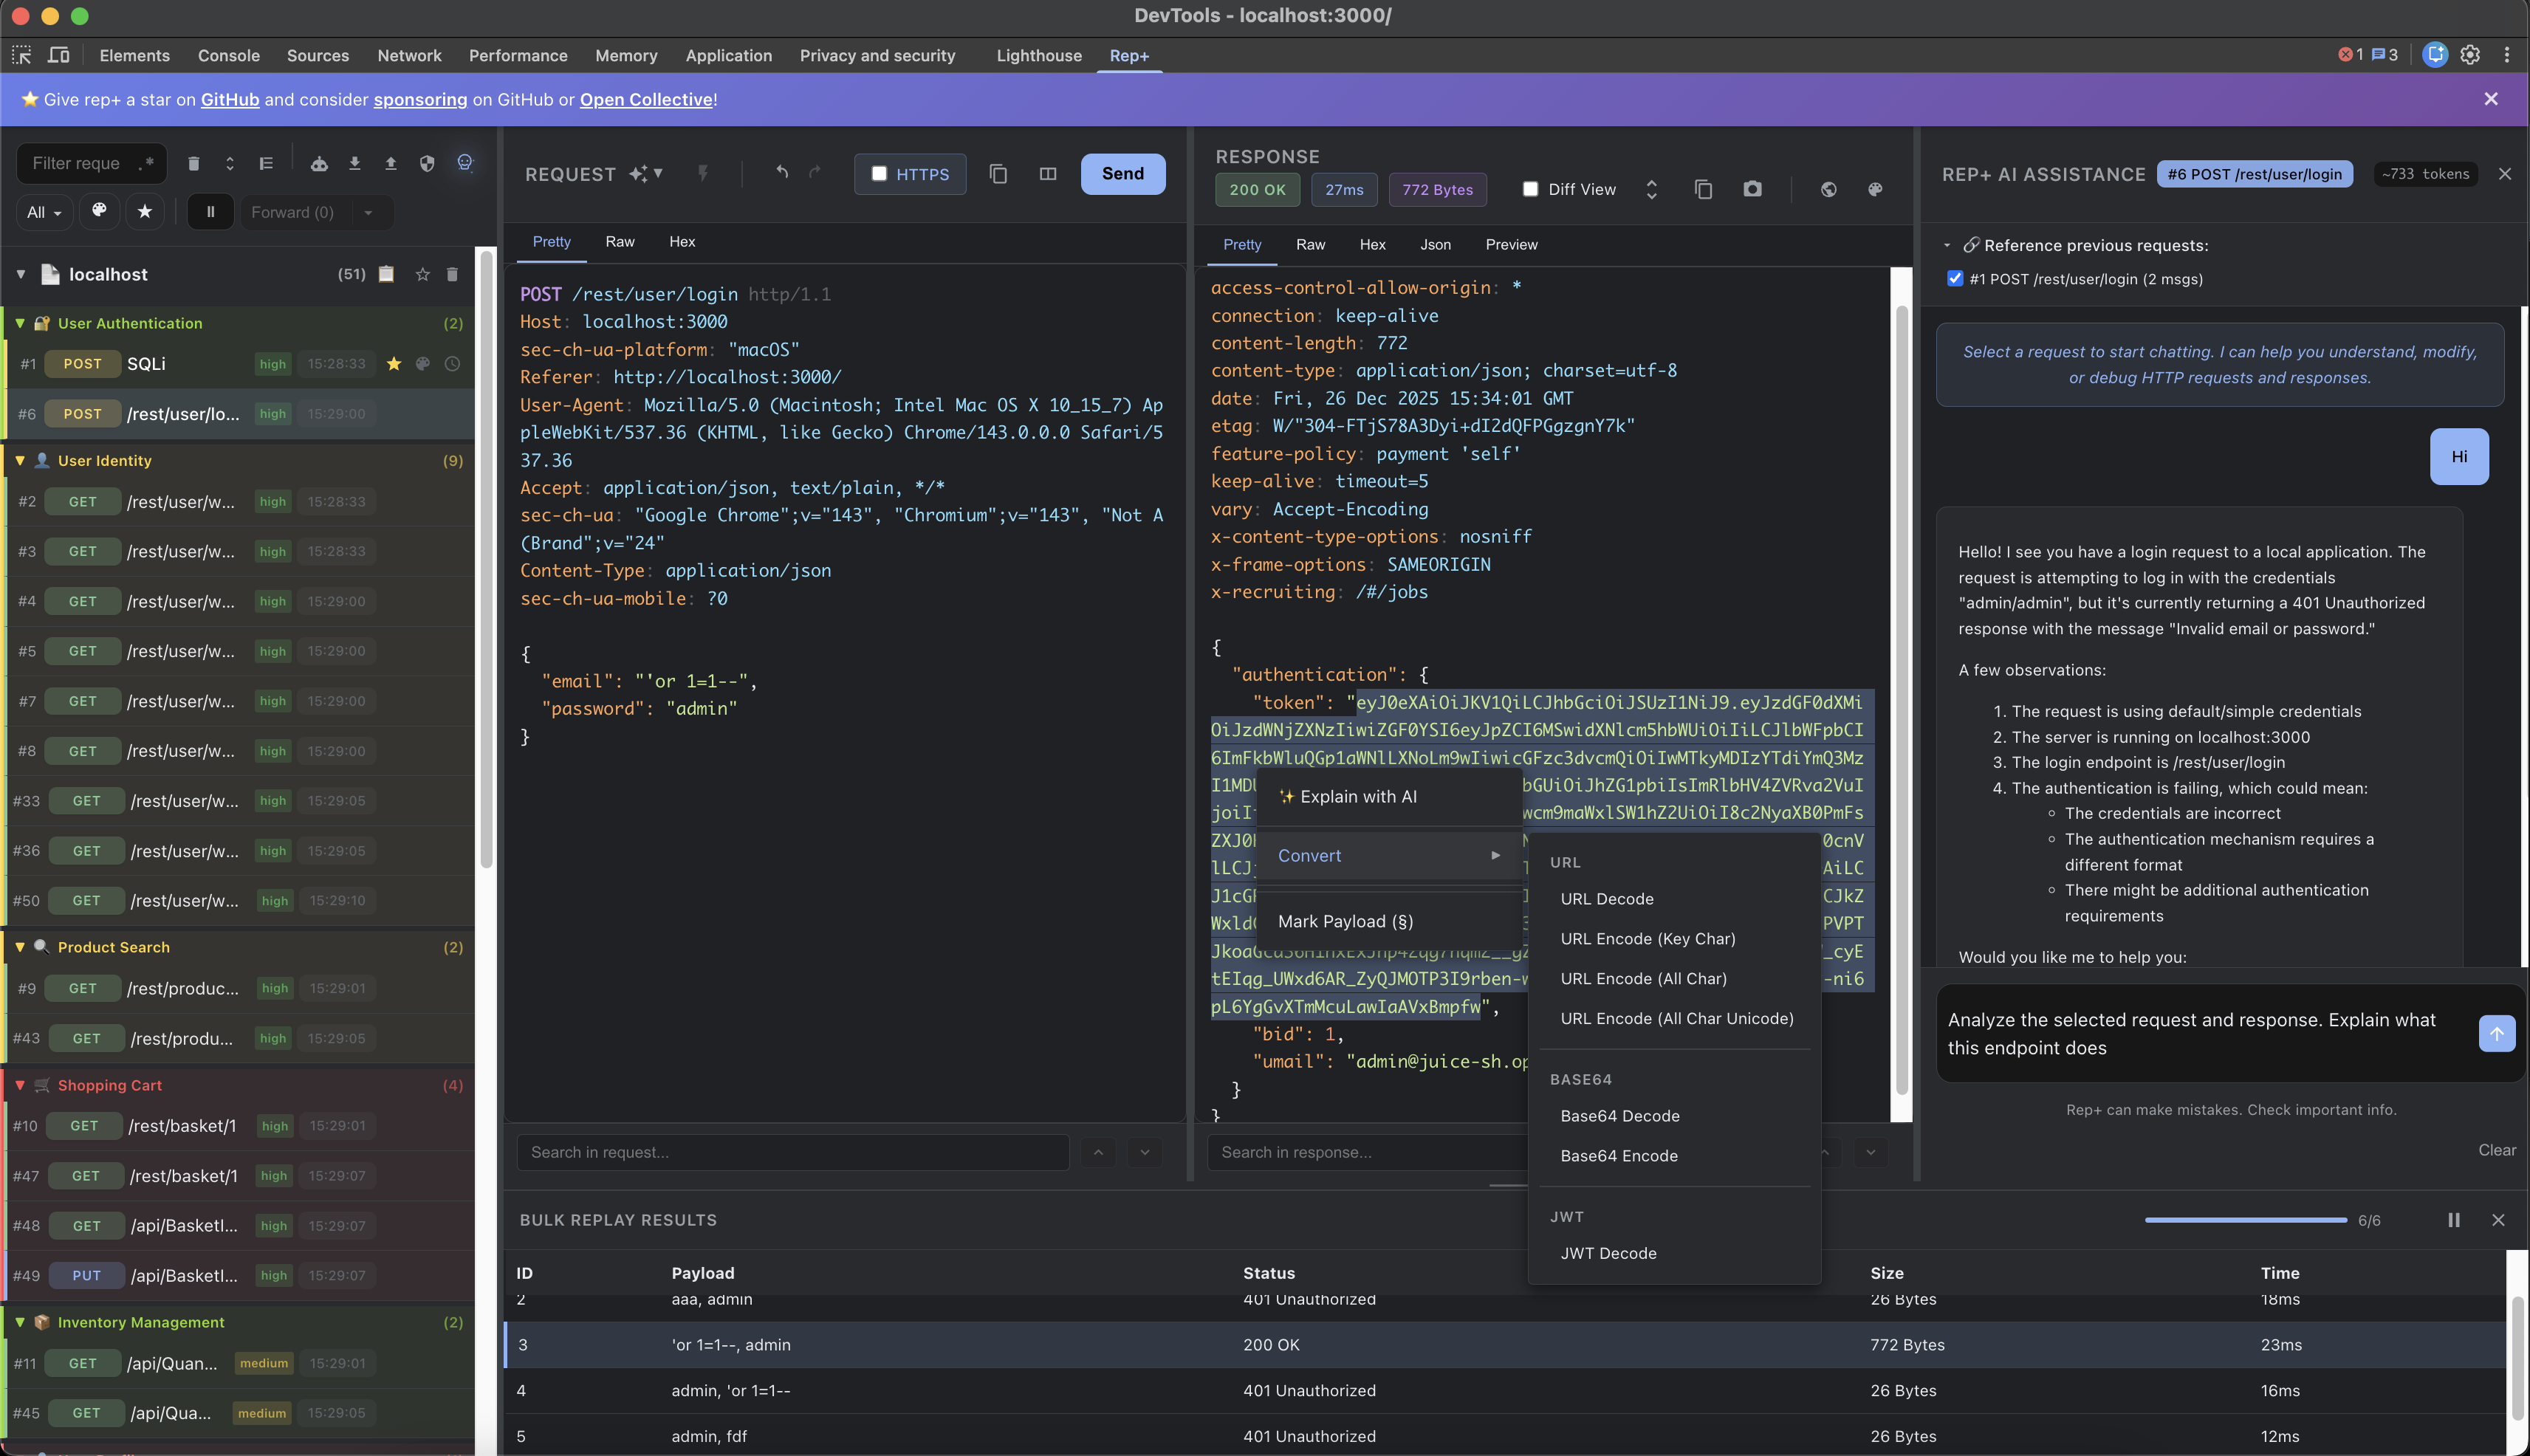 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
 pentagridsec/pentagridresponseoverview
Response Overview Extension for BurpSuite - Find exotic responses by grouping response bodies
 cyberdudebivash/cyberdudebivash-modular-ds-cve-2026-23550-detector
authorized CYBERDUDEBIVASH ECOSYSTEM tool for detecting CVE-2026-23550 in WordPress Modular DS plugin
 perunchess/cve-2025-66698
Proof-of-concept for CVE-2025-66698: authentication bypass in Veda v5.4.8 via empty ticket parameter, enabling enumeration of users, policies, and…
 bose122/cve-2024-3094
Exploit code for CVE-2024-3094, a critical vulnerability in XZ Utils, demonstrating the backdoor and its exploitation.








