
 #1
Tools for assessing the security of physical hardware, embedded systems, and IoT devices.
Kitploit recommended

 davidrxchester/smart-sketcher-upload
Exploits Bluetooth authentication bypass on smART Sketcher 2.0 toy projector, allowing unauthenticated connection and image upload via Python scripts.
 ang13t/bluesnoop
A TUI bluetooth utility for radar analysis and war driving 🦉
 whitej3rry/cve-2025-65731
Advisory for CVE-2025-65731
 enovella/tee-reversing
A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
 remenis/cve-2025-67160
Vatilon-based IP cameras expose internal web directories without authentication, leading to information disclosure.
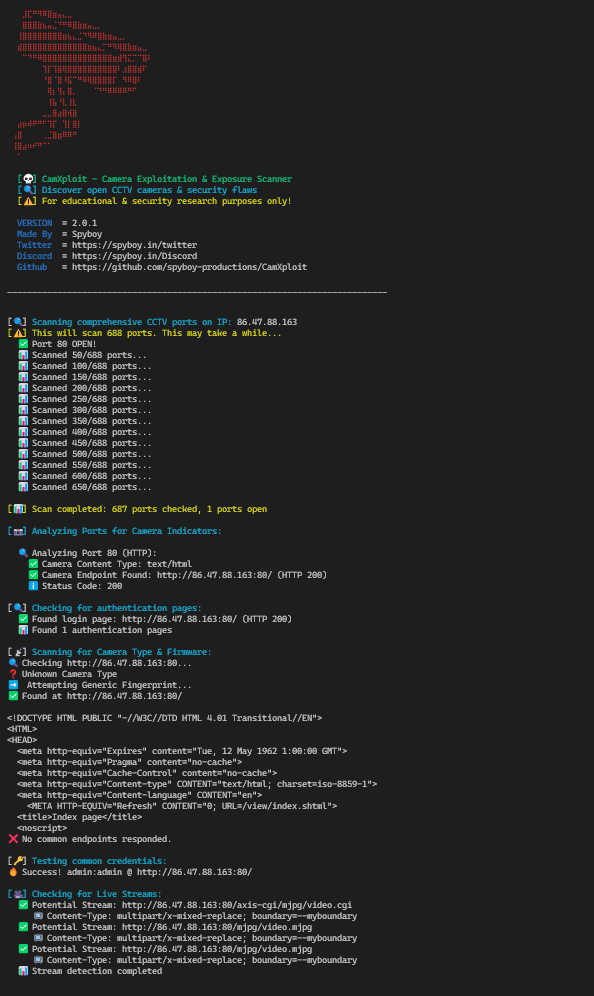 spyboy-productions/camxploit
Security reconnaissance and assessment tool for identifying potentially exposed IP cameras by analyzing open ports, service configurations, and…
 cybervinner/tp-link-tl-wr820n-cve-2025-14175
Responsible disclosure write-up for CVE-2025-14175 involving weak cryptographic algorithm support in the SSH server of TP-Link TL-WR820N.
 intellabs/kafl
A fuzzer for full VM kernel/driver targets
 hivesecurity/pso-printer-security-offensive
Offensive security tool for printer pentesting

 remenis/cve-2025-67159
Vatilon-based IP camera firmware allows authentication bypass and plaintext credential exposure via web.cgi API requests.
 remenis/cve-2025-67158
Revotech I6032W-FHW IP camera firmware fails to validate authentication fields in API requests, allowing attackers to bypass authentication and…
 wiliam227user/cve-2018-12633-tplink-auth-bypass
A technical case study and exploitation analysis of the Authentication Bypass vulnerability in TP-Link TL-WR840N firmware (CVE-2018-12633).
 yt2w/cve-2025-9961
Exploit for TP-Link AX10/AX1500 stack buffer overflow in CWMP (TR-069) enabling remote code execution via ret2libc with ASLR bypass. Includes…
 rizzziom/cve-2024-30167
Proof-of-concept exploit for authenticated command injection in Atlona AT-OME-RX21, allowing root-level command execution via the time configuration…
 nsm-barii/cve-2025-15474
A denial-of-service vulnerability in the AuntyFey BLE smart padlock allows unauthenticated connection floods to lock out legitimate users. …
 tamim1089/hikvisionexploiter
HikvisionExploiter is a Python-based utility designed to automate exploitation and directory accessibility checks on Hikvision network cameras…
 resi-le/nxloader
An app that enables payload injection into a Switch console from an Android device by exploiting the CVE-2018-6242 vulnerability








