
 #1
Fuzz testing, mutation-based, generation-based, and coverage-guided fuzzing tools.
Kitploit recommended

 bethington/ghidra-mcp
MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 xoreaxeaxeax/sandsifter
The x86 processor fuzzer
 google/honggfuzz
Security oriented software fuzzer. Supports evolutionary, feedback-driven fuzzing based on code coverage (SW and HW based)
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 foospidy/payloads
Git All the Payloads! A collection of web attack payloads.
 xmendez/wfuzz
Modular web fuzzer for automated security testing. Injects payloads into any HTTP request field to discover vulnerabilities, brute-force parameters,…
 1n3/intruderpayloads
A collection of Burpsuite Intruder payloads, BurpBounty payloads, fuzz lists, malicious file uploads and web pentesting methodologies and checklists.
 gwen001/pentest-tools
A collection of custom security tools for quick needs.
 trailofbits/publications
Publications from Trail of Bits
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
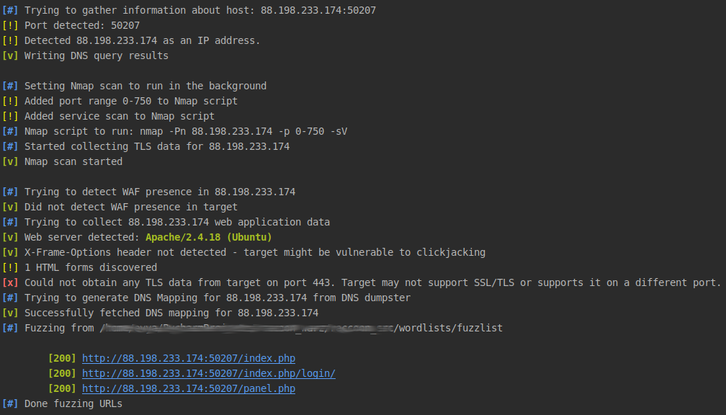 evyatarmeged/raccoon
A high performance offensive security tool for reconnaissance and vulnerability scanning
 google/boringssl
Fork of OpenSSL implementing TLS, cryptographic primitives, and X.509 certificate handling for use in Chrome and Android, with no API/ABI…
 ticarpi/jwt_tool
:snake: A toolkit for testing, tweaking and cracking JSON Web Tokens
 googleprojectzero/fuzzilli
A JavaScript Engine Fuzzer
 s0md3v/arjun
HTTP parameter discovery tool that finds valid query parameters for URL endpoints using a large dictionary, supporting GET/POST/JSON/XML requests,…
 elceef/dnstwist
Domain name permutation engine for detecting homograph phishing attacks, typo squatting, and brand impersonation







