
 #1
Digital forensics, evidence collection, timeline analysis, and incident investigation tools.
Kitploit recommended

 jumpseclabs/printnightmare
Information on the Windows Spooler vulnerability - CVE-2021-1675; CVE 2021 34527
 r3mrum/loki-parse
A python script that can detect and parse loki-bot (malware) related network traffic. This script can be helpful to DFIR analysts and security…
 f5devcentral/cve-2020-5902-ioc-bigip-checker
Local F5 BIG-IP script that scans for Indicators of Compromise (IoCs) related to CVE-2020-5902, checking logs, files, and system integrity to detect…
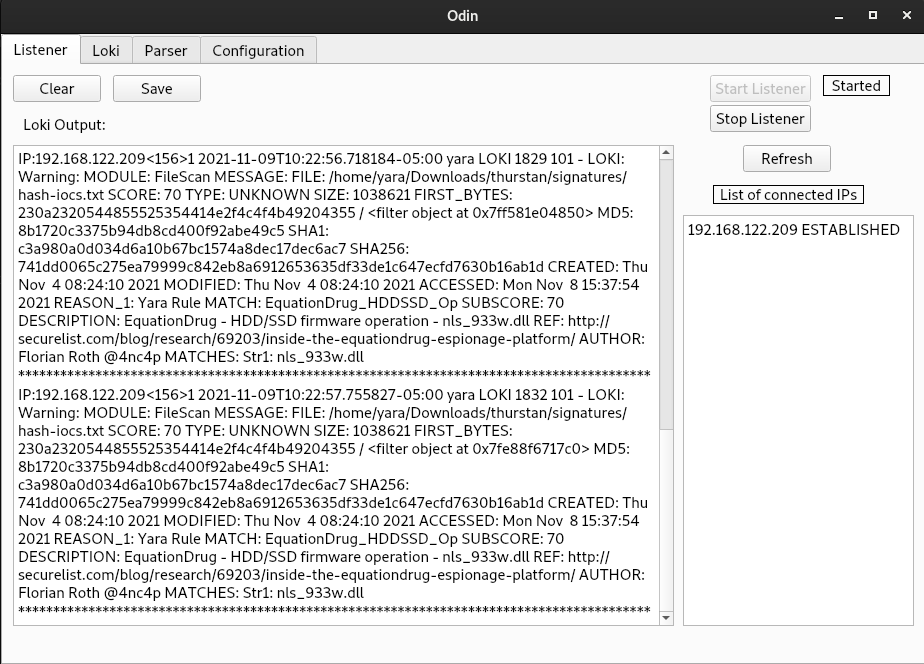 hamza-megahed/odin
Centralized IoC scanner that deploys Loki across endpoints, collects detection results, and parses logs into CSV for incident response and forensic…
 synacktiv/pike-agent
Experimental Linux strace LLM agent
 lucacav/steg-tools
A list of tools and material on steganography and information hiding
 unicornunicode/fact
Collects, processes, and visualizes forensic data from cloud and on-premise machine clusters for incident response and digital investigations.
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 onhexgroup/tabpe
A monthly Windows PE baseline dataset for Cyber security researchers
 lascc/dfirhub
Search Windows forensic artifacts, see where each one lives on disk, and copy the KAPE command to collect it. Also builds collection scripts and…
 s4larie/walletool
A utility for extracting cryptocurrency wallet data from wallet.dat files.
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
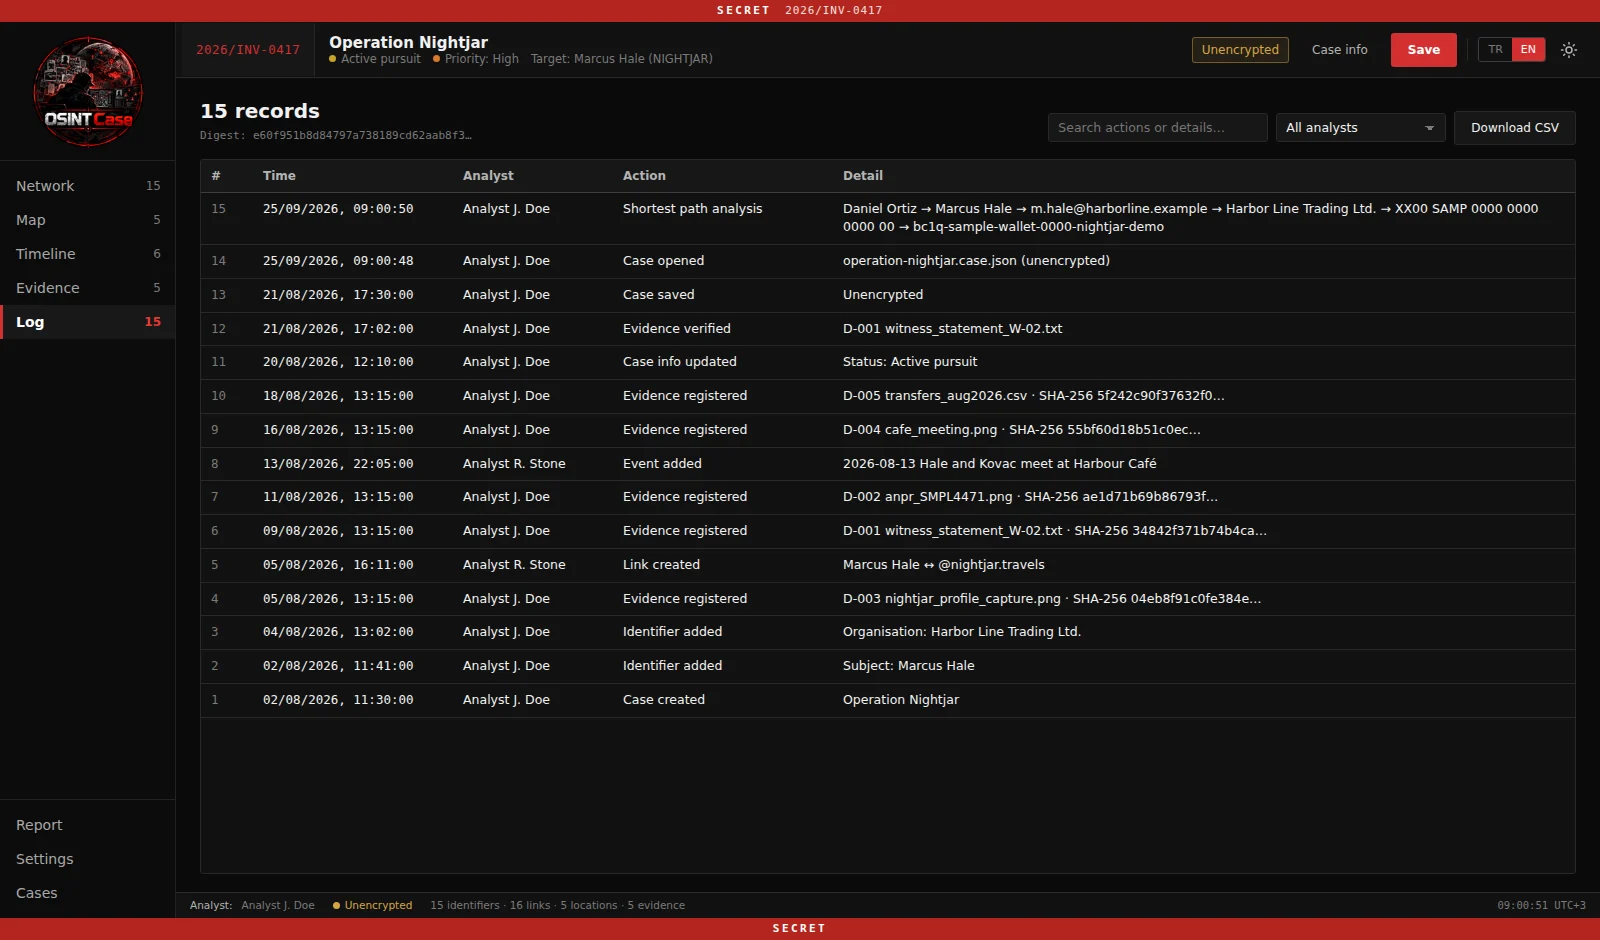 emrekybs/osintcase
An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.
 nccgroup/mortimer
A collection of scripts for processing network forensics type data and intelligence, mainly into a postgres database.
 0xlane/xz-cve-2024-3094
XZ Backdoor Extract(Test on Ubuntu 23.10)
 logisek/baconsampler
Sniffs outbound traffic for suspicious, beacon-like callbacks, because if it keeps coming back on schedule, it's probably not breakfast.
 farjadahmed/agentwatch
Silent session recorder for Claude Code that logs every action, flags dangerous commands (rm -rf, sudo, curl|sh), and provides timeline review, risk…








