
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Forensics — Page 26 | Kitploit
Categories

Forensics

Digital forensics, evidence collection, timeline analysis, and incident investigation tools.

Kitploit recommended

Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k6 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k5 days ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k20 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k7h 41m ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k21 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k1 day ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k6 days ago
mvt preview#8

mvt

GitHubmvt-project/mvt
15.7k3 days ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
23012 days ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k9 days ago
NewestRelevanceMost popularRecently updated
940 results
ssj preview

ssj

GitHubthirdbyte/ssj

Your everyday Linux distribution gone Super Saiyan.

penetration-testing-frameworkscontainer-securityforensics+2
603 years ago
HiddenDesktop preview

HiddenDesktop

GitHubmalwaretech/hiddendesktop

Create and enumerate hidden desktops.
defensive-toolsprivilege-escalationforensics+3
912 years ago
MrHandler preview

MrHandler

GitHubemrekybs/mrhandler

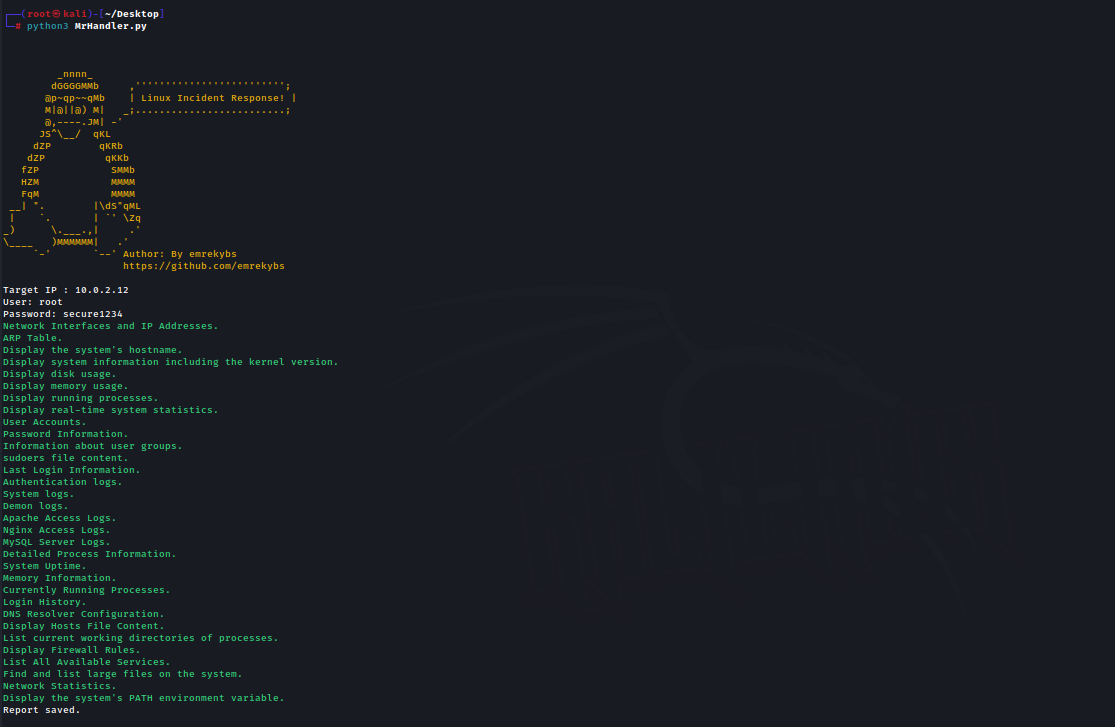
SSH-based Linux incident response tool that executes diagnostic commands to collect network configs, logs, user accounts, and processes, then…

forensicsdigital-forensicsincident-response+1
867 months ago
intelligence preview

intelligence

GitHubctrlaltint3l/intelligence

Centralized repository for malware samples, threat intelligence, IOCs, and security tooling logs to support threat research and incident response…
ioc-managementforensicsinformation-gathering+3
592 months ago
psc preview

psc

GitHubstealth/psc

E2E encryption for multi-hop tty sessions or portshells + TCP/UDP port forward
encryption-decryption-toolsforensicsnetwork-security+2
1331 year ago
proctools preview

proctools

GitHubmlcsec/proctools

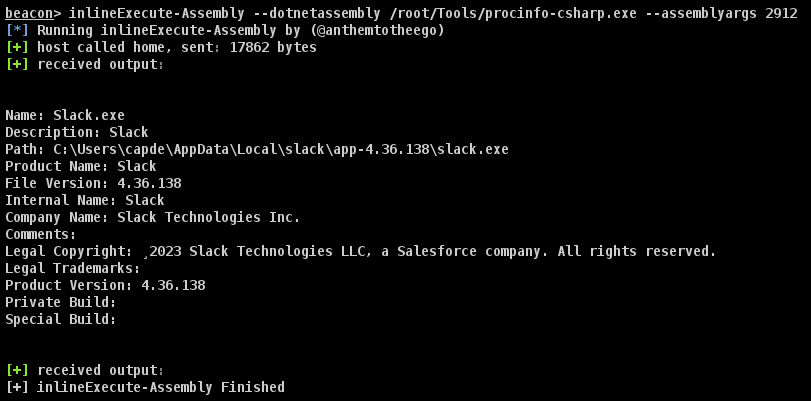
Small toolkit for extracting information and dumping sensitive strings from Windows processes
memory-forensicsforensicsinformation-gathering+2
1162 years ago
z9 preview

z9

GitHubsh1n0g1/z9

Detects PowerShell-based malware artifacts from event logs and performs static analysis on PowerShell scripts to identify malicious activity.
static-analysisforensicsmalware-analysis+2
683 years ago
hashr preview

hashr

GitHubgoogle/hashr

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
disk-forensicshash-analysisforensics+2
1308 months ago
StegoScan preview

StegoScan

GitHublcbower33/stegoscan

Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
osintforensicsinformation-gathering+7
1091 year ago
telfhash preview

telfhash

GitHubtrendmicro/telfhash

Symbol hash for ELF files

hash-analysisforensicsmalware-analysis+1
1184 years ago
subparse preview

subparse

GitHubjstrosch/subparse

Modular malware analysis artifact collection and correlation framework
static-analysisdynamic-analysis-sandboxingforensics+3
562 years ago
norimaci preview

norimaci

GitHubmnrkbys/norimaci

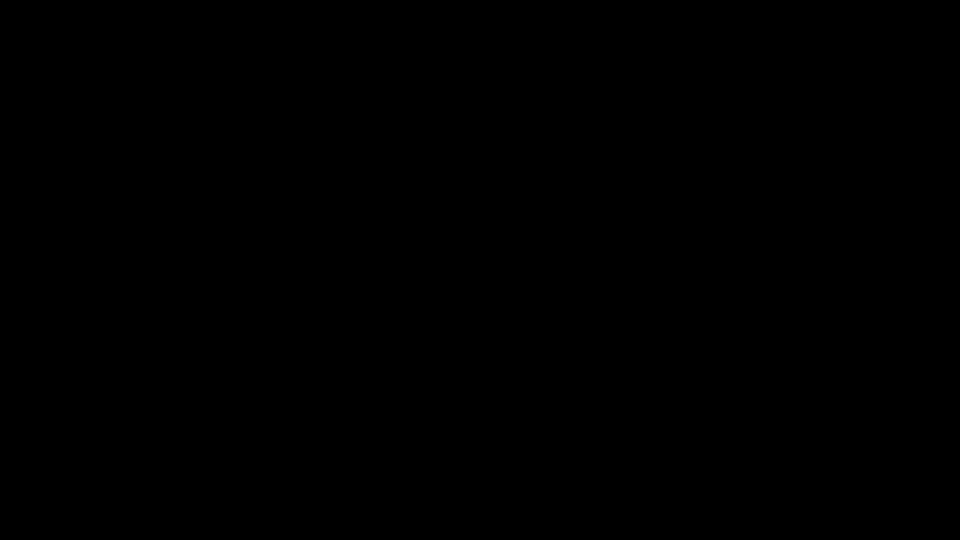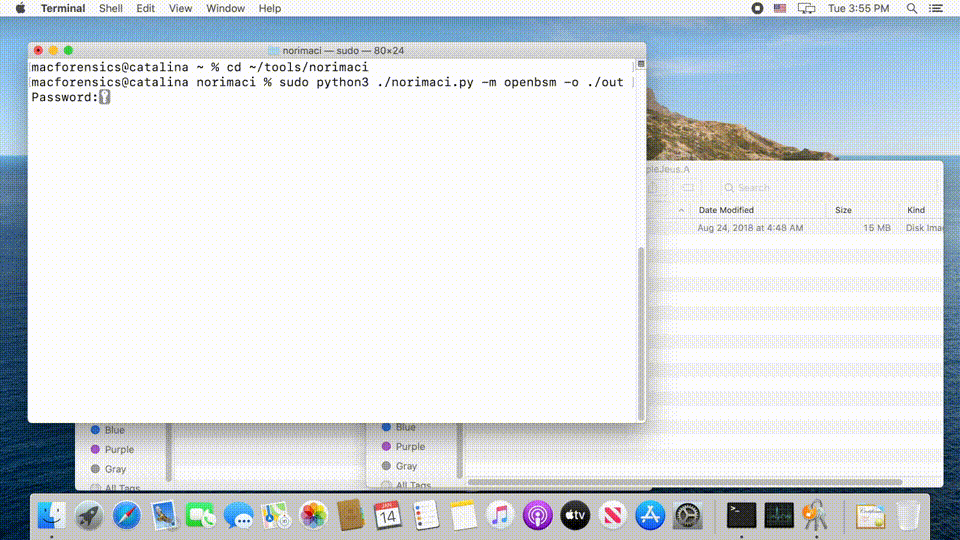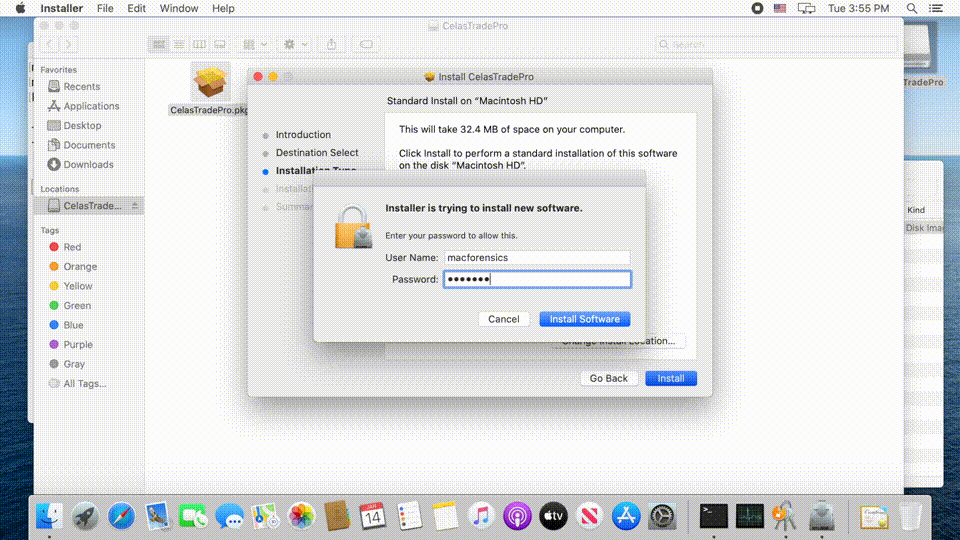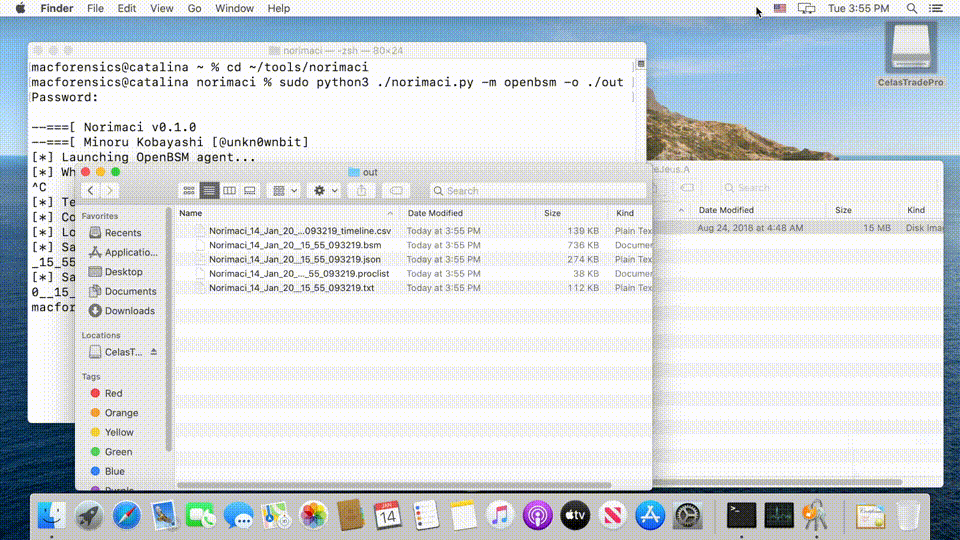
Lightweight macOS malware analysis sandbox that monitors system activity via OpenBSM or Monitor.app, generating detailed reports and timelines of…
dynamic-analysis-sandboxingforensicsmalware-analysis
716 years ago
Snap-Scraper preview

Snap-Scraper

GitHubrhematt/snap-scraper

Extracts and downloads Snap Map media by coordinates for OSINT, forensic analysis, and research. Supports metadata logging and bulk download.
osintreconnaissanceforensics+3
1143 years ago
pict preview

pict

GitHubthomasareed/pict

Modular incident response toolkit for collecting forensic data from potentially infected macOS endpoints, capturing browser artifacts, persistence…
forensicsinformation-gatheringpost-exploitation+2
953 years ago
UnjailMe preview

UnjailMe

GitHubmtjailed/unjailme

A sandbox escape based on the proof-of-concept (CVE-2018-4087) by Rani Idan (Zimperium)
privilege-escalationexploit-frameworksios-security+7
828 years ago
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
ioc-managementstatic-analysisdynamic-analysis-sandboxing+8
839 months ago
Registry-Spy preview

Registry-Spy

GitHubandyjsmith/registry-spy

Cross-platform registry browser for raw Windows registry files

forensicsdigital-forensics
1193 years ago
binwally preview

binwally

GitHubbmaia/binwally

Binary and Directory tree comparison tool using Fuzzy Hashing

hash-analysisforensicsdata-recovery+3
8411 years ago
Previous1…252627…53Next








