
 #1
Digital forensics, evidence collection, timeline analysis, and incident investigation tools.
Kitploit recommended
 devploit/awesome-ctf-resources
A list of Capture The Flag (CTF) frameworks, libraries, resources and software for started/experienced CTF players 🚩
 bkuan001/halo-record
Tamper-evident audit trails for AI agents: hash-chained Runtime Records, dependency-free, verifiable by anyone.
 sjzar/chatlog
chat log tool, easily use your own chat data. 聊天记录工具,轻松使用自己的聊天数据
 kevoreilly/capev2
Malware Configuration And Payload Extraction
 psypanda/hashid
Software to identify the different types of hashes -
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 elevenpaths/iphonerestrictionspasscodebf
Extracts and decrypts the 4-digit restriction passcode from iPhone backups on Windows machines, enabling recovery of device access controls.
 piotr-kniaz/eslockdecryptor
Tool for recovering and decrypting ES File Explorer encrypted files (.eslock)
 the-tcpdump-group/tcpdump
the TCPdump network dissector
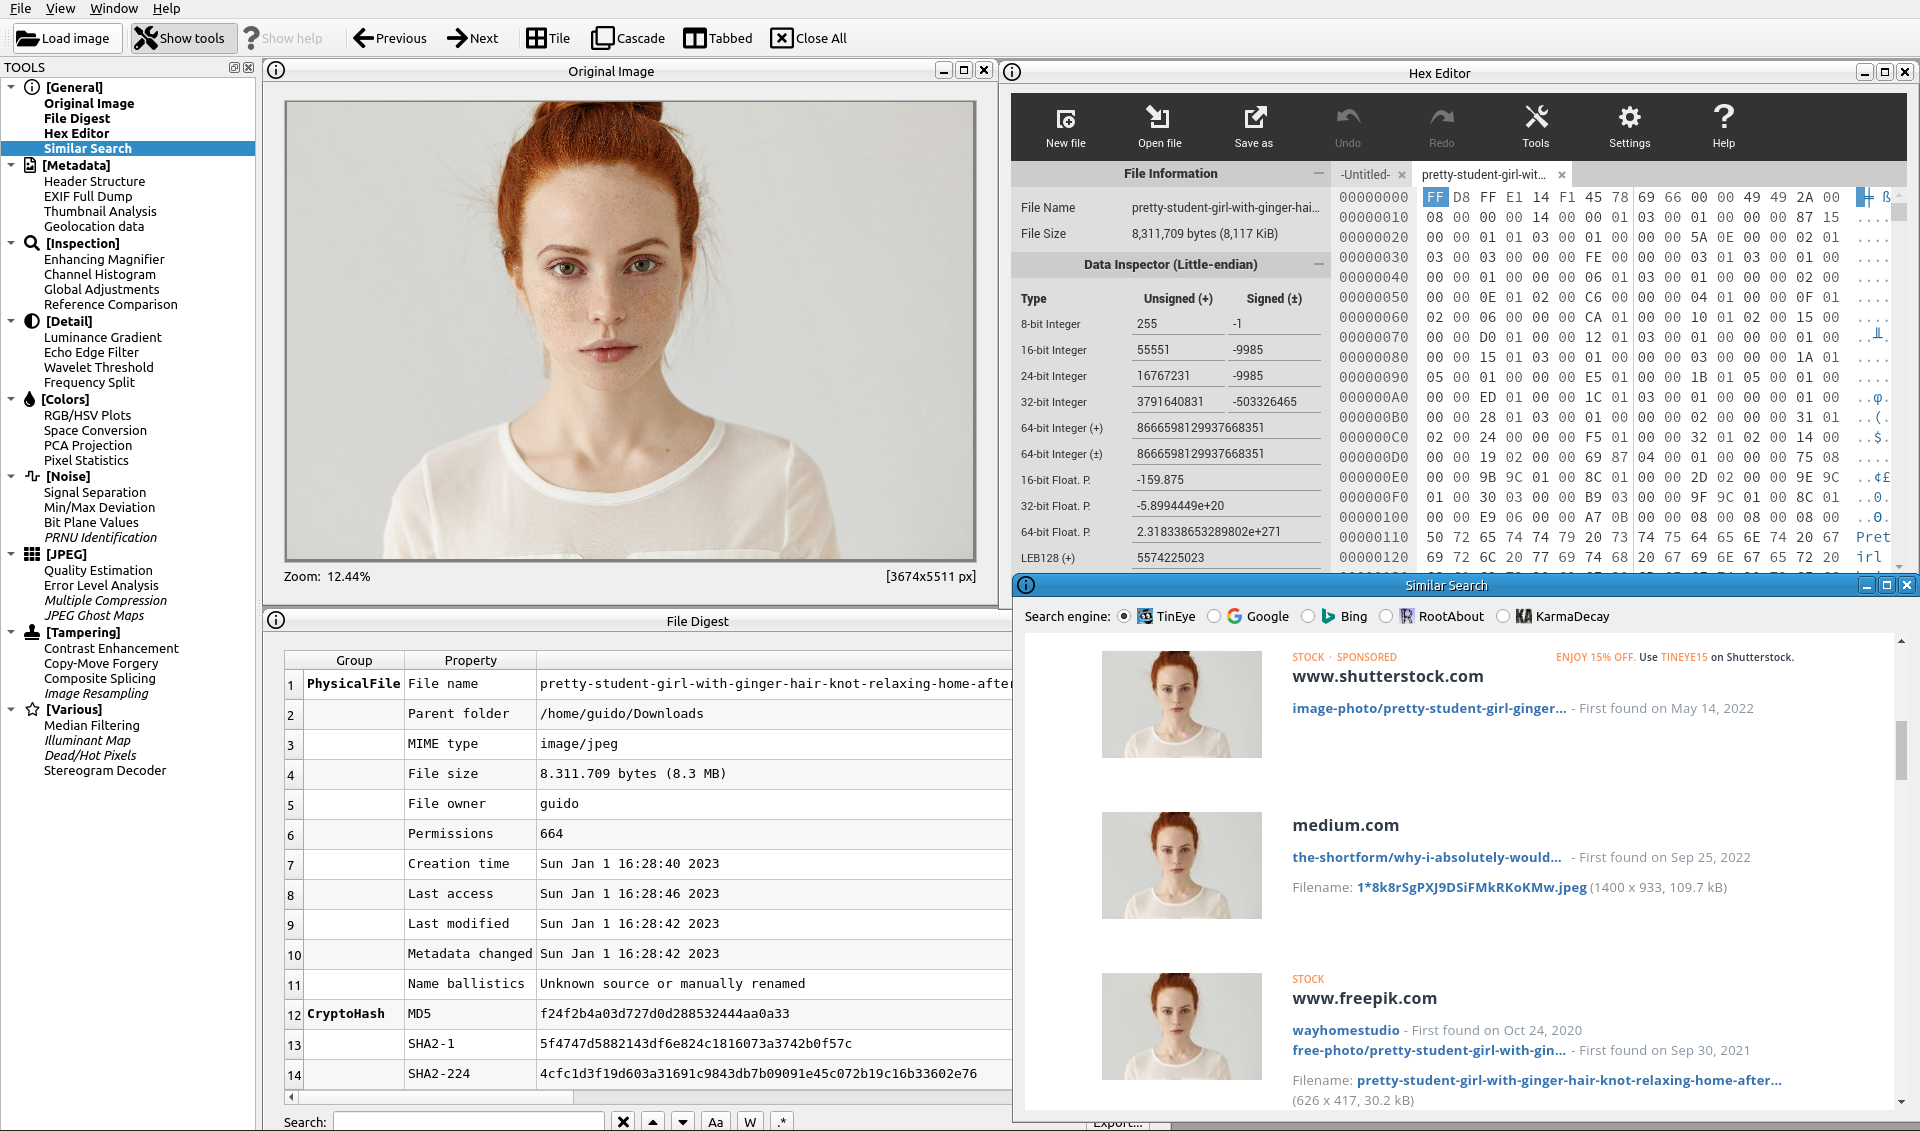 guidobartoli/sherloq
An open-source digital image forensic toolset
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
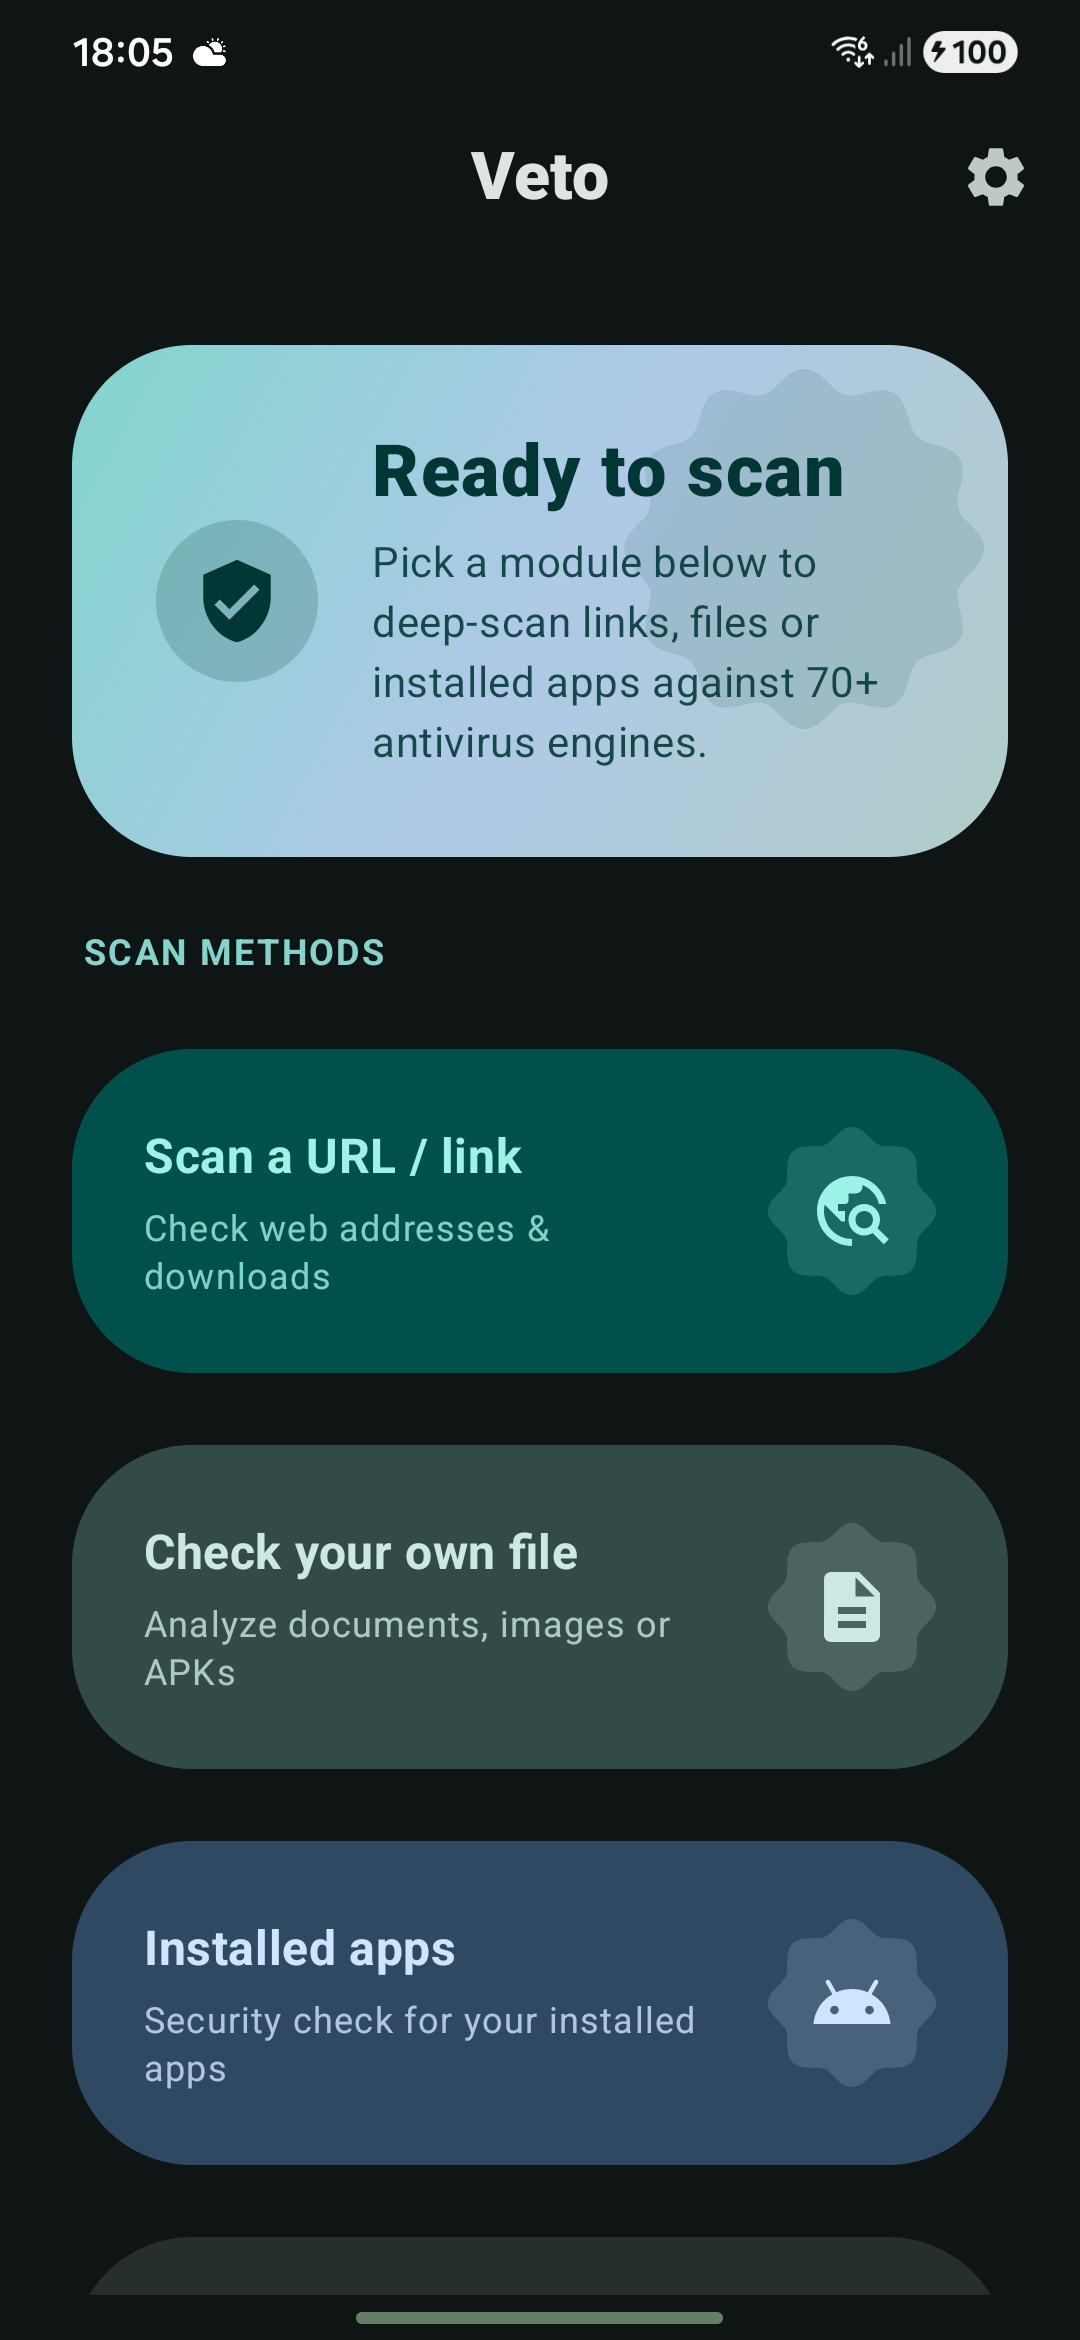 professorquantumuniverse/veto
Open-source Android client for VirusTotal. Scan files, URLs, and installed apps against 70+ antivirus engines. View detailed reports with hashes,…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 simsong/bulk_extractor
This is the development tree. Production downloads are at:
 soteria-security/hafnium-ioc
A PowerShell script to identify indicators of exploitation of CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-26865
 rshipp/awesome-malware-analysis
Defund the Police.
 idescriptor/idescriptor
privacy-first, open-source and free idevice management tool written in Rust and Qt
 lascc/dfirhub
Search artifact paths, build collection scripts, and convert Sigma rules. All in one place.







