Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Forensics — Page 2 | Kitploit
Categories

Forensics

Digital forensics, evidence collection, timeline analysis, and incident investigation tools.

Kitploit recommended

Top tools

10 selected
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3k5 months ago
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k22h 5m ago
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3k8 days ago
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2k19h 32m ago
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k8 days ago
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2k3 days ago
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.4k6 days ago
mvt preview#8

mvt

GitHubmvt-project/mvt
15.5k11h 55m ago
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
23011h 36m ago
avml preview#10

avml

GitHubmicrosoft/avml
1.1k1 day ago
NewestRelevanceMost popularRecently updated
931 results
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

cloud-infrastructure-securitypacket-sniffing-analysiscontainer-security+9
12.0k5 days ago
Dshell preview

Dshell

GitHubusarmyresearchlab/dshell

Dshell is a network forensic analysis framework.
packet-sniffing-analysisnetwork-forensicsforensics+3
5.5k2 years ago
pftriage preview

pftriage

GitHubidiom/pftriage

Python tool and library to help analyze files during malware triage and analysis.

static-analysisdynamic-analysis-sandboxinghash-analysis+4
796 years ago
DFIR-Companion preview

DFIR-Companion

GitHubhasamba/dfir-companion

DFIR forensics companion server + capture extension
defensive-toolsioc-managementmemory-forensics+9
333 days ago
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

static-analysisreverse-engineeringforensics+3
1281 month ago
etl2pcapng preview

etl2pcapng

GitHubmicrosoft/etl2pcapng

Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.

packet-sniffing-analysisnetwork-forensicsforensics+2
7351 year ago
Sandroid_Dexray-Intercept preview

Sandroid_Dexray-Intercept

GitHubfkie-cad/sandroid_dexray-intercept

A Android malware analysis tool that creates comprehensive runtime profiles by hooking into application behavior across cryptography, file systems,…

android-securitydynamic-analysis-sandboxingdynamic-code-analysis+8
101 month ago
ImHex preview

ImHex

GitHubwerwolv/imhex

🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.

static-analysismemory-forensicshash-analysis+10
54.4k12 days ago
openclaw-security-monitor preview

openclaw-security-monitor

GitHubadibirzu/openclaw-security-monitor

Proactive security monitoring for OpenClaw deployments. Detects ClawHavoc, AMOS stealer, CVE-2026-25253, memory poisoning, and supply chain attacks.

defensive-toolsvulnerability-scannersforensics+9
481 month ago
radare2 preview

radare2

GitHubradareorg/radare2

UNIX-like reverse engineering framework and command-line toolset

android-securityembedded-systems-securitystatic-analysis+16
24.5k11h 30m ago
Incident-Response-Powershell preview

Incident-Response-Powershell

GitHubbert-janp/incident-response-powershell

PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…

disk-forensicsioc-managementmemory-forensics+6
8074 months ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
forensicsdigital-forensicsthreat-intelligence+2
3.3k7 days ago
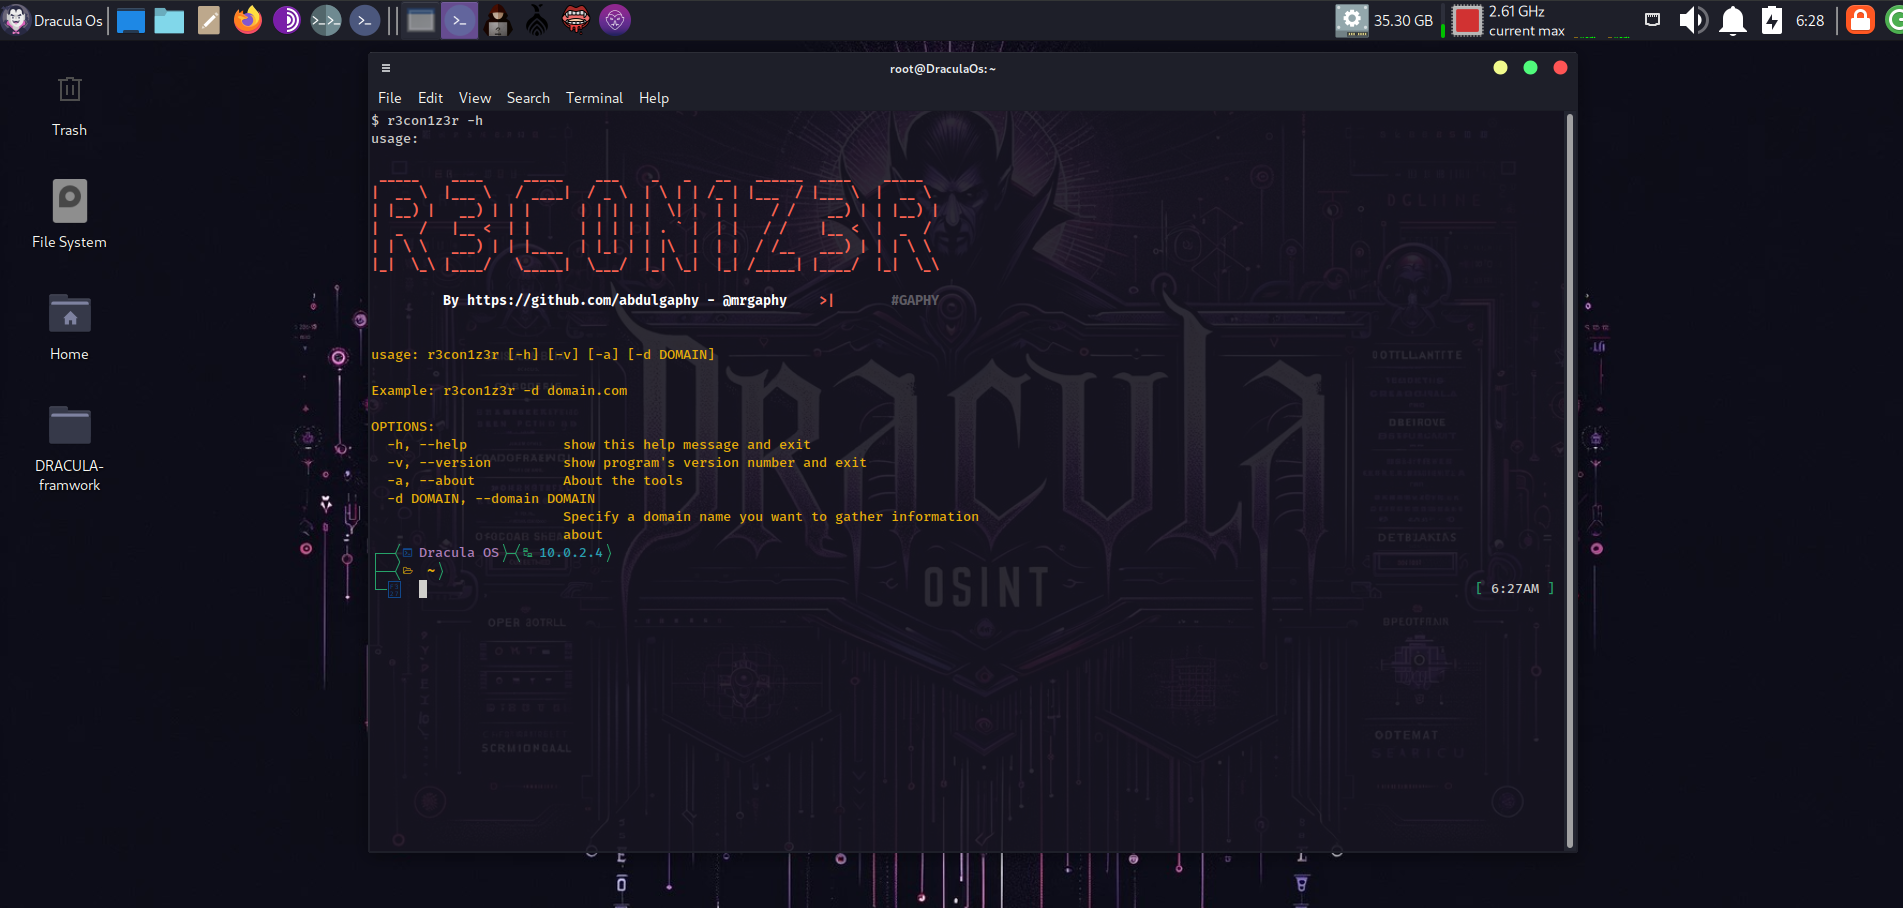
DraculaOS preview

DraculaOS

GitHubemrekybs/draculaos

Dracula OS is a Linux operating system meticulously designed for OSINT (Open Source Intelligence) and Cyber ​​Intelligence missions.

osintreconnaissancevulnerability-scanners+9
9411 months ago
Hacking-Tools preview

Hacking-Tools

GitHubyogsec/hacking-tools

A curated list of penetration testing and ethical hacking tools, organized by category. This compilation includes tools from Kali Linux and other…

osintpenetration-testing-frameworksvulnerability-scanners+9
1.8k2 days ago
whapa preview

whapa

GitHubb16f00t/whapa

Graphical forensic toolkit for parsing, decrypting, and extracting WhatsApp data from Android and iOS devices, including Google Drive and iCloud…


android-securityencryption-decryption-toolsios-security+5
1.5k2 months ago
MemProcFS preview

MemProcFS

GitHubufrisk/memprocfs

MemProcFS

memory-forensicsreverse-engineeringforensics+5
4.2k15 days ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

defensive-toolsdisk-forensicsmemory-forensics+8
4.2k3 days ago
OsintCase preview

OsintCase

GitHubemrekybs/osintcase

An OSINT investigation case mapping tool for organizing entities, relationships, evidence, and intelligence.


ioc-managementosintforensics+6
521 days ago
Previous123…52Next