
 #1
Comprehensive frameworks for exploit development, testing, and execution.
Kitploit recommended
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations

 exploit-database/exploitdb-bin-sploits
exploitdb-bin-sploits // Exploit-Database's binary exploits (what was located in the /sploits directory)
 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 cogensec/gideon
Autonomous security operations agent for threat intelligence, vulnerability research, IOC analysis, and red teaming. Supports dual-mode operations…
 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 cisc0-gif/kitt
Python-Based Pentesting Framework
 nikolajschlej/hydroph0bia
Binaries, drivers, PoCs and other stuff on Hydroph0bia vulnerability (CVE-2025-4275)
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
 skyshell20082008/cve-2019-0708-poc-hitting-path
It's only hitting vulnerable path in termdd.sys!!! NOT DOS
 infobyte/cve-2016-2776
CVE-2016-2776
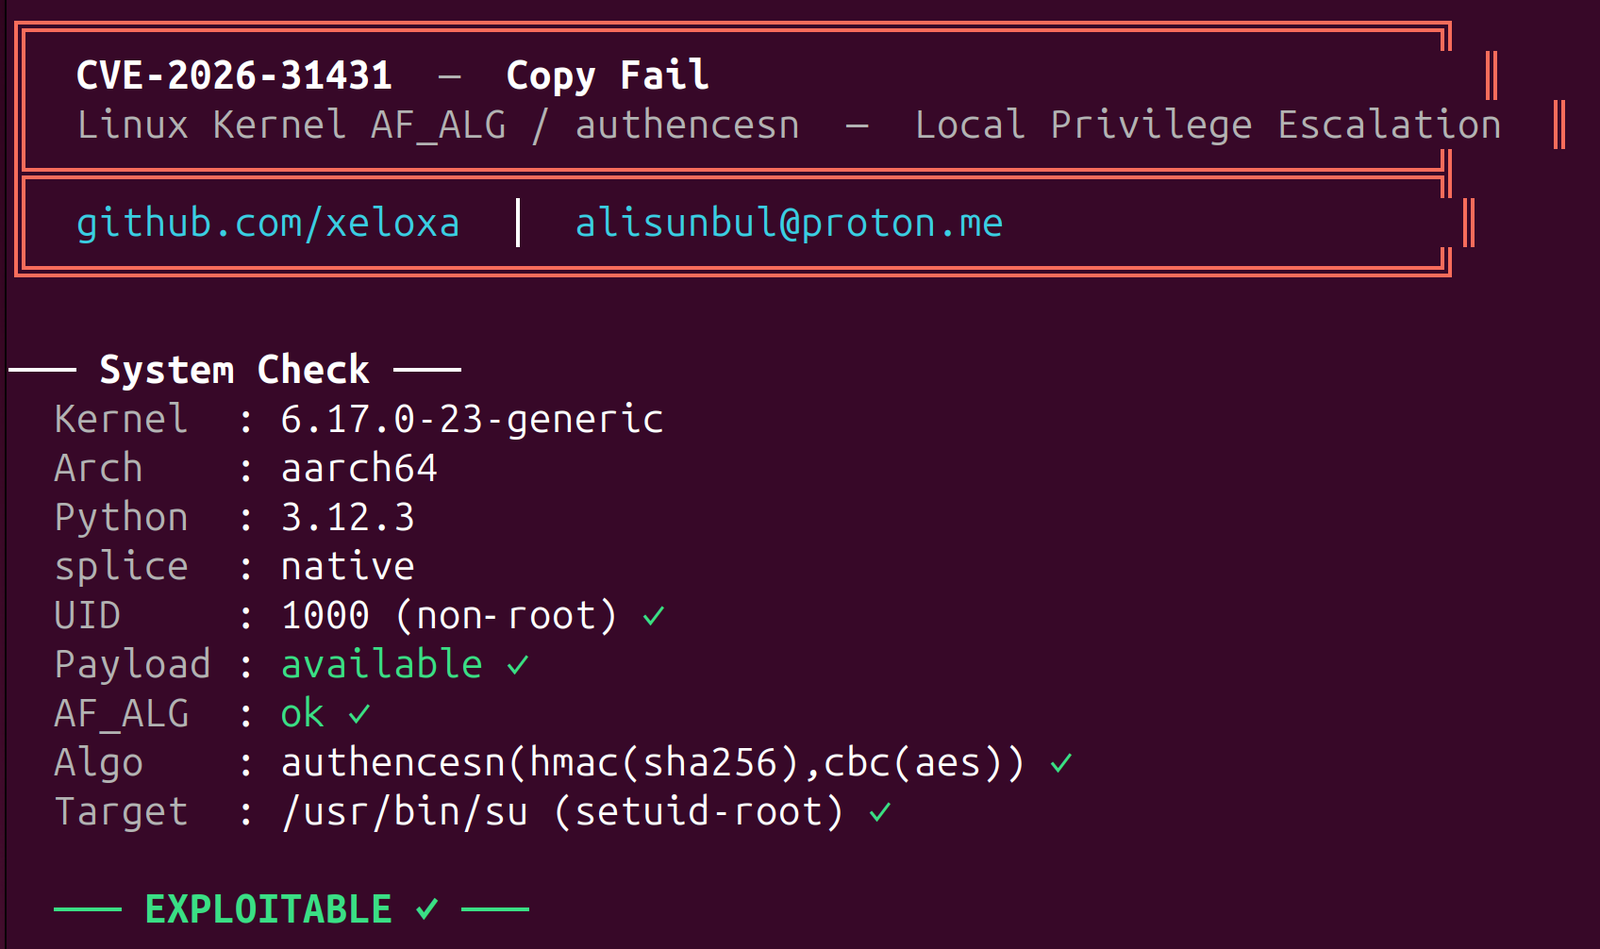 xeloxa/copyfail-exploit
Copy Fail (CVE-2026-31431) LPE exploit. A clean, multi-arch Python reimplementation targeting the Linux kernel AF_ALG page cache vulnerability.
 kyle41111/ai-file
A listener profile for the Mythic C2 framework that utilizes AI vendors file API's
 tc4dy/cve-2026-54121-poc-exploit
👻 CVE-2026-54121 - Best CertiGhost AD CS Multi-Exploit Framework | Advanced toolkit with rogue DC/LDAP servers, certificate abuse, PKINIT hash…
 geosn0w/cve-2025-24203-ios-exploit-with-error-logging
Slightly improved exploit of the CVE-2025-24203 iOS vulnerability by Ian Beer of Google Project Zero
 denizparlak/blackhat-arsenal-tools
Black Hat Arsenal Tools Official Account
 erarnitox/malvexc2
A simple C2 Framework written in modern C++








