
 #1
Comprehensive frameworks for exploit development, testing, and execution.
Kitploit recommended
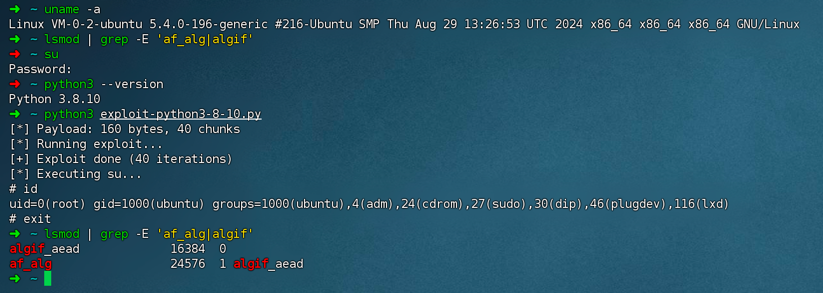
 y5neko/copy-fail-cve-2026-31431-universal
Multi-language implementation and compatibility with older versions of Python.
 sfrdevelopment/windows-smb-vulnerability-framework-cve-2025-33073
Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…
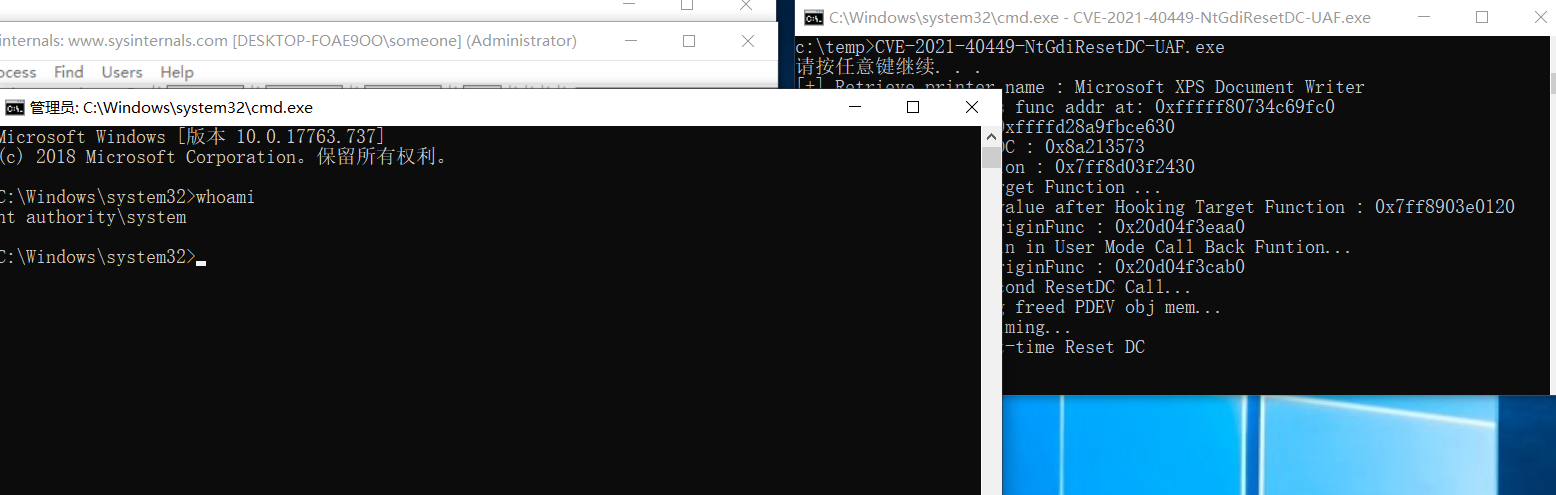 bl0odz/cve-2021-40449-ntgdiresetdc-uaf
Proof-of-concept exploit for CVE-2021-40449, a Windows kernel use-after-free in NtGdiResetDC, demonstrating privilege escalation via user-space…
 almorabea/pkexec-exploit
pwnkit: Local Privilege Escalation in polkit's pkexec (CVE-2021-4034)
 timwr/cve-2019-2215
Android kernel privilege escalation exploit for CVE-2019-2215, providing a proof-of-concept to achieve root access via a use-after-free vulnerability…
 ssrsec/cve-2020-11651-cve-2020-11652-exp
CVE-2020-11651&&CVE-2020-11652 EXP
 venglin/setcred
CVE-2026-45250: FreeBSD 14.4 setcred kernel buffer overflow (LPE)
 fenalik/cve-2021-1732
CVE-2021-1732 local privilege escalation exploit for Windows 10, with research and proof-of-concept code targeting kernel-mode vulnerabilities.
 rickgeex/msf-module-cve-2019-0708
Metasploit module for CVE-2019-0708 (BlueKeep) - https://github.com/rapid7/metasploit-framework/tree/5a0119b04309c8e61b44763ac08811cd3ecbbf8d/modules/…
 jakabakos/shadowray-rce-poc-cve-2023-48022
ShadowRay RCE POC (CVE-2023-48022)
 pupiles/bof-dnsmasq-cve-2017-14493
dnsmasq rop exploit with NX bypass
 darrynb89/cve-2004-1561
Python port of a Metasploit exploit targeting CVE-2004-1561 for remote code execution. Designed for penetration testing and vulnerability validation…
 vsai94/ece9069_smbghost_exploit_cve-2020-0796-
Description of Exploit SMBGhost CVE-2020-0796
 randarts/react-rce
CVE-2025-55182 취약점에 대한 샘플을 AI와 함께 작성 및 테스트 했습니다.
 abdullaabdullazade/cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root via page cache manipulation.
 joyghoshs/cve-2021-4034
Exploit for Local Privilege Escalation Vulnerability in polkit’s pkexec
 dennisdgr/cve-2026-31431-poc
An adapted version of the copy fail exploit to use parameters instead of dropping you into a root shell
 chacka0101/exploits
Exploits project Hacking Command Center








