 #1
 gregory-chatelier/huntglyph
Detect visually similar characters (homoglyphs) and hidden data in text to protect against deceptive attacks

 jason996/maritime-security-paper
Comprehensive research on security vulnerabilities in autonomous maritime vessels and defense recommendations
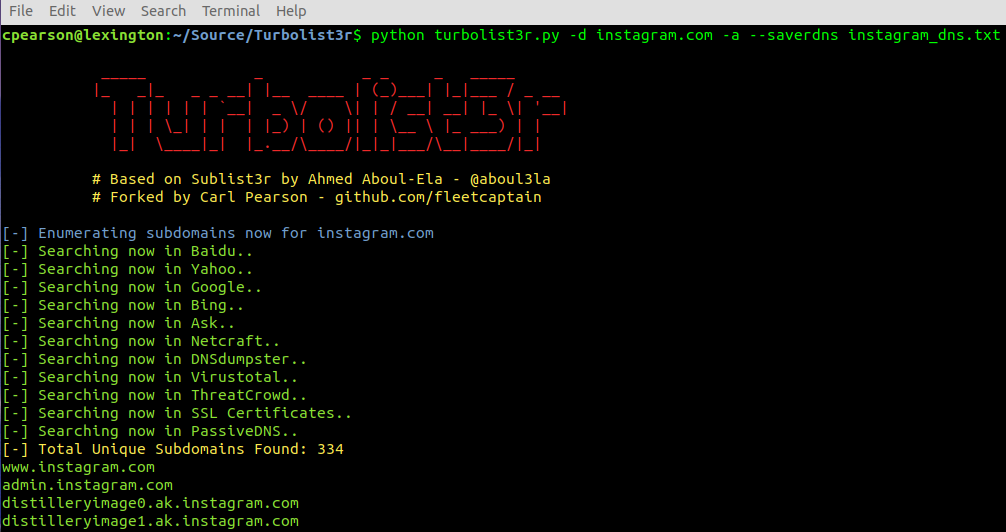 fleetcaptain/turbolist3r
Subdomain enumeration tool with analysis features for discovered domains
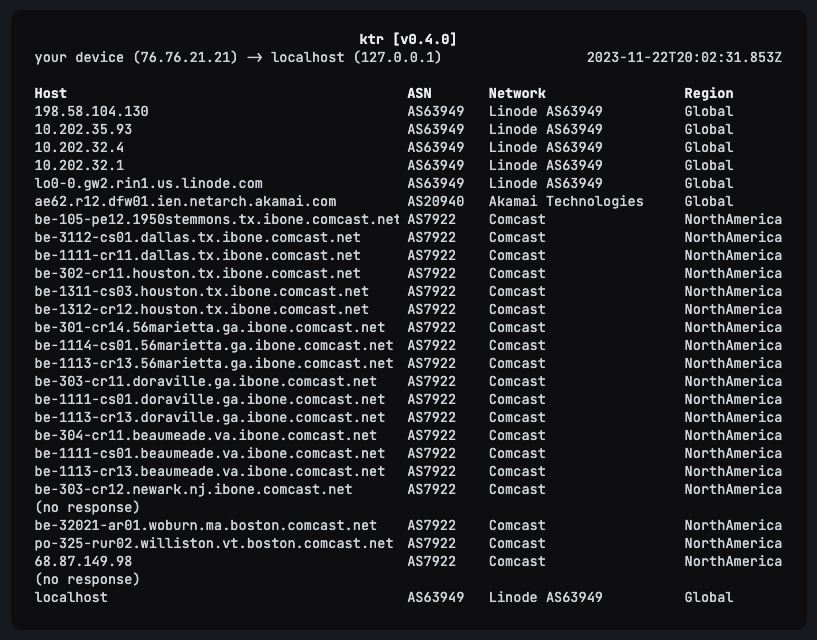 hackclub/ktr
Kog traceroute. Highly asynchronous traceroute program written in Rust with ASN WHOIS and PeeringDB lookups.
 desaivinayak449/bug-bounty-reports-desai-vinayak
Bug bounty and vulnerability research reports by Desai Vinayak — includes CVE-2023-50290 (Apache Solr) and Zscaler subdomain takeover findings.
 artur-augustyniak/class_struggle
Autoencoder-based anomaly detection for identifying phishing domains using CERT Polska warning list data, with Jupyter notebooks for research and…
 nehkark/cve-2025-40778
Proof-of-concept demonstrating DNS cache poisoning via additional record injection in BIND 9, with tools to validate and exploit CVE-2025-40778 for…
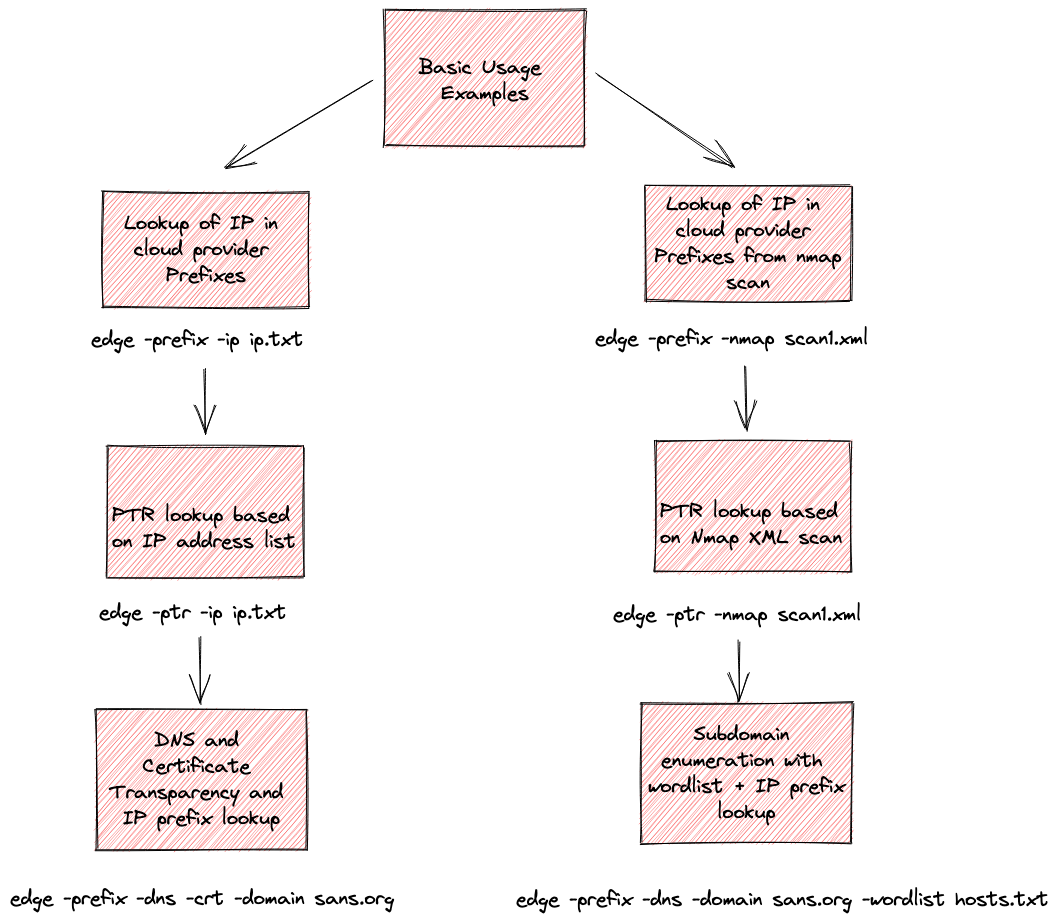 iknowjason/edge
Whois for the Cloud: Recon tool for cloud provider attribution. Supports AWS, Azure, Google, Cloudflare, and Digital Ocean.
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
 baderj/domain_generation_algorithms
Some results of my DGA reversing efforts
 jgoyd/ams-failopen
Zero-day in AppleMediaServices: Bag fetch failure disables Mescal/Absinthe signing. Requests to Apple services proceed unsigned, exposing downgrade,…
 0xxon/cve-2020-13777
Zeek script to detect servers vulnerable to CVE-2020-13777
 manaswijaiswal/reproducing-connman-1.34
CVE-2017-12865 exploit
 netspi/ateam
Python reconnaissance tool for discovering Azure services and attributing tenant ownership via DNS validation, multi-service probing, and response…
 6lj/evil-cve-2021-23017-update-2025
vulnerability in NGINX servers (versions 0.6.18–1.20.0). The scripts aim to cause a Denial of Service (DoS) by sending malicious DNS responses, with…