#1
Tools for blue team, defensive security, and threat protection.
Kitploit recommended

 ph0lk3r/anti-jndi
Fun things against the abuse of the recent CVE-2021-44228 (Log4Shell) vulnerability using common web servers.
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
 muhammad-ali007/follina_msdt_cve-2022-30190
Educational exploit for CVE-2022-30190 (Follina) demonstrating MSDT remote code execution via malicious Office documents, with detection and…
 scitotec/log4j-recognizer
A Java helper to identify log4j in the current classpath
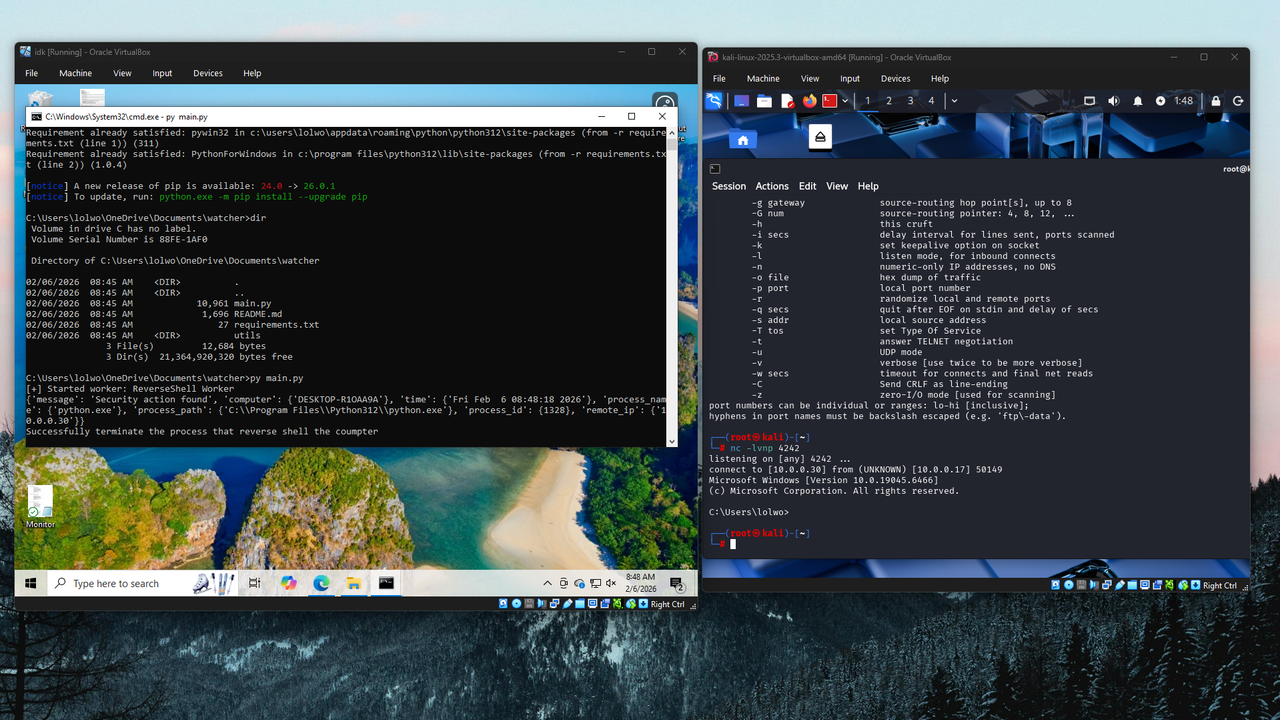 themoonsir/watcher
Detection reverse shell and kill it before trying shell.
 rxerium/internal-security-detect
The detection of internal security controls at a company
 ridhinva/defender-privilege-escalation-scanner
Scanner: CVE-2026-41091/45498 Microsoft Defender LPE/DoS — Python scanner for Windows Defender privilege escalation (CISA KEV)
 silent0x0/copy-fail---cve-2026-31431
CVE-2026-31431 "Copy Fail" - Analysis and defensive research for the Linux kernel AF_ALG privilege escalation vulnerability affecting all major…
 rdboboia/disable-registerspoolerremoterpcendpoint
Workaround for Windows Print Spooler Remote Code Execution Vulnerability(CVE-2021-34527). See:…
 kondordevsecuritycorp/cve-2025-60709
Windows CLFS LPE exploit PoC for security research
 jenderal92/ddos-traffic-monitor
A real-time traffic monitoring tool that detects and displays network traffic volume per IP address to identify potential DDoS attacks.
 derco0n/mitigate-folina
Mitigates the "Folina"-ZeroDay (CVE-2022-30190)
 edu0x01/hack-tools
Project that brings together several pentest tools
 corelight/petitpotam
Detects NTLM relay attacks via PetitPotam exploit using Zeek, distinguishing successful and unsuccessful attempts by analyzing DCERPC return codes.
 tieupham267/log4shell-coraza
Log4Shell (CVE-2021-44228) defense lab — nginx + Coraza WAF dynamic module + OWASP CRS v4. Educational use only.
 boliu83/cve-2026-31431-algif-aead-remediator
Kubernetes DaemonSet to detect and remediate CVE-2026-31431 (GHSA-2274-3hgr-wxv6) — algif_aead LPE via modprobe blacklist
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 areebashoaib42/keepass-cve-2023-32784-exploitation-and-defense
Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).