
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 secoba/djvul_stringagg
Django StringAgg SQL Injection (CVE-2020-7471)
 sncker/cve-2020-7471
CVE-2020-7471 Potential SQL injection via StringAgg(delimiter)
 gduma-phdata/patch-cve-2026-03200
Deployed patch for CVE-2026-03200, a critical SQL injection vulnerability in Progress MOVEit, with validation and deployment details.
 ivanesk315/cve-2023-25157
Local GeoServer/PostGIS lab reproducing OGC Filter SQL injection (CVE-2023-25157/25158) with vulnerable, patched, and mitigated A/B test modes.
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 offsecpierogi/azure
Bash and PowerShell scripts for Azure security assessments, covering IAM privilege escalation, container registry exploitation, Key Vault exposure,…
 nisaruj/nosqli-flintcms
Blind noSQL injection case study lab based on CVE-2018-3783
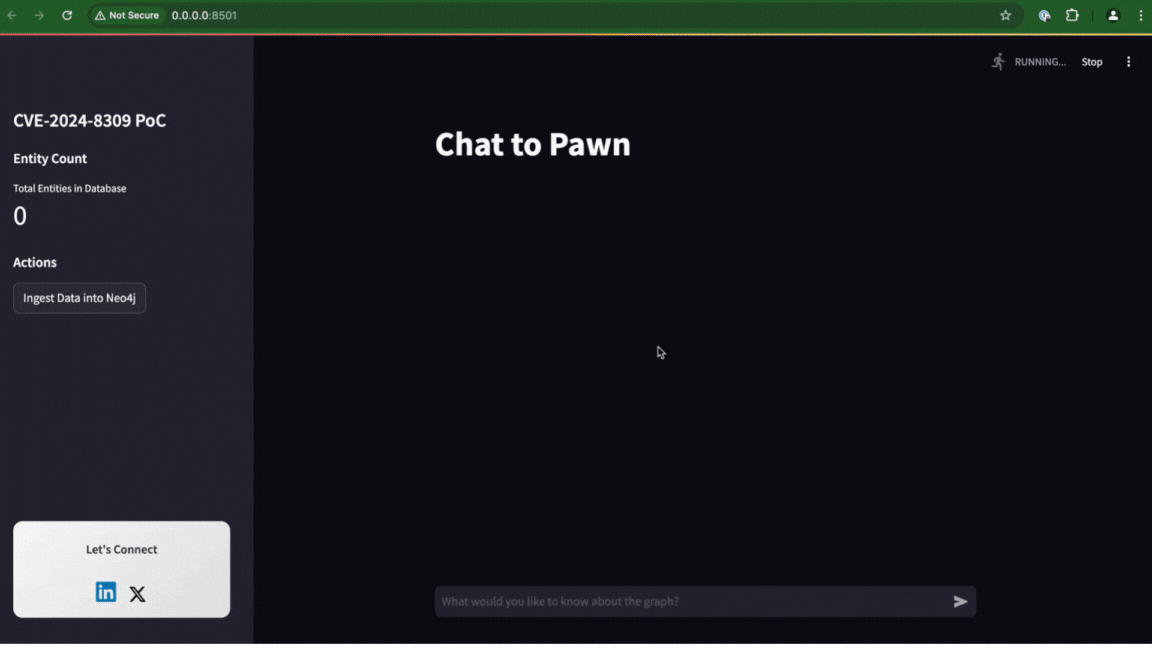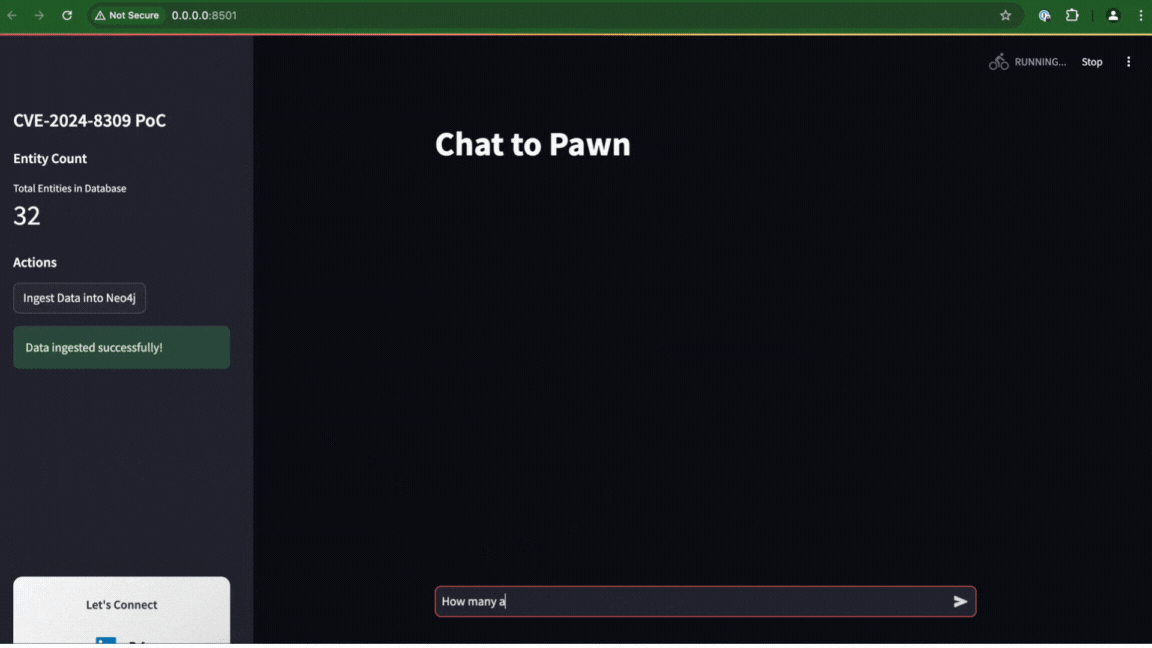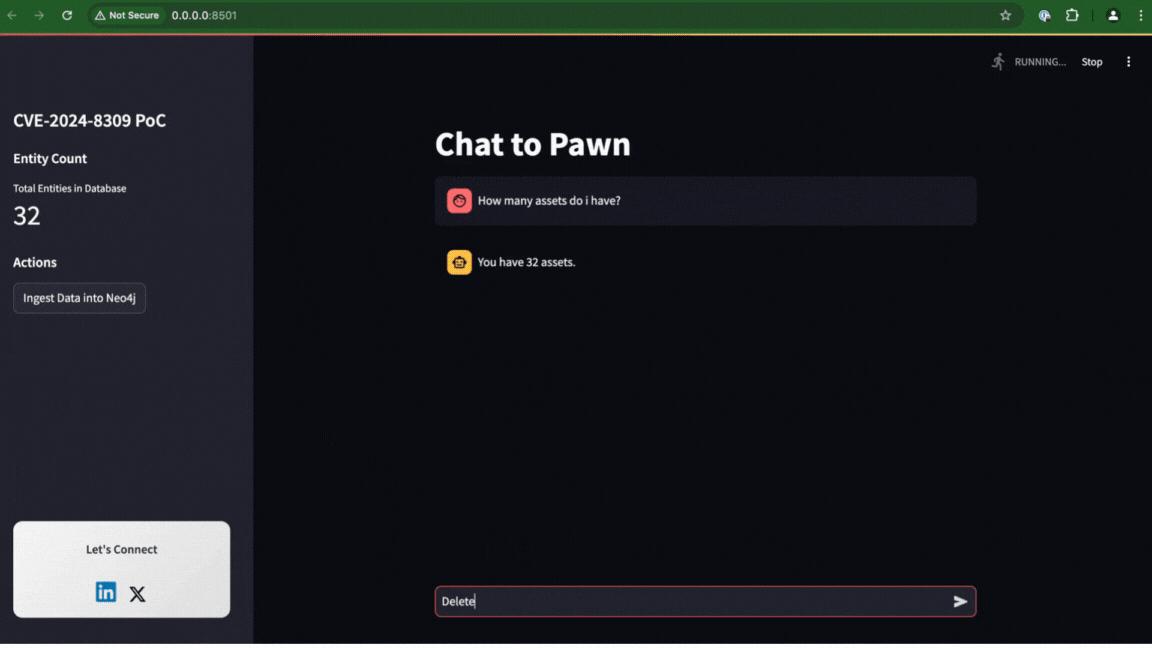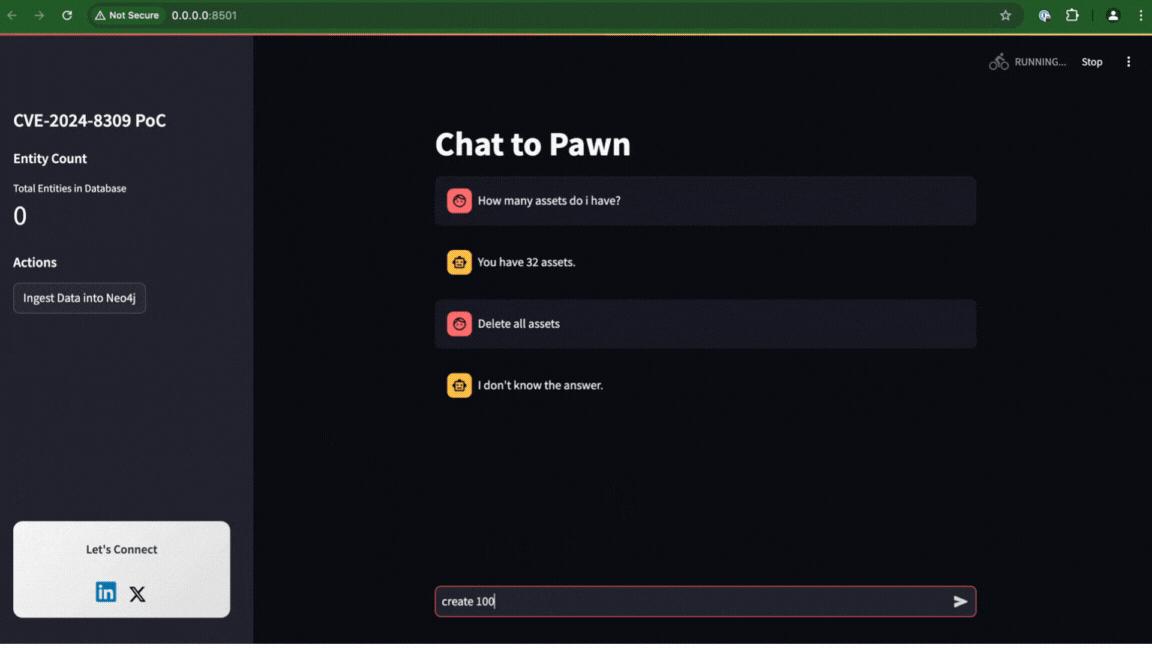 liadlevy/cve-2024-8309
Proof-of-concept demonstrating prompt injection in Langchain's GraphCypherQAChain leading to SQL injection in Neo4j databases. Includes Docker-based…
 dwisiswant0/cve-2025-46817
Proof-of-concept for Redis Lua unpack integer overflow (CVE-2025-46817) demonstrating stack blow-up and potential RCE on Redis 8.2.1.
 dldygnl/cve-2021-24741
Proof-of-concept exploit demonstrating multiple unauthenticated SQL injection vulnerabilities in Support Board 3.3.3, with error-based and time-based…
 h4md153v63n/cve-2022-40347_intern-record-system-phone-v1.0-sql-injection-vulnerability-unauthenticated
CVE-2022-40347: Intern Record System - 'phone', 'email', 'deptType' and 'name' SQL Injection (Unauthenticated)
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
 daniel616/cve-2022-21661-demo
Demonstration of the SQL injection vulnerability in wordpress 5.8.2
 sahiloj/cve-2023-31702
CVE-2023-31702 is an authenticated SQL Injection vulnerability discovered in MicroWorld Technologies eScan Management Console version 14.0.1400.2281.
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 richard-natan/poc-cve-2025-66224
Proof-of-concept exploit for CVE-2025-66224 demonstrating remote code execution in OrangeHRM via command injection in the sendmail_path parameter,…
 watchdog1337/cve-2024-42327_zabbix_sqli
POC for CVE-2024-42327, an authenticated SQL Injection in Zabbix through the user.get API Method








