
 #1
Database assessment, SQL injection testing, auditing, encryption, and activity monitoring tools.
Kitploit recommended
 al1ex/rogue-mysql-server
Rogue-MySql-Server
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
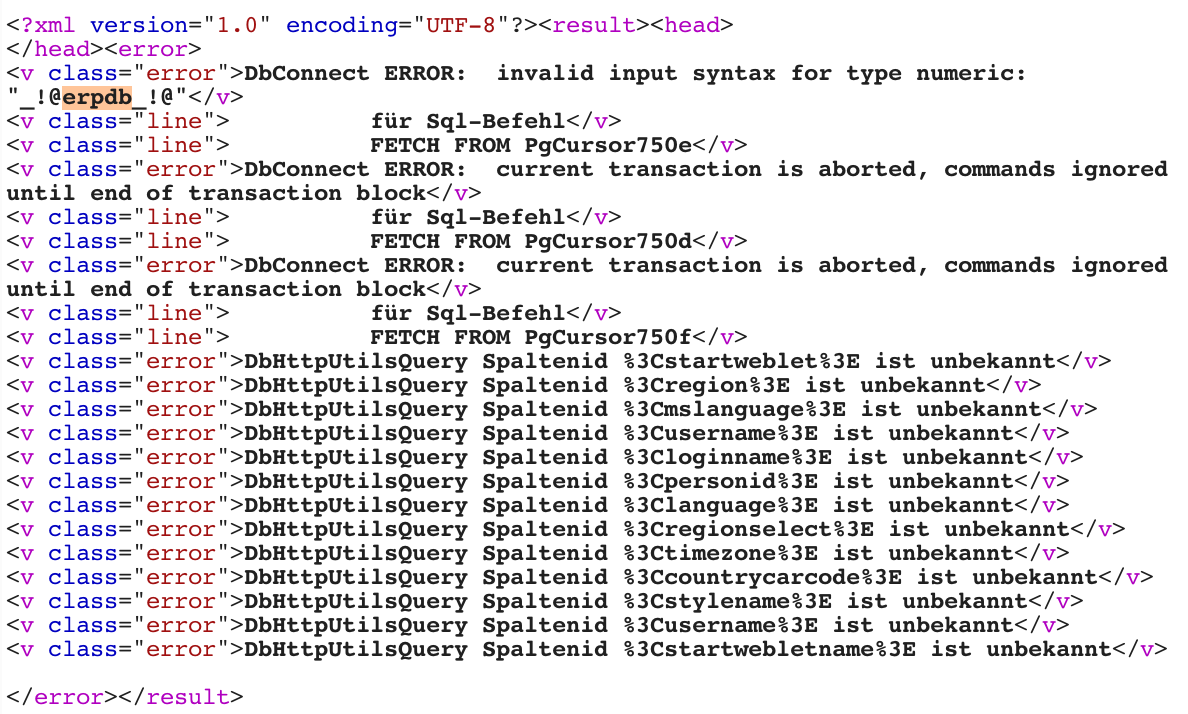 emreovunc/opensource-erp-sql-injection
CVE-2019-5893 | OpenSource ERP application has SQL Injection vulnerability.
 mbadanoiu/cve-2024-34693
CVE-2024-34693: Server Arbitrary File Read in Apache Superset
 abraxas/cve-2026-79752
CVE-2026-79752 disclosure pack for CakePHP 5.2.13 SQL injection via FunctionsBuilder::cast, with a Python PoC script and Docker lab for authorized…
 tc4dy/cve-2026-57821-poc-exploit
🔐 CVE-2026-57821 - Apache Fineract SQL Injection Toolkit 📚 Two Python scripts for authorized security testing: verifier.py (safe detection, no…
 neko-chanqwq/cve-2020-9483
PoC of SQL Injection vul(CVE-2020-9483,Apache SkyWalking)
 abraxas/phpmyadmin-auth-plugin-unquoted
phpMyAdmin 5.2.3 - High - Remote - SQLi - auth plugin identifier unquoted
 abraxas/cakephp-collate-sqli
CakePHP 5.4.2 - High - Remote - SQLi - COLLATE collation is a raw SQL fragment
 abraxas/phpmyadmin-designer-json-sqli
phpMyAdmin 5.2.3 - High - Remote - SQLi - Designer JSON unsanitized identifiers
 abraxas/sqlite-fts5-securedel
SQLite 3.53.4 - High - Local - Crash - FTS5 secure-delete PutVarint footer overrun
 joakimbulow/cve-2026-1337
CVE-2026-1337 - Neo4j - Log Injection
 abraxas/sqlite-rtree-rowid0
SQLite 3.53.4 - High - Local - UAF - rtree last_insert_rowid 0 node hash
 emad-almousa/cve-2025-53051
Proof-of-concept code and technical write-up demonstrating CVE-2025-53051, an Oracle 26ai histogram dictionary vulnerability exploitable through a…
 abraxas/sqlite-session-ncol
SQLite 3.53.4 - High - Local - heap OOB write - session changeset same-name nCol growth
 abraxas/moodle-enrol-database-sqli
Moodle 5.2.3 - High - Remote - SQLi - enrol_database concatenates course idnumber into SQL
 abraxas/mysql-mysqldump-tab-path
MySQL Community Server 26.7.0 - High - mysqldump --tab path leftover - client file write
 abraxas/sqlite-fj-using-auth
SQLite 3.53.4 - High - Local - Privilege leftover - FULL JOIN USING skips sqlite3AuthRead








