
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Data Recovery — Page 5 | Kitploit
Categories

Data Recovery

File recovery, disk recovery, deleted data restoration, and forensic carving tools.

Kitploit recommended

Top tools

10 selected
testdisk preview#1

testdisk

GitHubcgsecurity/testdisk
2.6k20 days ago
autopsy preview#2

autopsy

GitHubsleuthkit/autopsy
3.3k5 months ago
sleuthkit preview#3

sleuthkit

GitHubsleuthkit/sleuthkit
3.2k4 days ago
bulk_extractor preview#4

bulk_extractor

GitHubsimsong/bulk_extractor
1.4k12 days ago
foremost preview#5

foremost

GitHubkorczis/foremost
3819 years ago
scalpel preview#6

scalpel

GitHubsleuthkit/scalpel
6905 years ago
libewf preview#7

libewf

GitHublibyal/libewf
31811 days ago
libfsntfs preview#8

libfsntfs

GitHublibyal/libfsntfs
23812 days ago
libvshadow preview#9

libvshadow

GitHublibyal/libvshadow
11912 days ago
libqcow preview#10

libqcow

GitHublibyal/libqcow
623 months ago
NewestRelevanceMost popularRecently updated
155 results
android-forensics preview
Archived

android-forensics

GitHubnowsecure/android-forensics

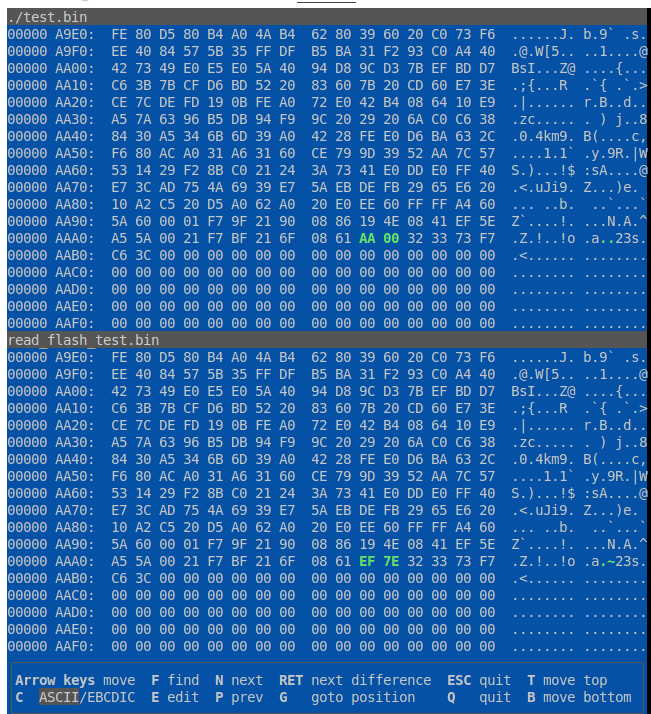
Open source Android Forensics app and framework
android-securityforensicsmobile-forensics+2
39711 years ago
ME2-Writeup preview

ME2-Writeup

GitHubcoremaze/me2-writeup

Reconstructing a Dead USB Protocol: A Handheld's Secrets Unlocked by a Hot Knife, a multi-disciplinary journey to reviving a forgotten USB interface

embedded-systems-securityreverse-engineeringdata-recovery+5
486 months ago
libvmdk preview

libvmdk

GitHublibyal/libvmdk

Library and tools to access the VMware Virtual Disk (VMDK) format
disk-forensicsdata-recoverydigital-forensics
18711 days ago
010-Editor-Template preview

010-Editor-Template

GitHubjas502n/010-editor-template

Binary template repository for 010 Editor, providing .bt scripts for parsing executables, filesystem images, registry hives, and forensic artifacts…
reverse-engineeringforensicsdata-recovery+4
445 years ago
xz preview

xz

GitHubx-cmd-build/xz

Portable binary distribution of xz-utils 5.8.3 with CVE-2024-3094 verification. Provides static builds for Linux, macOS, and Windows for compression…

general-purpose-utilitiesencryption-decryption-toolsscripting-automation+2
3 months ago
ffs preview

ffs

GitHubdmtrkovalenko/ffs

F*ck file system - cli file search tool that bypasses OS kernel and reads your disc directlry
disk-forensicsgeneral-purpose-utilitiesscripting-automation+3
1744 months ago
hashdeep preview

hashdeep

GitHubjessek/hashdeep

Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
hash-analysisforensicsdata-recovery+1
7869 years ago
DroneXtract preview

DroneXtract

GitHubang13t/dronextract

Digital forensics suite for DJI drones that parses telemetry files, extracts hidden data via steganography, visualizes flight paths, and detects…

forensicssteganographydata-recovery+3
3633 years ago
RawCopy preview

RawCopy

GitHubjschicht/rawcopy

Commandline low level file extractor for NTFS
disk-forensicsforensicsdata-recovery+1
3187 years ago
dwipe preview

dwipe

GitHubjoedefen/dwipe

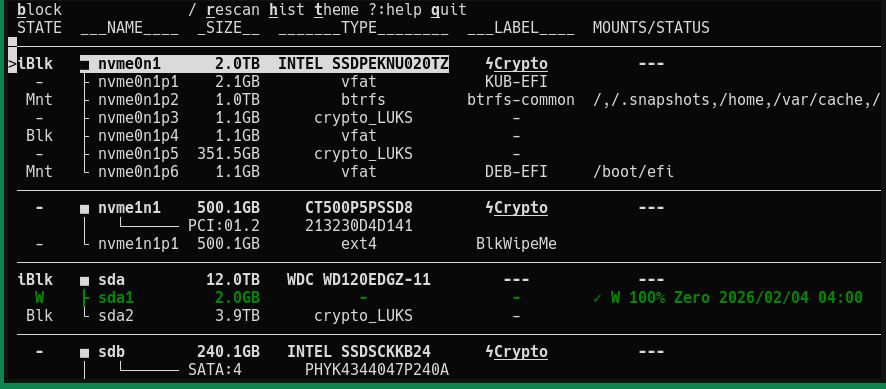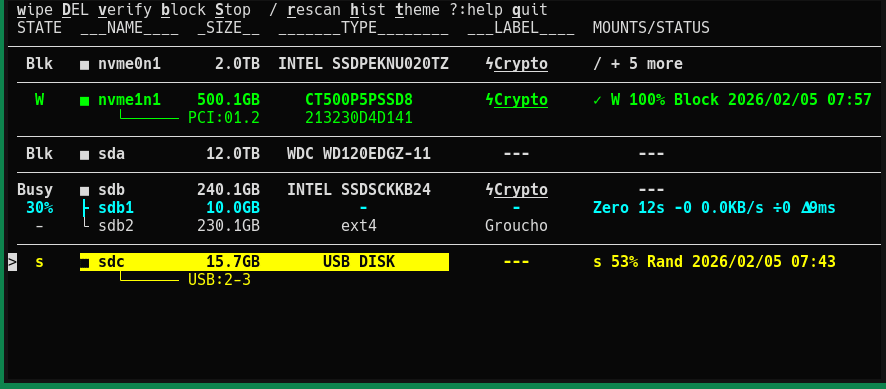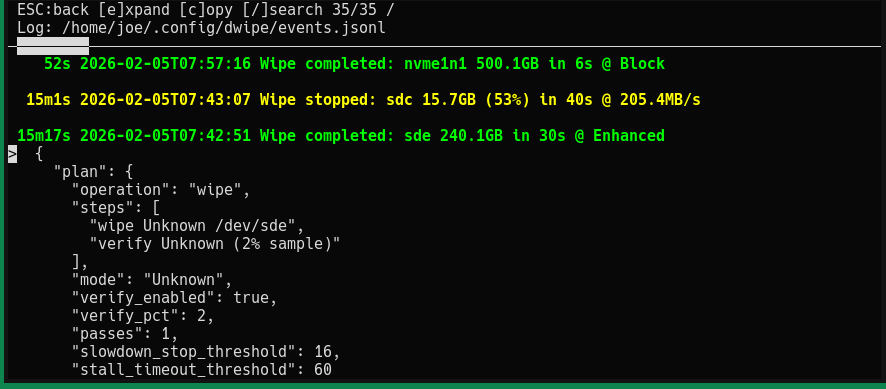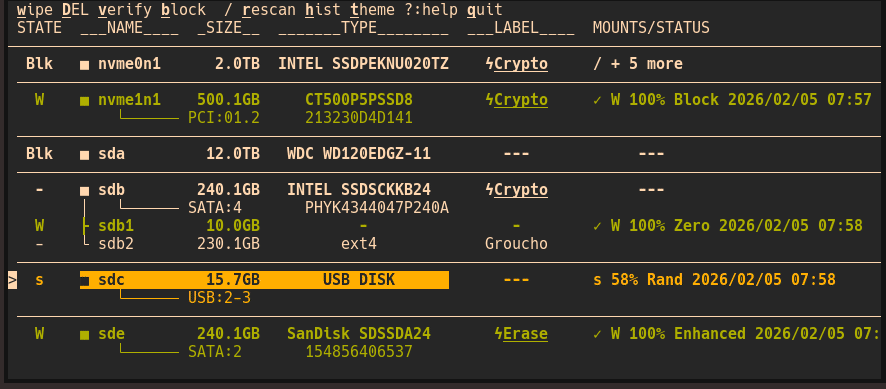
Tool to securely and efficiently wipe devices and partiitions for Linux
general-purpose-utilitiesencryption-decryption-toolsforensics+3
1649 days ago
Exif-Grabber preview

Exif-Grabber

GitHubd4vinci/exif-grabber

A python tool that will extract exif data from picture with two methods

osintforensicsinformation-gathering+3
4210 years ago
RecoverPy preview

RecoverPy

GitHubpablolec/recoverpy

Interactively find and recover deleted or :point_right: overwritten :point_left: files from your terminal

disk-forensicsforensicsdata-recovery+1
1.8k3 months ago
pcapfex preview

pcapfex

GitHubvikwin/pcapfex

'Packet Capture Forensic Evidence eXtractor' is a tool that finds and extracts files from packet capture files
packet-sniffing-analysisnetwork-forensicsforensics+2
2296 years ago
android-locdump preview

android-locdump

GitHubpacketlss/android-locdump

android location service cache dumper
android-securityforensicsinformation-gathering+4
17913 years ago
MK4001MTD-USB-Bridge preview

MK4001MTD-USB-Bridge

GitHubwill127534/mk4001mtd-usb-bridge

RP2040 firmware that bridges a Toshiba MK4001MTD 0.85" SDIO microdrive as a USB mass storage device, implementing the full SDIO-ATA protocol stack…

embedded-systems-securityreverse-engineeringdata-recovery+4
423 months ago
truehunter preview

truehunter

GitHubadoreste/truehunter

Truehunter

disk-forensicsencryption-decryption-toolsforensics+2
317 years ago
aws-firmware-dump preview

aws-firmware-dump

GitHubradkawar/aws-firmware-dump

Acquires the EBS disks of an AWS AMI you can launch, streaming snapshots via EBS direct APIs to a private S3 bucket with sha256 manifests and…
cloud-infrastructure-securitydisk-forensicsscripting-automation+5
2811 days ago
tools preview

tools

GitHubthreatlabz/tools

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

encryption-decryption-toolsreverse-engineeringdata-recovery+4
10223 days ago
Previous1…456…9Next








