
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
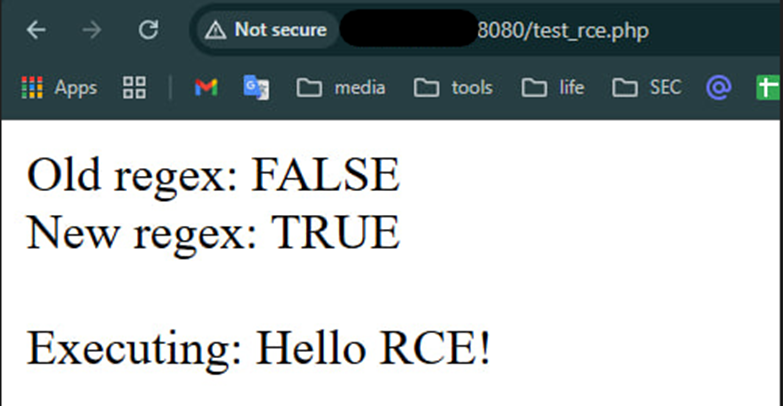
 soltanali0/cve-2024-12877-exploit
Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…
 ravi-lk/cve-2024-51482-zoneminder-v1.37.-1.37.64-sql-injection-poc
ZoneMinder Time-Based SQL Injection (CVE-2024-51482) Exploit POC
 d0cnull/nextjs-cve-2025-55182
Proof-of-concept exploit for critical unauthenticated RCE in Next.js Server Actions via React Flight Protocol deserialization, enabling arbitrary…
 ahmedf000/cve-2025-49132_htb_season10
Unauthenticated RCE exploit for CVE-2025-49132 in Pterodactyl Panel via path traversal, PEAR command injection, and PHP code execution. Includes HTB…
 erhui-li/cve-2024-51482-zoneminder-cctv-htb-reliable-exp
Performing multiple time-based blind injections for the same character and selecting the most frequent result significantly reduces errors and…
 sn0wbaall/cve-2024-23334-poc
Automated proof-of-concept exploit for CVE-2024-23334, a path traversal vulnerability in aiohttp, enabling remote directory traversal and…
 rahul-securify/react2shell-cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182 demonstrating remote code execution in Next.js via prototype pollution. Includes a pre-configured…
 fankh/cve-2025-55182-test-lab-windows
Docker-based test lab for CVE-2025-55182 (React2Shell) RCE vulnerability in React 19.1.0/Next.js 15.1.0. Includes exploit scripts, WAF bypass testing…
 carlosaruy/cve-2025-55182
a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…
 nxploited/cve-2025-5304
PT Project Notebooks 1.0.0 - 1.1.3 - Missing Authorization to Unauthenticated Privilege Escalation
 threatradarai/trai-001-critical-rce-vulnerability-in-apache-parquet-cve-2025-30065-simulation
A CVSS 10.0-rated vulnerability in the parquet-avro Java module allows remote code execution via unsafe deserialization when parsing schemas. Tracked…
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 pasan2002/cve-2019-9053---cms-made-simple-sql-injection-exploit-modified-
This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…
 rishi-kaul/n8n-cve-2025-68613
Research and exploitation toolkit for CVE-2025-68613, a critical RCE in n8n. Includes root cause analysis, exploit development, browser-based PoC,…
 wired0ut/cve-2012-6422
An exploitation for the /dev/exynos-mem vulnerability introduced in earlier samsung phones.
 hrmtz/snet
AI-guided CTF - Break into a real server with Claude Code as your trainer
 goultarde/cve-2025-55182-react2shell-lab
CTF lab environment exploiting CVE-2025-55182 (RCE in React Server Components) with vulnerable Next.js blog, detection scripts, and manual exploit…








