
 #1
Capture The Flag platforms, challenge creation, solving tools, and competitive cybersecurity frameworks.
Kitploit recommended
 pixel-defaultbr/cve-2023-50164
Educational exploit for CVE-2023-50164 (Apache Struts 2) demonstrating path traversal and remote code execution via malicious file upload, designed…
 androidteacher/cve-2025-64424-coolify-
Containerized CTF lab for learning and exploiting CVE-2025-64424, a command injection RCE in Coolify. Includes vulnerable environment, walkthrough,…
 heymrsalt/ais3-2024-project-d5team
Reappear-CVE-2022-21449-TLS-PoC
 mrintern/thm_steelmountain_cve-2014-6287
a python3 version of the exploit written for CVE-2014-6287. Useful for completing the "Steel Mountain" room on TryHackMe.com without the use of…
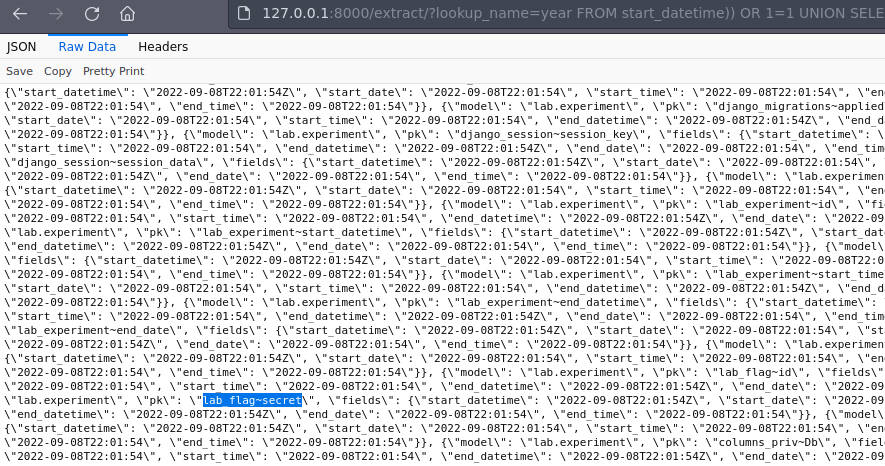 lnwza0x0a/ctf_django_cve-2022-34265
Docker-based CTF challenge demonstrating SQL injection in Django's Trunc() and Extract() database functions (CVE-2022-34265) with UNION-based payload…
 amusedx/cve-2026-22686
CTF challenge focused on sandbox escape via source code review of a JavaScript execution environment, designed for hands-on vulnerability analysis…
 the-cyber-ledger/tcl-xss-labs
An interactive, self-hosted XSS training platform with 33 progressively harder challenges
 ethicalpap/cve-2025-29775
Educational lab environment demonstrating SAMLStorm (CVE-2025-29775) vulnerability in xml-crypto library. Includes vulnerable SAML service provider,…
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 arnavps/ctf-web-exploitation
A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
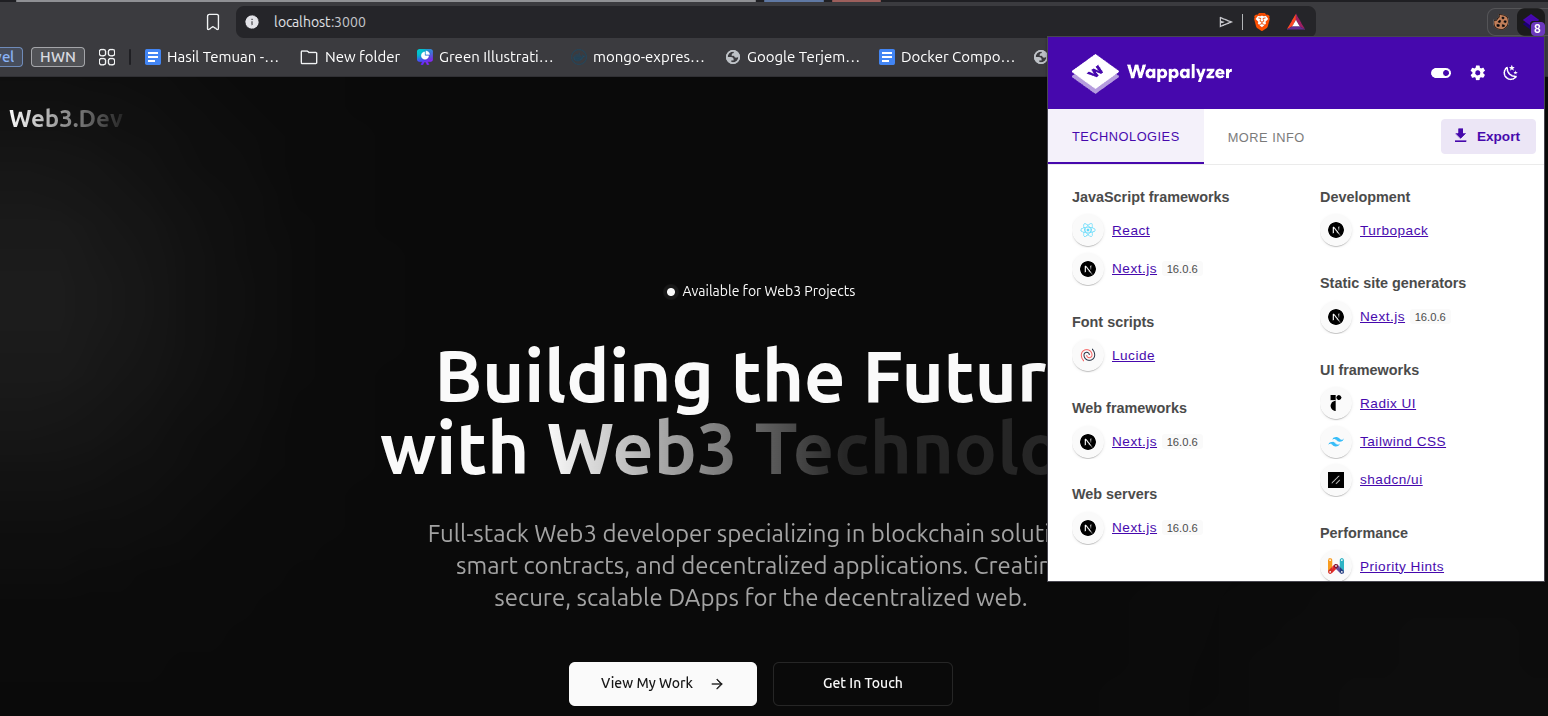 xxxtectationxxx/react2shell-cve-lab
A self-hosted vulnerable Next.js environment running on Docker for simulating CVE-2025-55182. Built for educational security research and CTF…
 trailofbits/break-golf
Cryptanalysis golf: break schemes and prove it in Lean 4. Proof-of-concept board.
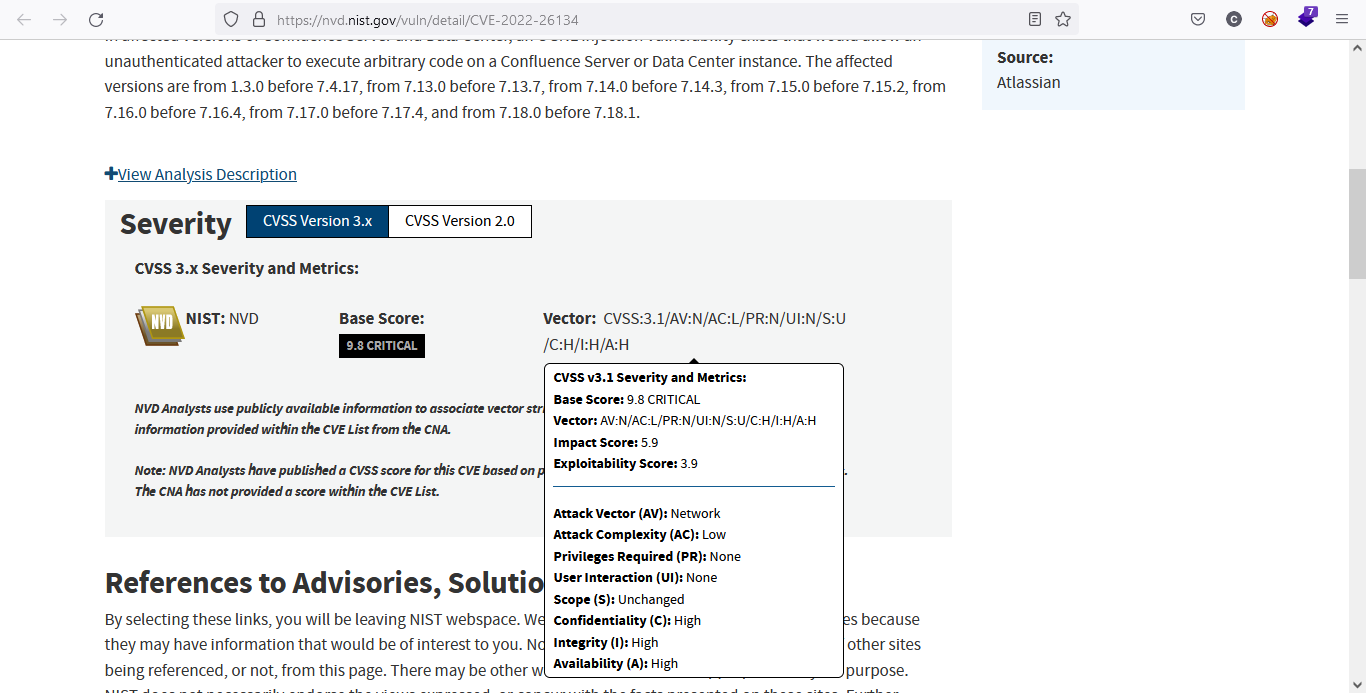 r1skkam/tryhackme-atlassian-cve-2022-26134
Atlassian, CVE-2022-26134 An interactive lab showcasing the Confluence Server and Data Center un-authenticated RCE vulnerability.
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
 eddieoz/dual-ec-drbg
Educational Jupyter notebook demonstrating the Dual_EC_DRBG cryptographic backdoor (CVE-2014-8610) with NIST P-256 state recovery attack, historical…
 0xw1ld/cve-2026-29000
Rust-based exploit generator for CVE-2026-29000, an authentication bypass in pac4j-jwt via alg:none JWT nested in JWE, automating JWKS retrieval and…
 fazaroot/cve-2025-2539---file-away-wordpress-plugin-arbitrary-file-read
Authenticated arbitrary file read exploit for the File Away WordPress plugin (CVE-2025-2539). Includes PoC, attack flow, detection signatures, and…
 pouriam23/vulnerability-in-remix-react-router-cve-2025-31137-
CTF challenge replicating CVE-2025-31137 in Remix/React Router Express. Learn to exploit a server-side vulnerability to find the admin flag.








