 #1
Tools for implementing, analyzing, breaking, and implementing cryptographic systems and algorithms.
Kitploit recommended
 mdsecactivebreach/dragoncastle
A PoC that combines AutodialDLL lateral movement technique and SSP to scrape NTLM hashes from LSASS process.
 st1lly/dc-sonar
Analyzing AD domains for security risks related to user accounts
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 kira2040k/redbloodc2
Node.js command-and-control server with FUD payload generation, encrypted communication, session management, and modules for data exfiltration and…
 kimci86/bkcrack
Crack legacy zip encryption with Biham and Kocher's known plaintext attack.
 tls-attacker/tls-scanner
Automated TLS server and client configuration scanner for pentesters and researchers. Evaluates cipher suites, protocol versions, and security…
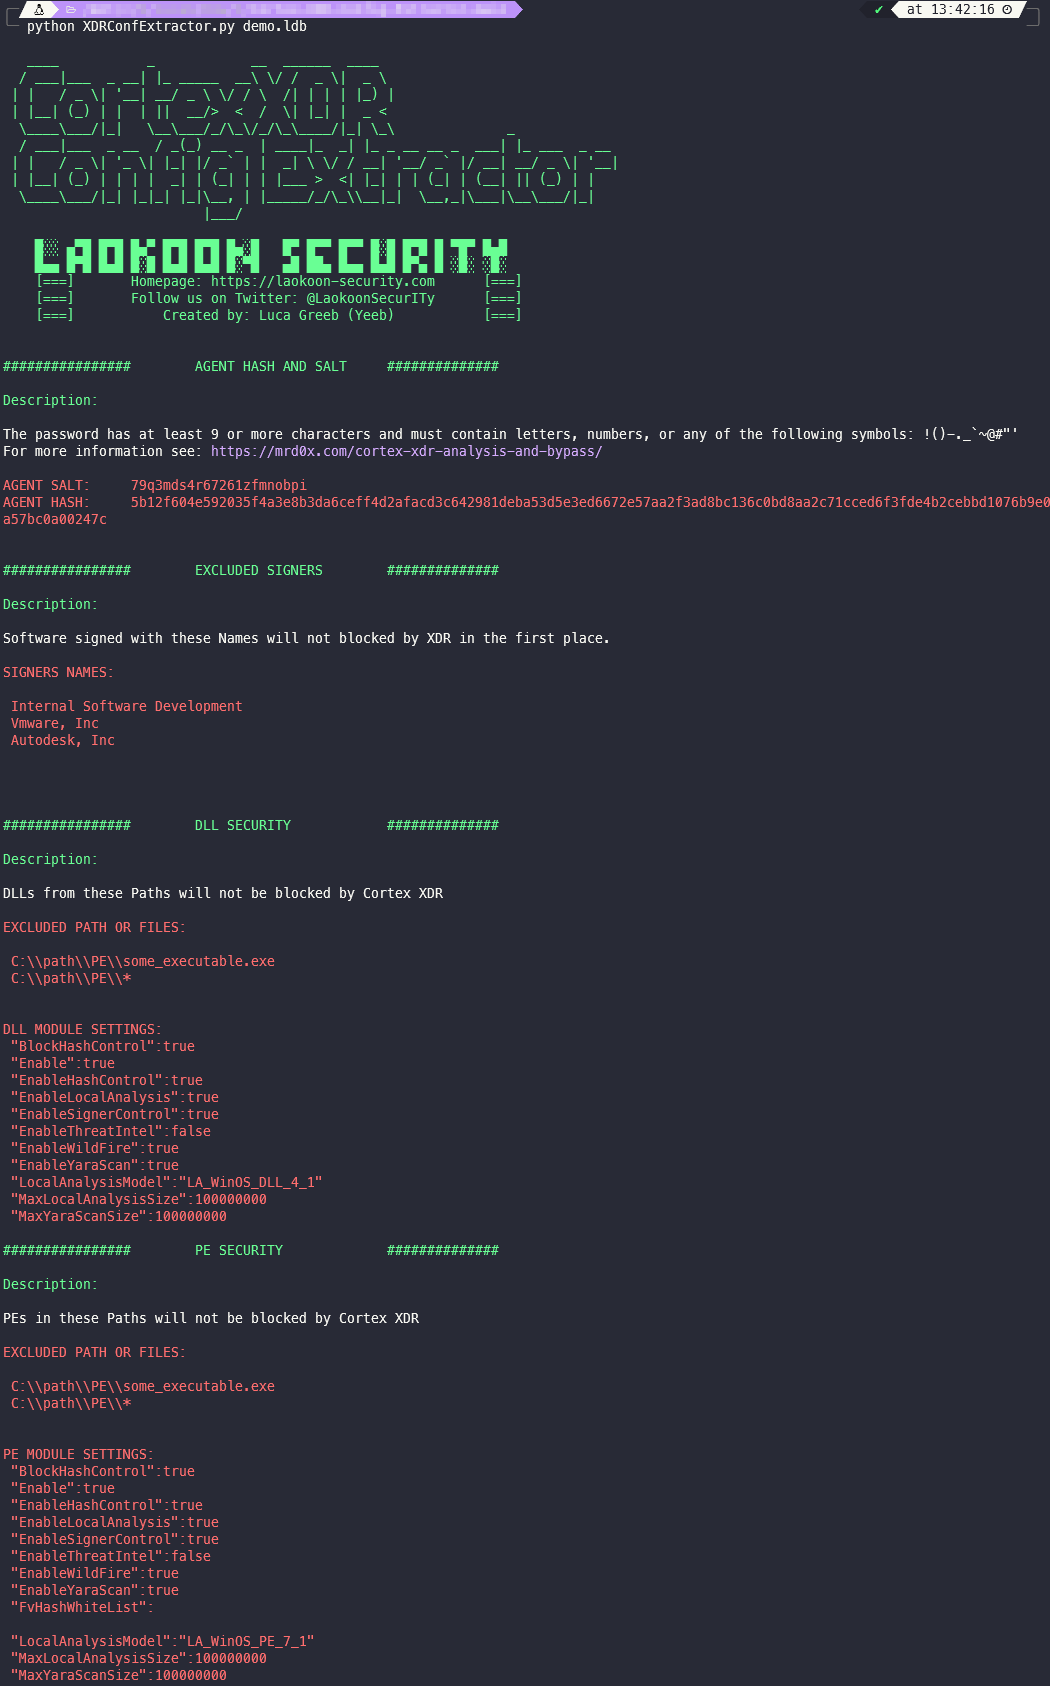 laokoon-security/cortex-xdr-config-extractor
Parses Cortex XDR agent database lock files to extract agent settings, uninstall password hash/salt, and security exclusions for red team assessments…
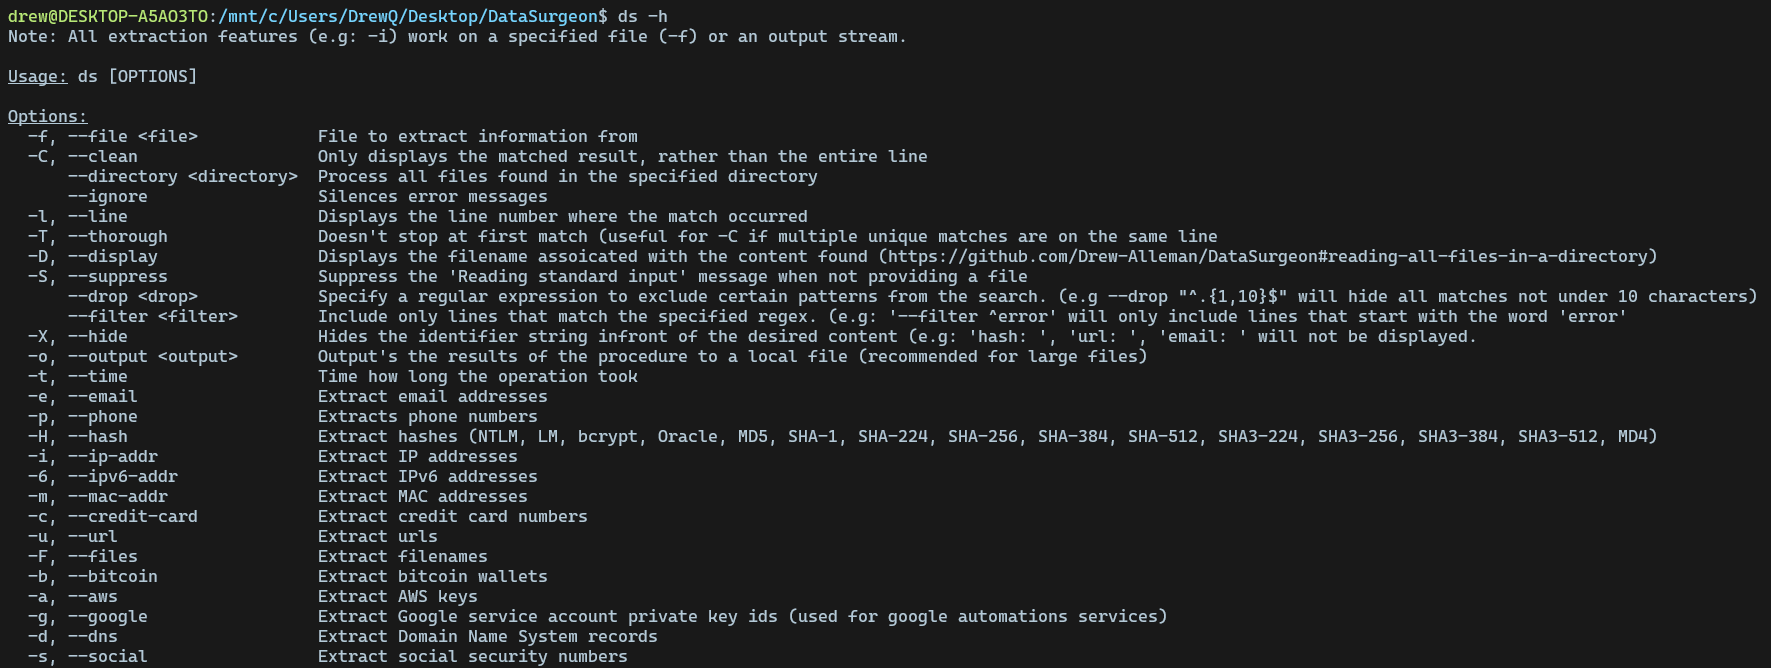 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
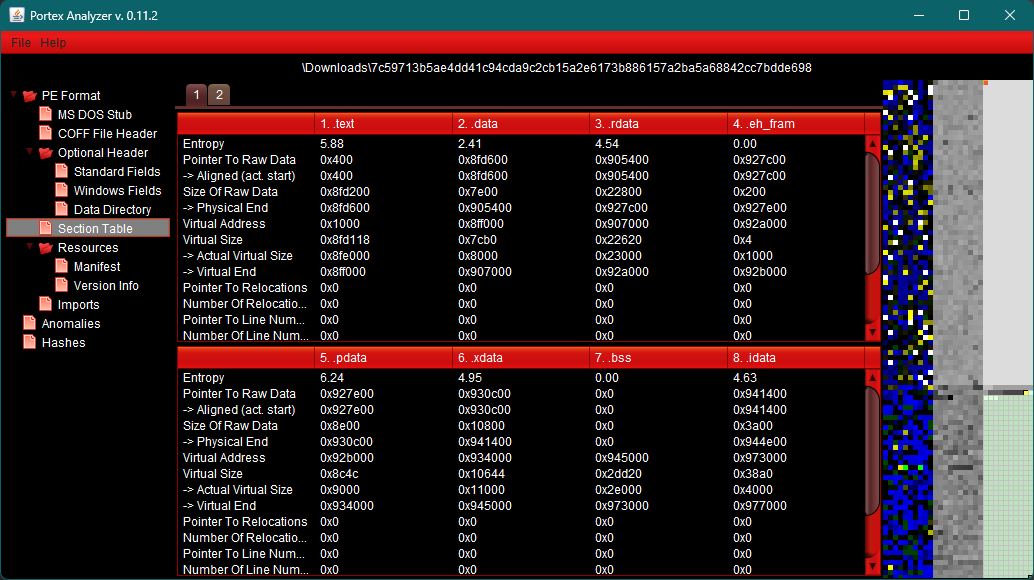 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
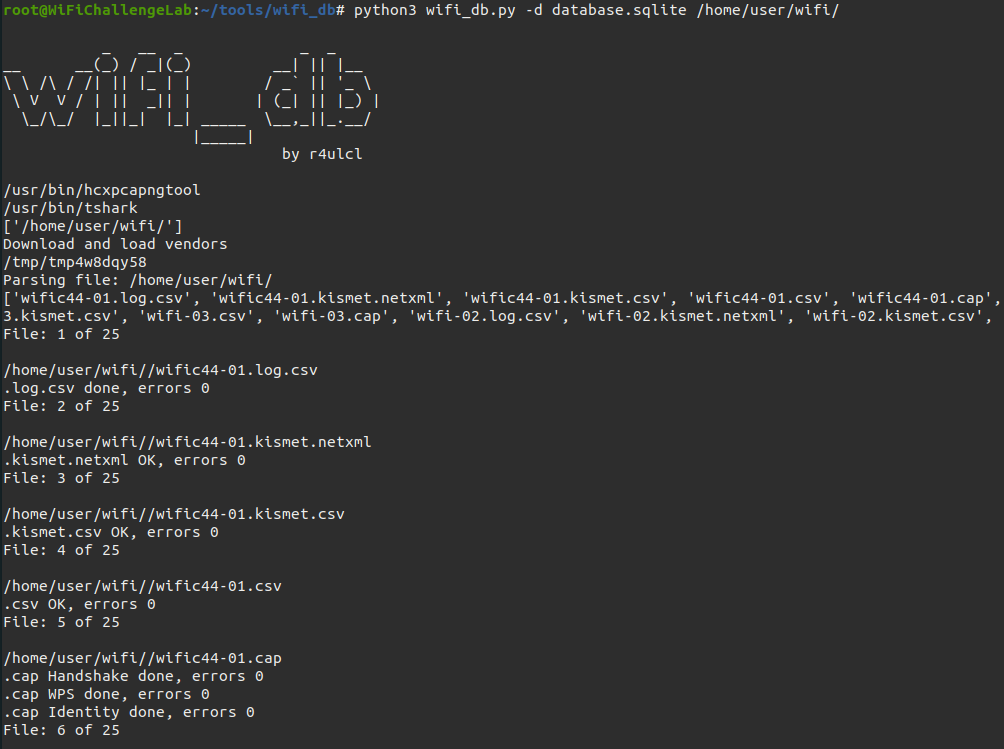 r4ulcl/wifi_db
Script to parse Aircrack-ng captures into a SQLite database and extract useful information like handshakes, MGT identities, interesting relations…
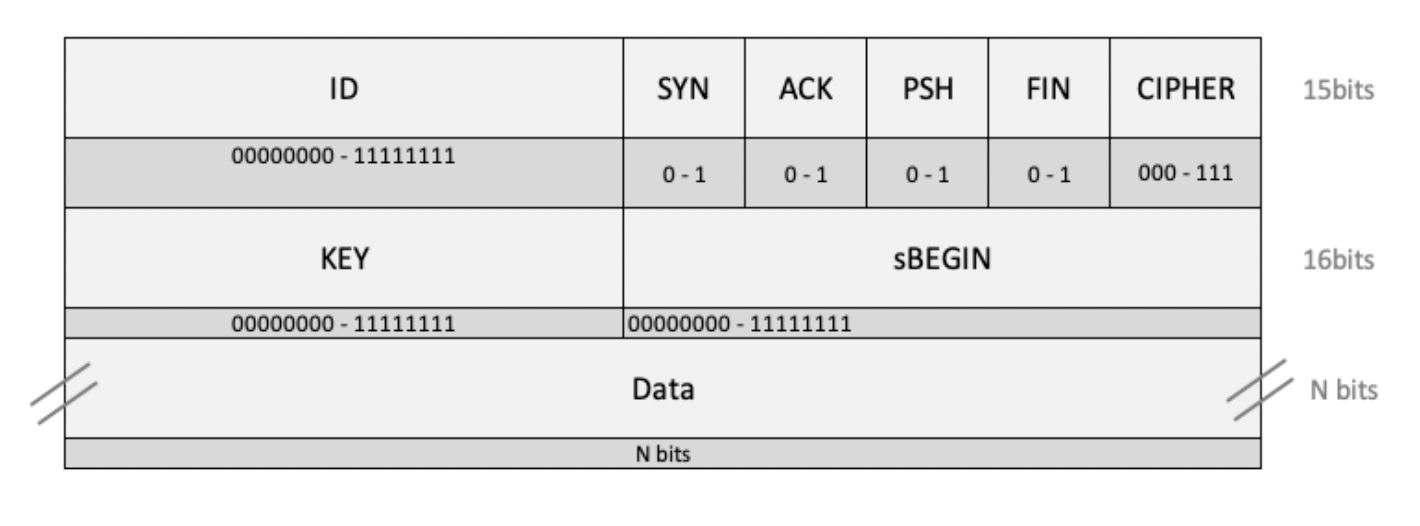 telefonica/sdk-sms-stack
Framework providing TCP/IP-like characteristics over GSM SMS with AES+CTR encryption, enabling secure, ordered message streams for device-to-device…
 ciscocxsecurity/creddump7
Offline Windows credential extractor that dumps LM/NT hashes, cached domain passwords, and LSA secrets from registry hives without relying on system…
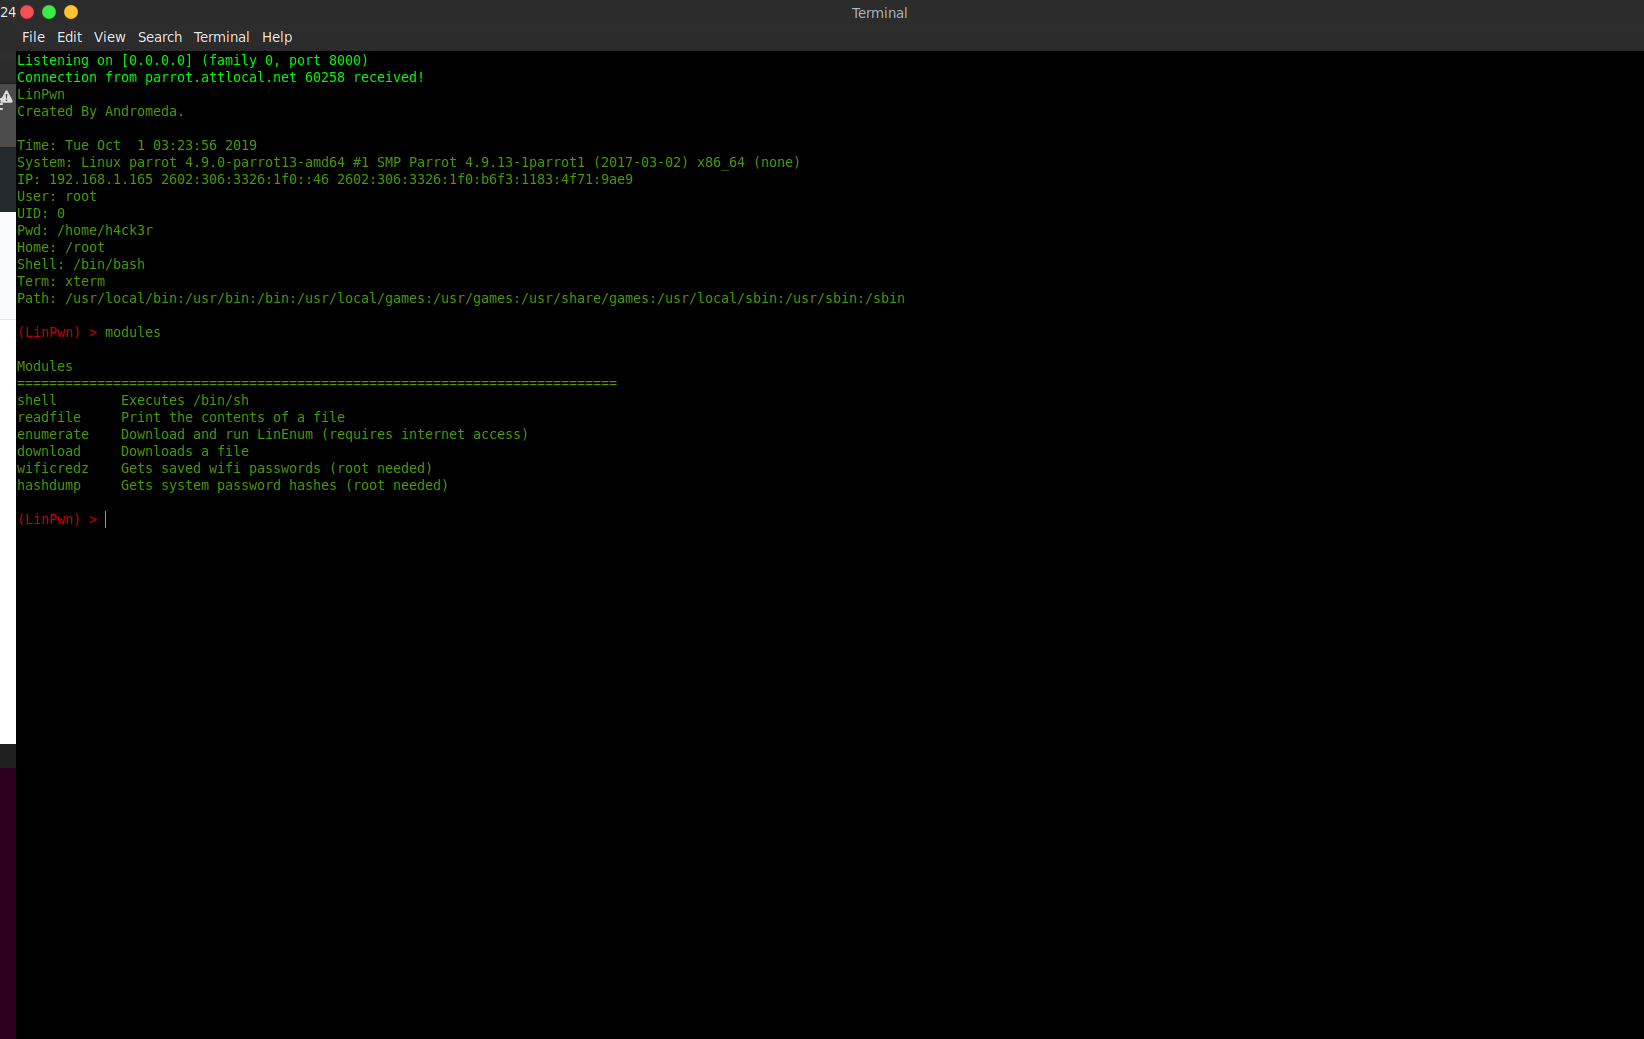 andromeda1957/linpwn
Interactive post-exploitation tool for Linux privilege escalation, enumeration, file exfiltration, and credential harvesting via reverse shell.
 thatcherclough/betterbackdoor
A backdoor with a multitude of features.
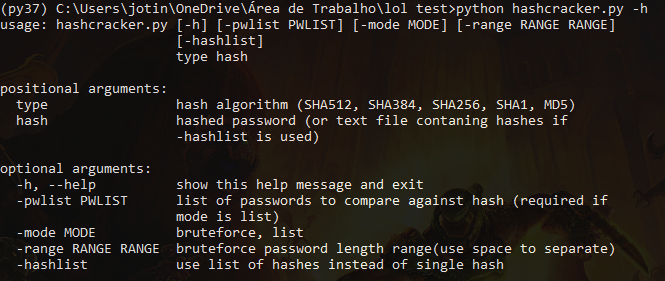 joaovdonaton/hashcracker
Python-based hash cracker supporting SHA512, SHA256, SHA1, MD5, and more. Features auto-detection of hash type, bruteforce, and password list modes…
 aaaguirrep/offensive-docker
Offensive Docker is an image with the more used offensive tools to create an environment easily and quickly to launch assessment to the targets.
 jasondrawdy/memorymapper
Lightweight library which allows the ability to map both native and managed assemblies into memory by either using process injection of a process…
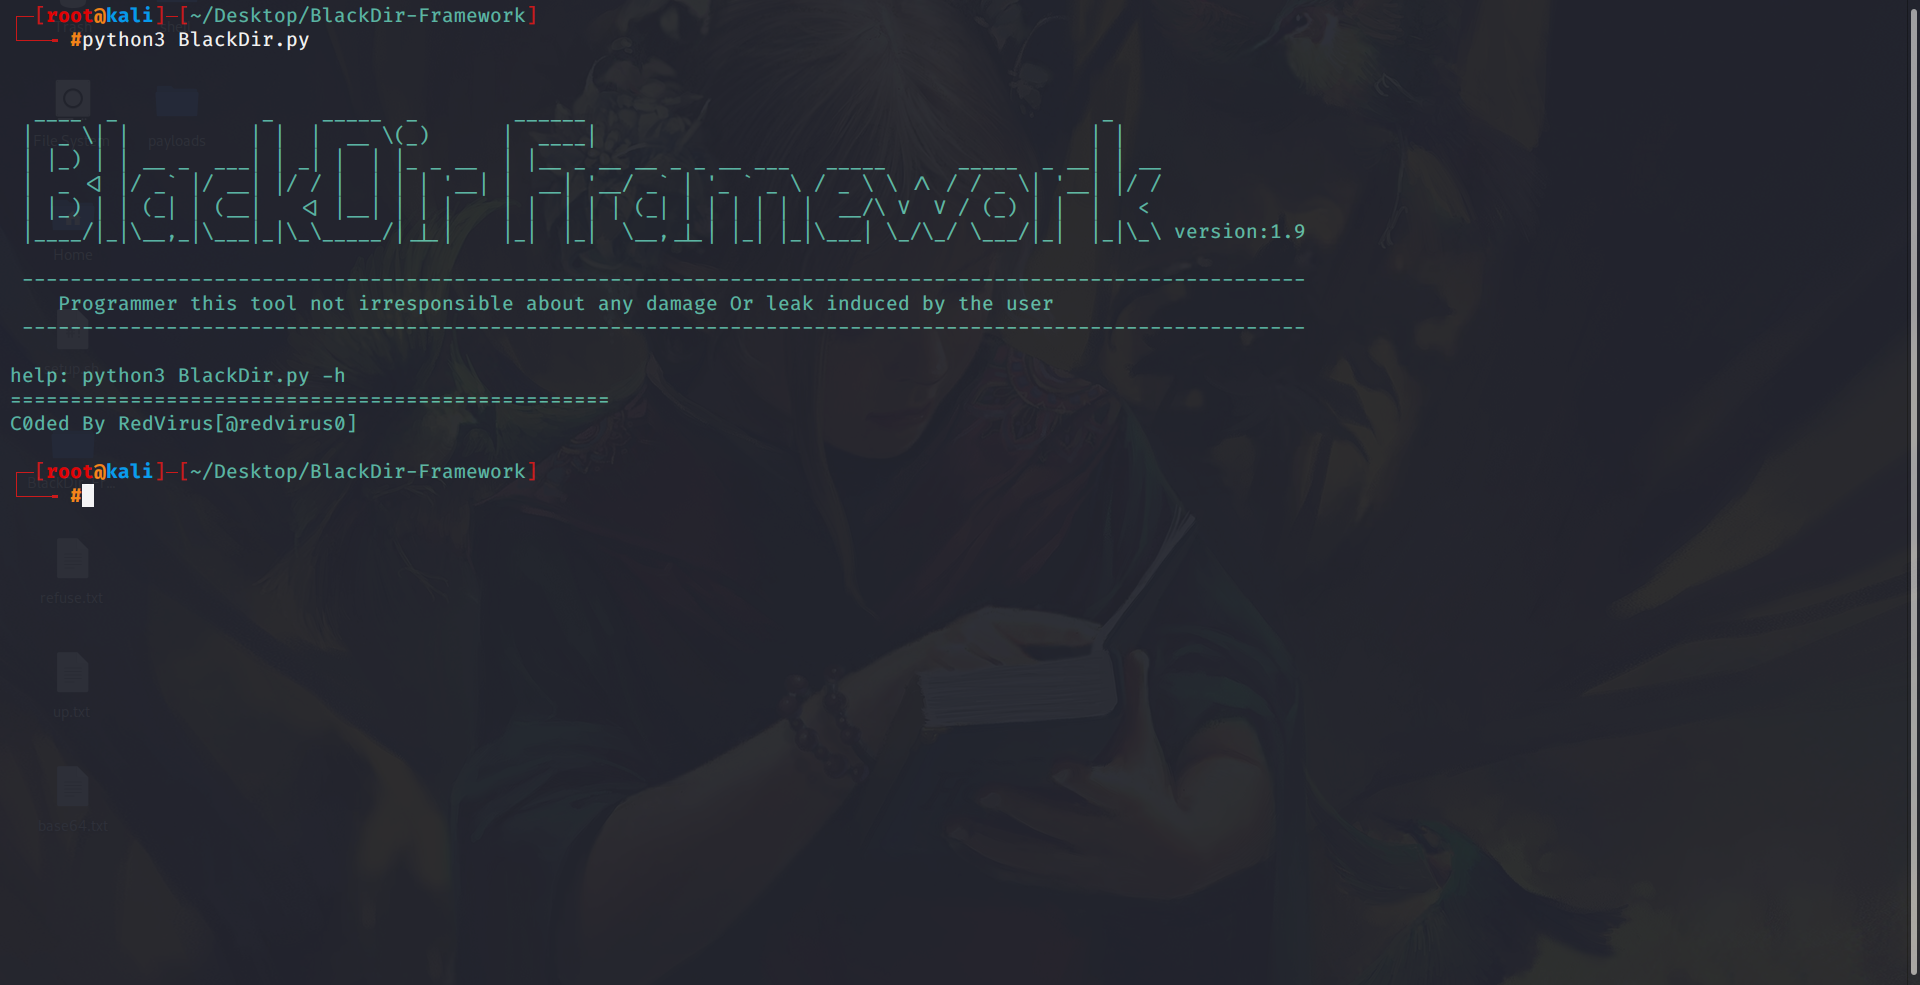 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner