
 #1
Tools for reviewing system and application configurations for security weaknesses and compliance.
Kitploit recommended
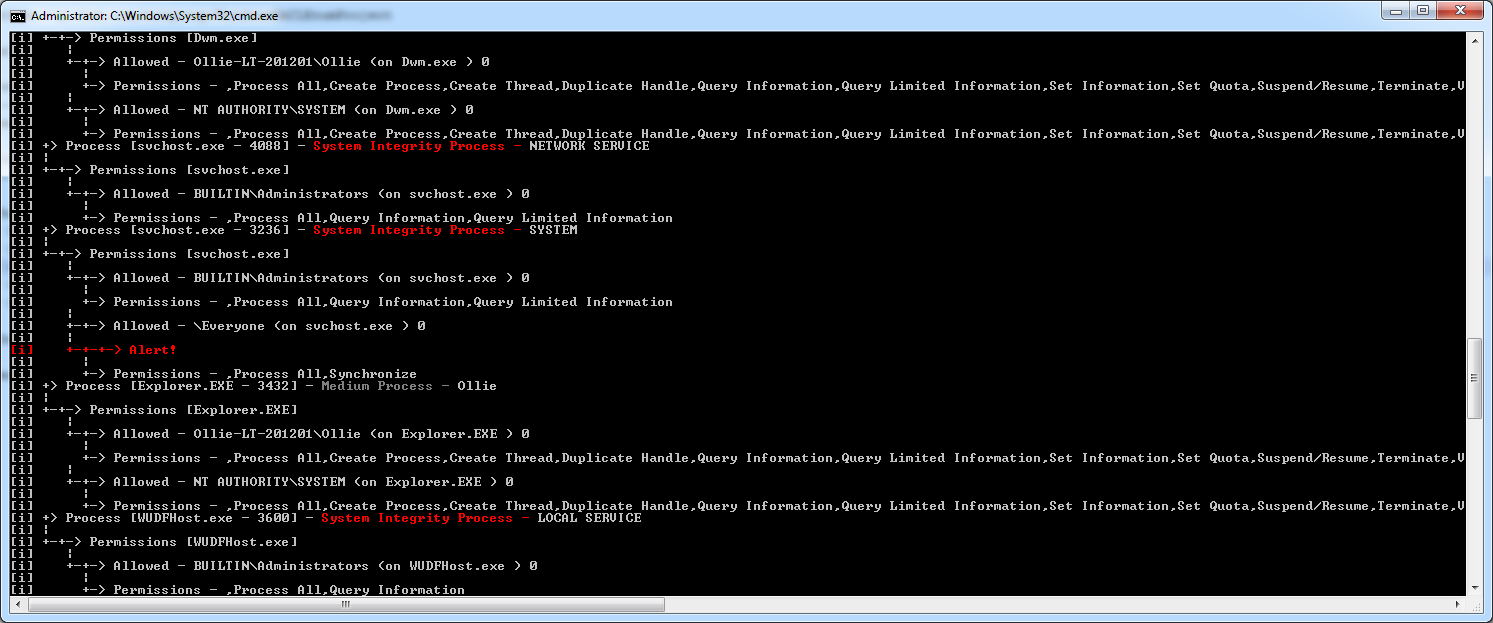
 nccgroup/windowsdaclenumproject
A collection of tools to enumerate and analyse Windows DACLs
 otrf/set-auditrule
Useful access control entries (ACE) on system access control list (SACL) of securable objects to find potential adversarial activity
 owasp/kubelight
OWASP Kubernetes security and compliance tool [WIP]
 appliscale/cloud-security-audit
A command line security audit tool for Amazon Web Services
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
 blacksky-algorithms/atproto
Fork of the AT Protocol reference implementation with performance-optimized AppView, Rust-based firehose indexer, Redis caching, and community…
 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 nccgroup/conmachi
Container Blackbox Security Auditing Tool: enumerates security configuration from within the target container
 kiprotect/kodex
A privacy and security engineering toolkit: Discover, understand, pseudonymize, anonymize, encrypt and securely share sensitive and personal data:…
 stintel/vallumd
Centralize or distribute IPset blacklists
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 t3l3machus/aceshark
ACEshark is a utility designed for rapid extraction and analysis of Windows service configurations and Access Control Entries, eliminating the need…
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
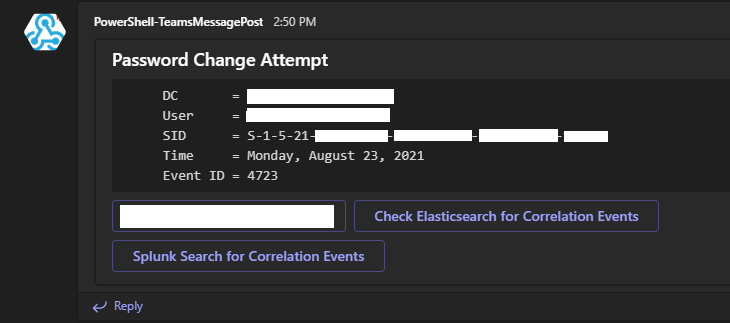 osbornepro/btps-secpack
PowerShell-based security toolkit for small-to-medium enterprises, providing automated alerts, Active Directory hardening, Windows Event Forwarding,…
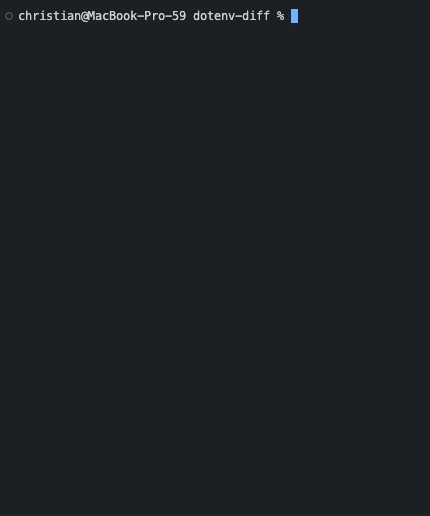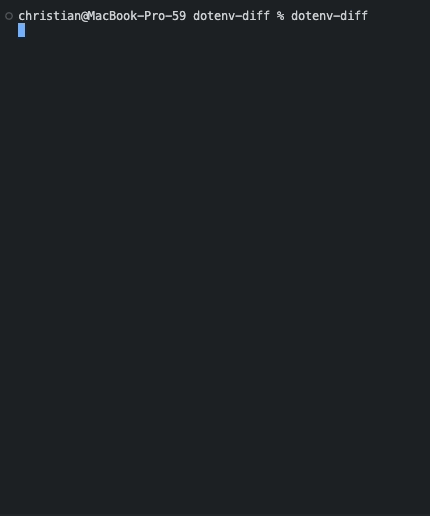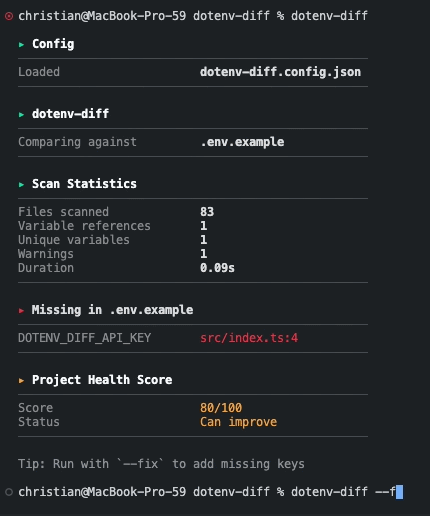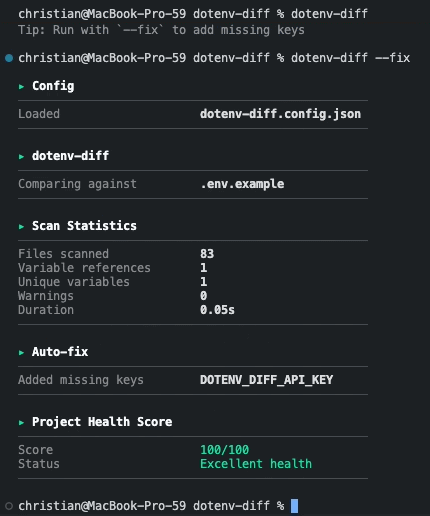 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 xfhg/intercept
INTERCEPT / Policy as Code Auditing
 nicholasjackson/cnitch
Container Snitch checks running processes under the Docker Engine and alerts if any are found to be running as root
 synacktiv/shh
Systemd Hardening Helper - Mirror of https://github.com/desbma/shh








