
 #1
Tools for reviewing system and application configurations for security weaknesses and compliance.
Kitploit recommended
 nickanderson/cfengine-cve-2016-2118
An example detection and remediation policy.
 rexifiles/rex-sec-glibc
glibc check and update in light of CVE-2015-7547
 nccgroup/cisco-snmp-enumeration
Automated Cisco SNMP Enumeration, Brute Force, Configuration Download and Password Cracking
 f88/ghostbusters15
Playbooks 'Fix for CVE-2015-0235(GHOST)' running on Ansible
 gina-alaska/bash-cve-2014-7169-cookbook
Chef cookbook to detect and patch the Shellshock (CVE-2014-7169) bash vulnerability across servers using automated configuration management.
 cloudpassage/mangy-beast
CloudPassage Halo policy for detecting vulnerability to CVE-2014-3566 (AKA POODLE)
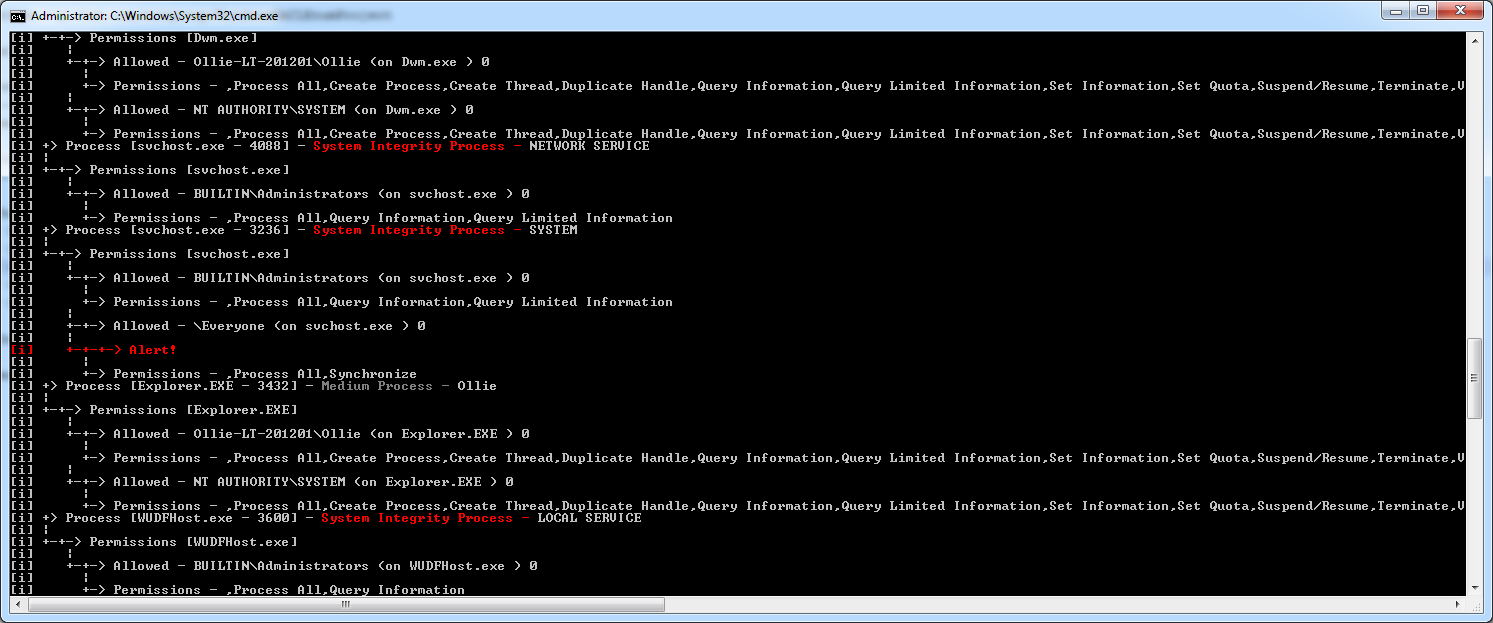 nccgroup/windowsdaclenumproject
A collection of tools to enumerate and analyse Windows DACLs
 averagesecurityguy/prometheus
Prometheus Firewall Analyzer
 niccox/patch-openssl-cve-2014-0291_cve-2015-0204
Ansible playbook to patch OpenSSL against CVE-2014-0291 and CVE-2015-0204 on Red Hat family servers, with automated service restart and verification.
 ehabhussein/snmpvlan
SNMP scanner and brute-forcer targeting Cisco Nexus switches (5000/6000) to exploit CVE-2014-3341, enumerate VLANs, crack SNMP community strings, and…
 koudaiii-archives/cookbook-update-glibc
cookbook for update glibc. CVE-2015-0235(GHOST)
 aaronfay/cve-2015-0235-test
Ansible playbook to check vulnerability for CVE-2015-0235
 adherzog/ansible-cve-2015-0235-ghost
Ansible playbook, to check for CVE-2015-0235 (GHOST) vulnerability
 mikesplain/cve-2015-0235-cookbook
A chef cookbook to test the GHOST vulnerability
 macminivault/ntpupdatesnowleopard
Updates OS X 10.6.8 NTP to include patch for CVE-2014-9295
 jdauphant/patch-openssl-cve-2014-0160
Patch openssl #heartbleed with ansible
 mikesplain/cve-2014-3566-poodle-cookbook
Chef cookbook that detects and fails runs on servers vulnerable to CVE-2014-3566 (POODLE) by scanning specified SSL ports, serving as both a security…
 isecpartners/sslyze
Current development of SSLyze now takes place on a separate repository








