#1

 bfuzzy/auditd-attack
A Linux Auditd rule set mapped to MITRE's Attack Framework
 lxkxc/vmxnet3hunter
Use this tool to prioritize cluster patching for the recent VMware advisory VMSA-2018-0027 related to CVE-2018-6981 and CVE-2018-6982.
 andypitcher/check_struts
Apache Struts version analyzer (Ansible) based on CVE-2017-5638
 gquere/cve-2018-16987
Technical disclosure of CVE-2018-16987: cleartext storage of external service passwords in Squash TM administration panel, with CVSS 4.1 scoring and…
 nsacyber/detect-cve-2017-15361-tpm
Detects Windows and Linux systems with enabled Trusted Platform Modules (TPM) vulnerable to CVE-2017-15361. #nsacyber
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 vulnerscom/vulners-scanner
Vulnerability scanner based on vulners.com audit API
 foospidy/dbdat
Db Database Assessment Tool
 malindarathnayake/intel-cve-2018-3639-mitigation_registryupdate
PowerShell script to apply Windows registry mitigation for CVE-2018-3639 (Speculative Store Bypass), enabling automated security hardening against…
 ymgh96/detecting-the-patch-of-cve-2018-1010
C++ utility that checks Windows OS version and detects whether the patch for CVE-2018-1010 is installed using systeminfo and wmic commands.
 sirpsycho/firecall
Automate SSH communication with firewalls, switches, etc.
 leonbroseliske/cfc
Centralized Firewall Control
 jdmulloy/meltdown-aws-scanner
Naive shell script to verify Meltdown (CVE-2017-5754) patch status of EC2 instances
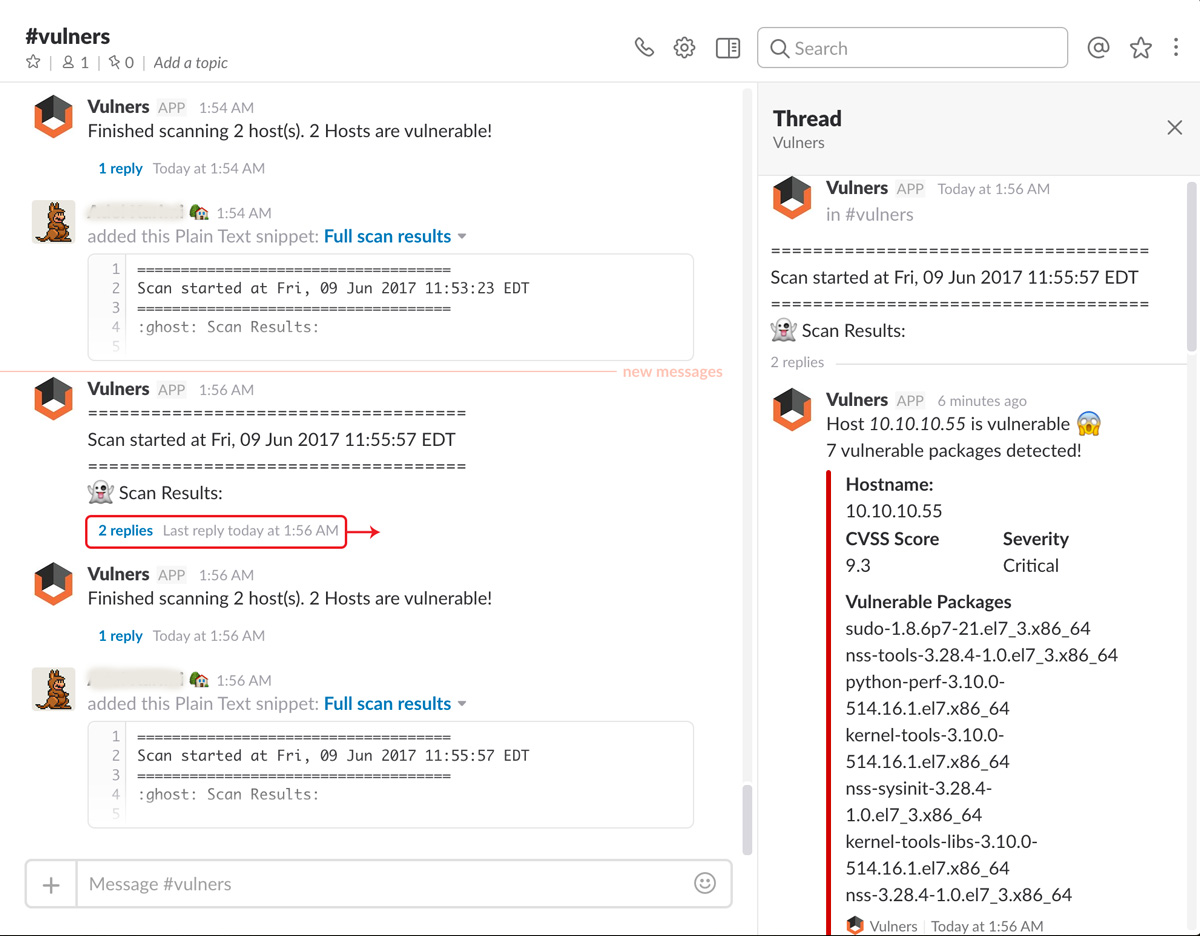 0x4d31/salt-scanner
Linux vulnerability scanner based on Salt Open and Vulners audit API, with Slack notifications and JIRA integration
 nicholasjackson/cnitch
Container Snitch checks running processes under the Docker Engine and alerts if any are found to be running as root
 americanhanko/windows-security-cve-2017-8543
InSpec profile to verify a node is patched and compliant for CVE-2017-8543