
 #1
Tools for assessing, testing, and securing cloud environments (AWS, Azure, GCP) and their services.
Kitploit recommended
 deepfence/threatmapper
Open Source Cloud Native Application Protection Platform (CNAPP)
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 cyberstrikeus/cyberstrike
Autonomous AI red team agent for penetration testing with 13+ specialized agents, 120+ OWASP test cases, and MITRE ATT&CK integration. Supports 15+…
 kubearmor/kubearmor
Runtime Security Enforcement System. Workload hardening/sandboxing and implementing least-permissive policies made easy leveraging LSMs (LSM-BPF,…
 duo-labs/cloudmapper
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 browserbox/browserbox
💚🇺🇸🗽Secure remote browsing anywhere, any way you like it.
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
 onecli/onecli
Open-source sandboxed agent harness for teams. Giving every employee a secured personal agent.
 zerobootdev/zeroboot
Sub-millisecond VM sandboxes for AI agents via copy-on-write forking
 madhuakula/kubernetes-goat
Intentionally vulnerable Kubernetes cluster environment for hands-on security training. Includes 22+ scenarios covering container escape, RBAC…
 cloudflare/flan
A pretty sweet vulnerability scanner
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
 splunk/attack_range
A tool that allows you to create vulnerable instrumented local or cloud environments to simulate attacks against and collect the data into Splunk
 usmannasir/cyberpanel
Cyber Panel - The hosting control panel for OpenLiteSpeed
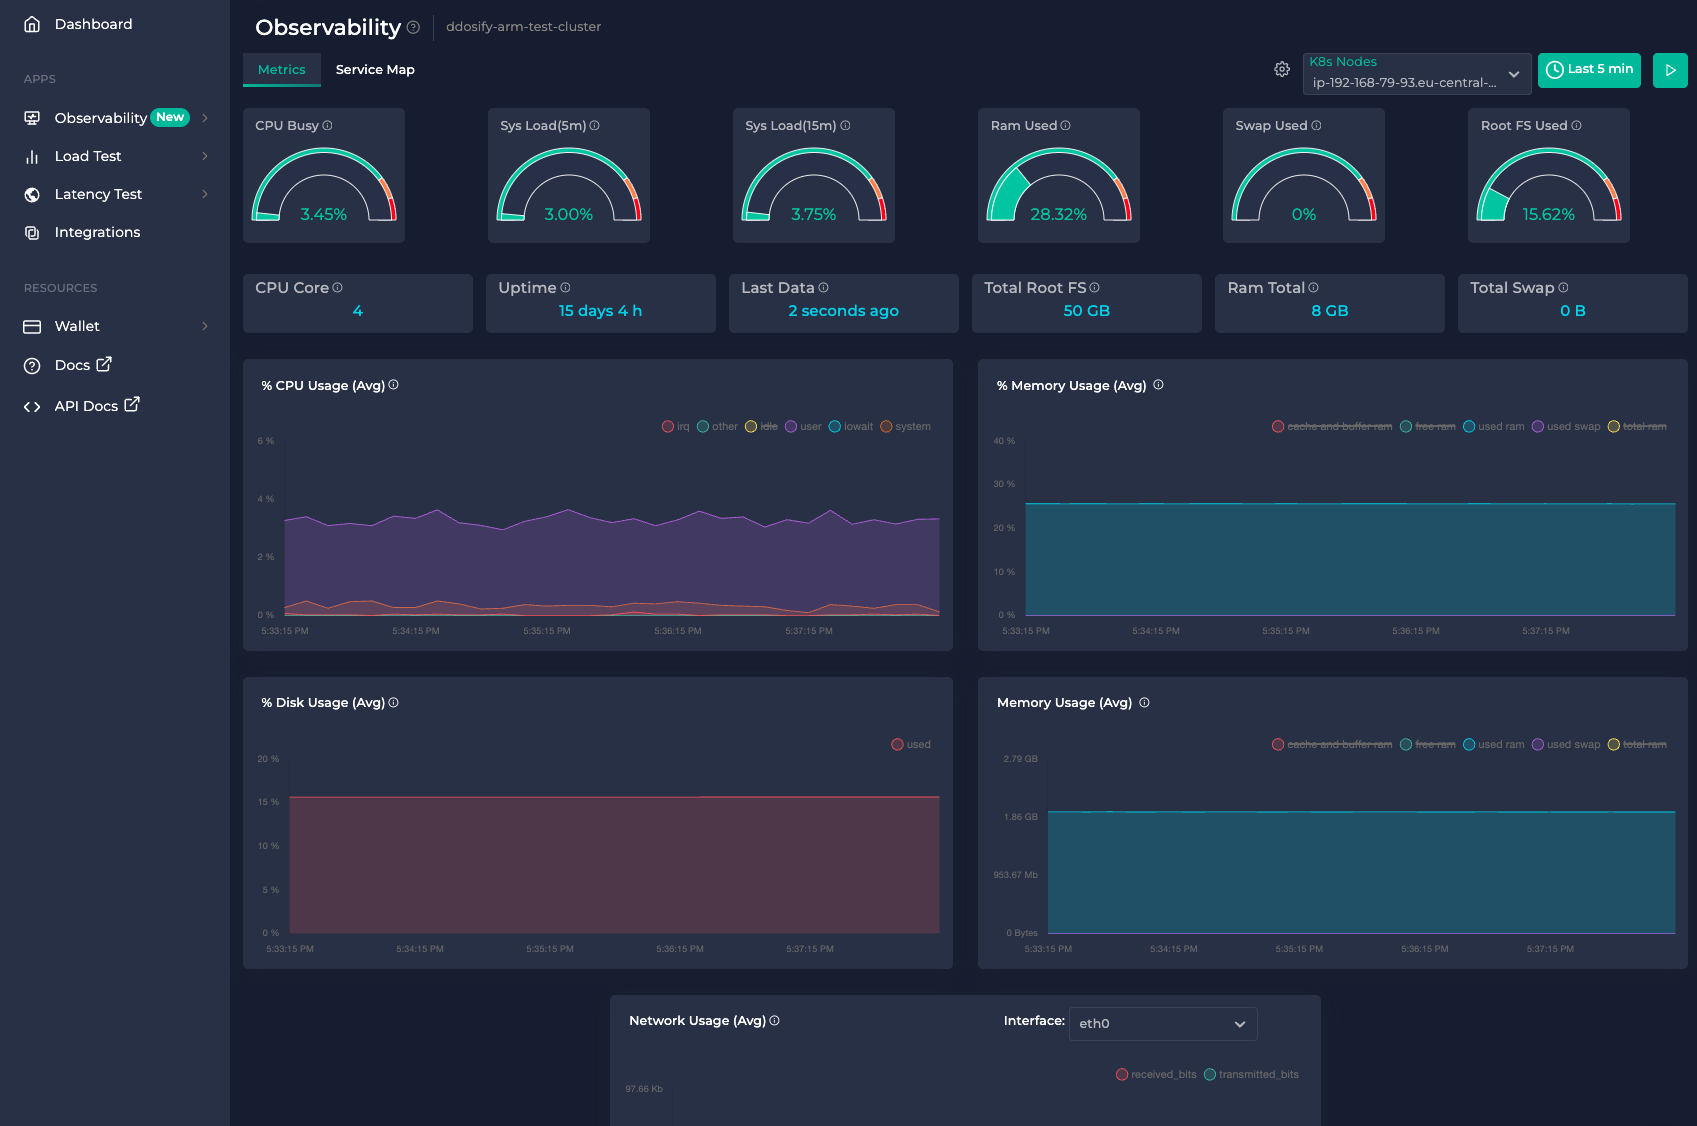 getanteon/anteon
eBPF-powered Kubernetes monitoring and performance testing platform that automatically generates service maps, tracks real-time metrics, and runs…






