
 #1
Binary exploitation techniques, ROP chains, heap exploitation, format strings, and memory corruption research.
Kitploit recommended
 yaunsky/cve-2021-3156
cve-2021-3156;sudo堆溢出漏洞;漏洞检测
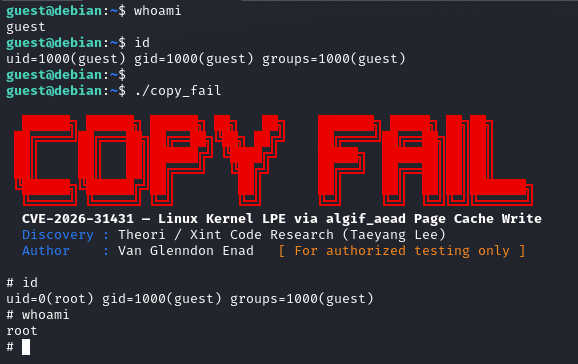 sl4ck0th/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 littlelailo/incomplete-exploit-for-cve-2018-4150-bpf-filter-poc-
Proof-of-concept exploit for CVE-2018-4150 targeting macOS kernel BPF filter on devices without SMAP. Demonstrates local privilege escalation via…
 mbanyamer/cve-2025-11001---7-zip
CVE-2025-11001 (CVSS 7.0) – 7-Zip < 25.00 Directory Traversal → RCE via crafted ZIP with symlink. Allows arbitrary file write when extracted as…
 sec-zone/cve-2026-36213
CVE-2026-36213 | Local Privilege Escalation in MEmu Android Emulator 9.2.7.0 via Insecure Service Binary Permissions | Patched in 9.3.2
 0x06060606/cve-2023-41993
CVE-2023-41993
 p4x1s/cve-2023-0386
CVE-2023-0386 EXP
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 bigwario/copy-fail-cve-2026-31431-c
C exploit for CVE-2026-31431, targeting multiple Ubuntu and Kali versions with x86_64 and ARM64 builds.
 piffd0s/ntoskrnl-metadata
eprocess offset puller for relevant member offsets and function addresses for cve-2026-40369
 modulexcite/systracingpoc
CVE-2020-0668 - Microsoft Windows Service Tracing Arbitrary File Move Local Privilege Escalation Vulnerability
 mbanyamer/msc-eviltwin-local-privilege-escalation
CVE-2025-26633 (CVSS 7.8) – Zero-day MMC .msc EvilTwin LPE actively exploited by Water Gamayun APT. PoC creates local admin via malicious MSC file on…
 xerxes-2/cve-2026-31431-rs
Rust-based proof-of-concept for CVE-2026-31431, exploiting AF_ALG and splice to overwrite /bin/su and spawn a root shell. Self-contained no_std…
 vnik5287/cve-2016-6187-poc
cve-2016-6187
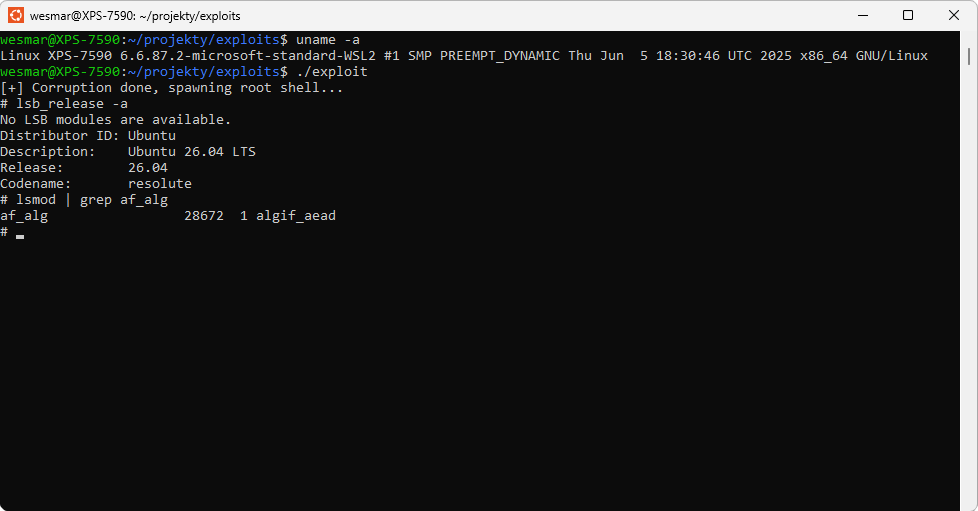 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
 segura2010/lenovo-dispatcher-poc
PoC to exploit lenovo dispatcher driver (LnvMSRIO.sys) (CVE-2025-8061)








