
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
 zxj-hub/cve-2024-41713poc
Mitel MiCollab 企业协作平台 任意文件读取漏洞(CVE-2024-41713)由于Mitel MiCollab软件的 NuPoint 统一消息 (NPM) 组件中存在身份验证绕过漏洞,并且输入验证不足,未经身份验证的远程攻击者可利用该漏洞执行路径遍历攻击,成功利用可能导致未授权访问、破…
 thetrueartist/abo.cms-login-sqli-cve-2024-25227
Unauthenticated SQL injection exploit for ABO.CMS 5.8 enabling login bypass and database takeover via the tb_login parameter.
 cve-2024/cve-2024-4898-poc
Proof-of-concept exploit for CVE-2024-4898, a missing authorization vulnerability in InstaWP Connect WordPress plugin allowing unauthenticated API…
 azhao1981/cve-2021-29441
Exploit for CVE-2021-29441 targeting Alibaba Nacos to add unauthorized accounts, enabling authentication bypass and unauthorized access.
 thejoyofhacking/securabv-cve-2020-1472
Python script using Impacket to test for the Zerologon vulnerability (CVE-2020-1472) by attempting Netlogon authentication bypass against domain…
 anonymous-family/cve-2020-1472
Test tool for CVE-2020-1472
 yowise/cve-2022-26923
Detailed technical write-up and proof-of-concept for CVE-2022-26923, an Active Directory Certificate Services privilege escalation vulnerability,…
 shoucheng3/jenkinsci__git-client-plugin_cve-2019-10392_2-8-4
Jenkins plugin providing Git APIs for automated repository operations including fetch, checkout, merge, and tag, with support for credential-based…
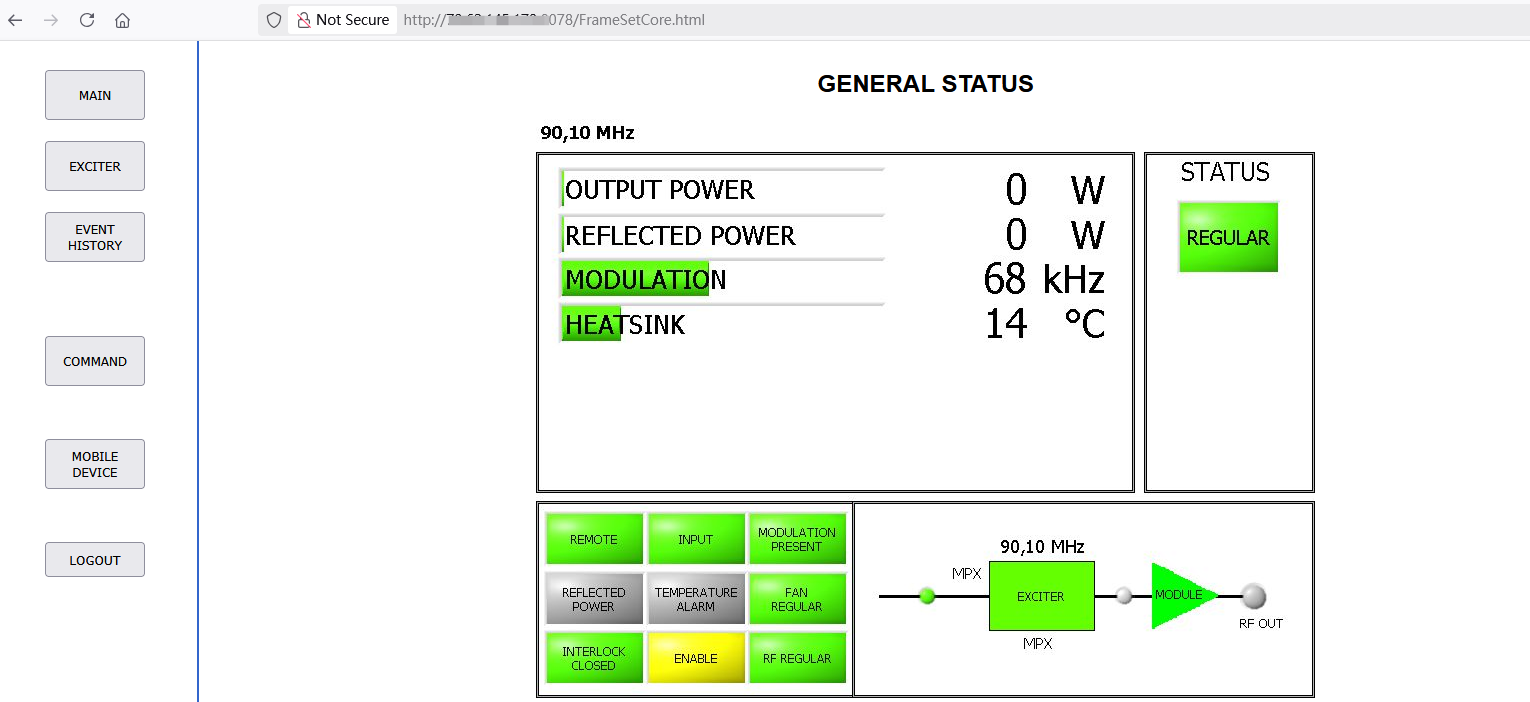 p0et08/electrolink-fm-dab-tv
There is a POC for CVE-2025-51040 in Electrolink FM/DAB/TV Transmitter Web Management System Unauthorized access vulnerability
 stefandorresteijn/cve-2021-39409
Admin account registration in Online Student Rate System
 nxploited/cve-2025-1639
Animation Addons for Elementor Pro <= 1.6 - Missing Authorization to Authenticated (Subscriber+) Arbitrary Plugin Installation/Activation
 lcartey/proftpd-cve-2019-12815
Exploit for CVE-2019-12815 in ProFTPD 1.3.x, a configurable FTP daemon with virtual users, multiple authentication methods, and modular architecture…
 julesbsz/cve-2024-10924
POC for CVE-2024-10924 written in Python
 wtn-arny/vmware-esxi
CVE-2024-37085 unauthenticated shell upload to full administrator on domain-joined esxi hypervisors.
 ken-abruzzi/cve-2020-1472
Python script to test domain controllers for CVE-2020-1472 (Zerologon) using Impacket. Performs Netlogon authentication bypass detection with minimal…
 underprotection/cve-2020-24029
Proof-of-concept for CVE-2020-24029: unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege…
 puckiestyle/cve-2022-40684
Proof-of-concept exploit for CVE-2022-40684 authentication bypass in Fortinet FortiOS, FortiProxy, and FortiSwitchManager, enabling SSH key injection…
 jrbh4ck/cve-2024-27198
PoC about CVE-2024-27198








