
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
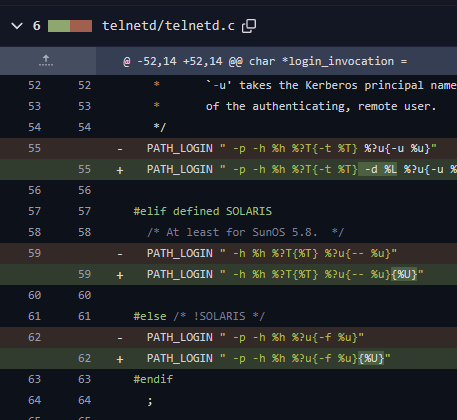
 lucaspdiniz/cve-2026-24061
Vulnerability in GNU InetUtils telnetd Enables Remote Root Access
 ready2disclose/cve-2022-43110
CVE-2022-43110
 0xmandor/cve-2025-50433
Proof of concept for a critical Monnit Cloud account takeover (CVE-2025-50433), exploiting missing token-email validation in password reset and…
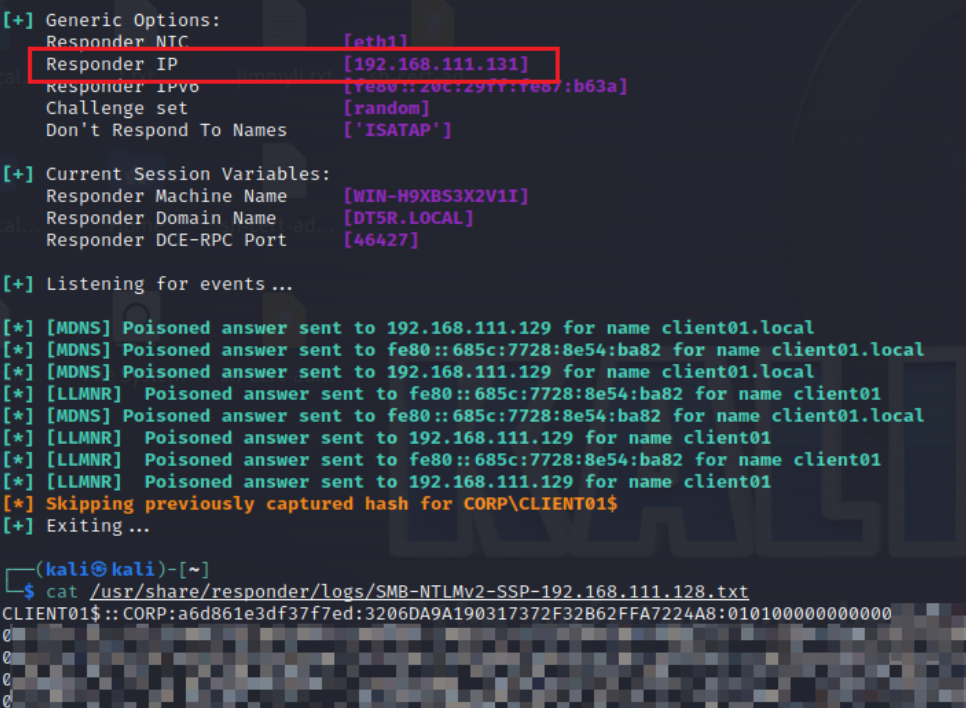 hagrid29/cve-2024-40586-windows-coerced-authentication-in-forticlient
Exploit for CVE-2024-40586: coerces Windows hosts to authenticate via a vulnerable FortiClient named pipe, enabling privilege escalation to SYSTEM or…
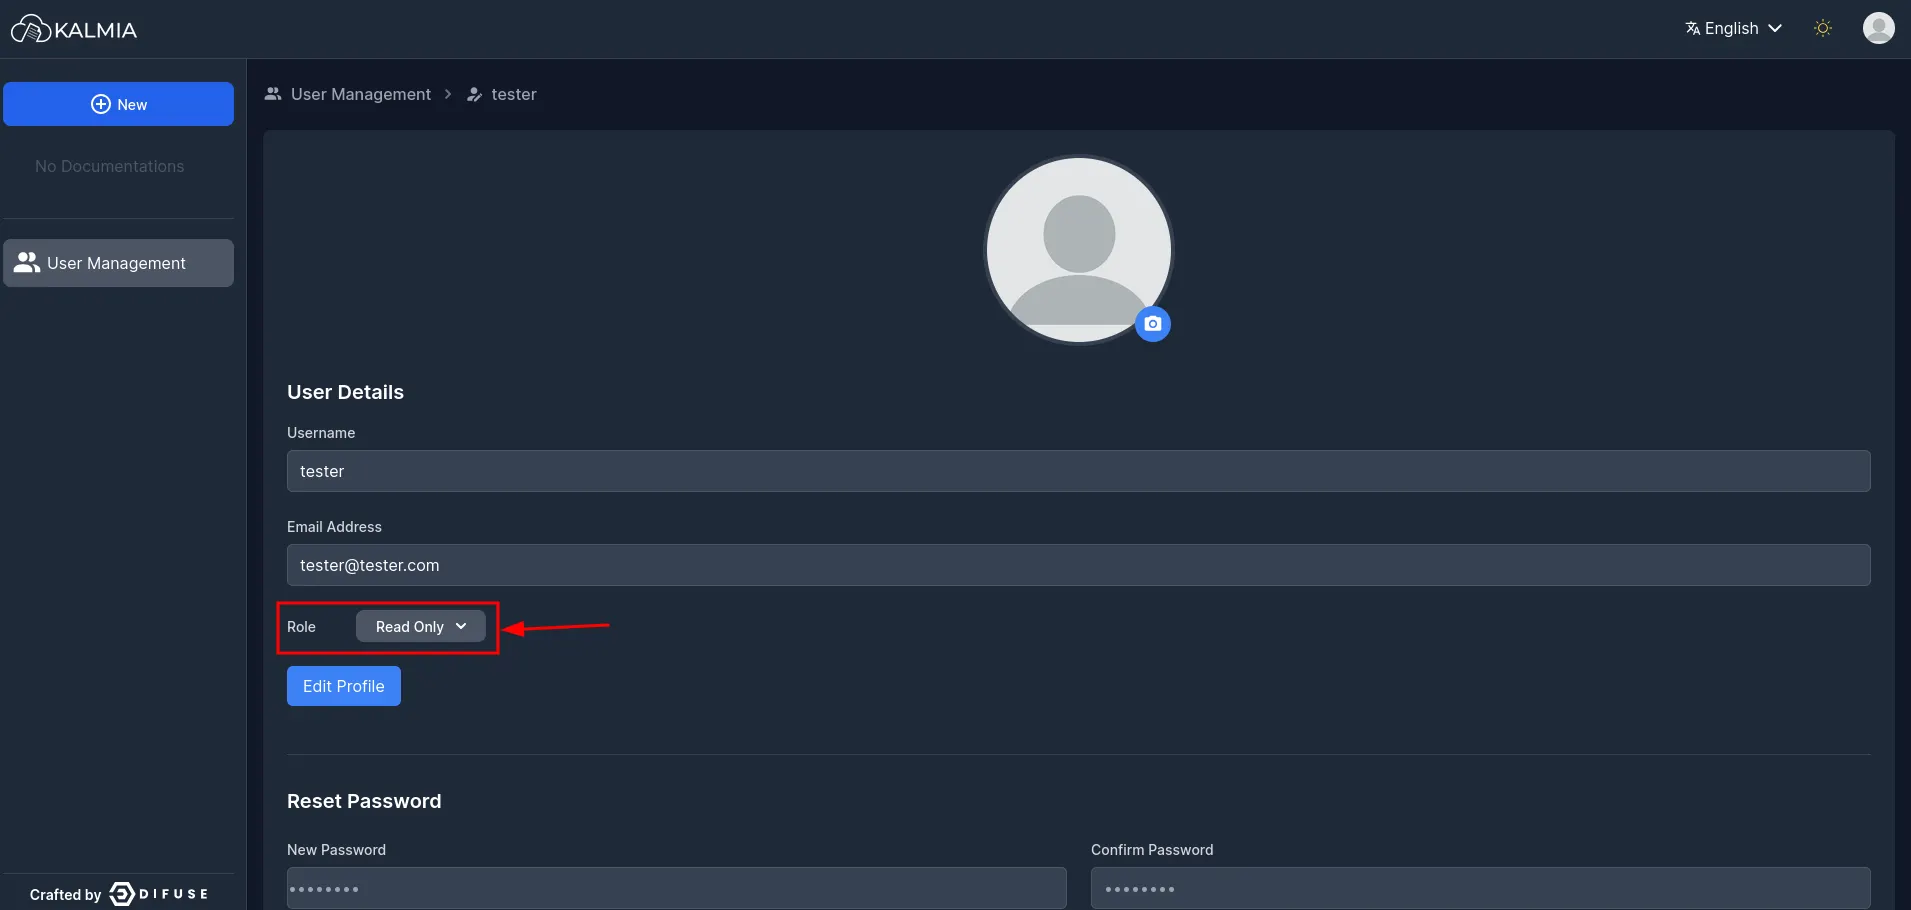 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 d0n601/buffalo
A python3 multithreaded SSH dictionary attack tool
 nxvh1337/cve-2025-15602-poc
Snipe-IT < 8.3.7 Mass Assignment Vulnerability Leading to Privilege Escalation
 clearcdq/zabbix-saml-sso-_cve-2022-23131
Exploit for CVE-2022-23131 targeting Zabbix SAML SSO authentication bypass vulnerability. Enables session hijacking and unauthorized admin access.
 realbatuhan/jwt-bruteforcer
Jwt Bruteforcer with CVE-2018-1000531 Test
 ccordeiro/cve-2022-40684
PoC for CVE-2022-40684 - Authentication bypass lead to Full device takeover (Read-only)
 jfriedli/cve-2025-11986
Proof-of-concept exploit for CVE-2025-11986 demonstrating unauthenticated access bypass in WordPress crypto_connect plugin via nonce extraction and…
 cappricio-securities/cve-2022-21500
Oracle E-Business Suite <=12.2 - Authentication Bypass
 imjdl/cve-2026-31816-rshell
Exploits CVE-2026-31816 in Budibase to bypass authentication, upload a malicious datasource plugin, and execute a reverse shell for remote access.
 0xblackash/cve-2025-13315
CVE-2025-13315
 nrtlox/cve-2025-63587
CVE-2025-63587
 zgsnj123/cve-2025-45466
It is the details of CVE-2025-45466
 b4d-53ct0r/cve-2025-3616
Metasploit module exploiting arbitrary file upload in Greenshift WordPress plugin (CVE-2025-3616) to achieve RCE via MIME spoofing, with…








