
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
 bigzooooz/cve-2022-31294
Online Discussion Forum Site 1.0 - Account Takeover
 yucaerin/cve-2025-4322
Motors <= 5.6.67 - Unauthenticated Privilege Escalation via Password Update/Account Takeover
 sangsenimanwartefak/cve-2026-7458
Python proof-of-concept exploit for CVE-2026-7458, an unauthenticated authentication bypass in PickPlugins User Verification WordPress plugin via…
 izxci/cve-2026-8809
Advanced Custom Fields: Extended <= 0.9.2.5 - Unauthenticated Privilege Escalation via Validation Bypass to '_acf_post_id' Parameter
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 sanupl/cve-2021-46067
CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.
 pulentoski/explotacion-cve-2023-32315-openfire
Python exploit for CVE-2023-32315 targeting Openfire servers. Bypasses admin panel authentication via Unicode path traversal to create an…
 ex-cal1bur/cve-2026-44596
YAMCS yamcs-core < 5.12.7 lacks rate limiting on POST /auth/token. An unauthenticated attacker can perform unlimited brute-force attempts against any…
 nickpaulsec/2026-41940-poc
CVE-2026-41940: detect and exploit cpanel vuln
 chenjp/cve-2026-29145-tester
This repository contains a proof-of-concept (PoC) environment designed to test for CVE-2026-29145.
 michaeladamgroberman/cve-2025-1242
CVE-2025-1242: Hardcoded iothubowner Connection String — Gardyn Home Kit (ICSA-26-055-03)
 itres-labs/usbcoercer
USBCoercer turns an ESP32 development board with native USB-OTG into an Ethernet-over-USB gadget capable of coercing proxy configuration via WPAD.
 simoesctt/ctt-enhanced-apache-mod_auth_digest-timing-attack-exploit
Remote timing attack exploit for Apache mod_auth_digest (CVE-2026-33006) that bypasses Digest authentication via a 33-layer temporal cascade,…
 nefhara/cve-2022-26923
Automated CVE-2022-26923 Exploitation (Certifried)
 randomrobbiebf/sap-brute
SAP Netweaver Login Bruteforcer.
 0xrixet/craftcms-poc-cve-2026-31266
Security research on Craft CMS authentication mechanism
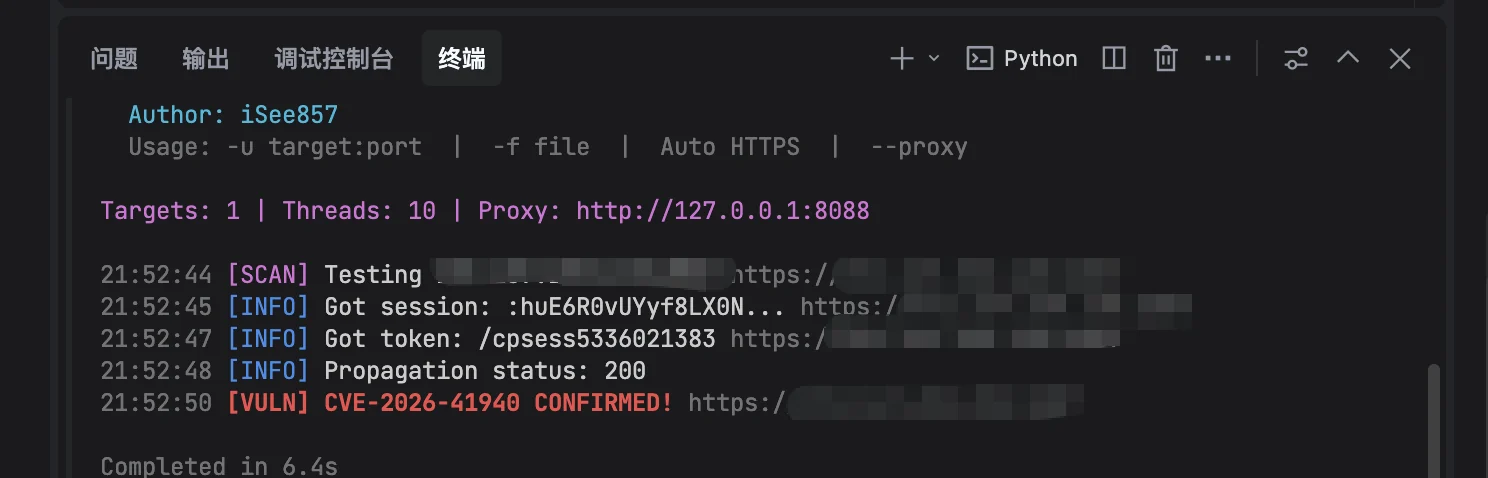 isee857/cpanel-whm-cve-2026-41940-authbypass
Scanner for cPanel & WHM authentication bypass (CVE-2026-41940) that detects vulnerable versions via CRLF injection and session manipulation, with…
 sangsenimanwartefak/cve-2026-23550
Bash exploit for CVE-2026-23550 that triggers unauthenticated WordPress admin login via crafted REST API request to Modular Connector's…








