
 #1
MFA, SSO, passwordless, biometric, and identity provider tools.
Kitploit recommended
 abraxas/element-fragment-guest
Element Web v1.12.29 - High - Remote - Session - fragment guest creds wipe a real session before whoami
 abraxas/phpmyadmin-config-set-2fa
phpMyAdmin 5.2.3 - High - Remote - 2FA - config/set clears two-factor
 abraxas/phpmyadmin-webauthn
phpMyAdmin 5.2.3 - High - Remote - 2FA skip - WebAuthn ceremony can be skipped
 mafifrizi/tanuki
Tactical Identity Operator for Linux & Hybrid Active Directory
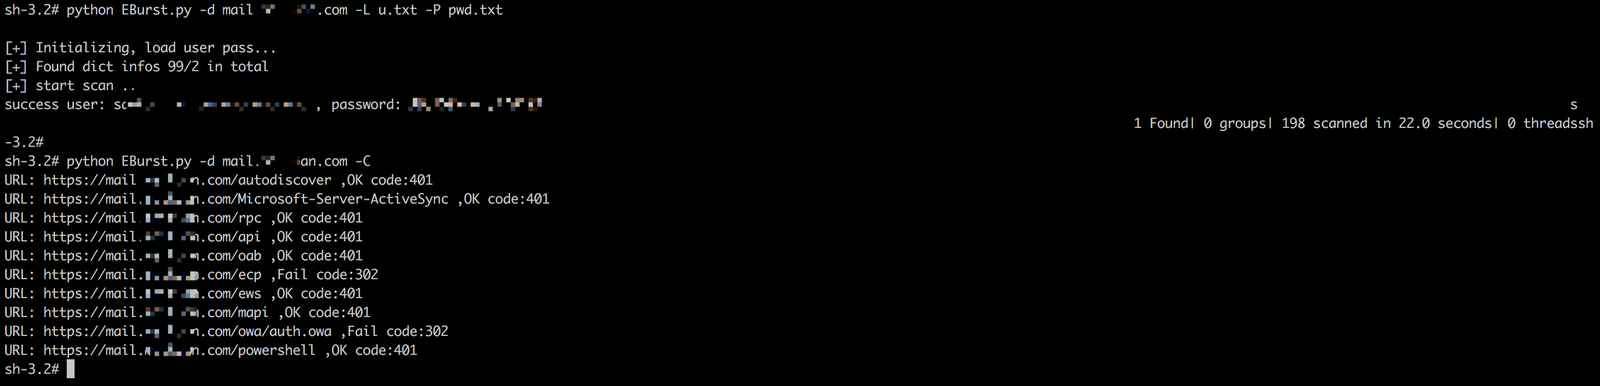 grayddq/eburst
这个脚本主要提供对Exchange邮件服务器的账户爆破功能,集成了现有主流接口的爆破方式。
 cyrusimap/cyrus-sasl
Cyrus SASL API implementation providing client- and server-side authentication and authorization services via pluggable SASL mechanisms per RFC 4422.
 wolfssl/wolfssh
Small, portable embeddable SSHv2 client and server library in C with SCP, SFTP, port forwarding, and post-quantum key exchange for embedded and IoT…
 softethervpn/softethervpn
Cross-platform multi-protocol VPN server and client supporting SSL-VPN, WireGuard, OpenVPN, IPsec, L2TP, MS-SSTP, L2TPv3 and EtherIP with AES-256…
 j-baines/even-you-brutus
Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 d0ge/xsw
XML Signature Wrapping Burp Suite Extensions
 saml-toolkits/ruby-saml
Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…
 lxdwnpiper/cve-2026-48611-phpbb
Python proof-of-concept exploit that bypasses authentication in phpBB 3.3.16 and below by forging session cookies to gain admin access.
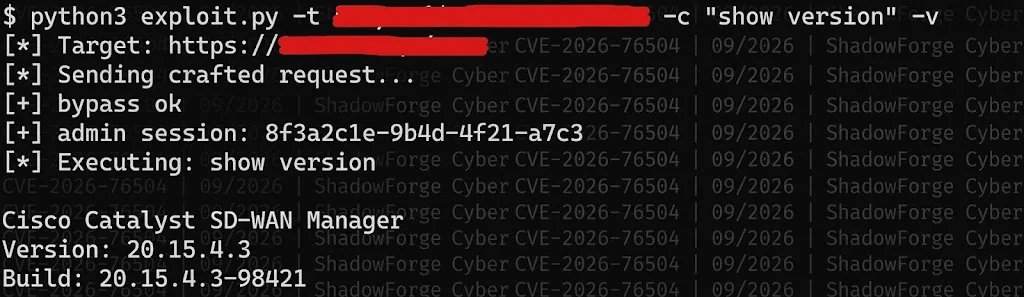 shadowforge-cyber/cve-2026-76504-proof-of-concept
EUVD-2026-89950 Improper Handling of URL Encoding (Hex Encoding) (CWE-177)
 99designs/aws-vault
A vault for securely storing and accessing AWS credentials in development environments
 karaaslanlabs/kl-security-key
Experimental RP2040 FIDO2/WebAuthn authenticator with packed attestation and documented Windows/Entra interoperability
 abraxas/cve-2026-103956-loom-unauth
CVE-2026-103956 - Loom for AWS - Critical - Auth bypass - unauthenticated super-admin when no IdP is configured








