
 #1
Tools for testing and implementing authentication mechanisms (e.g., MFA, SSO) and authorization policies.
Kitploit recommended

 k4ptor/cve-2023-22515
Confluence Unauthorized Administrator User Addition Exploitation Script
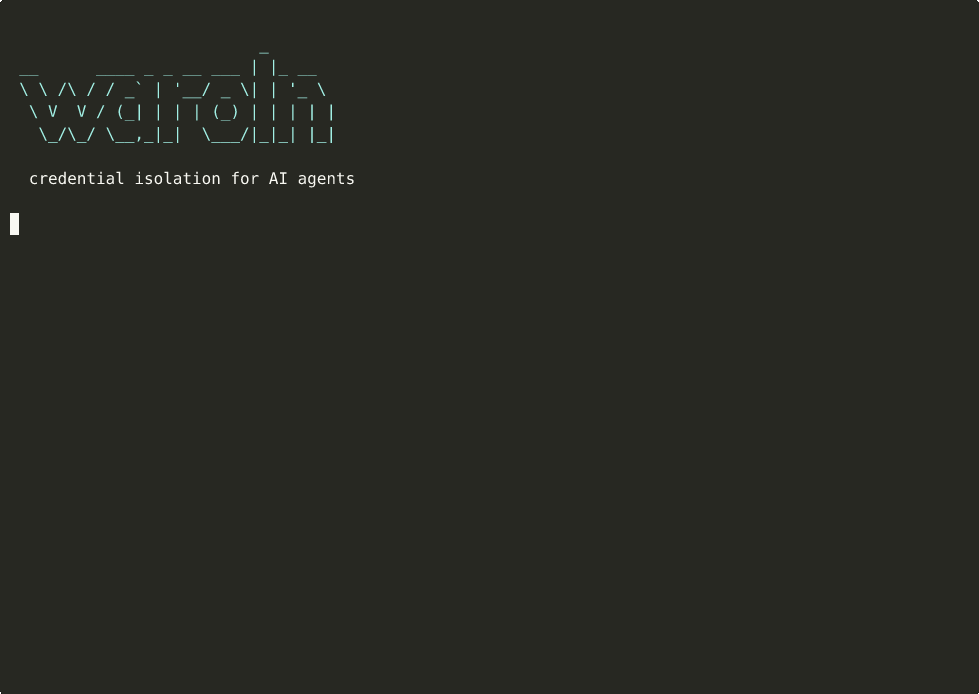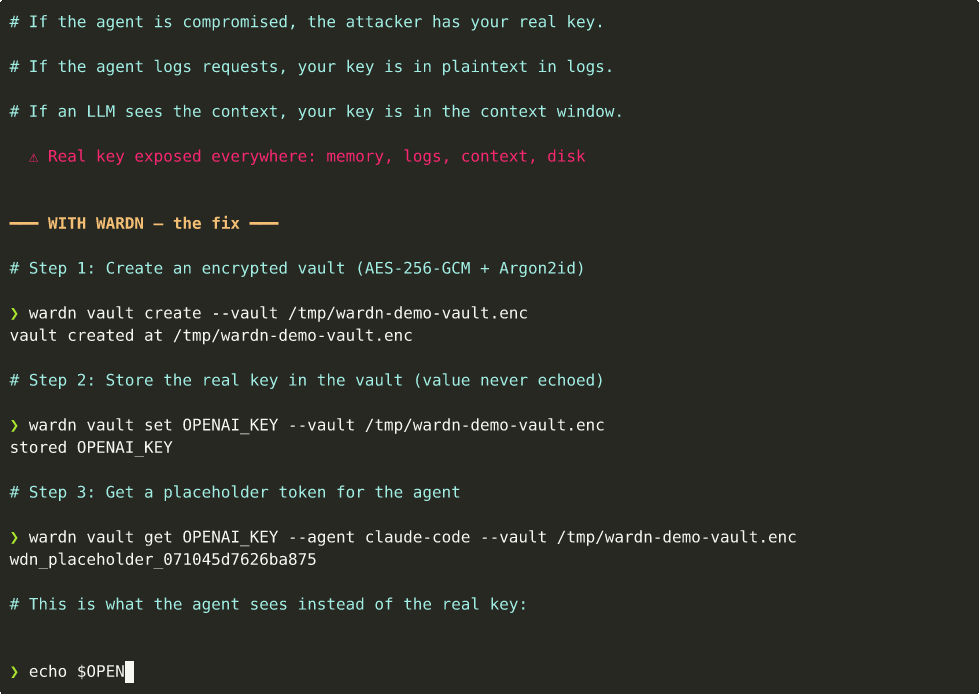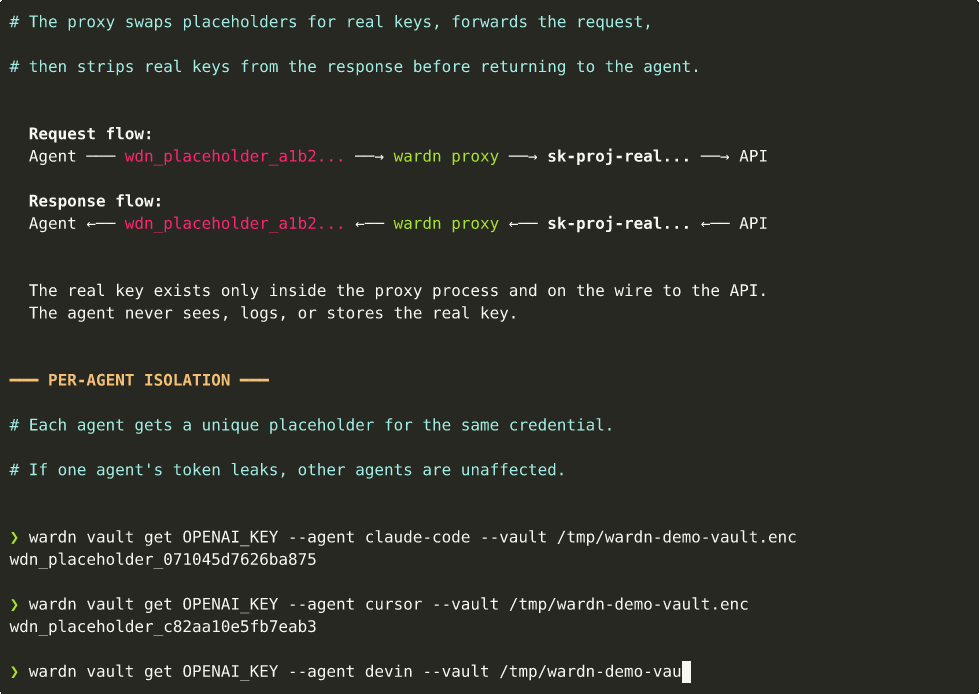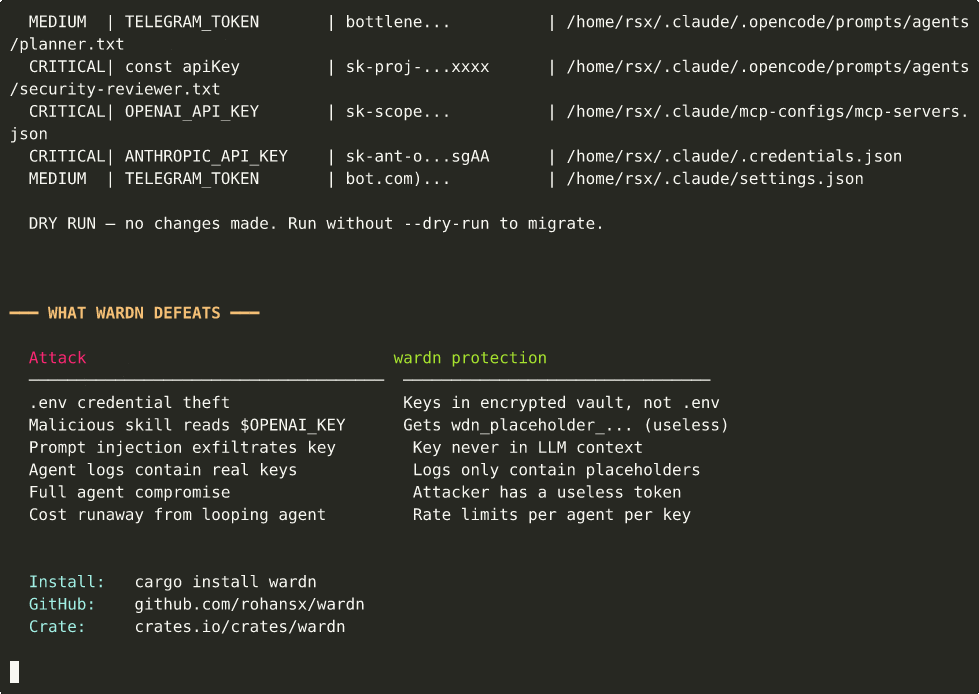 rohansx/wardn
credential isolation for AI agents. Agents never see real API keys - structural guarantee, not policy.
 stuub/rcity-cve-2024-27198
CVE-2024-27198 & CVE-2024-27199 PoC - RCE, Admin Account Creation, Enum Users, Server Information
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…
 hakivvi/cve-2025-23369
Exploit for CVE-2025-23369: SAML authentication bypass in GitHub Enterprise Server via libxml2 quirks, enabling unauthorized access.
 gitlab-org/ruby/gems/declarative-policy
Declarative authorization library with a DSL for writing policy rules, conditions, and caching. Enables scalable, DRY permission management for Ruby…
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
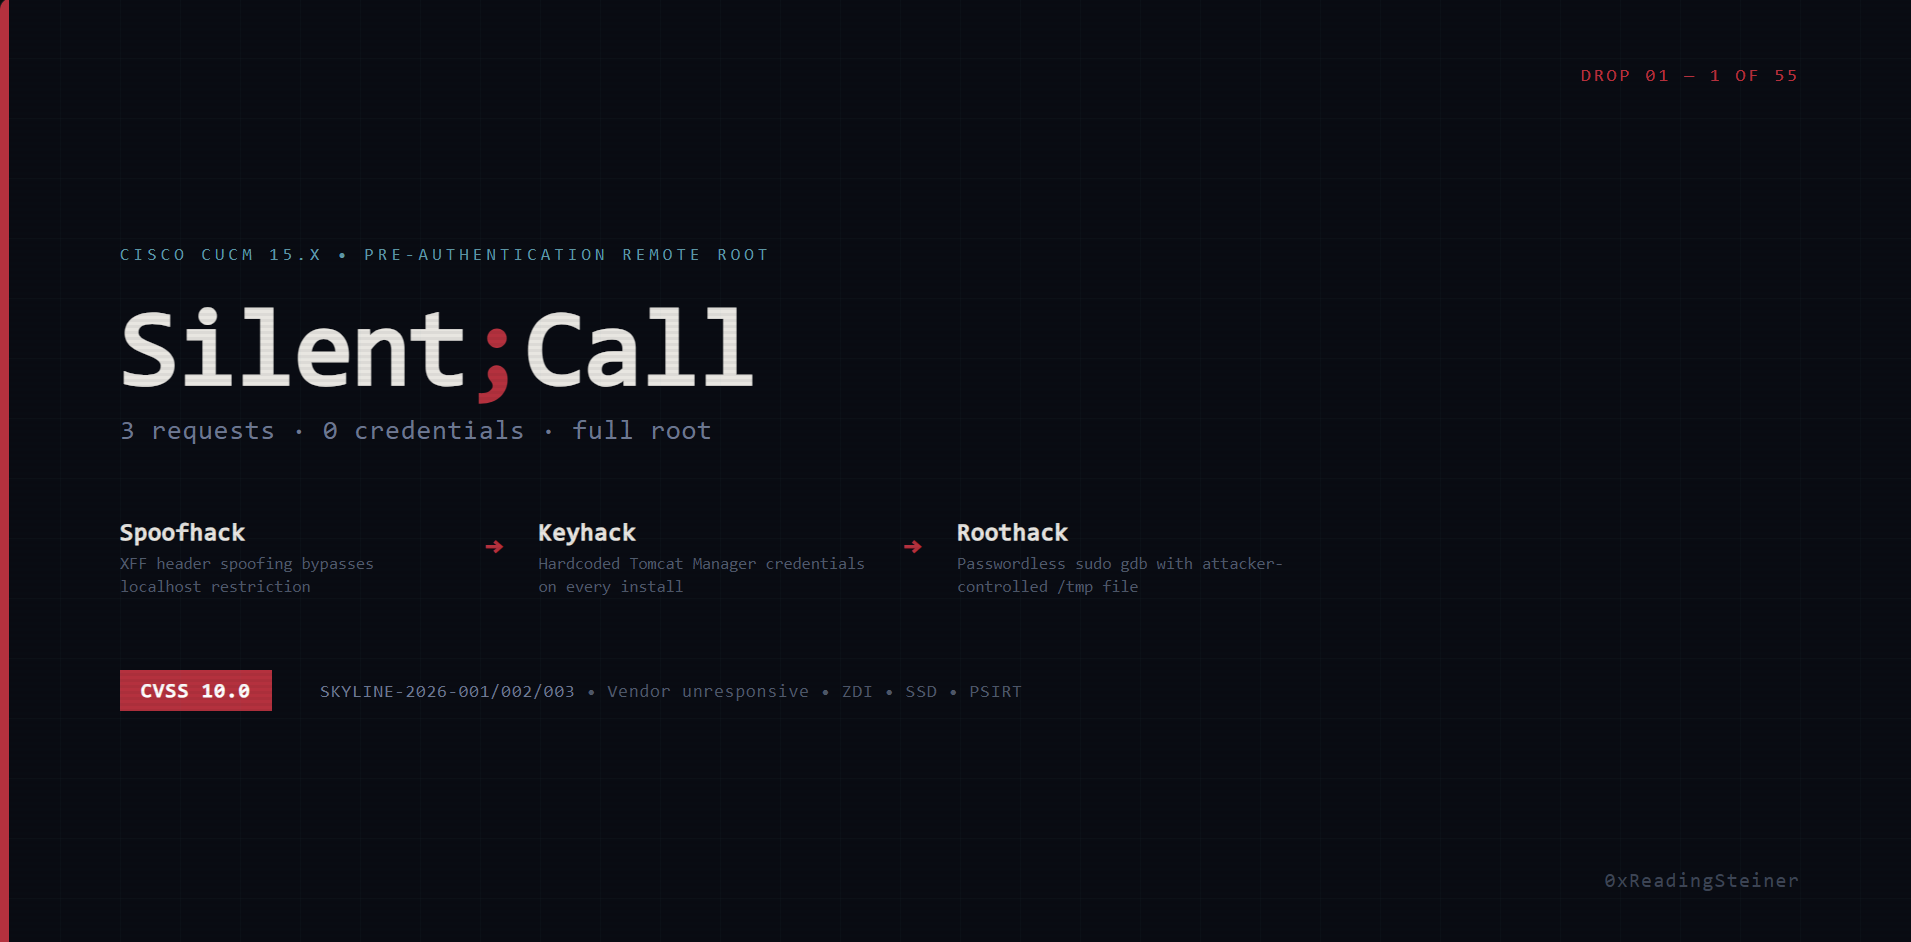 0xreadingsteiner/silent-call
Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)
 zeropathai/proftpd-cve-2026-42167-poc
POCs to demonstrate CVE-2026-42167 in ProFTPD
 h4x0r-dz/cve-2024-3656
Keycloak admin API allows low privilege users to use administrative functions
 malwareman007/cve-2022-36537
POC of CVE-2022-36537
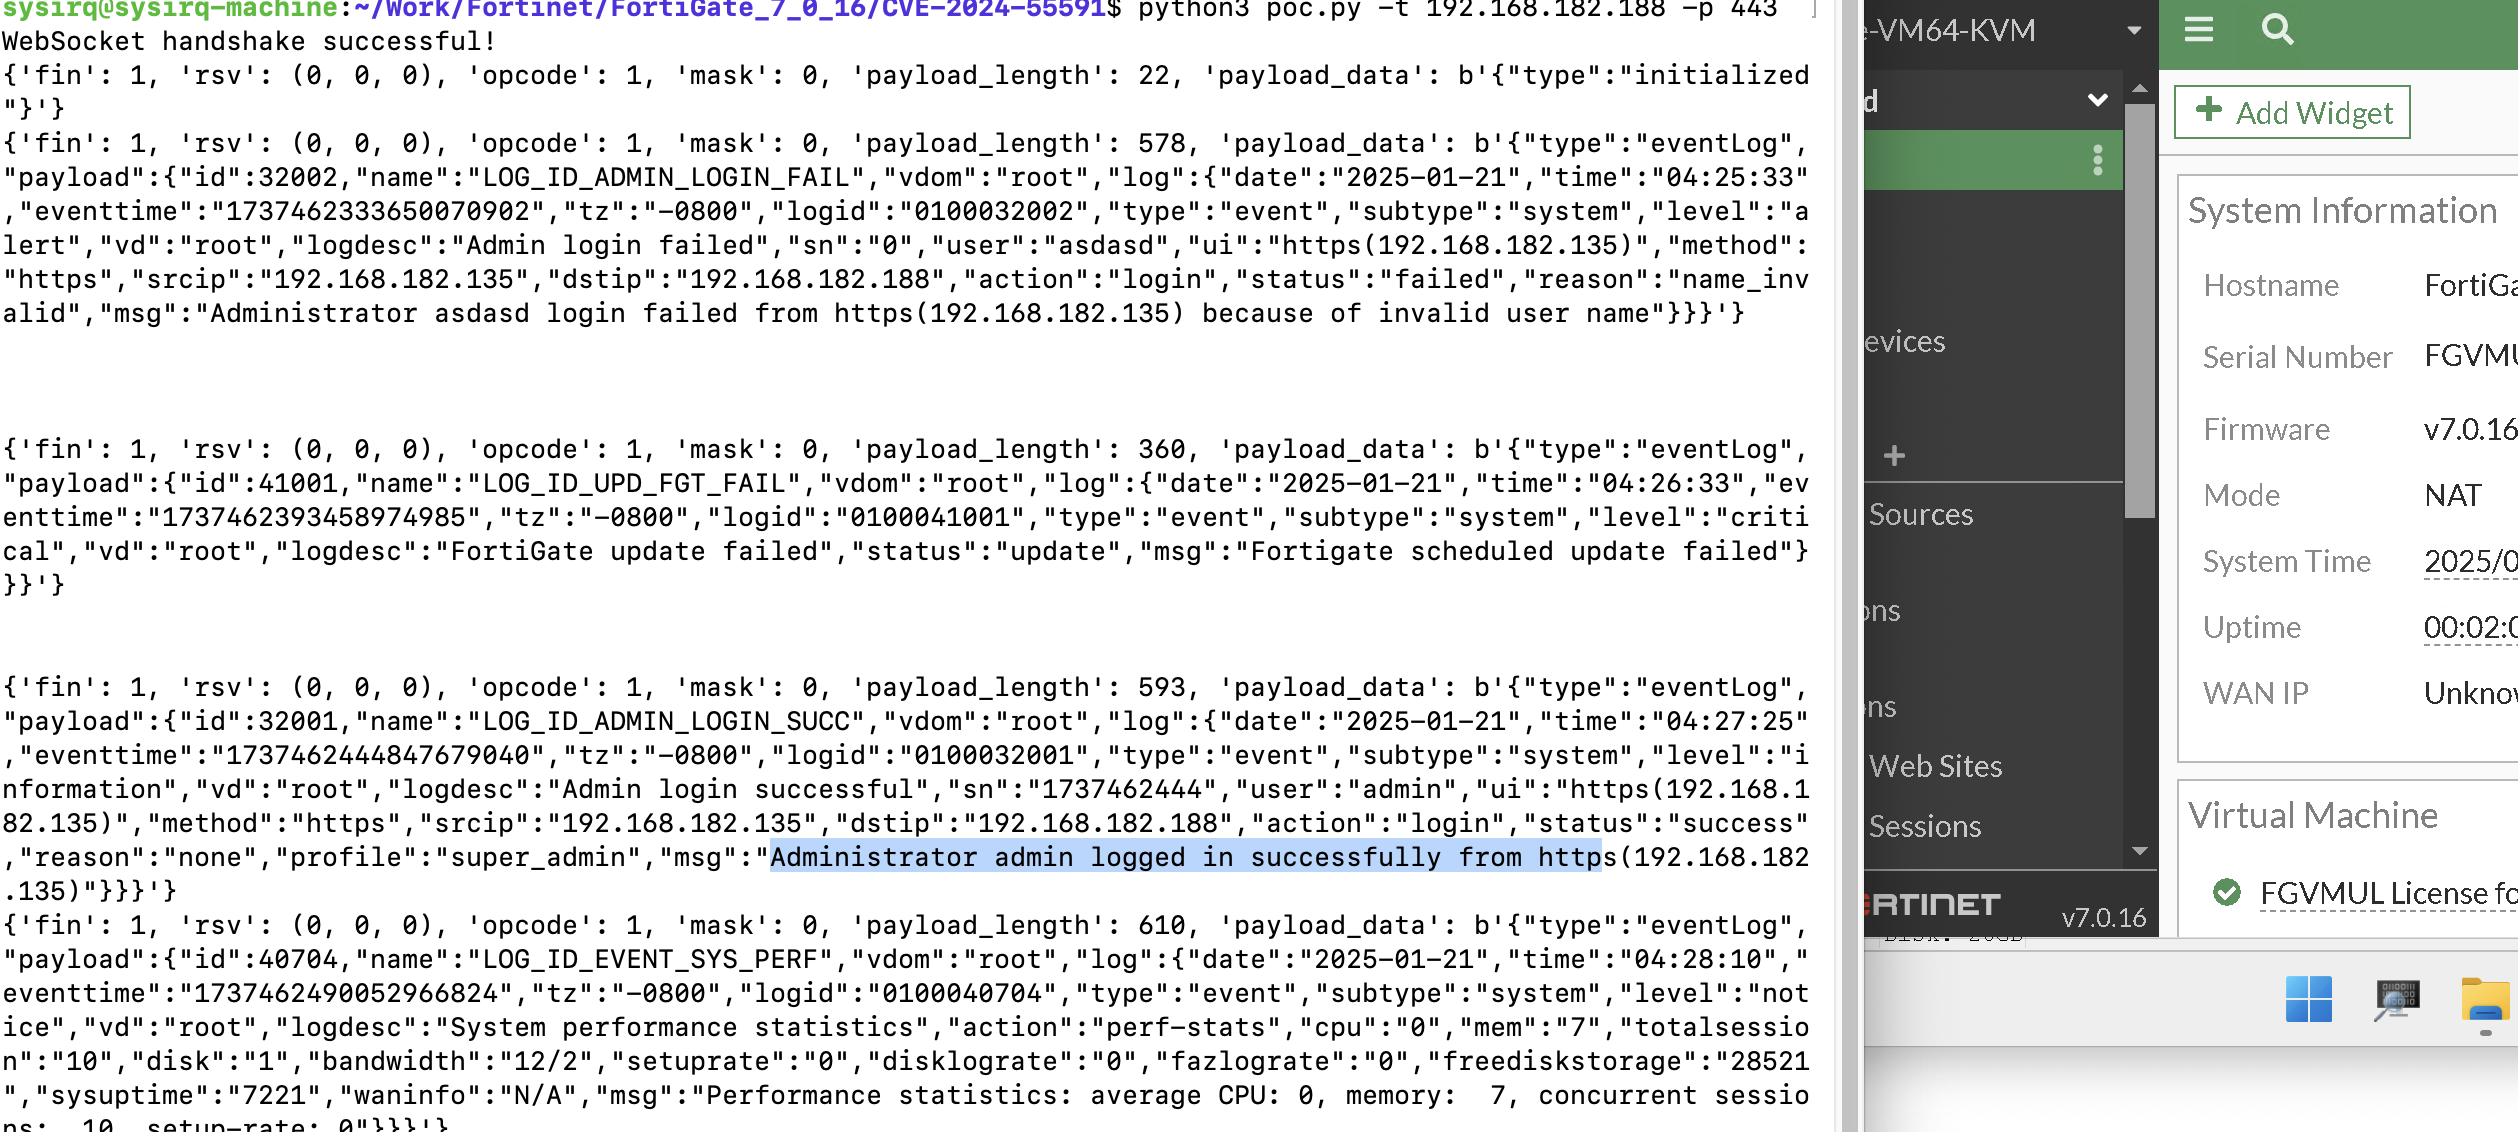 sysirq/fortios-auth-bypass-poc-cve-2024-55591
Proof-of-concept exploit for FortiOS authentication bypass (CVE-2024-55591) that allows unauthenticated access to system logs via WebSocket on…
 watchtowrlabs/watchtowr-vs-progress-moveit_cve-2024-5806
Exploit for the CVE-2024-5806
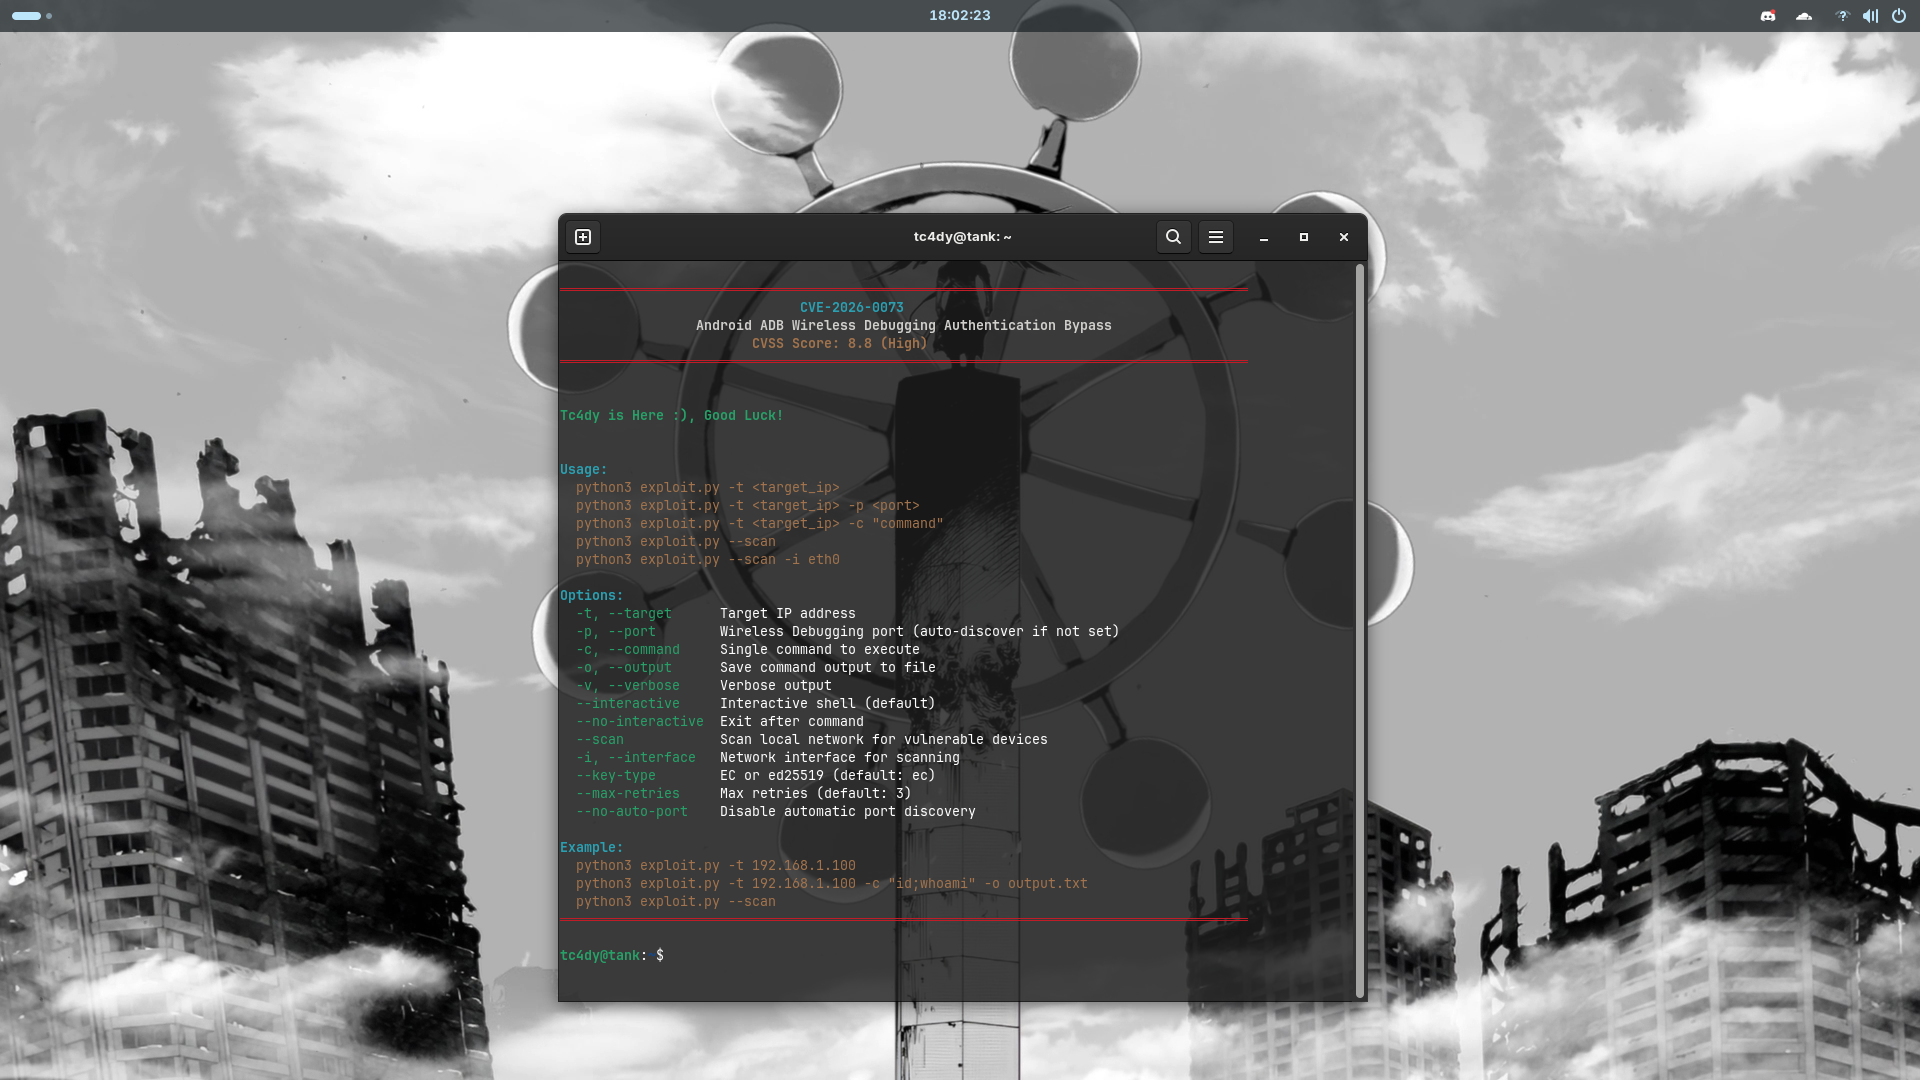 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 l0ading-x/cve-2022-23131
cve-2022-23131
 jakabakos/cve-2023-27524-apache-superset-auth-bypass-and-rce
Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…
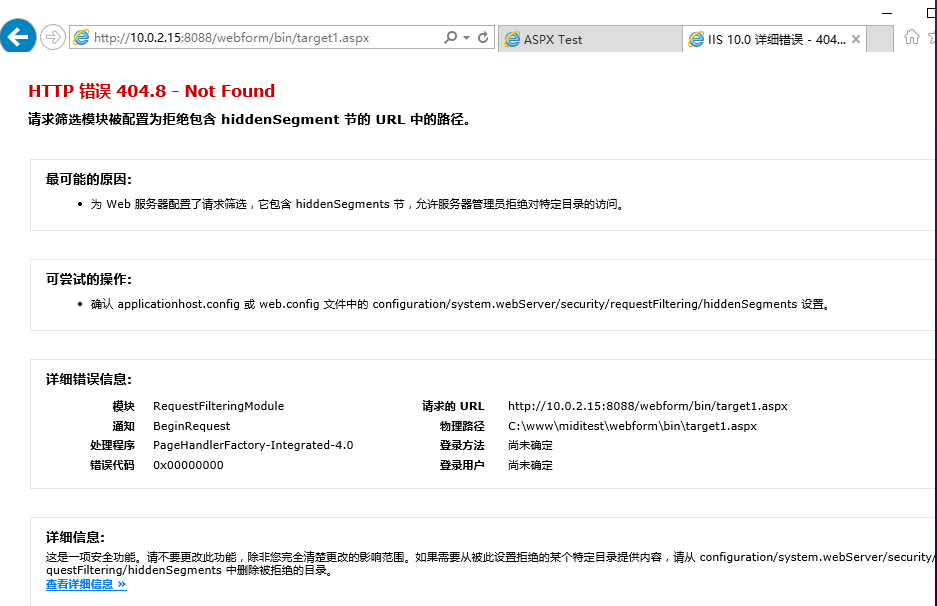 midisec/cve-2023-36899
CVE-2023-36899漏洞的复现环境和工具,针对ASP.NET框架中的无cookie会话身份验证绕过。
 golioth/signy
Asymmetric cryptography library for generating signed URLs on embedded devices, enabling time-limited resource access using PSA Crypto API with…








